 Do Son
TL;DR Two Linux kernel flaws now have public proof-of-concept exploit code and full technical write-ups. Bad Epoll...
Vulnerability Report

TL;DR X.Org shipped fixes for two memory-safety flaws in the X.Org Server and Xwayland. The more severe...
TL;DR PHP Composer, the main dependency manager for the language, patched three security flaws. The most serious,...
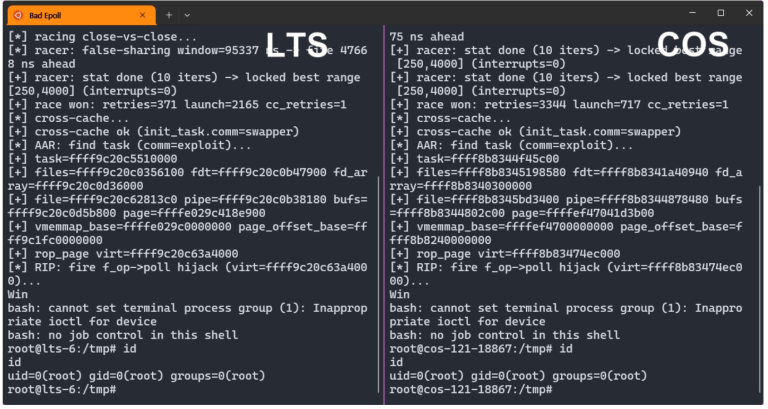
TL;DR Bad Epoll is a Linux kernel use-after-free that turns any unprivileged user into root. It is...
VMware Avi Load Balancer Authentication Bypass (CVE-2026-47865, CVSS 9.8) Headlines Seven-Flaw Patch

VMware Avi Load Balancer Authentication Bypass (CVE-2026-47865, CVSS 9.8) Headlines Seven-Flaw Patch
TL;DR Broadcom has patched seven vulnerabilities in VMware Avi Load Balancer under advisory VMSA-2026-0005. The most serious,...

TL;DR SAP Security Patch Day July 2026 shipped 16 new security notes and one GitHub advisory. The...

TL;DR CrowdStrike added 18 new methods to its AI security taxonomy. These new prompt injection attacks target...
TL;DR The WinFsp project has fixed two WinFsp vulnerabilities, CVE-2026-3006 (CVSS 7.0) and CVE-2026-7162 (CVSS 7.8). Both...
TL;DR Netwrix has fixed two Netwrix Password Secure vulnerabilities disclosed in advisory ADV-2026-008. The most severe flaw,...

TL;DR ServiceNow has patched a critical ServiceNow sandbox escape flaw, tracked as CVE-2026-6875 (CVSS 9.5), in its...
TL;DR A critical Better Auth SSRF flaw, tracked as CVE-2026-53513, lets any logged-in user reach internal services....
Hydro-Québec recently disclosed a severe privilege escalation flaw impacting its electric vehicle charging network. This critical vulnerability...
TL;DR Summary WatchTowr researchers disclosed a critical remote code execution flaw in Veeam Backup & Replication. The...

TL;DR A critical flaw in WAGO System I/O field devices now has a fix. Tracked as CVE-2026-4769,...
TL;DR Apache has patched a new flaw in Apache Log4j, tracked as CVE-2026-49844. The bug lets an...
TL;DR A high-severity decompress npm vulnerability lets crafted archives write files outside the extraction folder. Tracked as...
TL;DR Apache IoTDB has patched three flaws in its time-series database. The worst is a critical path...
TL;DR The Apache Camel project patched four high-severity flaws across five components. Three Apache Camel vulnerabilities let...
TL;DR CISA published an advisory for three flaws in the Gardyn IoT Hub, the controller for Gardyn’s...
TL;DR On June 30, 2026, the FreeBSD Project shipped three advisories covering FreeBSD privilege escalation bugs in...
TL;DR A researcher disclosed a Kafka authentication bypass in the OAUTHBEARER login path. It affects Apache Kafka...
TL;DR Security researchers discovered an HP Deskjet missing authorization vulnerability in the 2800 printer series. This flaw,...