 Do Son
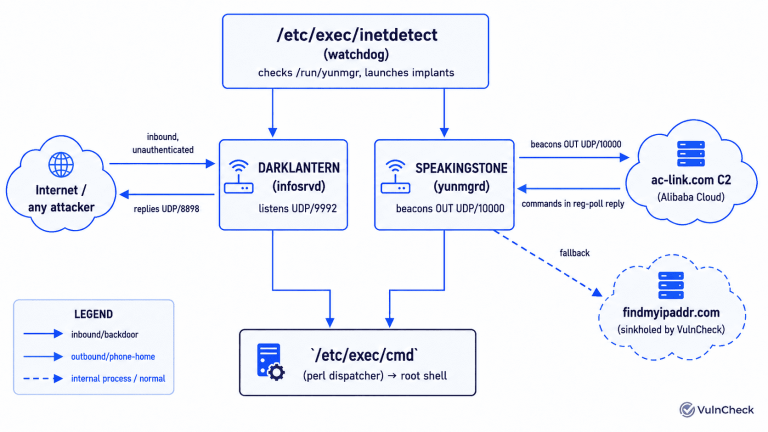
VulnCheck found a ZBT router backdoor in firmware, tracked as CVE-2026-74232 and CVE-2026-74233, granting unauthenticated root over the internet.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
ServiceNow patched CVE-2026-18885, CVE-2026-18886, and CVE-2026-74820, code injection and SQL injection flaws rated CVSS 10, plus a CVSS 8.7 bug.
PaperCut confirms a NG/MF vulnerability exploited in the wild. Restrict server access now and apply the emergency patch for versions 25 and 26.
CISA KEV Catalog updates include CVE-2023-49105, CVE-2026-53362, and CVE-2026-66384. These actively exploited flaws can fully compromise device security.
CISA warns that Xiiaozet LK100W vulnerabilities, including CVE-2026-78239, allow attackers to take full control of affected devices. Update now.
Attackers exploit CVE-2026-71362, an unauthenticated Adobe Commerce account takeover flaw (CVSS 9.1). Details and PoC are public. Patch now.
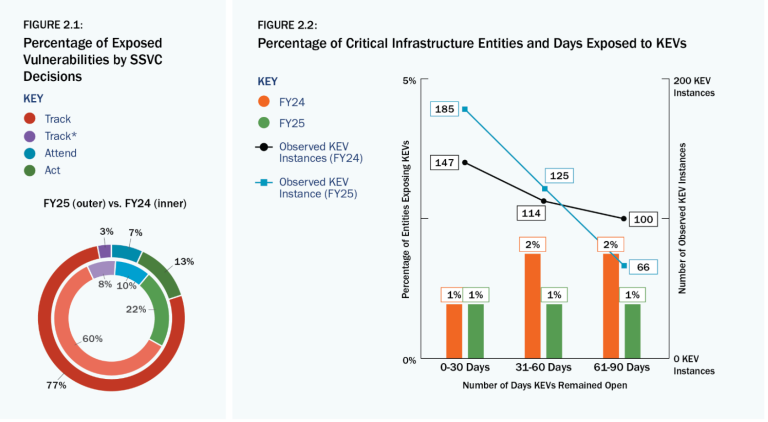
The CISA Vulnerability Review finds known exploited vulnerabilities and decades-old software flaws drive most compromises across FY2024 and FY2025.
TeamViewer patched CVE-2026-19042, a Linux command injection flaw, and a path traversal bug. Both TeamViewer vulnerabilities enable code execution.
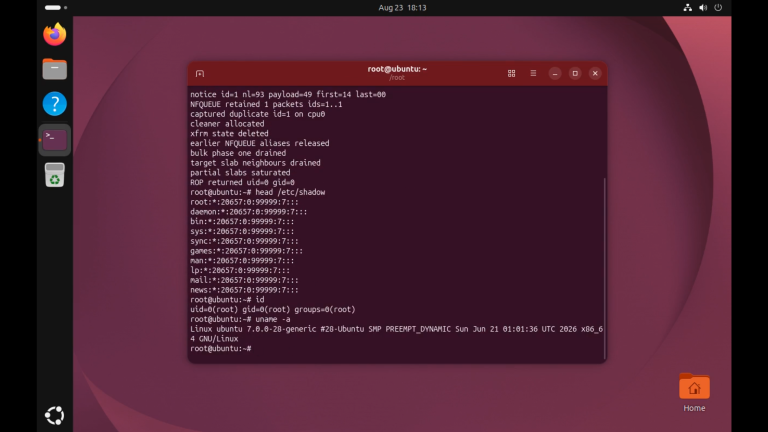
A public PoC exploit targets CVE-2026-72137, a CVSS 9.8 Linux kernel double-free that enables root privilege escalation. Patch now.
CISA adds six exploited vulnerabilities to its KEV Catalog, including a Citrix NetScaler flaw and CVE-2026-8452, with active exploitation confirmed.
Dell patched 5 Cloud Disaster Recovery flaws. The top bug, CVE-2026-70419 (CVSS 9.1), allows command execution. Update to CDR 20.3 now.
A high-severity TP-Link Kasa vulnerability (CVE-2026-76784) allows unauthorized smart home device control. Apply the latest firmware patch immediately.
A public PoC for CVE-2026-53361 turns an AF_UNIX kernel race into a local container escape on Linux. Details and exploit code are now disclosed.
Critical NVIDIA security updates patch multiple flaws in UFM and DGX Spark systems, addressing CVE-2026-24170 and CVE-2026-24262.
A critical GitLab EE security patch addresses CVE-2026-18252, fixing a command execution flaw. Learn about affected versions, mechanisms, and mitigation.
FreeBSD patched 8 vulnerabilities on August 25, 2026, mostly local privilege escalation flaws plus a ppp code execution bug. Update now.
Ubiquiti patched 22 UniFi flaws. Three hit CVSS 10.0, including command injection CVE-2026-77537. Update UniFi Protect, OS, and Talk now.
NVIDIA patched 20 NemoClaw and OpenShell flaws. The worst, CVE-2026-65093 (CVSS 9.9), enables code execution via sandbox escape. Update now.
A critical Veeam ONE vulnerability (CVE-2026-65641, CVSS 9.3) lets an unauthenticated attacker coerce SMB authentication. Patch Veeam now.
An unpatched Log4j RCE vulnerability was publicly disclosed on Apache's issue tracker. No CVE is assigned and no fix exists yet. Workaround inside.
Apache Tomcat fixed 11 vulnerabilities on August 25, 2026, including auth bypass (CVE-2026-68569) and HTTP/2 DoS flaws. Update to 11.0.25 now.
Two unpatched FURUNO FA-50 vulnerabilities (CVE-2026-59769, CVE-2026-67578) let attackers alter maritime transponder settings. Learn the mitigation steps.