
 Do Son
Google has rolled out a critical security update for the Chrome browser in its Stable channel, bumping...
Vulnerability Report

A newly disclosed vulnerability affecting Netcomm Wireless devices—now under Lantronix ownership—has been assigned CVE-2025-4010, and it poses...

MediaTek, a leading global chipset manufacturer, has published its June 2025 Product Security Bulletin, disclosing one high-severity...

Roundcube Webmail, a widely-used browser-based IMAP client, has patched a critical security vulnerability, tracked as CVE-2025-49113 (CVSS...
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued an advisory warning of two critical security...

Security researchers at Rapid7 have uncovered a troubling trio of vulnerabilities in MICI Network Co., Ltd.’s NetFax...
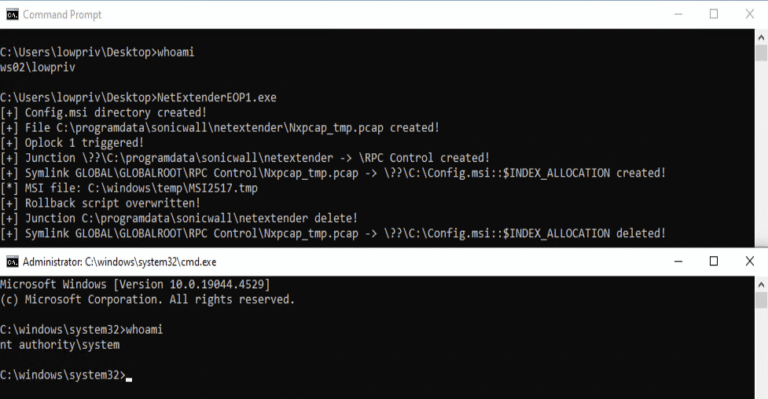
In a detailed investigation, NetSPI security researchers have uncovered multiple high-risk local privilege escalation (LPE) vulnerabilities in...

A study titled “Eradicating the Unseen” reveals the widespread presence of a critical path traversal vulnerability (CWE-22)...

Hitachi Energy has issued a cybersecurity advisory warning of multiple vulnerabilities impacting its Asset Suite product—a widely...

A newly disclosed vulnerability in Perl’s threading mechanism, tracked as CVE-2025-40909, exposes systems to race conditions involving...

A serious security vulnerability has been discovered in Apache Superset, a widely used open-source data exploration and...

A critical vulnerability—CVE-2025-20188—has been disclosed in Cisco IOS XE Wireless LAN Controller (WLC) software, allowing unauthenticated attackers...

Varnish Software has disclosed a client-side desynchronization vulnerability, tracked as CVE-2025-47905, in both Varnish Cache and Varnish...

The Ladybird browser engine, a relatively new entrant originating from the SerenityOS project, has been found to...

Popular VPN client app, OpenVPN Connect, patched a critical security flaw that could have exposed users’ private...