
 Do Son
CISA adds critical CitrixBleed 2 (CVE-2025-5777, CVSS 9.2) to KEV, confirming active exploitation. Attackers are extracting session tokens to bypass MFA and hijack sessions on NetScaler ADC/Gateway
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.

Apache HTTP Server 2.4.64 patches 8 vulnerabilities, including HTTP Response Splitting, SSRF, DoS, and TLS desync attacks. Upgrade immediately!

Huntress witnessed active exploitation of a critical RCE flaw (CVE-2025-47812) in Wing FTP Server, allowing root/SYSTEM access via null byte injection and Lua code execution.
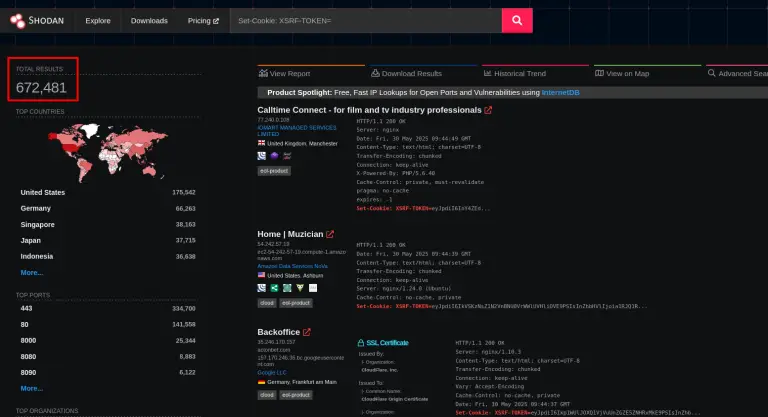
Synacktiv reveals Laravel’s APP_KEY vulnerability allows RCE via deserialization attacks when the key is leaked or guessable, risking full application compromise.

A flaw in Helm (CVE-2025-53547, CVSS 8.5) allows local code execution when updating dependencies via a malicious Chart.yaml and symlinked Chart.lock file

A critical flaw (CVE-2025-6691, CVSS 8.8) in the SureForms WordPress plugin allows unauthenticated arbitrary file deletion (e.g., wp-config.php), leading to full site takeover.

GitLab releases urgent security updates to fix critical vulnerabilities, including an 8.7 CVSS score XSS flaw. Update your instances now to prevent attacks.

A critical flaw (CVE-2025-7206, CVSS 9.8) in D-Link DIR-825 firmware 2.10 allows unauthenticated remote buffer overflow, crashing the web interface.

Multiple critical flaws (CVE-2025-44954, -44957, -44963, -44955, -6243) in Ruckus vSZ/RND allow unauthenticated RCE, auth bypass via hardcoded SSH keys and JWT.

The Opossum Attack is a new desynchronization flaw exploiting implicit/opportunistic TLS in protocols like HTTP, allowing MitM to compromise encrypted connections. Over 3M servers affected.

Schneider Electric warns of critical flaws (CVSS 10.0 RCE, SSRF, EoP) in EcoStruxure IT Data Center Expert. Patch to v9.0 immediately to prevent data center disruption.

GeoServer's RCE flaw (CVE-2024-36401) is actively exploited to deploy NetCat reverse shells and XMRig CoinMiners on Windows/Linux, hijacking resources.

CISA warns of critical flaws in Emerson ValveLink software, exposing cleartext data, allowing code execution, and compromising industrial systems. Update to v14.0 now.

Zoom rolls out security updates for 6 newly disclosed flaws in Workplace, Rooms, and SDK, addressing DoS, info disclosure, and XSS across all platforms. Update now!

The Git Project has released updates addressing three significant vulnerabilities impacting Git versions up to v2.50.0, including...

Siemens warns of critical flaws (CVE-2025-40736 CVSS 9.8 Auth Bypass, SQLi, Path Traversal) in SINEC NMS, allowing unauthenticated remote root access and RCE.
Citrix Warns of Privilege Escalation Vulnerability in Windows Virtual Delivery Agent (CVE-2025-6759)

Citrix Warns of Privilege Escalation Vulnerability in Windows Virtual Delivery Agent (CVE-2025-6759)
Citrix warns of a high-severity local privilege escalation flaw (CVE-2025-6759, CVSSv4 7.3) in Windows VDA, allowing low-privileged users to gain SYSTEM access.

Microsoft's July 2025 Patch Tuesday fixes 140 flaws, including a SQL Server zero-day (CVE-2025-49719), multiple RCEs, critical Office/Word bugs, and AMD CPU-level threats.

Fortinet released a critical patch for FortiWeb (CVE-2025-25257, CVSS 9.6). This unauthenticated SQL injection flaw allows remote code execution; update immediately!

Phoenix Contact warns of critical flaws (CVE-2025-25270 CVSS 9.8 RCE, CVE-2025-25268 Auth Bypass, CVE-2025-25271 OCPP Reconfig, CVE-2025-25269 LPE) in CHARX SEC-3xxx EV controllers.

MediaTek's July 2025 bulletin reveals critical flaws in chipsets, enabling local EoP, remote RCE, and info disclosure in smartphones, AIoT devices, and smart TVs.

SAP's July 2025 Patch Day fixes 27 vulnerabilities, including critical RCE (CVSS 10.0) in Live Auction Cockpit and multiple insecure deserialization flaws (CVSS 9.1) across NetWeaver components.