
 Do Son
A critical RCE flaw (CVE-2025-47812, CVSS 10.0) in Wing FTP Server allows unauthenticated attackers to execute arbitrary Lua code via NULL byte injection, compromising the server
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.

A critical flaw (CVE-2025-6463, CVSS 8.8) in Forminator WordPress plugin allows unauthenticated arbitrary file deletion, leading to site takeover.

DataEase has critical flaws in database connection handling, allowing remote RCE and JDBC parameter bypasses for H2, Redshift, and PostgreSQL. Update to v2.10.11 now!

A flaw (CVE-2025-53106) in Graylog allows authenticated users to escalate privileges via API token abuse. Update to 6.2.4 or 6.3.0-rc.2 immediately.

Three flaws in Frappe Framework allow account takeover via password reset token leaks, XSS via file upload, and SQL injection. Update self-hosted ERPNext immediately!

CERT@VDE and Pilz disclose critical flaws in IndustrialPI 4: unauthenticated remote bypass (CVSS 9.6) and RCE (CVSS 10.0) via exposed Node-RED. Update or mitigate immediately.

Two Sudo flaws (CVE-2025-32463 & CVE-2025-32462) allow local users full root via PoC. Critical privilege escalation vulnerabilities revealed by Stratascale CRU.

A critical flaw (CVE-2025-6543, CVSS 9.2) in NetScaler ADC/Gateway is actively exploited for DoS. Over 2,100 unpatched appliances remain susceptible. Update immediately!

A critical vulnerability—CVE-2025-49596—affected the AI developer ecosystem in June 2025, when Oligo Security Research disclosed a severe...

Google has urgently patched a high-severity zero-day (CVE-2025-6554) in Chrome's V8 JavaScript engine. This type confusion flaw is actively exploited in the wild, risking RCE.

Citrix Bleed 2 (CVE-2025-5777, CVSS 9.2) is actively exploited to hijack sessions and bypass MFA on NetScaler ADC/Gateway. Patch immediately to prevent covert access and data theft.

Six critical flaws in D-Link's EOL DIR-816 routers are exposed. No patches will be issued; replace device immediately to avoid remote code execution.

A flaw (CVE-2025-4679) in Synology ABM leaked a static client_secret, allowing unauthenticated attackers read-only access to all Microsoft 365 tenants with ABM installed.

IBM warns of a critical RCE flaw (CVE-2025-36038) in WebSphere Application Server 8.5/9.0, allowing unauthenticated attackers to execute arbitrary code via serialization.

A critical flaw (CVE-2025-3699) in Mitsubishi Electric AC systems allows remote authentication bypass, risking illegal control and firmware tampering.
A critical flaw (CVE-2025-6561, CVSS 9.8) in Hunt Electronic DVRs allows unauthenticated remote attackers to access configuration files and obtain plaintext admin credentials.
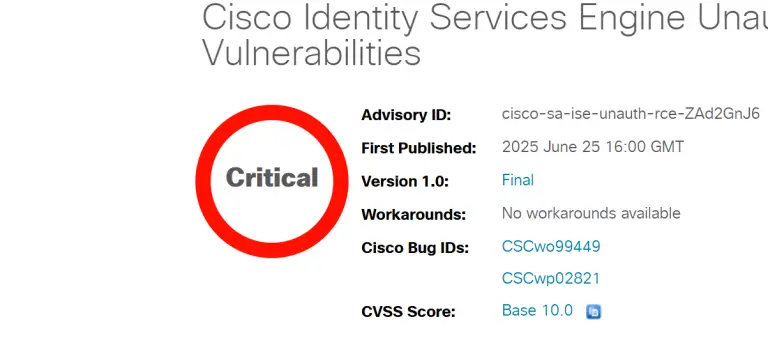
Cisco warns of two critical flaws (CVE-2025-20281, CVE-2025-20282, CVSS 10.0) in ISE and ISE-PIC allowing unauthenticated remote root code execution. Apply patches immediately.
Citrix warns of a critical memory overflow flaw (CVE-2025-6543, CVSS 9.2) in NetScaler ADC/Gateway, actively exploited for DoS. Update to patched versions immediately!
CISA warns of critical flaws in MICROSENS NMP Web+ (v3.2.5 & earlier), including hardcoded JWTs, persistent sessions, and path traversal (CVSS 9.8 RCE). Update to 3.3.0 now!
Rapid7 warns of critical flaws (CVE-2024-51978, CVSS 9.8) in multi Brother printers, allowing auth bypass and RCE. Update firmware & change passwords immediately!
CISA, FBI, and NSA call for adopting memory-safe languages (Rust, Go, Java, Swift) to slash software vulnerabilities. Android saw a 52% drop in memory bugs after embracing MSLs.
IBM warns of a high-severity flaw (CVE-2025-36004, CVSS 8.8) in IBM i Facsimile Support that allows local users to gain elevated privileges. Apply PTF SJ06024 immediately.