
 Do Son
Cisco ClamAV versions 1.4.3 and 1.0.9 fix critical flaws: CVE-2025-20260 (CVSS 9.8) in PDF scanning could allow RCE, and CVE-2025-20234 (UDF) leads to DoS.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.

A critical flaw (CVE-2025-5071) in WordPress's AI Engine plugin allows subscribers to escalate privileges and take over websites with Dev Tools/MCP enabled.
Cisco warns of a critical flaw (CVE-2025-20271, CVSS 8.6) in Meraki MX/Z Series devices, allowing unauthenticated remote DoS on AnyConnect VPN. Update firmware now!

A critical SSRF flaw (CVE-2025-6087) in @opennextjs/cloudflare allows unauthenticated users to proxy arbitrary remote content via /_next/image endpoint.

A critical flaw (CVE-2025-51381) in KAON KCM3100 Wi-Fi gateways allows local attackers to bypass authentication. Update firmware to version 1.4.8 immediately.

Qualys uncovered two critical Linux flaws (CVE-2025-6018, CVE-2025-6019) allowing local root privilege escalation via PAM and UDisks. Patching is urgent for major distros.

CISA has added CVE-2023-0386, a critical Linux kernel OverlayFS flaw, to its KEV Catalog, confirming active exploitation allowing local users to gain root privileges.

Cloud Software Group issues urgent patches for two critical NetScaler flaws allowing access bypass and memory overread. Update immediately.

Veeam released a critical update for Backup & Replication, patching three flaws, including a CVSS 9.9 RCE (CVE-2025-23121) allowing authenticated users to execute code.

Google Chrome 137.0.7151.119/.120 is rolling out with crucial security fixes, addressing two high-severity flaws: an integer overflow in V8 and a use-after-free in Profiler.

WAGO Device Manager security updates address two vulnerabilities allowing unauthenticated remote access to sensitive system files.

Microsoft disabled Windows Hello facial recognition in dark environments on Windows 10/11 due to a security flaw that could allow local spoofing attacks.

ASUS warns of a high-severity flaw in Armoury Crate that allows authentication bypass and privilege escalation. Update immediately!

Team46 (TaxOff) is exploiting a Google Chrome sandbox escape zero-day (CVE-2025-2783) to deploy the multi-layered Trinper malware via phishing campaigns

A critical flaw (CVE-2025-49596, CVSS 9.4) in MCP Inspector allows unauthenticated remote code execution, threatening AI application development environments.

SUSE disclosed flaws in sslh (CVE-2025-46807, CVE-2025-46806) allowing remote DoS attacks via file descriptor exhaustion and unsafe memory access.

Apache Tomcat patched four vulnerabilities affecting versions 9.0, 10.1, and 11.0, ranging from DoS to privilege bypass. Update immediately

CISA adds two actively exploited zero-days to KEV: an iOS zero-click flaw used by spyware (CVE-2025-43200) and a command injection in TP-Link routers
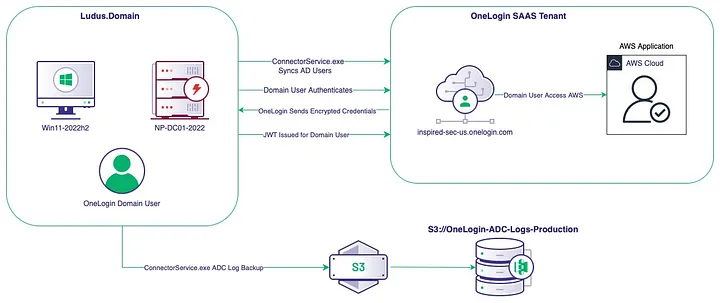
A critical flaw in OneLogin's AD Connector exposed API keys, allowing attackers to impersonate users across organizations via unclaimed S3 buckets and forged JWT tokens.

PoCGen is a new AI tool using LLMs, static, and dynamic analysis to automate PoC exploit generation for npm vulnerabilities, achieving high success rates at low cost.

Zyxel firewalls are under a coordinated attack exploiting critical RCE flaw CVE-2023-28771 (CVSS 9.8) via UDP port 500, likely by Mirai botnets. Patch immediately

A critical RCE flaw (CVE-2025-3248) in Langflow is being actively exploited to deploy the stealthy Flodrix botnet for reconnaissance and diverse DDoS attacks on AI app servers.