
 Do Son
A critical 9.8 CVSS vulnerability in PayU CommercePro for WordPress allows unauthenticated admin account takeover. No patch available, immediate removal advised.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.

QNAP releases urgent patches for high-severity flaws in Qsync Central and File Station 5, enabling RCE and data compromise. Update immediately!

B. Braun's OnlineSuite AP 3.0 faces severe vulnerabilities, including a CVSS 10.0 RCE, risking hospital IT and data. Immediate patching is crucial.

CERT Polska warns of a critical Roundcube XSS flaw (CVE-2024-42009) exploited by UNC1151 in spear phishing, stealing credentials and compromising Polish organizations.

Go 1.24.4 and 1.23.10 fix flaws in net/http, os, and crypto/x509, addressing data leaks, file inconsistencies, and certificate validation bypasses. Update now!

CVE-2025-4318 (CVSS 9.5) hits AWS Amplify Codegen UI with PoC exploit. RCE flaw puts CI/CD pipelines and developer environments at high risk.

A new Mirai botnet variant is exploiting CVE-2024-3721 to infect vulnerable DVRs. Learn how this sophisticated attack works and if your surveillance system is at risk.

Enthusiasts found a userland exploit in the new Nintendo Switch 2, altering program behavior. Nintendo maintains a strict stance on modifications.

A high-severity XSS flaw (CVE-2025-5806) in Jenkins Gatling Plugin bypasses CSP, risking session hijacking and credential theft. Downgrade to v1.3.0 immediately!

CISA issues critical warning for CyberData SIP Emergency Intercom (Model 011209) with severe vulnerabilities (CVSS 9.8), risking remote access and code execution. Update now.


Amazon warns of a high-severity (CVSS 8.4) memory corruption flaw (CVE-2025-5688) in FreeRTOS-Plus-TCP. Patch immediately to prevent crashes and RCE in affected devices.

A high-severity vulnerability (CVE-2025-1701) in MIM Admin service allows local code execution with elevated privileges, impacting medical imaging environments.
Weaponizing Group Policy: Custom Client-Side Extensions as a Stealthy Backdoor into Active Directory

Weaponizing Group Policy: Custom Client-Side Extensions as a Stealthy Backdoor into Active Directory
A new, stealthy AD persistence technique abuses custom Group Policy Client-Side Extensions (CSEs) for SYSTEM-level access. Learn how to detect it!

Critical CVSS 9.8 flaws in HPE Insight Remote Support could allow remote code execution and SYSTEM-level file access. Patch now to stay secure.

A critical RCE flaw (CVE-2025-49113) in Roundcube is under active exploitation with PoC sold on forums. Patch immediately to v1.5.10 or v1.6.11!

Cisco addresses CVE-2025-20129 and CVE-2025-20130 in CCP and ISE platforms. PoC exploits are public. Admins urged to migrate to fixed versions.

A critical Auth0 PHP SDK deserialization flaw (CVE-2025-48951, CVSS 9.3) allows unauthenticated RCE in web apps. Patch to v8.14.0+ immediately!

Cisco issues advisories for high-severity flaws (CVSS 8.8, 8.7) in IMC and NDFC, risking privilege escalation and device impersonation. Patch immediately!

Auth0 Next.js SDK flaw (CVE-2025-48947, CVSS 7.7) could expose session cookies via CDNs. Patch to v4.6.1 immediately to secure your app!

Kaspersky warns organizations are overestimating container isolation. New analysis reveals hidden attack surfaces and crucial detection blind spots.
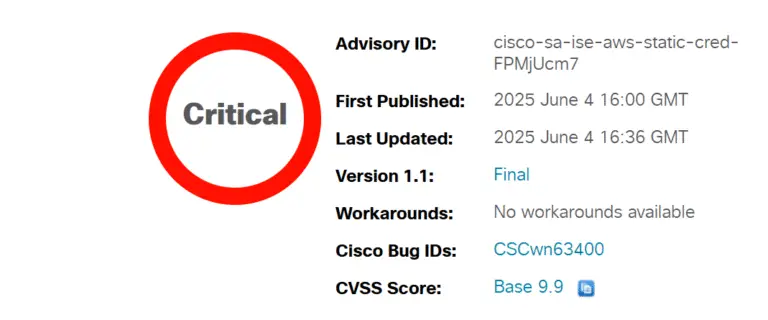
CVSS 9.9 flaw in Cisco ISE cloud deployments with public PoC exploit enables remote attacks on AWS, Azure, and OCI. Patch now.