
 Do Son
ABB warns of a critical session fixation vulnerability (CVE-2024-13967) in EIBPORT V3, allowing unauthorized access. Update to firmware 3.9.9 immediately.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.

Broadcom releases critical patches for three Stored XSS vulnerabilities (CVE-2025-22243, CVE-22244, CVE-22245) in VMware NSX, Cloud Foundation & Telco Cloud. Update immediately!

CISA adds 3 actively exploited Qualcomm Adreno GPU flaws to KEV catalog. Android devices at risk from memory corruption and use-after-free bugs.

Critical CVSS 9.6 vulnerability in IBM QRadar & Cloud Pak for Security exposes systems to RCE & DoS. Patch immediately to secure your platforms.

Discover VulBinLLM, a groundbreaking LLM-powered framework by UCLA & Cisco Research, revolutionizing binary vulnerability detection in stripped software.

A security researcher achieved full control of the FiberGateway GR241AG router, exposing 1.6M Portuguese households to RCE, DNS hijacking, and WPA2 key theft.
Qualys reveals two critical Linux vulnerabilities (CVE-2025-5054, CVE-2025-4598) in Apport & systemd-coredump, risking sensitive data exposure. Patch now!

Kaspersky's Q1 2025 report highlights a surge in attacks on aging systems, unpatched flaws, and mismanaged updates, urging vigilance and prompt action.

CISA warns of a critical vulnerability (CVE-2025-1907) in Instantel Micromate devices, allowing unauthenticated remote command execution. Immediate action is advised.

CISA adds 5 new exploited vulnerabilities to KEV, including flaws in ASUS routers, Craft CMS, and ConnectWise. Urgent patching required!

Critical Chrome security update released! Patching an actively exploited zero-day vulnerability (CVE-2025-5419) and other flaws. Update now to stay safe!

A critical vulnerability (CVE-2025-4010) in Netcomm Wireless devices allows remote code execution, impacting industrial and telecom networks.

MediaTek's June 2025 Security Bulletin reveals a high-severity Bluetooth flaw & multiple medium risks across chipsets, affecting WLAN & IMS. Update your devices!

Roundcube Webmail has patched a critical RCE vulnerability (CVE-2025-49113) allowing remote code execution post-authentication. Update to 1.6.2 or 1.5.10 immediately!
CISA warns of critical flaws (CVE-2025-41438, CVE-2025-46352) in Consilium Safety CS5000 Fire Panels, allowing remote access & disruption. Vendor won't patch.

Rapid7 found critical RCE flaws in MICI NetFax (versions < 3.0.1.0) via default credentials & command injection. Vendor refuses to patch, advising no internet exposure.
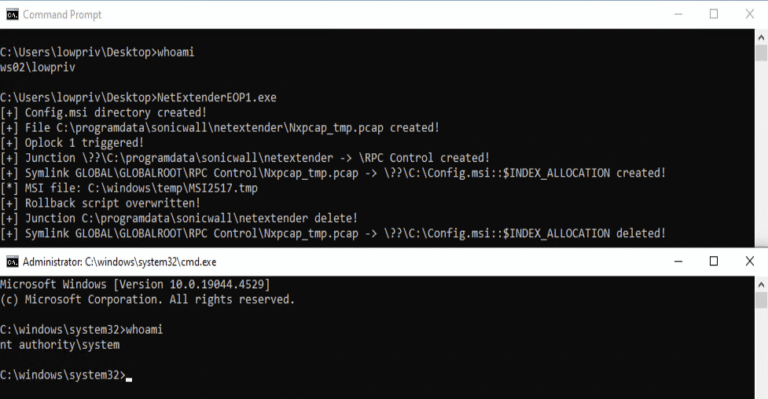
High-risk LPE vulnerabilities in SonicWall NetExtender for Windows (CVE-2025-23009, CVE-2025-23010) allow SYSTEM access or DoS. Patch immediately to version 10.3.2.

A study reveals widespread path traversal (CWE-22) in open-source projects, exacerbated by LLMs generating insecure code. Automated detection and patching are critical.

Hitachi Energy's Asset Suite, used in power gen, faces severe vulnerabilities including XSS, plaintext passwords, & RCE. Immediate action advised to secure systems.

A new race condition vulnerability in Perl's threading mechanism exposes systems to local attackers. Upgrade to Perl 5.41.13 or apply the patch immediately.

A SQL injection vulnerability (CVE-2025-48912) in Apache Superset allows authenticated attackers to bypass row-level security, exposing sensitive data.

A critical Cisco IOS XE WLC flaw (CVE-2025-20188, CVSS 10) allows unauthenticated RCE via arbitrary file uploads. Update or disable Out-of-Band AP Image Download.