 Do Son

TL;DR
On September 21, 2026, security researcher Rafie Muhammad published technical analysis of a high-severity flaw in WordPress core. The WordPress stored XSS flaw, tracked as CVE-2026-93485, allows unauthenticated visitors to execute arbitrary scripts through crafted comments. Furthermore, full technical details of the vulnerability and working proof-of-concept exploit code have been publicly disclosed.
- CVE: CVE-2026-93485
- CVSS: 7.2 (High · CVSSv3)
- Product: Automattic WordPress
- Affected: 7.1, 7.0, 6.9, 6.8, 6.7, 6.6 (+19 more)
- Impact: WordPress core <= 7.1 - Unauth. Cross Site Scripting (XSS) vulnerability
- Status: No confirmed exploitation yet
- Patched in: 7.1.1, 7.0.5, 6.9.8, 6.8.9 (+21 more)
- EPSS: 0.2% (30-day)
- Action: Update to 7.1.1, 7.0.5, 6.9.8, 6.8.9 (+21 more) now
Track every WordPress CVE the moment it's exploited.
Get free email alertsWhy It Matters
WordPress powers over 43 percent of all websites on the internet. Sourced estimates indicate this represents over 500 million active digital properties worldwide. Therefore, any security flaw in core comment handling poses massive risks to the global web ecosystem.
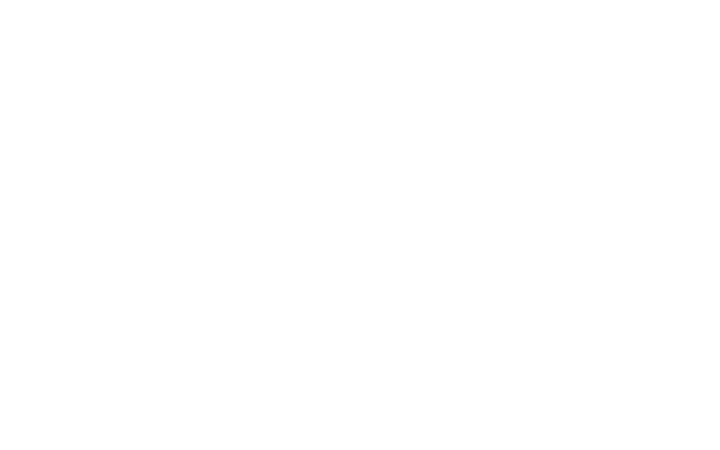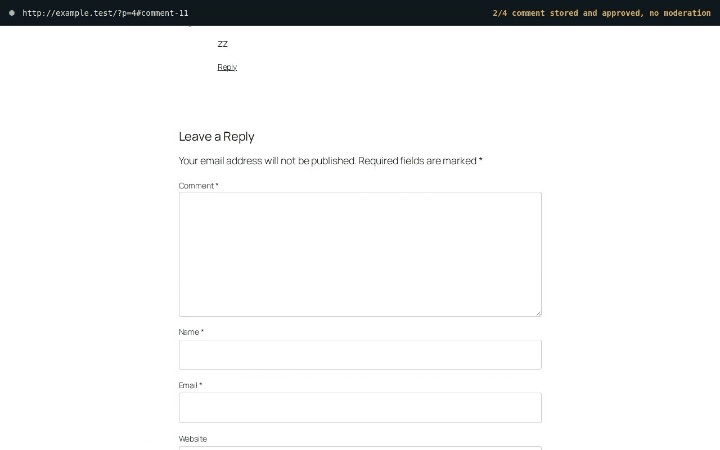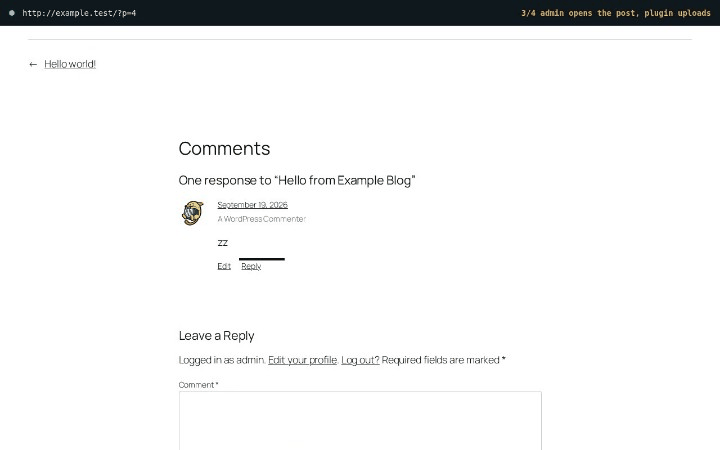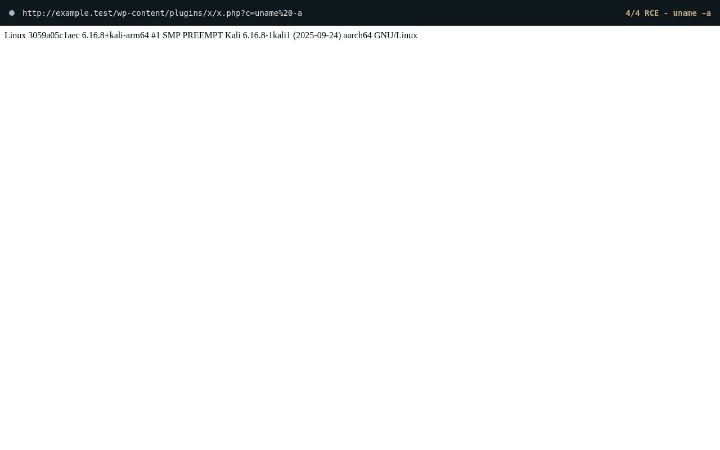
Currently, security researchers have confirmed no active exploitation in the wild. However, technical details and functional proof-of-concept code are now public. An unauthenticated attacker can submit a comment that executes malicious JavaScript in an administrator’s browser. When an administrator views the post, the script triggers without any further interaction. The script can then upload a malicious plugin package. Consequently, an attacker can gain full remote code execution on the underlying hosting server. This enables complete site takeover without needing any account credentials.
How The Attack Works
The Comment Rendering Pipeline
WordPress processes comments in two distinct phases. First, it cleans submitted text with the KSES HTML sanitizer. Later, it applies the comment_text filter chain during display rendering. As Muhammad explained, “WordPress sanitizes a comment when it is saved, using its HTML sanitizer (KSES), then formats it when it is displayed, using the comment_text filter chain.”
The vulnerability exists in the gap between these two processing stages. KSES allows blockquote tags with cite attributes. Crucially, the sanitizer permits newline characters inside those attributes. This behavior allows attackers to pass custom strings past initial input checks.
Insecure Filter Cascades
During output rendering, WordPress sends comment text through formatting filters such as wpautop. This function replaces newlines inside tags with temporary HTML comments. Then, wpautop wraps blocks of content in paragraph tags using regular expressions. As the researcher highlighted, “The key to this exploit is the newline (\n) in the cite attribute of, which causes an insecure cascading transformation in the filters.”
Because the regular expression stops at the first closing bracket, it breaks on the placeholder comment. This mistake injects an opening paragraph tag directly into the attribute string. Next, the wptexturize filter converts ordinary straight quotes into curly typographic quotes. However, wptexturize explicitly skips content inside code elements. By placing closing quotes inside code tags, an attacker preserves straight quotes. This structural misalignment forces the browser to treat subsequent text as real HTML attributes. The browser then executes event handlers such as autofocus and onfocus.
Escalating From XSS To RCE
The injected script runs within the active browser session of the reader. When a logged-in administrator opens the post, the code acts with administrative rights. The payload retrieves the plugin installer nonce from the WordPress administrative panel. Then, it sends an asynchronous request to upload a zip file containing a PHP web shell.
WordPress unpacks the archive directly into the plugins folder. Because the server stores these files in accessible directories, the attacker accesses the shell immediately. Stock WordPress configurations allow comments under default author identities without manual review. Therefore, threat actors can bypass approval queues and achieve remote execution instantly.
Affected Versions
This flaw impacts WordPress core versions prior to 7.1.1. It also exposes earlier unsupported releases across all branches down to version 4.7. Sites utilizing modern block themes or classic themes that process comment templates face direct risk. In a research report on the WordPress comment XSS exploit chain, analysts verified vulnerability on default installations.
Patch Or Mitigation Steps
WordPress released version 7.1.1 to fix this security defect. The engineering team updated the wpautop formatting logic with a quote-aware pattern. This modification prevents the regular expression from breaking inside attribute values. The developers also backported the fix to all branches down to version 4.7.36.
Administrators should update their WordPress sites to version 7.1.1 immediately. Additionally, site owners can enforce manual comment moderation. Under Discussion settings, require administrators to approve all incoming submissions before publication. Applying these defenses eliminates this critical WordPress stored XSS vulnerability.
Support Our Threat Intelligence
Find our vulnerability reports and weekly recaps helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
