 Do Son
Three LiteSpeed Cache vulnerabilities, including stored XSS flaws CVE-2026-113499 and CVE-2026-113500, affect 7M+ WordPress sites. Update to 7.9.2.
Stored XSS
An unpatched Shopware vulnerability, CVE-2026-104937, lets stored XSS steal admin tokens and lead to RCE in Shopware 6.7. Restrict media uploads now.
The WordPress 7.1.3 security update is a WordPress security release that fixes stored XSS, SQL injection and more. Update your site now.

Details and PoC exploit code for a critical WordPress stored XSS are public. Learn how CVE-2026-93485 enables RCE and patch WordPress today.
The Roundcube security update fixes 12 webmail flaws, including a zero-click stored XSS and an SSRF bypass. Update to 1.6.19 or 1.7.4 now.

A Confluence vulnerability, CVE-2026-21580, is a stored XSS flaw (CVSS 8.6) allowing unauthenticated attacks. A Jira flaw also patched. Update now.

Roundcube fixes a webmail RCE flaw and an SSRF filter bypass in versions 1.6.18 and 1.7.3. Update your mail server now.

A Ninja Forms vulnerability chain hits 600K+ sites. CVE-2026-65048 is an unauthenticated stored XSS rated CVSS 9.3. Update to 3.14.10 now.

A Roundcube zero-click XSS, CVE-2026-54433, lets an email run script with no click. Roundcube 1.7.2 also fixes a second stored XSS. Update now.
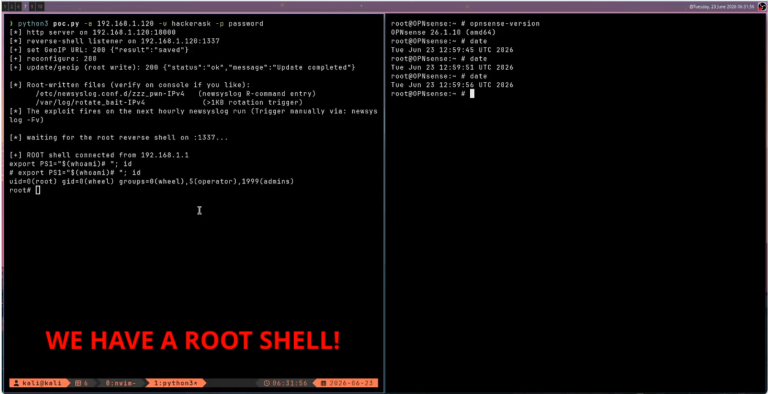
OPNsense root RCE flaws are public with PoC code. CVE-2026-57155 (9.9) chains an arbitrary file write to root. Patch 26.1.11 or 26.4.1p1 now.
Progress patched three MOVEit Transfer flaws, including a stored XSS bug (CVE-2026-11903). No exploitation is confirmed. Update now.

Three critical pgAdmin 4 vulnerabilities (CVE-2026-12046, CVE-2026-12048, CVE-2026-12045) risk XSS and RCE. Update to pgAdmin 4 9.16 now.

A major TinyMCE cross site scripting threat is uncovered. Patch this critical stored XSS vulnerability by updating your rich text editor now.

New Broadcom security updates fix critical VMware stored XSS bugs. Learn how these vulnerabilities affect Cloud Foundation and how to patch now.
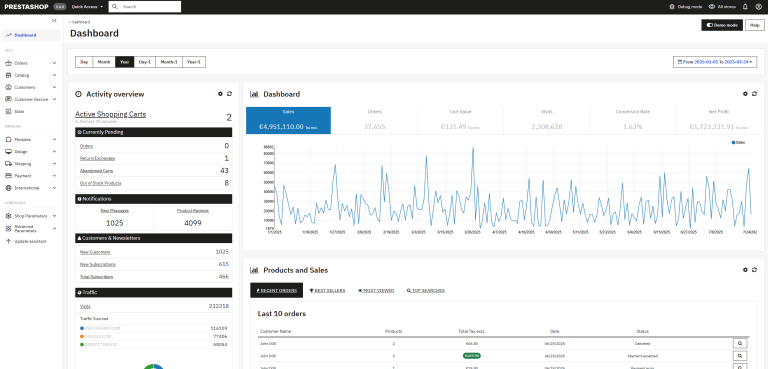
Urgent: PrestaShop patches a 9.3 severity XSS flaw (CVE-2026-44212) that allows unauthenticated attackers to hijack your store's back office. Update now!

Zabbix fixes high-severity XSS (CVE-2026-23926) and Oracle injection flaws. Don't let your monitoring tool become a backdoor—upgrade your Zabbix server now!

Unauthenticated attackers can hijack mailcow admin sessions via a critical CVSS 9.3 Stored XSS in Autodiscover logs. Patch to version 2026-03b immediately.

RustFS patches a critical 9.1 CVSS XSS flaw (CVE-2026-27822). Attackers can steal S3 credentials via a malicious file preview. Update to 1.0.0-alpha.83 now!

Samsung MagicInfo9 has critical flaws (CVSS 9.8) including hardcoded passwords and RCE. Update to v21.1090.1 immediately to secure your digital signage.

ConnectWise patches critical Stored XSS (CVE-2026-0695) in PSA Time Entry notes. Vulnerability allows session hijacking. Update to version 2026.1 immediately.
CISA warns of active exploitation of OpenPLC ScadaBR (CVE-2021-26829). This critical Stored XSS flaw puts SCADA systems at risk. Update now.

Apache SkyWalking patches a Stored XSS flaw (CVE-2025-54057) affecting versions 10.2.0 and older. Upgrade to v10.3.0 to secure your APM dashboards.