 Do Son
Update to Git 2.56.1 now to fix six Git security vulnerabilities, including CVE-2026-111760 and CVE-2026-105437 for code execution and heap bugs.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
Microsoft patches Outlook zero-day CVE-2026-124194, a spoofing flaw exploited in the wild and added to CISA KEV. Install the November 2026 updates.
Fortinet fixes eight critical vulnerabilities, including FortiManager RCE CVE-2026-126170 (CVSS 9.8). Fortinet critical vulnerabilities also hit FortiOS.
Update to version 30.0 now to fix three Bitcoin Core vulnerabilities, including CVE-2025-62861, CVE-2025-62860, and CVE-2025-62859 affecting nodes.
Microsoft November 2026 Patch Tuesday fixes 1,093 vulnerabilities, including an exploited Outlook zero-day, CVE-2026-124194, and a CVSS 10.0 Entra flaw.
Update self-managed servers to 19.5.4 now to fix the critical GitLab heap overflow flaw CVE-2026-105437 that allows command execution in Gitaly.
Update Synology DiskStation Manager now to patch CVE-2026-76954, CVE-2026-85101, and 25 other flaws allowing arbitrary file writes and crashes.
Zoom Workplace for Windows 7.1.8 fixes CVE-2026-108186 (CVSS 9.6) and CVE-2026-108187, two escalation of privilege flaws. Update now.
Ivanti security advisories fix 13 flaws, including Ivanti Endpoint Manager RCE CVE-2026-121653 (CVSS 9.8) and CSA bug CVE-2026-121683.
Details and proof-of-concept steps for five mailcow vulnerabilities are public, including a CVSS 9.1 cross-tenant RCE. Update to 2026-11.
Composer 2.11.2 and 2.2.32 fix three Composer vulnerabilities, including command execution via a crafted composer.lock file (CVSS 8.8).
The November 2026 OpenSSL security advisory fixes five Low-severity bugs in OpenSSL QUIC, AES-GCM-SIV and CMS. Releases are due December 1.
Apache Commons Codec 1.23.0 addresses CVE-2026-119078 and CVE-2026-124077, while Apache HTTP Server 2.4.70 fixes a heap buffer overflow.
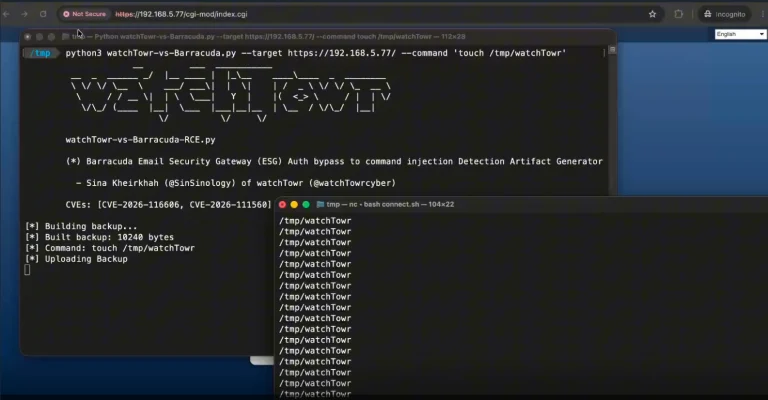
Attackers exploit a Barracuda ESG vulnerability chain (CVE-2026-116606, CVE-2026-111560) for root RCE after a proof-of-concept exploit went public.
Update Progress WS_FTP Server to 2025.0.5 now to patch CVE-2026-115338, CVE-2026-115341, and three other high-severity security vulnerabilities.
Patch critical Mongoose security flaws CVE-2026-125120 (CVSS 9.8) and CVE-2026-125117 affecting 4.8 million weekly npm users against NoSQL injection.
November SAP Security Patch Day fixes 38 CVEs, including nine Critical SAP NetWeaver, Web Dispatcher and Gateway flaws rated up to CVSS 10.0.
CERT/CC details six FrodoBots EarthRover vulnerabilities, including root remote code execution via MQTT. Patch status, risks and mitigations.
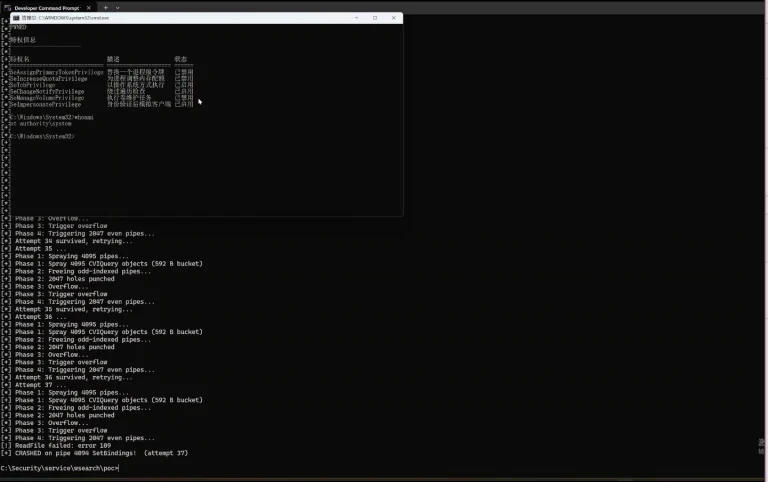
A proof-of-concept exploit for the Windows Search vulnerability CVE-2026-50679 is public. The heap overflow lets local users gain elevated privileges.
18 Apache Airflow vulnerabilities, including Celery code execution CVE-2026-68982, are fixed in Airflow 3.4.0, plus two Apache Storm flaws.
Logto vulnerabilities allow account takeover via Apple sign-in, MFA bypass and SAML login bypass. Upgrade to Logto 1.46.0 and patched packages now.