 Do Son
Gradle 9.9.1 and 8.14.7 fix three Gradle vulnerabilities, including a CVSS 9.3 version catalog code injection that runs during builds and IDE sync.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
Mitel fixes three MiVoice MX-ONE vulnerabilities, including a CVSS 9.4 authentication bypass and command injection. Apply 8.2 SP1 HF2 now.
Plone fixes an anonymous Plone remote code execution chain rated CVSS 9.8. Update to 6.2.3, 6.1.6 or 6.0.16, or install the Plone hotfix.
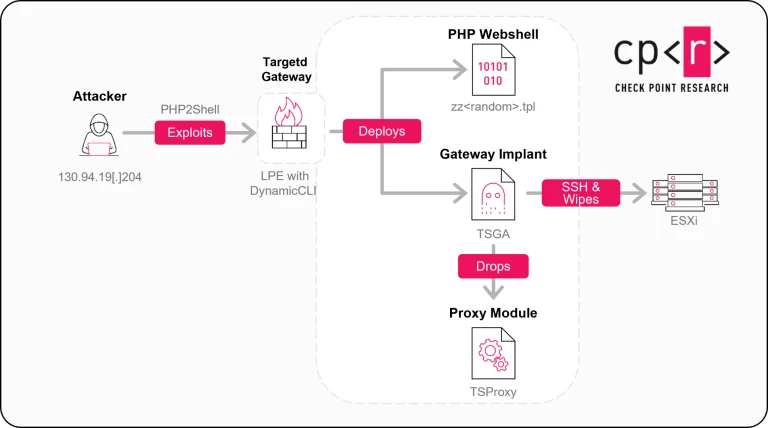
Check Point Gateway vulnerability CVE-2026-123039 exploited with PHP2Shell to gain root, plant backdoors and wipe ESXi. Patch to R82.20 Take 14.
Citrix NetScaler vulnerabilities fixed: CVE-2026-120868 hits default setups, CVE-2026-120869 bypasses Console login. Upgrade to 14.1-73.57 now.
A public exploit for CVE-2026-80521, an AF_UNIX use-after-free, enables Linux kernel privilege escalation. Fixed in 7.1.10, 6.12.111 and 7.2.
Telegram fixes a Telegram Android RCE flaw after V12 showed remote code execution through a bot message. No CVE yet. Update the Android app now.
Google Chrome security update 157.0.8103.78 fixes 83 flaws, including five Critical use-after-free bugs such as CVE-2026-126885. Update Chrome now.
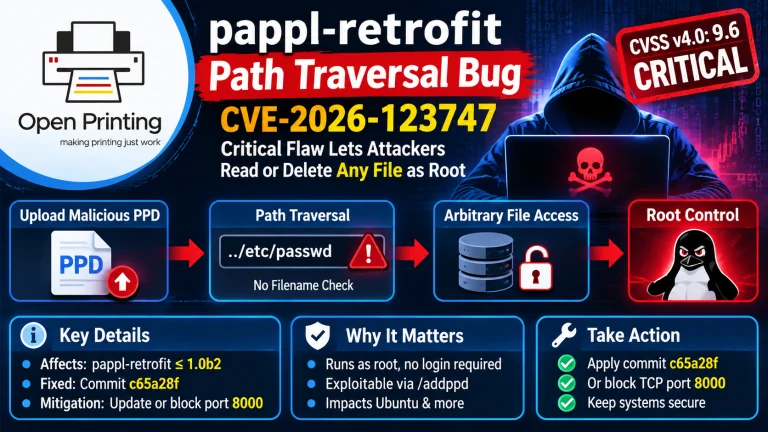
Full details and PoC exploit code for the critical pappl-retrofit path traversal flaw CVE-2026-123747 are now public. Apply commit c65a28f right away.
Zoho fixes eight ManageEngine vulnerabilities in DDI Central and ADAudit Plus, including Cisco router command injection and SQL injection flaws.
Go 1.27.4 and 1.26.11 deliver 12 Go security fixes, blocking cgo code execution at build time (CVE-2026-97033) and an HTTP/1 server crash.
Node.js fixes 17 bugs, including Node.js HTTP/2 vulnerabilities and a TLS heap leak (CVE-2026-123864). Update to 26.13.1, 24.22.3 or 22.23.5.
Update Apache HTTP Server to 2.4.71 now to fix CVE-2026-119618, a critical mod_http2 remote code execution flaw, alongside CVE-2026-106023.
N-able patches N-central vulnerabilities in 2026.4 HF2 as attackers scan with the public proof-of-concept exploit. Seven CVEs, up to CVSS 9.3.
The unpatched worse_query iOS sandbox escape flaw allows malicious apps to bypass container restrictions and siphon crypto wallet data and photos.
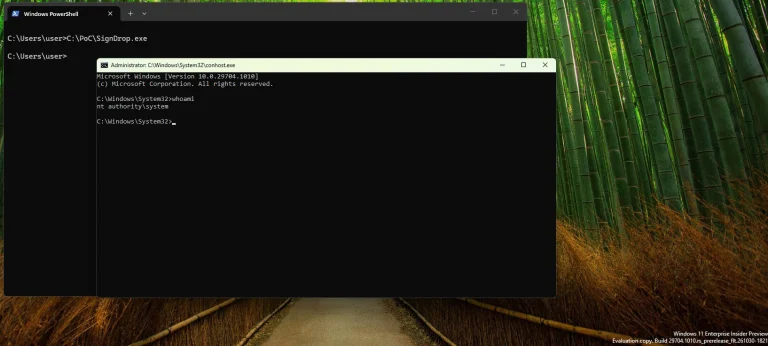
SignDrop, an unpatched Windows CLFS zero-day, now has a public proof-of-concept exploit that gives standard users SYSTEM privileges. No patch yet.
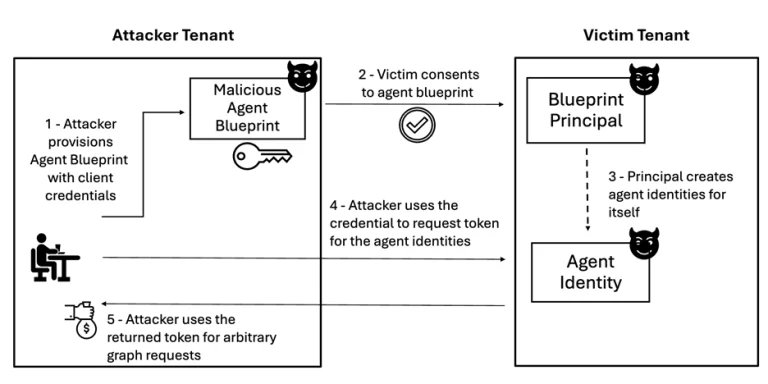
Proofpoint researchers detailed the BluePhishing attack Entra Agent ID technique, showing how malicious AI agent blueprints enable OAuth consent abuse.
Update MongoDB Server to 9.0.7 now to fix CVE-2026-118383, CVE-2026-120808, and 24 other flaws causing code execution, memory leaks, and crashes.
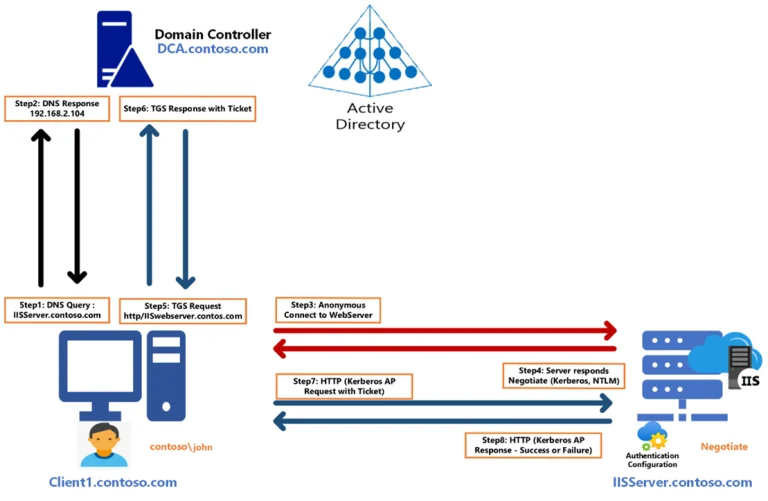
Five critical Windows vulnerabilities rated CVSS 9.8 hit Windows Kerberos, LDAP, DNS, DHCP and iSCSI. Patch domain controllers and servers first.
CISA KEV additions on November 10 cover six Known Exploited Vulnerabilities in Outlook, Chrome, Barracuda ESG, Cisco BroadWorks and Openwave.
Axis fixes 15 flaws, led by AXIS Camera Station bug CVE-2026-13312 (CVSS 9.9) that could compromise a system. AXIS OS updates also released.
Microsoft fixes a CVSS 9.9 SharePoint Server vulnerability, a 9.9 Azure DevOps Server RCE and a 9.8 SQL Server flaw in November 2026 Patch Tuesday.