Citrix NetScaler CVE-2026-88772 Exploited in the Wild as PoC and Full Details Go Public
 Do Son
TL;DR
CVE-2026-88772 is a pre-authentication memory overflow in Citrix NetScaler ADC and Gateway. Attackers exploited it in the wild as a zero-day, and CISA added it to its Known Exploited Vulnerabilities catalog on September 27, 2026. watchTowr has now published full technical details and proof-of-concept exploit code, which raises the risk for unpatched appliances. It carries a CVSS 4.0 score of 9.5.
- Product: Citrix NetScaler ADC
- Vulnerabilities: 2 flaws (CVE-2026-88772, CVE-2026-88771)
- Highest severity: 9.5 (Critical · CVSSv4)
- Worst impact: Memory overflow leading to Remote Code Execution or Denial of Service
- Status: 2 exploited; patches available
- Exploit Intel (PatchThis): 2 of 2 confirmed
- Action: Update to 14.1-73.37, 13.1-64.23, 14.1-73.37 FIPS, 13.1.37.279 FIPS and NDcPP now
| CVE | CVSS (CVSSv4) | Type | Fixed in | Status |
|---|---|---|---|---|
| CVE-2026-88772 | 9.5 | Memory overflow leading to Remote Code Execution or Denial of Service | 14.1-73.37, 13.1-64.23, 14.1-73.37 FIPS (+1) | Exploited |
| CVE-2026-88771 | 9.5 | A remote code execution exists due to improper input validation, which can allow an unauthenticated attacker to execute arbitrary commands | 14.1-73.37, 13.1-64.23, 14.1-73.37 FIPS (+1) | Exploited |
Track every Citrix CVE the moment it's exploited.
Get free email alertsWhy CVE-2026-88772 Matters
NetScaler appliances sit at the network edge and terminate VPN traffic. A pre-auth flaw there needs no login, so any exposed device is reachable. The bug also affects a default setting. DTLS is enabled by default on VPN virtual servers, unless an admin turned it off. Because attackers used it as a zero-day, defenders started behind.
How the Attack Works
The flaw lives in how NetScaler reassembles DTLS handshake data. DTLS runs TLS over UDP, and a handshake message can arrive split across many fragments. NetScaler collects those fragments, then copies the rebuilt message into a small fixed-size internal buffer.
The problem is a missing size check. According to the watchTowr technical analysis, the vulnerable copy routine did not confirm that the reassembled data fit before writing it. A crafted sequence of fragments can therefore make the rebuilt message far larger than the buffer holds. The write then spills past the buffer into adjacent memory. That memory corruption can crash the device or lead to remote code execution. The fixed build adds the missing check and rejects oversized data.
This requires no authentication. An attacker only needs to complete the standard DTLS cookie exchange, which proves reachability but logs nobody in.
Public Proof-of-Concept and Exploitation Status
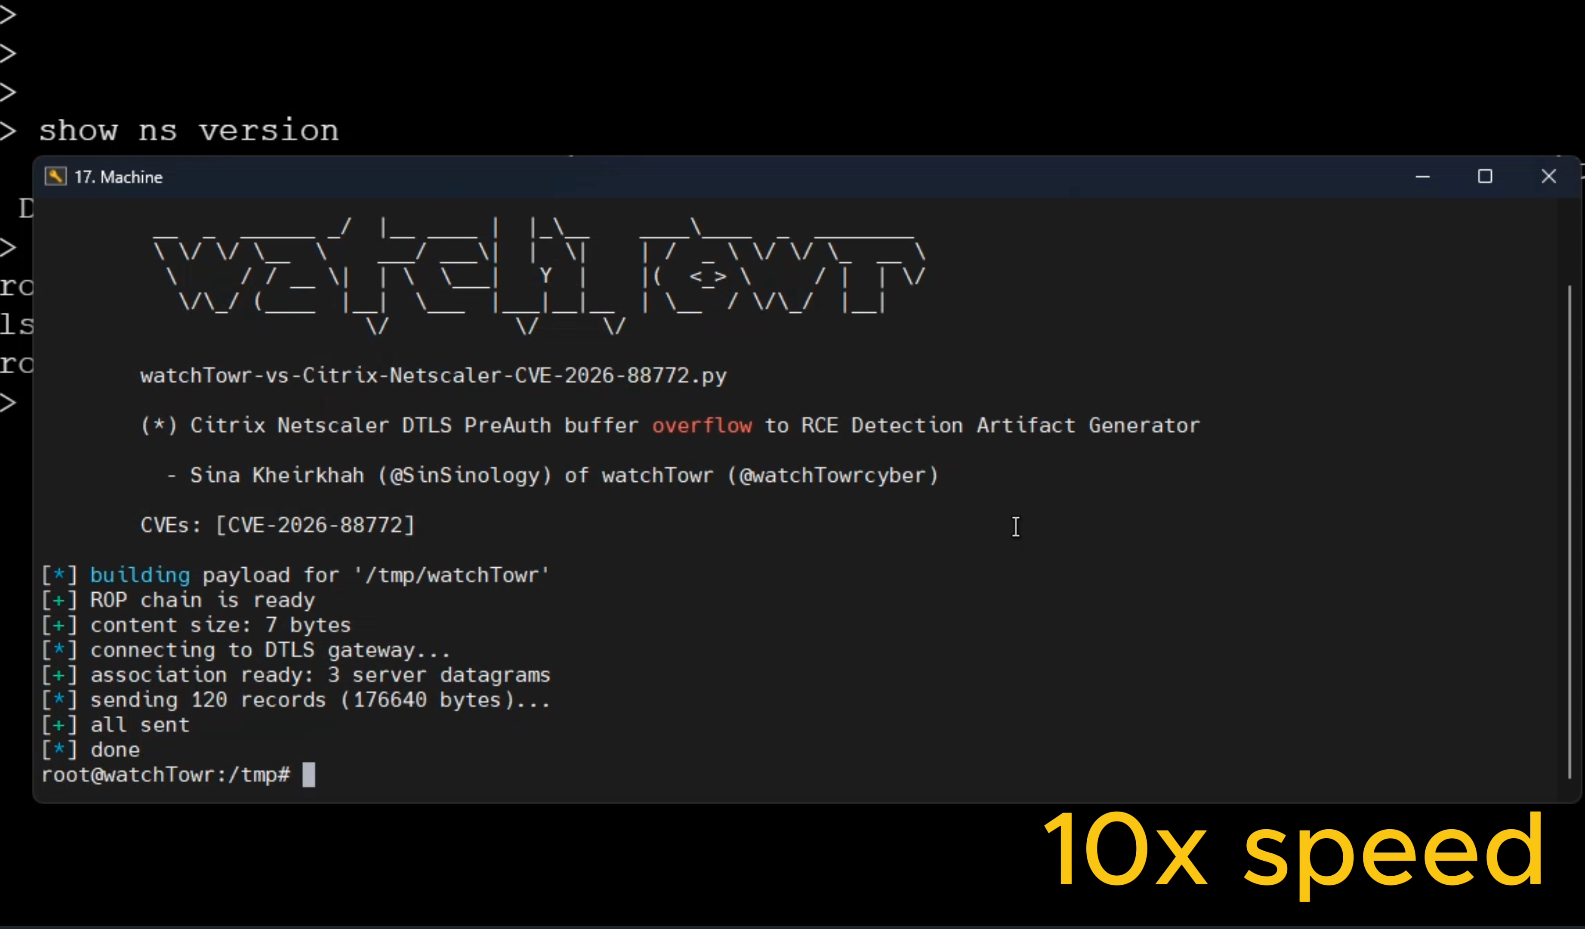
The details are no longer theoretical. watchTowr released its proof-of-concept on GitHub alongside the write-up. CISA confirmed active exploitation when it listed both CVE-2026-88772 and CVE-2026-88771 in the Known Exploited Vulnerabilities catalog. Federal agencies must patch on a set deadline, and every other operator should treat exposure as urgent.
Affected Versions
CVE-2026-88772 is one of eight flaws Citrix fixed in bulletin CTX697096. The companion critical bug, CVE-2026-88771, allows unauthenticated command execution and affects the default configuration. Both were exploited in the wild. Older releases across the 14.1 and 13.1 lines, including FIPS builds, are affected.
Patch and Mitigation Steps
Update now. The Citrix security bulletin CTX697096 lists these fixed versions:
- NetScaler ADC and Gateway 14.1-73.37 and later
- NetScaler ADC and Gateway 13.1-64.23 and later
- NetScaler ADC 14.1-FIPS 14.1-73.37 FIPS and later
- NetScaler ADC 13.1-FIPS and 13.1-NDcPP 13.1-37.279 and later
There is no full workaround for CVE-2026-88772, so patching is the fix. Disabling DTLS reduces exposure to this one bug, but CVE-2026-88771 still affects every deployment. After upgrading, review devices for signs of prior compromise, since these flaws were used before patches shipped.
Support Our Threat Intelligence
Find our vulnerability reports and weekly recaps helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
