 Do Son
Our Q3 2026 CVE report tracks 100 new CISA KEV catalog flaws, up 33%. Microsoft leads, and 26% were exploited within a week of disclosure.
Known Exploited Vulnerabilities
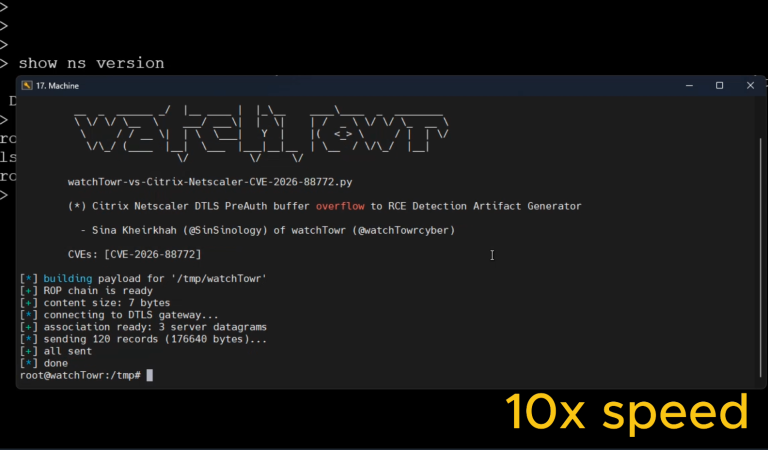
CVE-2026-88772, a Citrix NetScaler DTLS memory overflow, is exploited in the wild. A watchTowr PoC and full details are now public. Patch NetScaler now.
This CVE weekly report tracks 3,179 new CVEs and 9 exploited vulnerabilities added to CISA KEV, from Ray and MLflow to VMware and Apple.
CISA added four exploited flaws to its KEV Catalog, hitting SharePoint, VMware vCenter, macOS, and Windows IKE. Patch by August 21.
CISA KEV additions on July 27 flag two known exploited vulnerabilities: Arista VeloCloud CVE-2026-16812 and FortiOS CVE-2025-68686. Patch both now.
CISA added four flaws to its KEV catalog, including WordPress RCE (CVE-2026-63030) and Langflow RCE (CVE-2026-0770). All are exploited in the wild.
CISA added two flaws to its KEV Catalog: a Cisco Unified CM SSRF bug and a PTC Windchill RCE. Federal agencies must patch by June 28, 2026.
The CISA active exploit catalog now includes three known exploited vulnerabilities from Cisco, Arista, and Chromium. Update your systems today.

CISA expands its active exploit catalog with critical gateway flaws in BerriAI LiteLLM and Check Point configurations. Patch immediately.
CISA adds Microsoft SharePoint spoofing (CVE-2026-32201) and legacy Office RCE (CVE-2009-0238) to its KEV Catalog. Remediation deadline: April 28, 2026.
CISA adds three new vulnerabilities to its KEV Catalog, including flaws in the Linux kernel, Android Runtime, and Sitecore CMS. All are being actively exploited.

CISA adds two flaws to its KEV Catalog: a TP-Link factory reset flaw and a WhatsApp zero-click vulnerability used in targeted spyware attacks. Patching is urgent.

Urgent warning: Exploited vulnerability in Palo Alto Networks PAN-OS firewall software (CVE-2024-3393) allows attackers to disable network security.
Get the latest updates on exploited security vulnerabilities. Find out how to protect your systems from the newly added threats.

The first vulnerability, tracked as CVE-2023-43208 (CVSS 9.8), affects NextGen Healthcare's Mirth Connect.
CISA has added seven new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, indicating evidence of active exploitation.