 Do Son
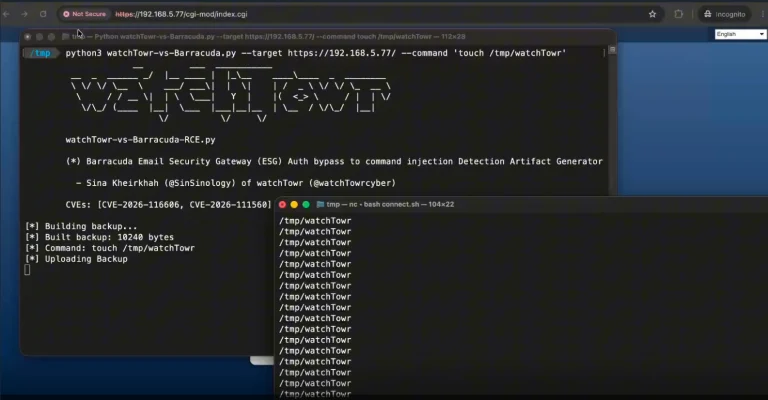
Attackers exploit a Barracuda ESG vulnerability chain (CVE-2026-116606, CVE-2026-111560) for root RCE after a proof-of-concept exploit went public.
watchTowr
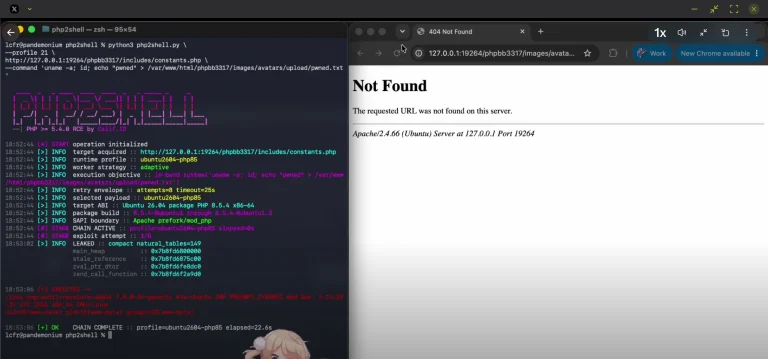
Cloudflare reports early attacks on two critical PHP flaws ahead of the PHP security release fixing remote code execution bugs CVE-2026-109618.
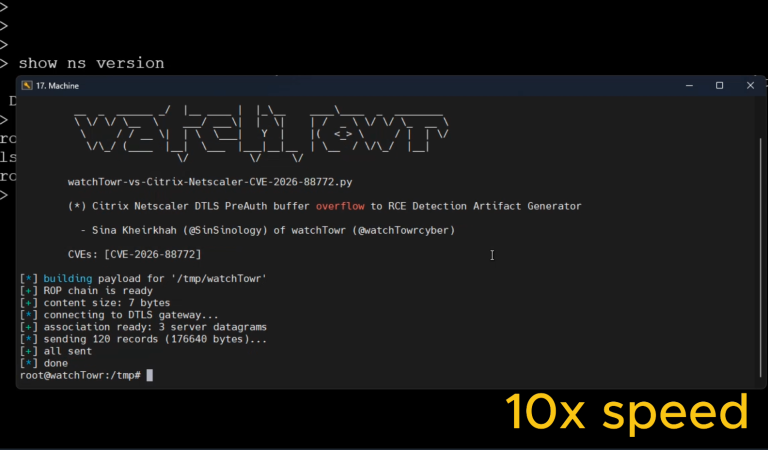
CVE-2026-88772, a Citrix NetScaler DTLS memory overflow, is exploited in the wild. A watchTowr PoC and full details are now public. Patch NetScaler now.
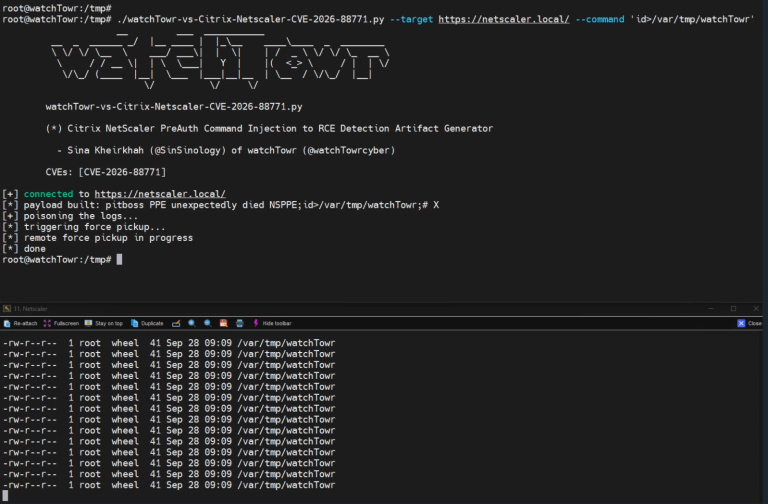
CVE-2026-88771 is a Citrix NetScaler command injection exploited in the wild. Details and a PoC are public. Patch NetScaler to 14.1-73.37 now.
Two Citrix NetScaler zero-day RCE flaws are under active exploitation. Citrix confirmed CVE-2026-88771 and CVE-2026-88772 and shipped patches. Update now.

A public PoC for CVE-2026-64849, an unauthenticated MLflow SSRF (CVSS 9.3), is now live. watchTowr reports exploitation attempts. Patch to 3.15.0.

PoC exploit code for CVE-2026-8452, a Citrix NetScaler pre-auth RCE, is now public. The SAML heap overflow grants root. Patch now.

Progress ShareFile hit by critical 9.8 CVSS RCE flaws (CVE-2026-2699). Unauthenticated attackers can hijack configuration and execute code. Update to v5.12.4!
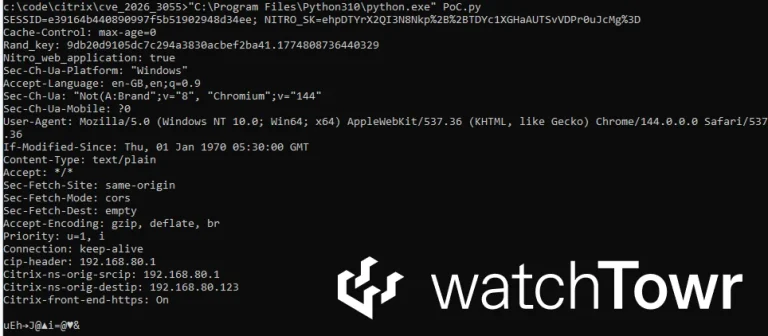
CISA adds Citrix NetScaler CVE-2026-3055 to KEV. This 9.3 CVSS flaw "bleeds" admin sessions via SAML. Federal agencies must patch by April 2, 2026.

Critical SolarWinds Web Help Desk flaws (CVSS 9.8) allow unauthenticated RCE and auth bypass. Hardcoded credentials also found. Patch immediately.

A zero-day authentication bypass flaw (CVE-2025-54309) in CrushFTP is being actively exploited in the wild. A PoC is available, and an urgent patch is required.