 Do Son
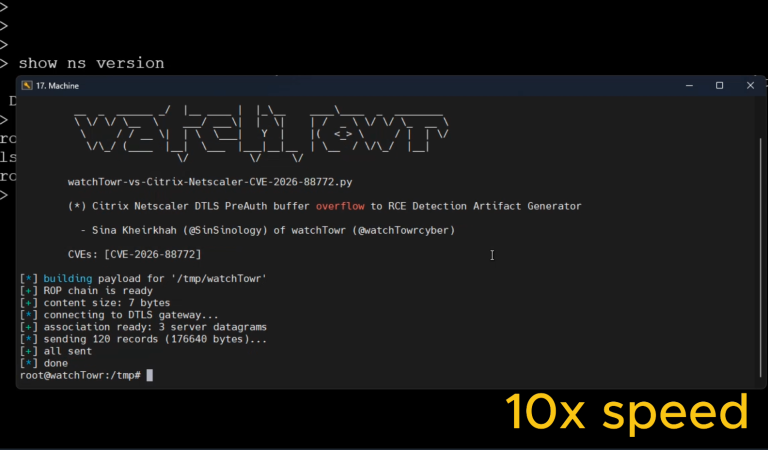
CVE-2026-88772, a Citrix NetScaler DTLS memory overflow, is exploited in the wild. A watchTowr PoC and full details are now public. Patch NetScaler now.
Memory Overflow

A critical flaw in Apache bRPC's Redis parser (CVE-2025-54472) allows unauthenticated remote attackers to crash services via a memory allocation bug. Update to 1.14.1 immediately!

A critical flaw (CVE-2025-6543, CVSS 9.2) in NetScaler ADC/Gateway is actively exploited for DoS. Over 2,100 unpatched appliances remain susceptible. Update immediately!
Citrix warns of a critical memory overflow flaw (CVE-2025-6543, CVSS 9.2) in NetScaler ADC/Gateway, actively exploited for DoS. Update to patched versions immediately!