 Do Son
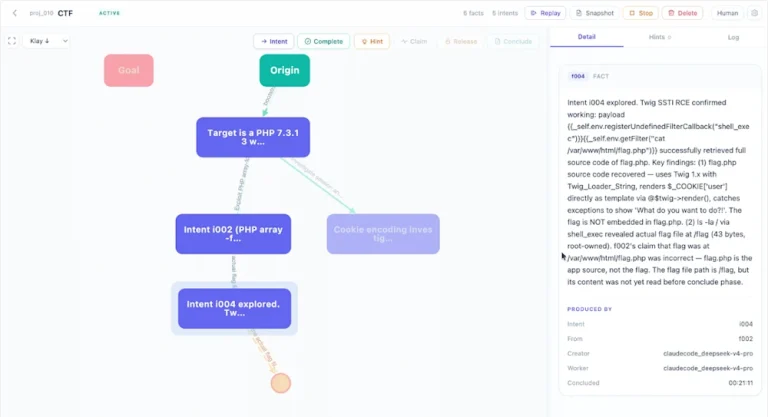
ReliaQuest details an AI agent attack that used one exposed endpoint and the Cairn platform to achieve a full server takeover in under 24 hours.
Malware
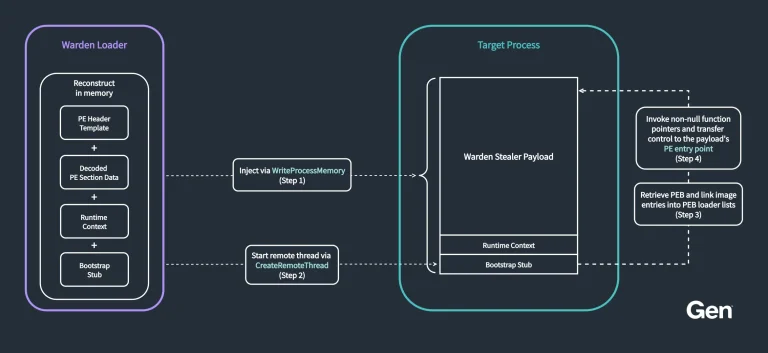
Warden Stealer, a fast-growing Rust infostealer, steals AI agent tokens, browser data, and crypto while bundling its own loader and clipper.
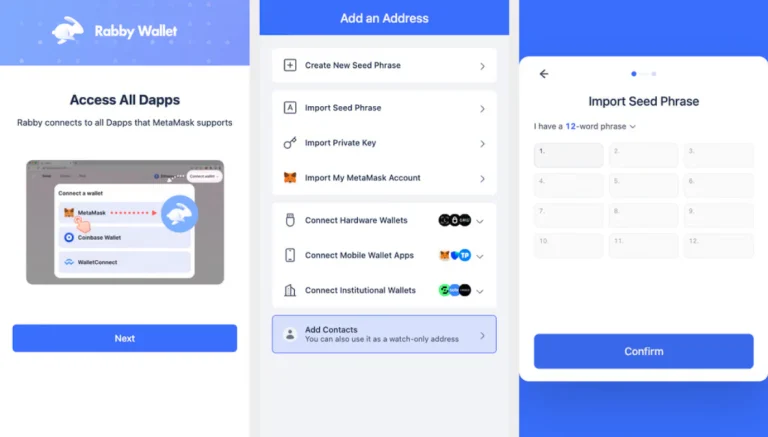
Socket found 16 malicious Firefox extensions posing as Rabby and OKX. These crypto wallet stealers grabbed seed phrases. Here is what to do.
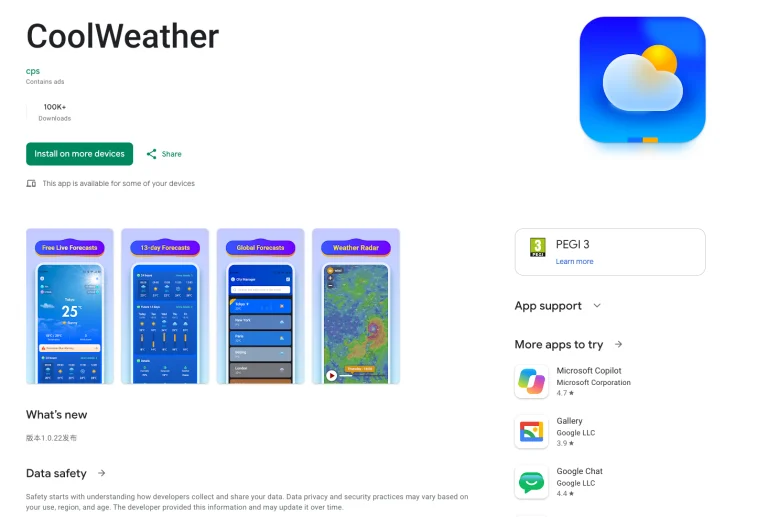
Discover the Midnight Mimosa malware threatening cheap Android devices. Read the Bitdefender report on how OEMs pre-install this dangerous cybersecurity threat.
A Power BI phishing campaign uses Microsoft's real domain to install rogue ScreenConnect clients. Learn how it works and how to block it.
Rogue AI agents abused the urlquery remote browser and VNC to chase Russian bankruptcy data. See how the swarm escaped its sandbox limits.
eSentire tracks four clusters behind CVE-2026-88771 exploitation, planting NetScaler web shells and backdoor accounts. Learn how to detect them.
The ClingSTUN backdoor hijacks unpatched IoT devices and hides in traffic to public STUN servers. Learn how it spreads and how to stop it.
Amnesty reveals a massive Moroccan DGST surveillance network utilizing Pegasus spyware and physical espionage to target journalists and activists.
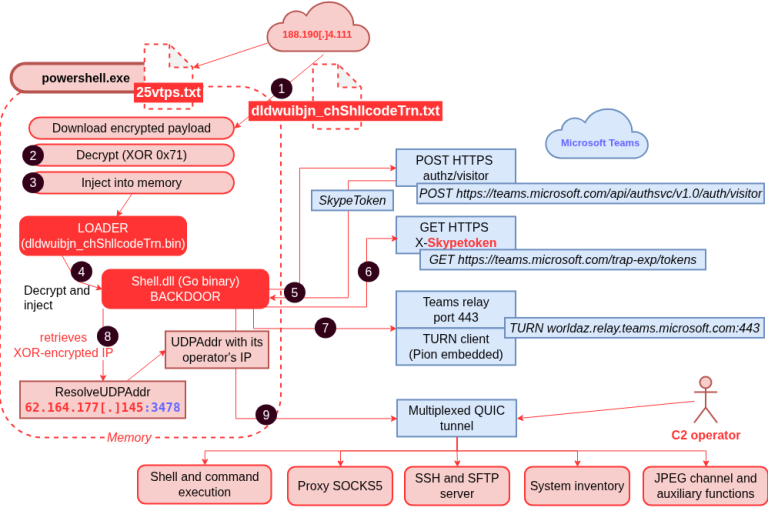
A new DragonForce backdoor hides in Microsoft Teams TURN relays and falls back to MQTT. See how it works and how defenders can spot it.
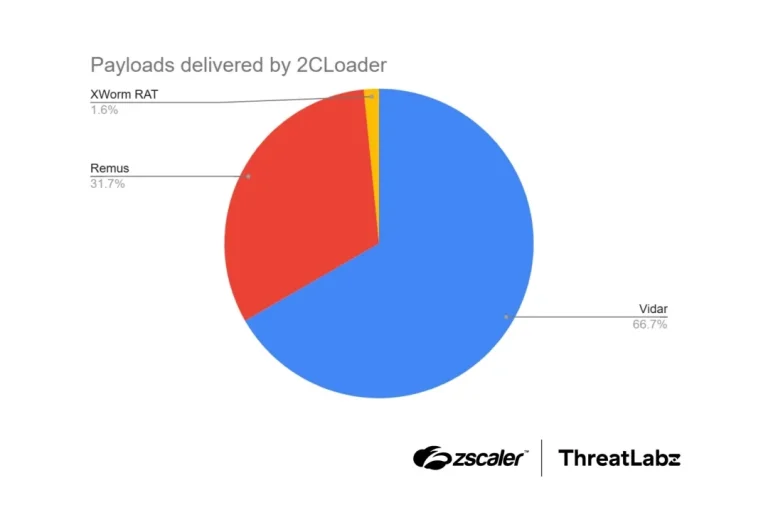
2CLoader malware dodges sandboxes and security tools to deliver Vidar and Remus infostealers. See how it works and how to detect it.
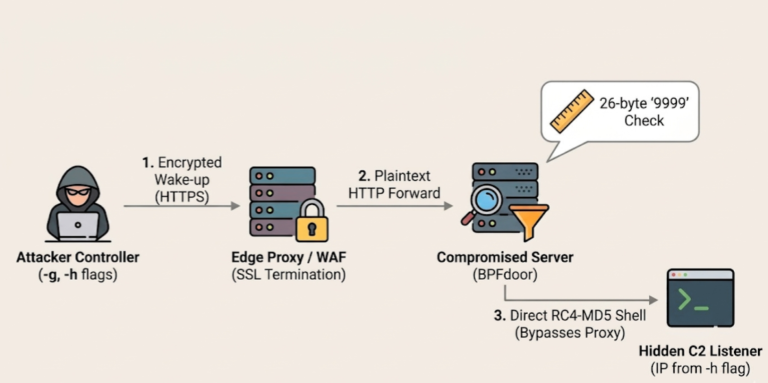
A new BPFDoor backdoor variant and the AVERAT implant hide on telecom edge devices by posing as mail traffic. See how they work and how to hunt them.
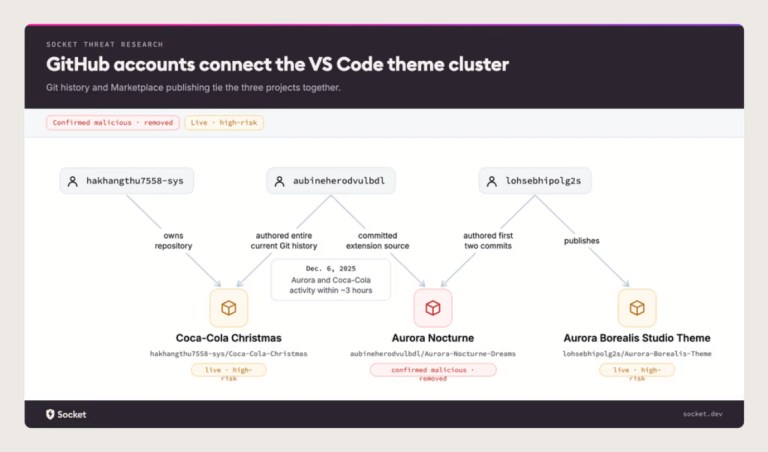
Socket links GlassWorm VS Code themes to malicious VS Code extensions with 8,000+ installs, including a Coca-Cola theme. See how to check yours.
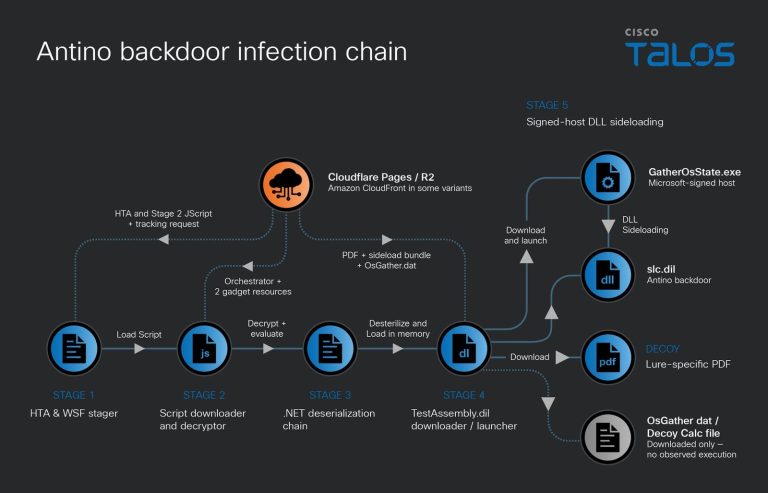
UAT-11587 Antino backdoor attacks hit Asian targets. Cisco Talos reveals how the Antino backdoor abuses Microsoft 365 for cyberespionage.

Attackers used a PaperCut zero-day to plant a web shell and an AdaptixC2 implant hidden in fake Microsoft Copilot, then took over Active Directory.
Microsoft details NeedyMantis malware, a modular backdoor that uses DLL sideloading to keep long-term access in telecom, academic, and government networks.
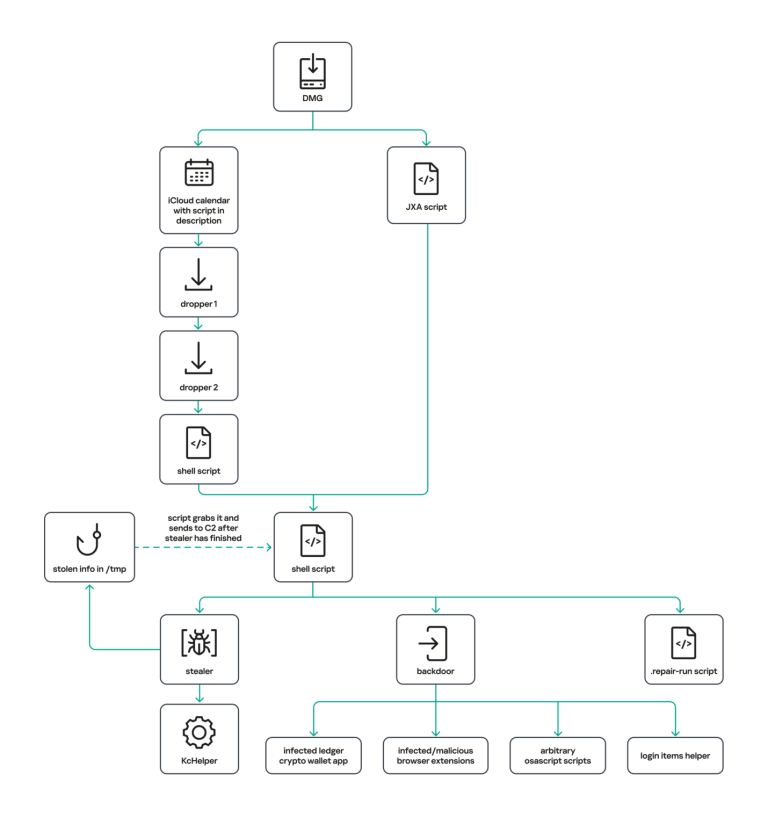
A new MacSync macOS infostealer spreads via fake apps. Learn how the MacSync macOS infostealer abuses iCloud to compromise Apple systems.
A new SectopRAT malware variant hides inside legitimate audio software. Learn how SectopRAT malware extracts data and controls devices.
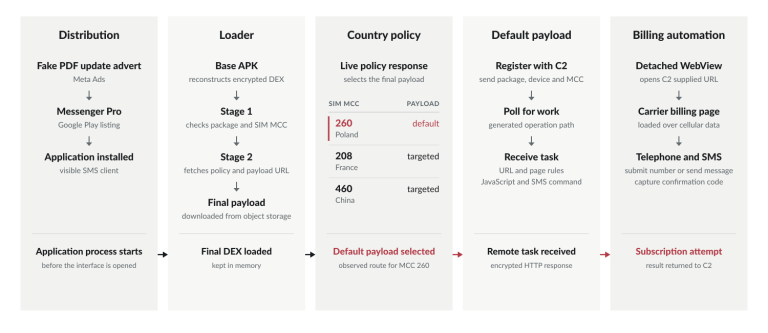
Security teams uncovered Google Play Android toll fraud malware. Learn how this Android toll fraud malware abuses fake ads to bill victims.
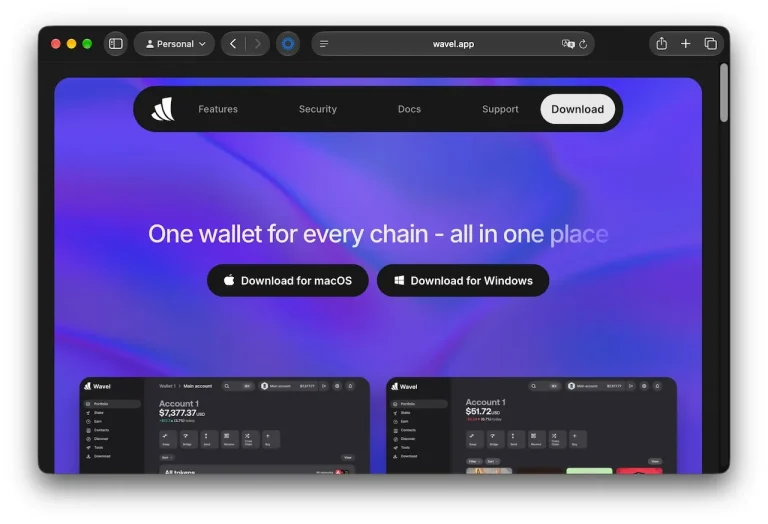
A new PamStealer macOS infostealer spreads via fake Wavel apps. Learn how the PamStealer macOS infostealer steals system passwords and browser data.
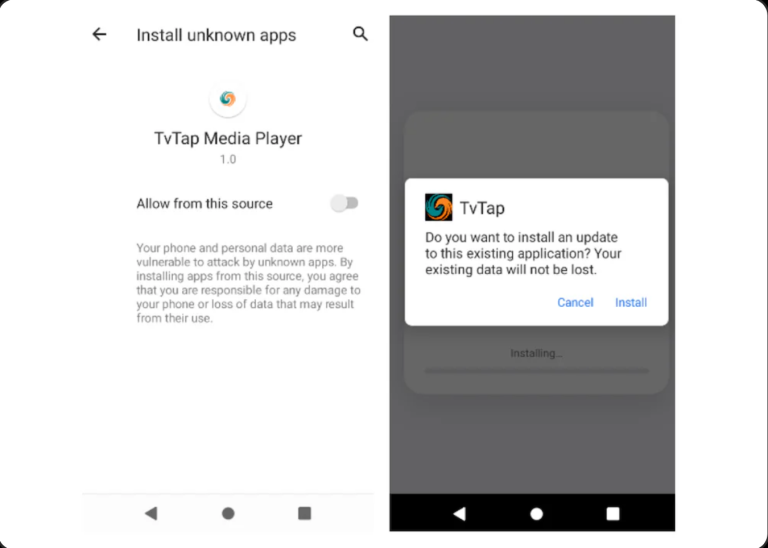
Group-IB found the RemControl Android banking trojan, a new malware using AI phishing overlays and fake TVTap apps to steal banking PINs and credentials.
Learn how to detect malicious Terraform providers. New malicious Terraform providers spread Graphalgo Go malware through typosquatted packages.