 Do Son
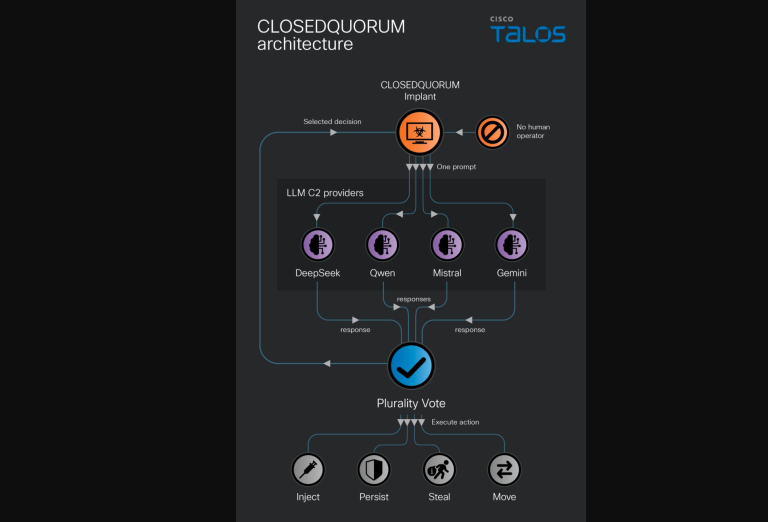
Cisco Talos discovered autonomous CLOSEDQUORUM AI malware. The CLOSEDQUORUM AI malware uses multiple LLMs to guide cyberattacks independently.
Malware
Wordfence uncovered stealthy WordPress must-use plugin malware. Learn how this WordPress must-use plugin malware abuses EtherHiding to steal secrets.

Learn how the new TASK#STOMP PowerShell backdoor steals data. The TASK#STOMP PowerShell backdoor abuses native Windows tools for persistence.
Discover the latest Vidar information stealer obfuscation tactics. ThreatLabz reveals how the malware uses a virtual machine and custom stream ciphers.
Discover the critical MemTensor MemOS compromise details. This MemTensor MemOS compromise targets AI developers via malicious npm and PyPI packages.
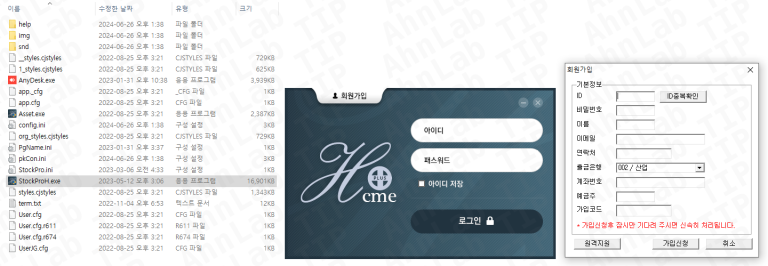
Fraudulent investment groups are using the UBP Asset private HTS malware to distribute KRSID ransomware. Learn how to protect your trading accounts today.
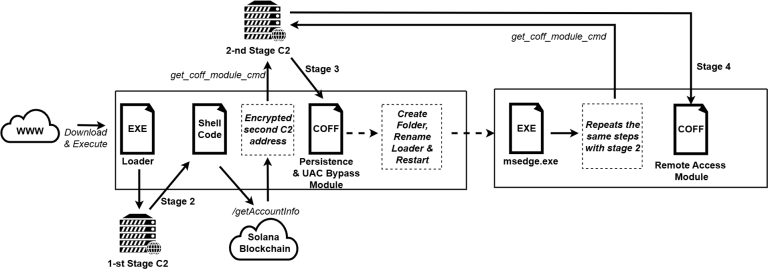
Learn how the MovieReaper malware compromises torrents. Experts warn that MovieReaper malware torrent attacks use Solana blockchain for command and control.
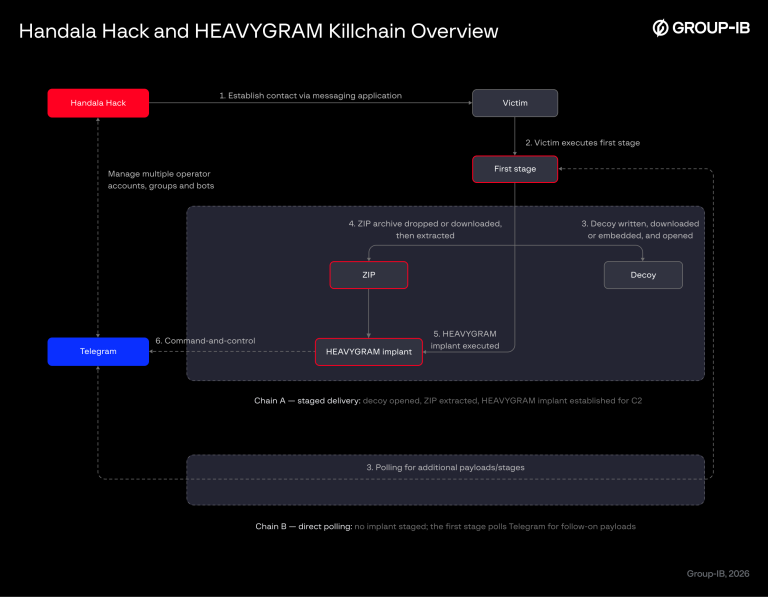
Group-IB uncovered Iranian HEAVYGRAM malware campaigns. The HEAVYGRAM malware abuses Telegram channels for command execution and data theft.
Learn how the LLM-generated PhantomRaven information stealer targets developers. The PhantomRaven information stealer uses npm to hijack CI/CD secrets.
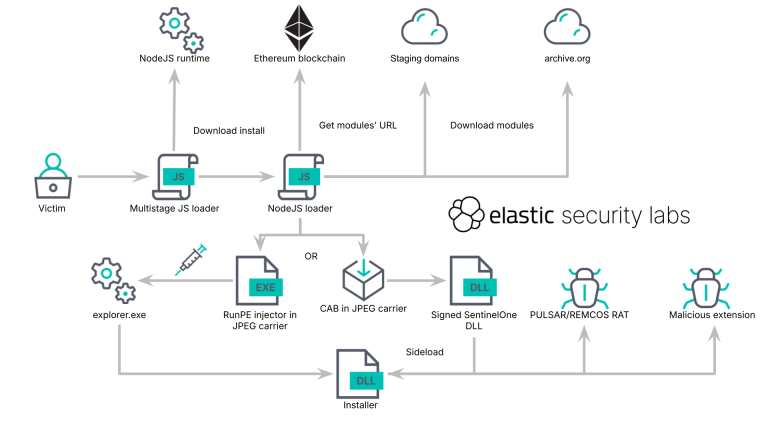
Learn how Brazilian KREMLIN banking malware steals credentials using fake browser extensions. Elastic Security Labs details the KREMLIN banking malware.
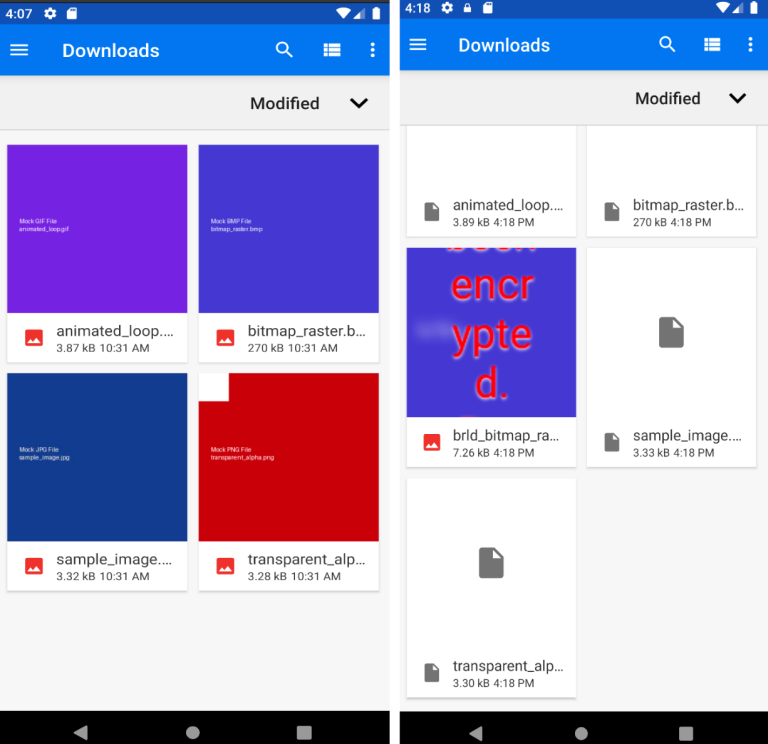
Zimperium zLabs discovered Mantax Otax Android malware, a fierce Indonesian mobile ransomware integrating spyware to hijack, record, and extort victims.
Discover how the new SloppyRAT malware uses a ClickFix infection chain to establish remote access for ransomware attacks, evading detection.
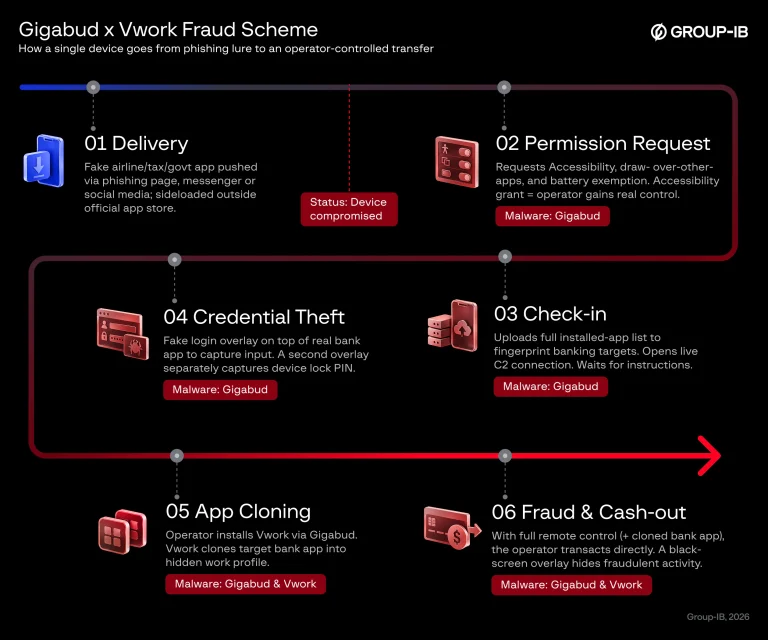
Group-IB uncovered how the Gigabud Vwork Android malware chain clones apps. Discover how Vwork Android malware evades bank detection.
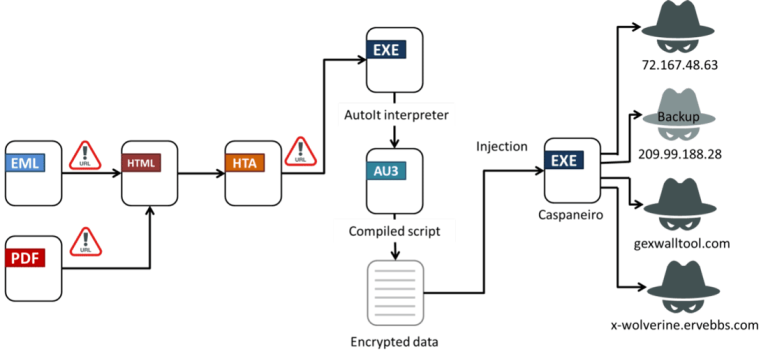
A new Casbaneiro banking trojan campaign hits Latin America. Learn how the Casbaneiro banking trojan evades detection and targets bank logins.
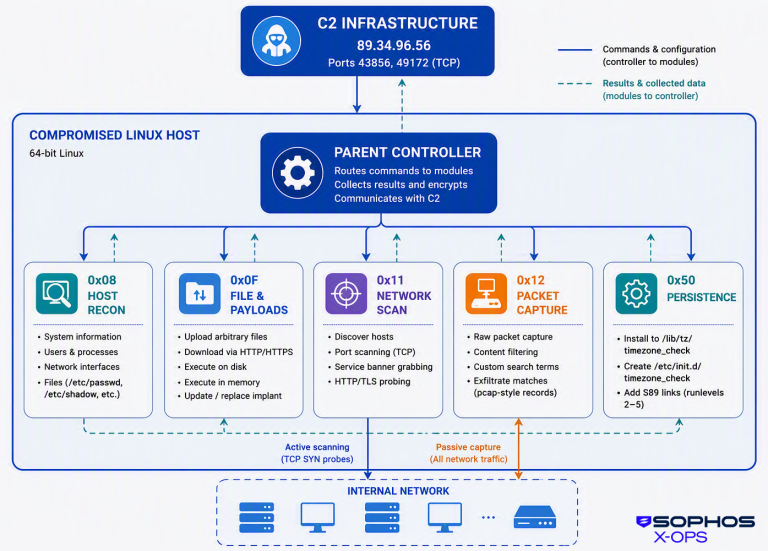
Sophos CTU researchers discovered a new 64-bit Linux variant of the Cyclops Blink malware targeting Cisco FMC devices, featuring advanced network scanning.
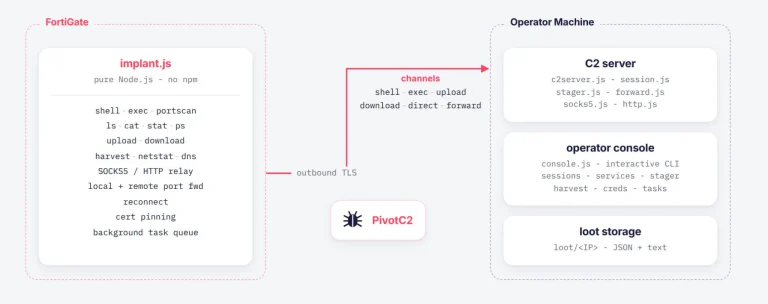
Discover how the PivotC2 FortiGate RAT uses CVE-2025-25249 exploitation to harvest credentials and tunnel traffic across corporate network environments.
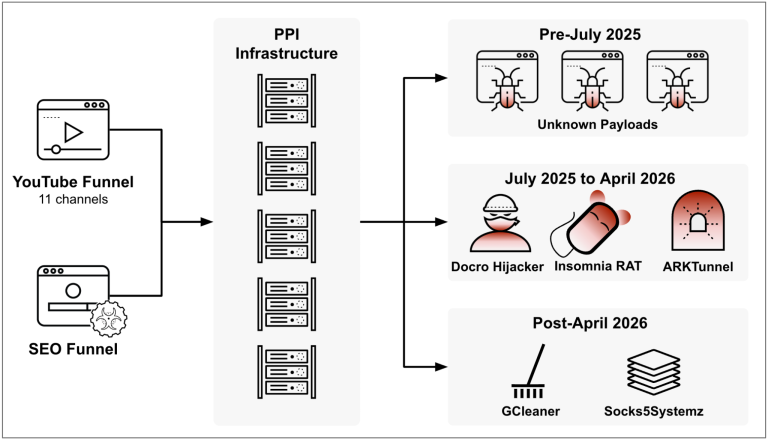
Unit 42 uncovered a large OfferLoader malware campaign distributing backdoors. Discover how OfferLoader malware abuses YouTube to compromise endpoints.

A ClearFake WebDAV infection chain deployed Amatera malware. See how the ClearFake WebDAV infection chain drops crypto stealers on targets.

The MacSync macOS stealer targets Apple users worldwide. See how MacSync macOS stealer ClickFix lures evade Gatekeeper to steal sensitive credentials.
A ClickFix browser attack uses Google Sheets C2 to inject a crypto web skimmer into Chrome. See how Cisco Talos traced the theft.
A Redis cryptomining botnet used a rogue replication attack to hijack 3,562 servers for Monero mining. See how the campaign worked.
Pegasus spyware infected a Serbian activist through a zero-click iMessage exploit, part of Serbia's largest spyware wave. Update iOS now.