 Do Son
Socket tracked 77 malicious Firefox extensions that steal crypto wallet secrets and credentials. See how the Offside Wallet Theft Factory works.
Malware

Grandoreiro banking trojan resurfaces in a DLL sideloading campaign that abuses Duplicate Files Finder to hit Mexico and Latin America.
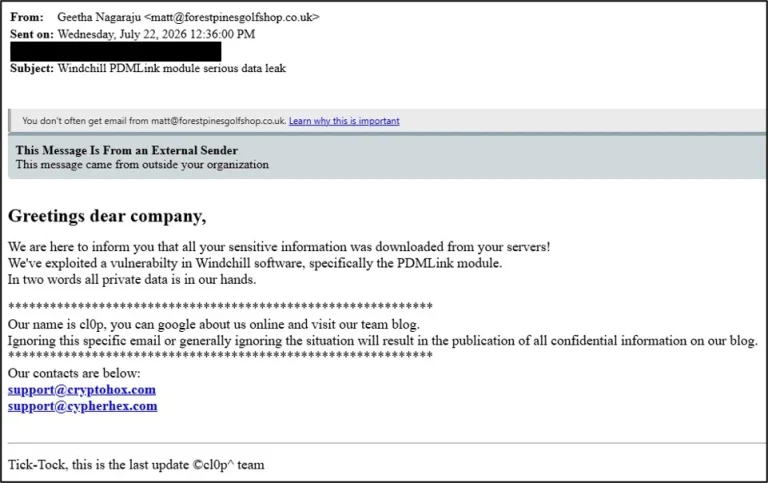
The Clop web shell targets PTC Windchill via CVE-2026-12569, stealing credentials and engineering data in a mass-extortion campaign.
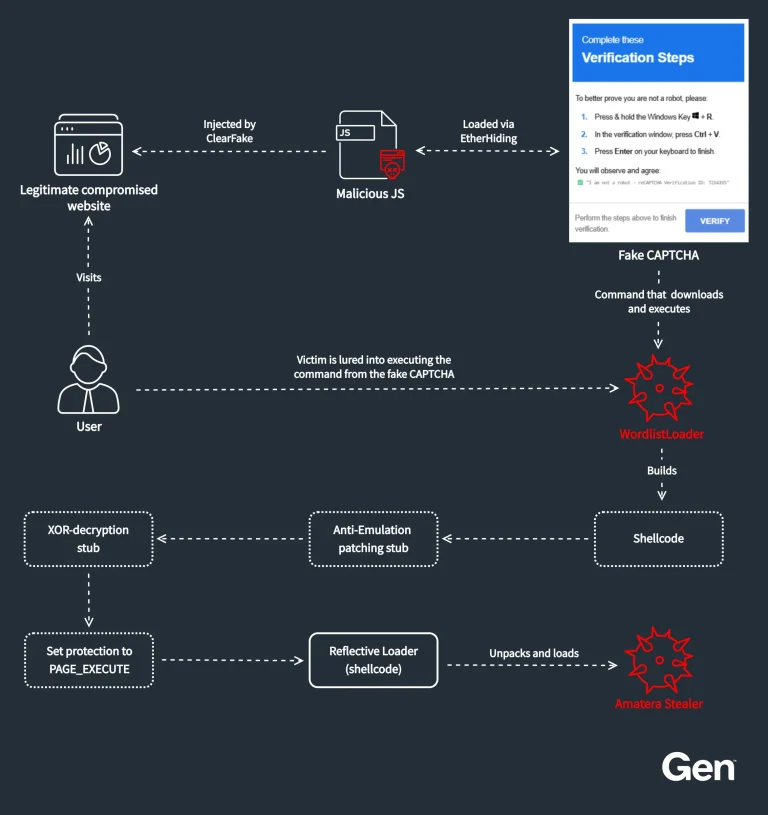
WordlistLoader malware delivers Amatera Stealer through ClearFake fake-CAPTCHA campaigns, using stealthy evasion to steal browser data.

Zscaler details the C2Looper backdoor, a Rust backdoor tied to ransomware that uses GitHub for C2 and likely spreads through ClickFix lures.
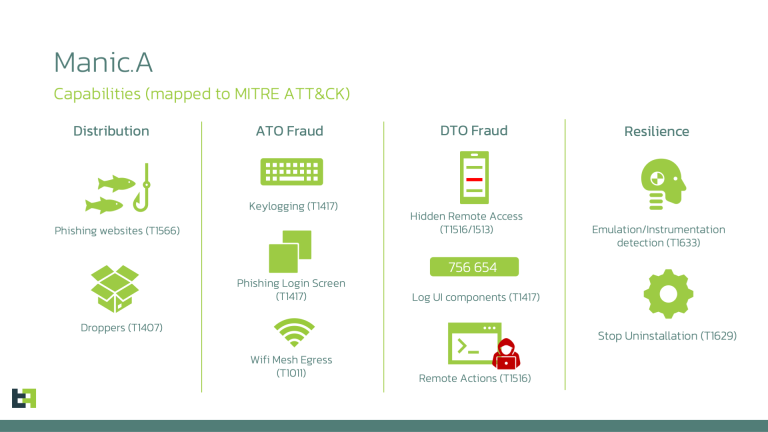
A new Manic Android malware campaign combines banking fraud and spyware, using a unique offline mesh relay to steal data even without internet access.
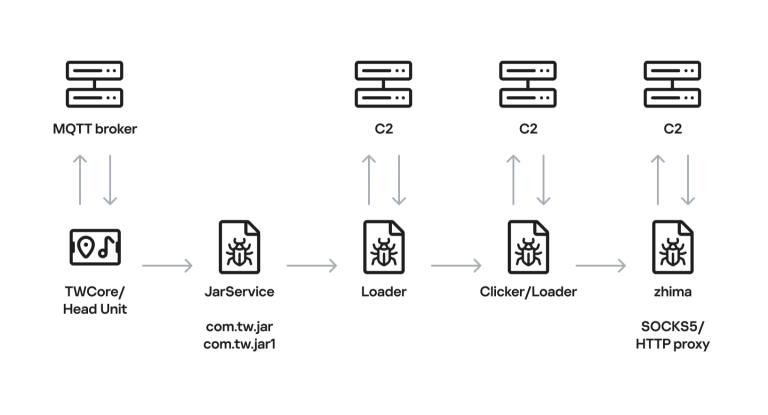
Kaspersky exposed Android head unit malware turned into a botnet. Discover how this Android head unit malware botnet infects smart cars.
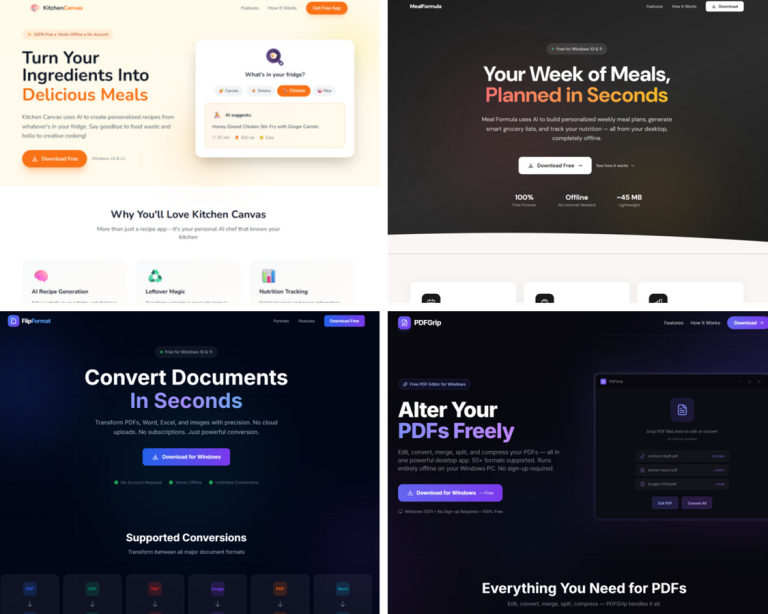
G DATA details Projextor, an Electron malware hidden in working PDF and recipe apps that runs injected scripts and captures the desktop.

FortiGuard Labs discovered the Evooo1Bot Linux botnet. Read our Evooo1Bot Linux botnet analysis to learn how this malware turns devices into proxy nodes.

Jamf Threat Labs has discovered a new AmnesiaStealer macOS infostealer malware. The AmnesiaStealer macOS infostealer steals data and hijacks browsers.

GEEKOM's official site served backdoored AMD mini PC drivers since December 2024 via a compromised legacy support page still indexed by Google.

Zscaler ThreatLabz analysts discovered the Abyssos modular RAT. This Abyssos RAT gives attackers total remote control, stealing data and credentials.

The Aeternum blockchain botnet hides C2 commands inside Polygon smart contracts, evading takedowns while dropping XWorm and XMRig payloads.
Trellix details a DCRat campaign using SVG HTML smuggling and process hollowing to deploy DarkCrystal RAT via a Colombian judicial lure.
Palo Alto Networks analyzed Kimwolf botnet malware. Read our Kimwolf botnet malware analysis to learn how it attacks Android TV boxes.

Kaspersky analyzed the Project CAV3RN framework. Read our Project CAV3RN framework analysis to see how attackers abuse DNS and Google Apps Script.
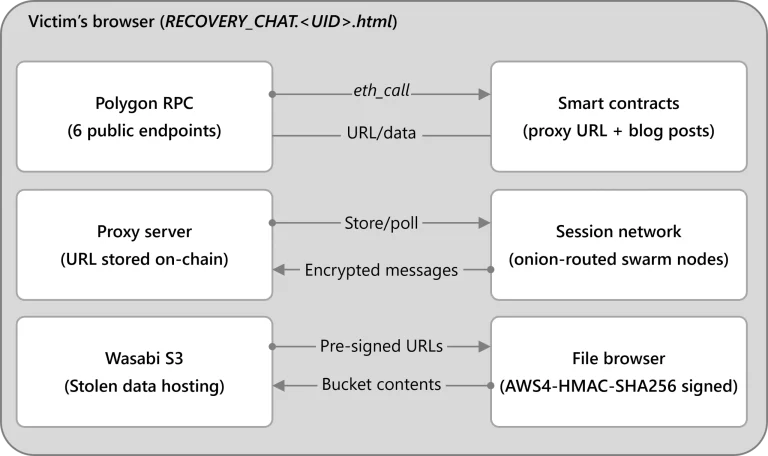
DeadLock ransomware uses blockchain nodes and Session chat. Learn how the DeadLock ransomware encryptor targets networks worldwide.

Apple has issued mercenary spyware attack warnings to users across 110+ countries, urging immediate security action and device hardening.
CISA and five agencies warn that Gunra ransomware is hitting critical infrastructure with double extortion. A Linux flaw may let victims recover free.

ChainDrop npm worm infected 400+ packages, stealing cloud keys and CI secrets via blockchain C2. Unit 42 details the full attack chain and fixes.

A fake Zoom installer delivers Overlord RAT on macOS via a .NET downloader. Jamf Threat Labs details the infection chain and defenses.

A macOS ClickFix campaign now uses a browser fingerprinting gate to hide AMOS infostealer lures from researchers. See how it works.