
 Do Son
Proofpoint details the Cruciferra crypter service that cloaks RATs and infostealers using BYOVD EDR tampering and 90+ custom encryption routines.
Malware

The NadMesh botnet targets cloud environments. This AI infrastructure threat harvests cloud credentials and exploits open services for autonomous spreading.

The new TAG-150 attack chain uses ClickFix to deploy DenoRAT malware and NightshadeC2. Learn how this threat targets financial sectors and crypto wallets.
Microsoft warns of rising ACR Stealer attacks using ClickFix lures to steal browser credentials and tokens from enterprises. Two chains detailed.

A new GST phishing campaign targets Indian taxpayers. This operation delivers Remcos RAT malware using an embedded bitmap payload to steal user credentials.

Spirals ransomware hit a South Asian IT firm in a double extortion attack, going from IIS breach to network-wide encryption in under 24 hours.
A global phishing campaign hides a low-detection Lua loader inside fake .ttf font files to drop Remcos, XWorm, Agent Tesla, and a Snake Keylogger.

Symantec found Daxin malware active in Taiwan in May 2026, alongside a new Stupig backdoor that runs commands from the Windows logon screen.

Attackers exploit a Langflow RCE flaw to drop a custom Gafgyt botnet built purely for DDoS, Akamai reports. The payload hides C2 with a modified RC4 cipher.

Kaspersky uncovered OkoBot, a modular framework with 20+ payloads driving cryptocurrency wallet theft. Hundreds of victims sit across more than 25 countries.

Elastic Security Labs found TELEPUZ malware spreading via a ClickFix attack chain. The modular MaaS uses WebSockets and blockchain C2 fallback.

Unit 42 exposed TuxBot v3 Evolution, an IoT botnet built with LLM help. AI-written bugs left the malware only 70% functional. See the full analysis.

ClickLock Stealer is macOS malware that freezes your Mac until you type your password. Group-IB found 100+ victims across 33 countries.

LG monitor adware installs itself via Windows device metadata and pushes McAfee pop-ups. Learn how a Group Policy tweak blocks the unwanted software.

HOLLOWGRAPH malware turns Microsoft 365 calendars into covert C2 through Microsoft Graph API abuse. Group-IB links it to the Cavern framework.

CrashStealer is a native C++ macOS infostealer posing as Apple's crash reporter. Jamf details its notarized dropper, AES-GCM theft, and persistence.

LabubaRAT is a Rust-based remote access tool disguised as NVIDIA software. It supports HTTPS, WebView2, and DNS tunneling for command and control.
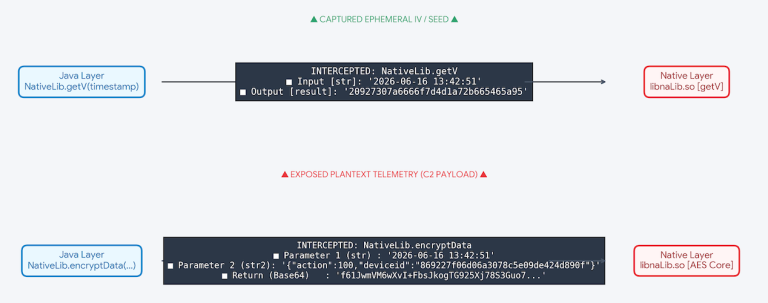
The GoldPickaxe banking Trojan returns, stealing biometric data, SMS, and lock screens from Android users across Asia, Zimperium warns.
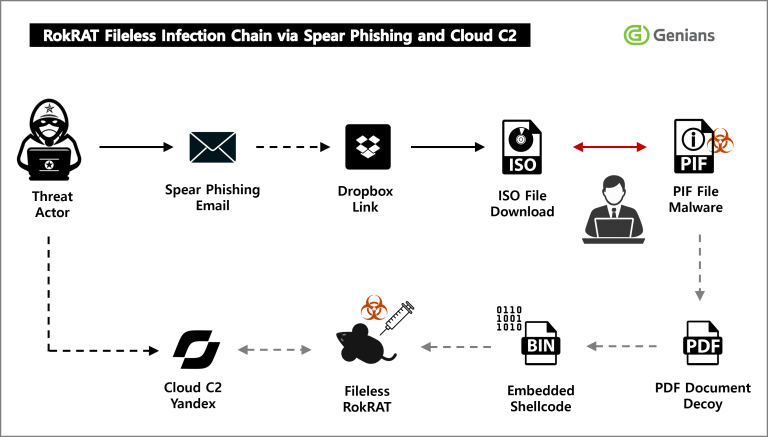
Genians exposed Operation Capsule Vault, an APT37 campaign. The RokRAT malware hides inside a fake PDF to spy on academics and researchers.
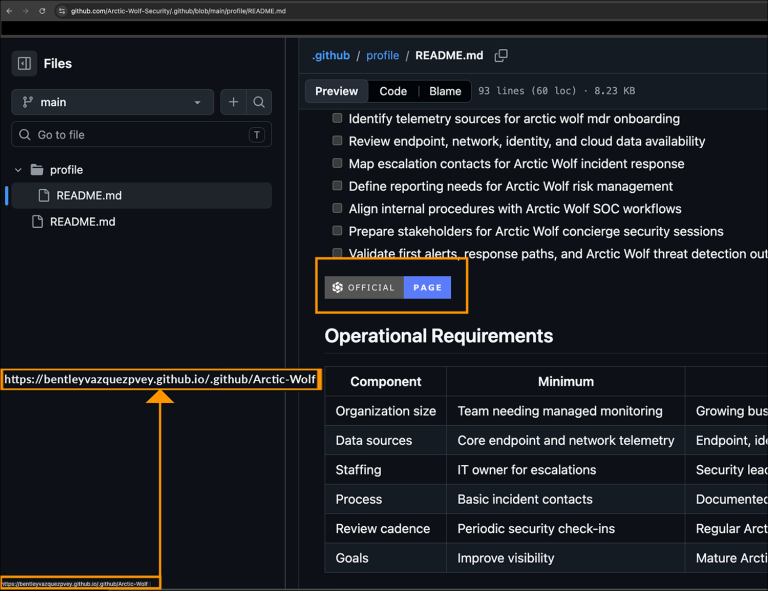
Arctic Wolf found 292 fake GitHub repositories impersonating software vendors to deliver a BoryptGrab-lineage infostealer via DLL side-loading.

Doctor Web found a supply chain trojan targeting software developers. This developer-targeting malware steals data, crypto wallets, and mines coins.
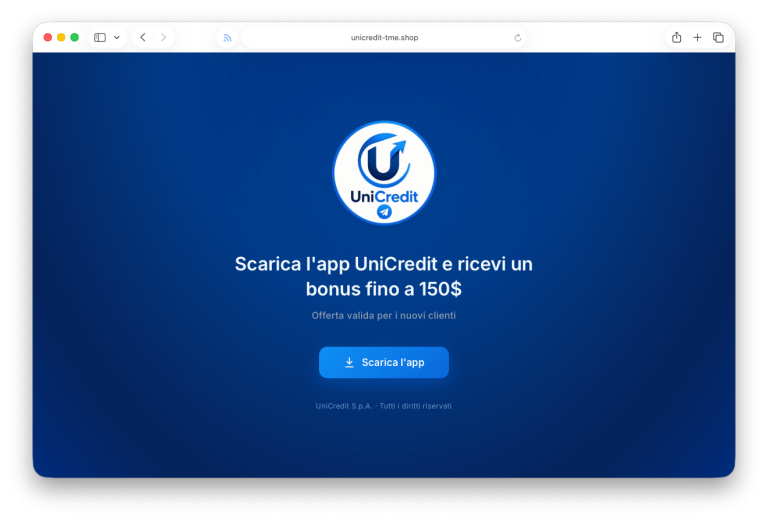
Albiriox malware spreads via a fake UniCredit reward and a Telegram bot. The Android banking trojan abuses Accessibility to steal OTPs and hijack devices.