 Do Son
INC ransomware targets mainframes using cross-platform ransomware payloads. Attackers expose a new campaign hitting APAC manufacturing and food companies.
Malware
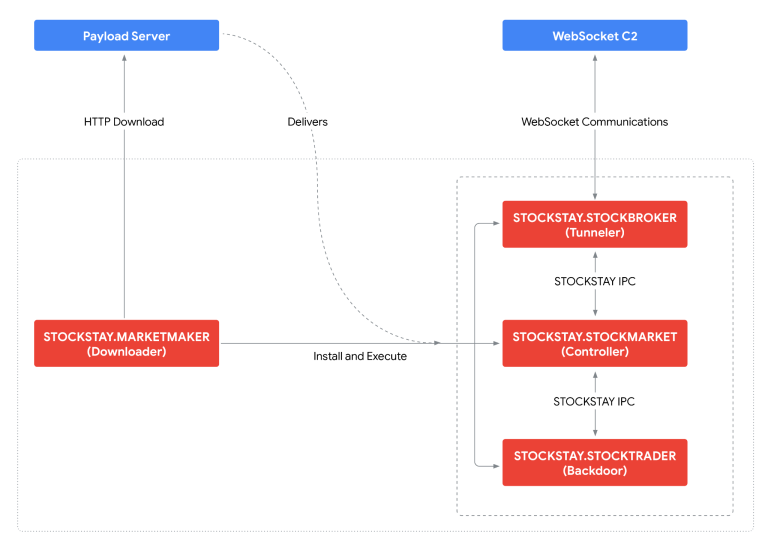
Turla STOCKSTAY backdoor attacks Ukrainian military targets. Russian cyber espionage groups deploy this .NET malware via malicious RDP and WinRAR flaws.
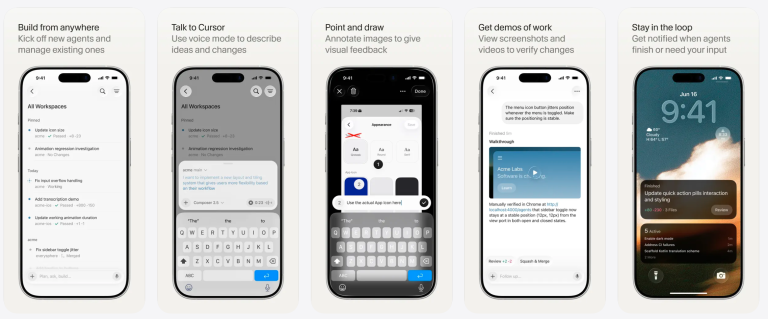
Discover the new Cursor iOS beta app. This remote AI coding tool lets developers manage agents, review code, and merge pull requests directly from mobile.
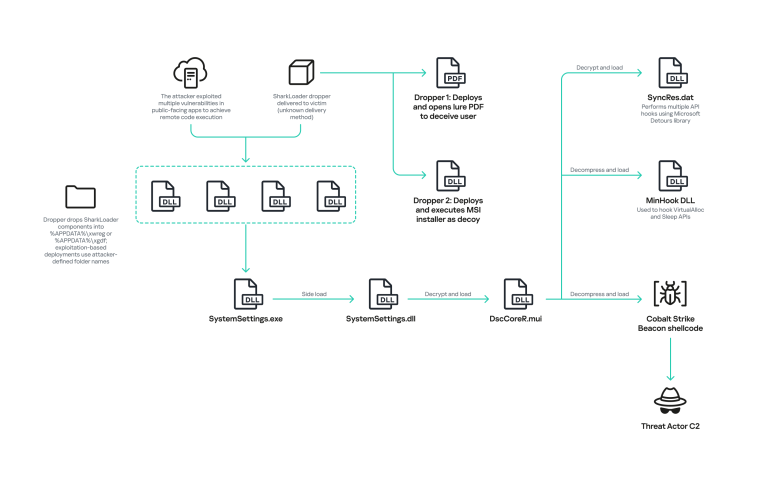
Kaspersky details SharkLoader malware, which deploys Cobalt Strike Beacon in the global StrikeShark campaign via DLL sideloading and exploited apps.
The new macOS Gaslight malware, a North Korean Rust backdoor, targets analysts with LLM prompt injection and steals sensitive keychain data.

Edgecution malware abuses a malicious Edge extension and native messaging to backdoor hosts. Zscaler links it to a Payouts King access broker.
A new Mistic backdoor malware campaign linked to a ransomware access broker targets multiple sectors. Learn how this stealthy threat evades detection.
A new Langflow cryptominer malware campaign exploits CVE-2026-33017 to deploy malicious payloads. Learn how this threat spreads and how to stay protected.

The OXLOADER malware loader spreads via malicious Google Ads, dropping the CASTLESTEALER infostealer with heavy obfuscation and anti-VM checks.
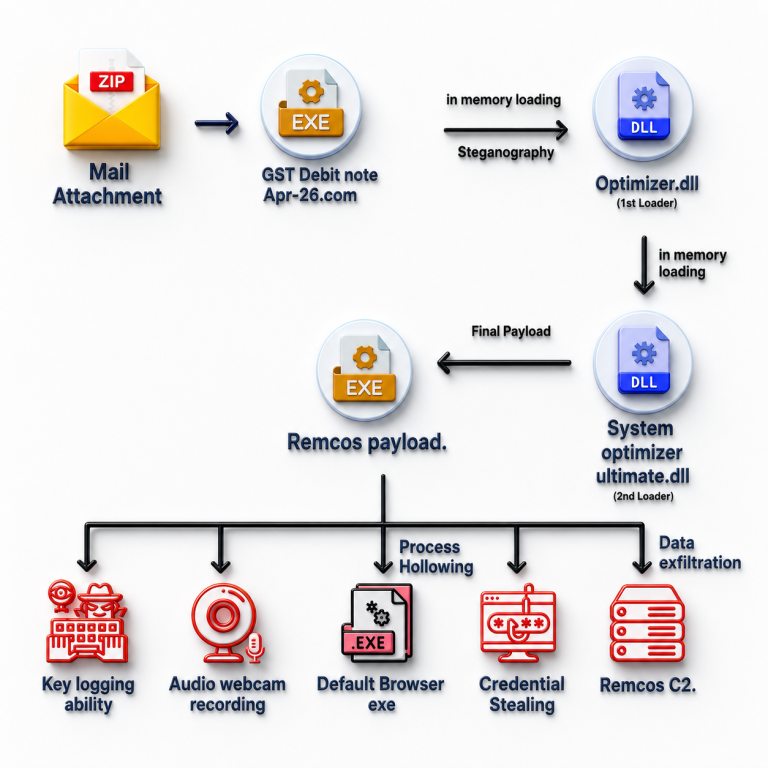
A steganographic loader hides Remcos RAT inside a bitmap and runs it in memory. K7 ties the fileless campaign to India via fake GST lures.

Microsoft discovered a new Windows crypto clipper malware. This Tor routed cryptocurrency stealer uses USB drives to spread and steal wallet addresses.
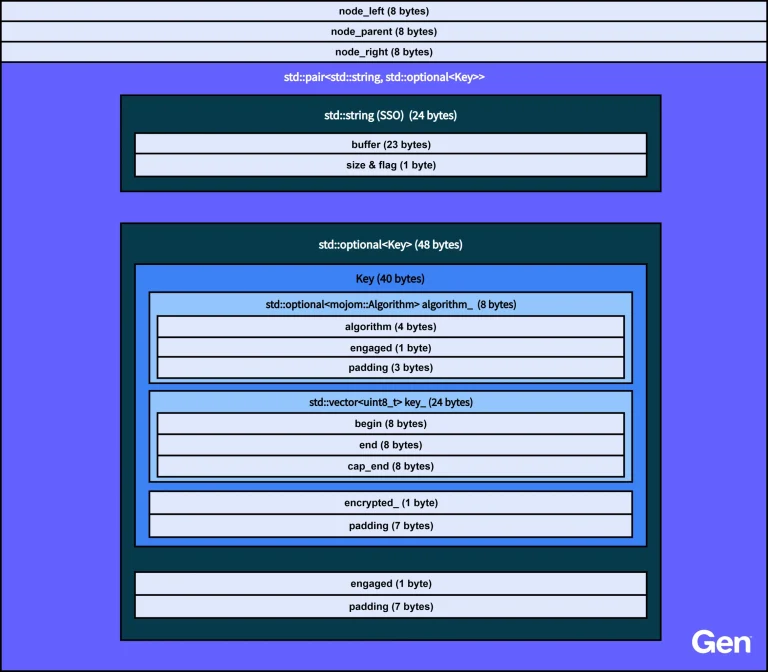
Gen Digital uncovered a new Vidar ABE bypass technique. The Vidar infostealer malware now uses memory scanning and APC injections to extract browser keys.
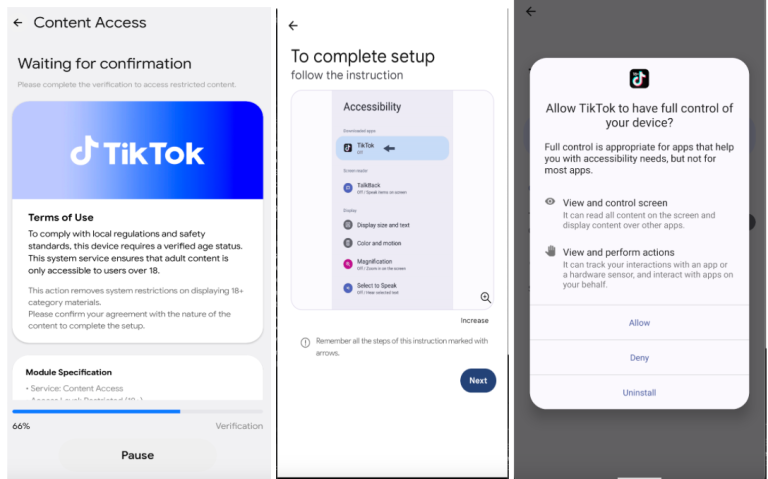
The Rokarolla Android banking trojan executes a complete device takeover. It targets 217 apps and steals credentials through fake overlays and keyloggers.
Check Point exposed a crypto clipboard hijacker spread by fake Ghost Networks. The Rust clipper swaps wallet addresses to steal crypto. Stay alert.
An AI-generated SmartRAT ClickFix campaign targets banking users, mimicking the Banana RAT. This threat relates to flaws like CVE-2026-26980.
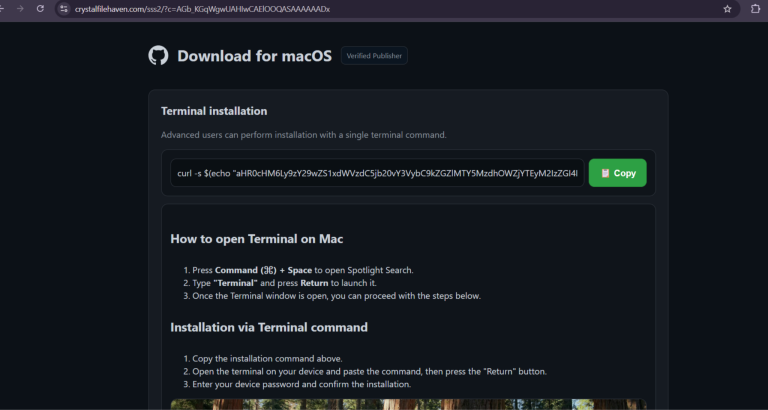
A new macOS ClickFix AppleScript stealer named the Meow macOS stealer acts as a persistent RAT, hijacking wallets and evading detection. Protect your Macs.
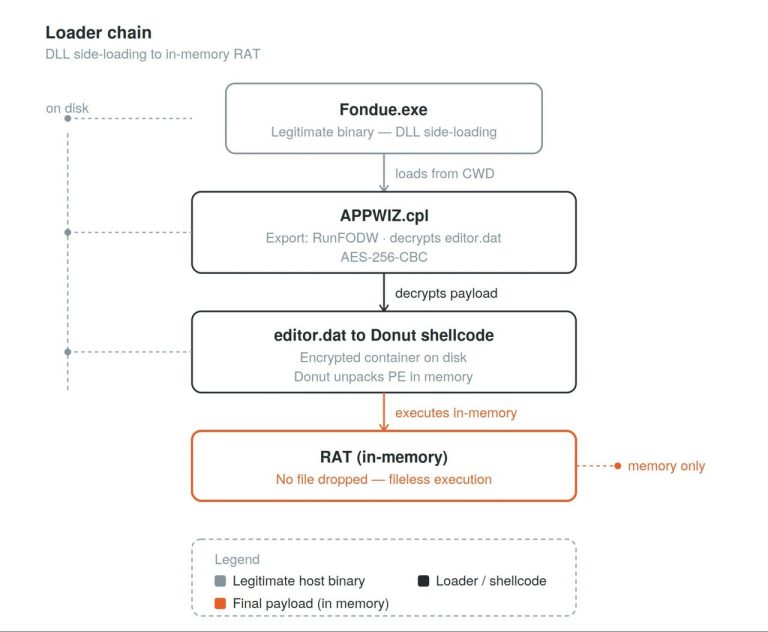
Rapid7 exposes a new Dropping Elephant malware campaign using a China-themed loader to deploy a fileless RAT. Learn about its evasion tactics and defense.

A new AryStinger malware campaign exploits CVE-2013-3307 and CVE-2016-5681 to compromise legacy routers, building a global attack proxy network.

Hackers are hiding malware inside malicious Steam wallpapers. Learn how the Wallpaper Engine app exposes gamers to account hijacking and crypto miners.
SHEETCREEP malware is a C# Google Sheets RAT tied to APT36. It hides command-and-control inside Google Sheets to evade network detection.
DragonForce ransomware deployed Backdoor.Turn, a Microsoft Teams backdoor that hides C2 in Teams TURN relays. Symantec details the novel technique.

ErrTraffic malware powers ClickFix attacks on hacked WordPress sites, using EtherHiding on the blockchain to hide its C2 and spread infostealers.