
 Do Son
Read how the MagicAd Android trojan exploits GetApps malware distribution networks to run background advertisements without user consent.
Malware

Discover how malicious traffic routing hijacks open-source downloads in this new Check Point research report on global malware distribution.

Read the Kaspersky malware analysis revealing how the Argamal Trojan campaign targets adult gamers using stealthy COM hijacking.
A new malicious PyPI package wave highlights evolving supply chain attacks. Learn how to protect your CI/CD pipelines from credential theft.
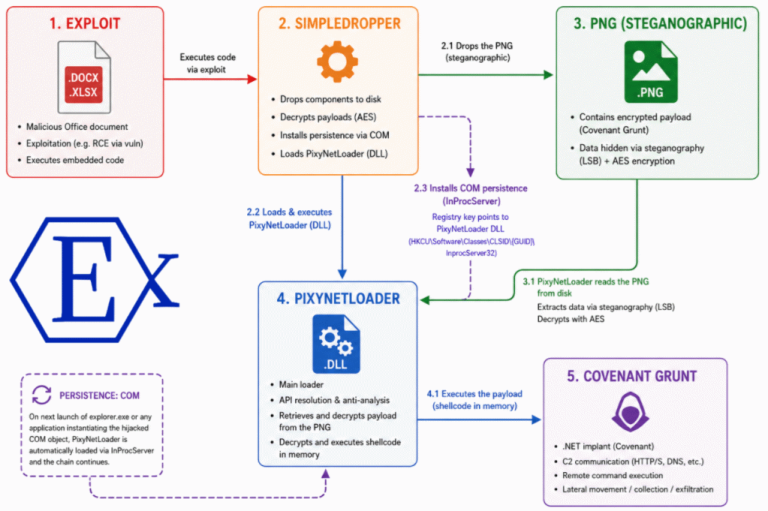
Researchers expose PixyNetLoader malware analysis revealing APT28's steganography APT28 attack, hiding Covenant Grunt payloads inside PNG pixels since 2024.
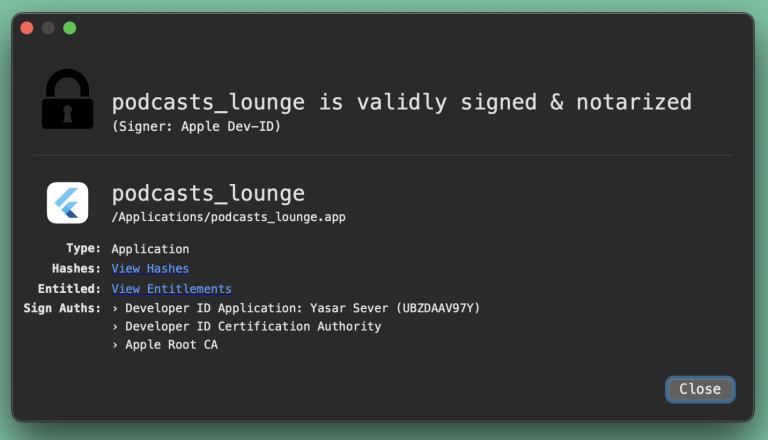
New details on the Operation FlutterBridge malware reveal a sneaky WebView-based architecture designed to hijack Chrome browsers on macOS.
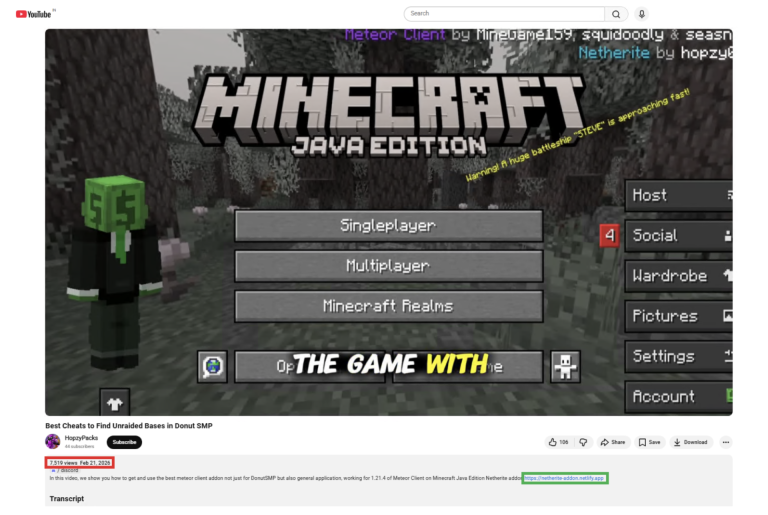
The active WeedHack malware campaign spreads via fake videos offering free Minecraft mods, leading to account hijacking and stealthy cyberbullying.

A massive PyPI supply chain attack has hit developers. Learn how Socket malware detection uncovered the Hades cluster stealing cloud credentials.

An in-depth PHANTOMPULSE malware analysis reveals a sneaky blockchain C2 channel and AI-assisted coding techniques used by advanced threats.

G Data uncovers a new Remcos RAT variant using DonutLoader shellcode and trusted LOLBins to bypass Windows security filters.
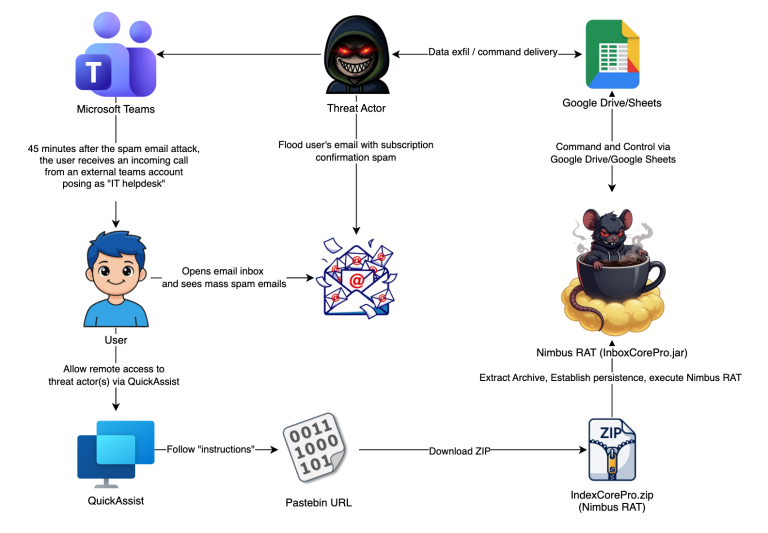
Learn how a Microsoft Teams vishing attack leverages email flooding and Quick Assist to execute a dangerous Nimbus RAT deployment chain.
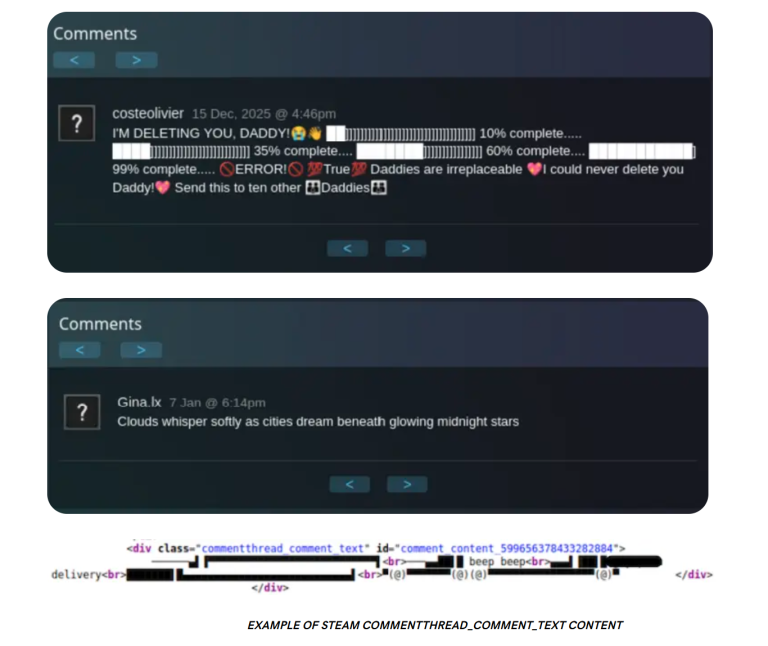
A sneaky Steam profile malware campaign targets WordPress. Attackers use invisible Unicode steganography to hide malicious command strings.
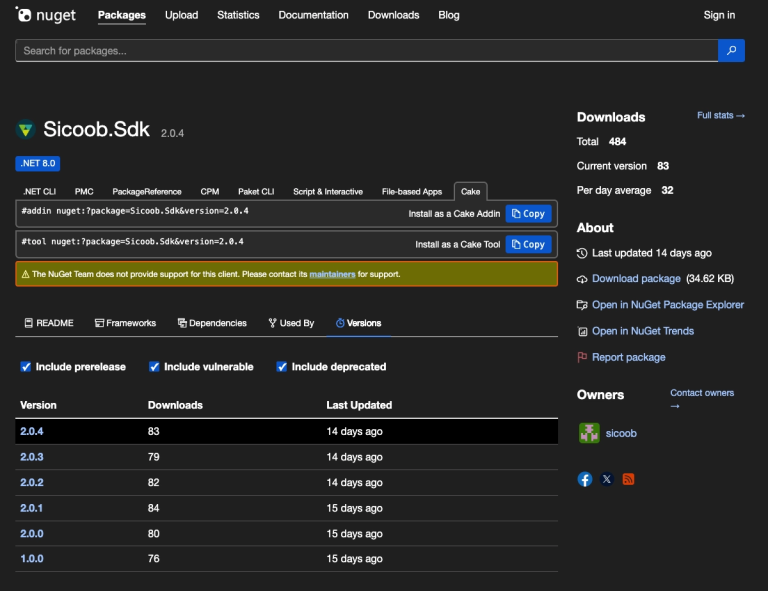
A dangerous Sicoob SDK banking malware campaign triggers a major NuGet supply chain attack. Learn how it exfiltrates private financial certificates.
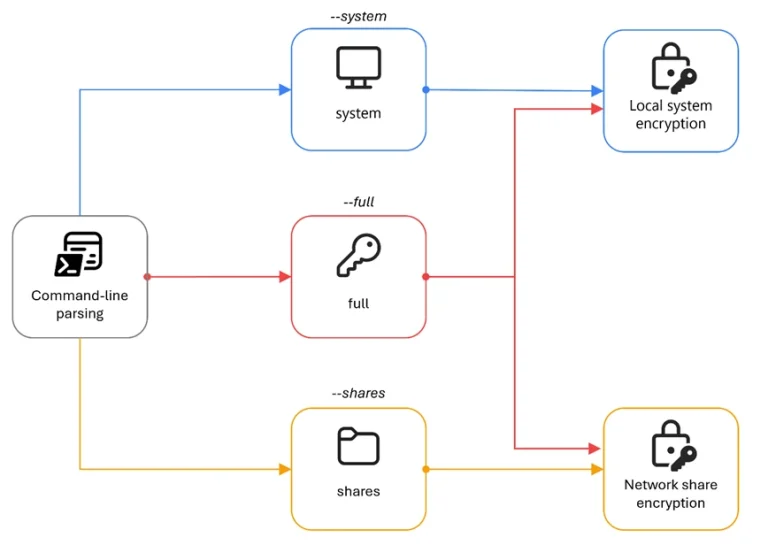
A deep Gentlemen ransomware threat analysis by Microsoft Threat Intelligence reveals an aggressive worm capability and double extortion tactics.
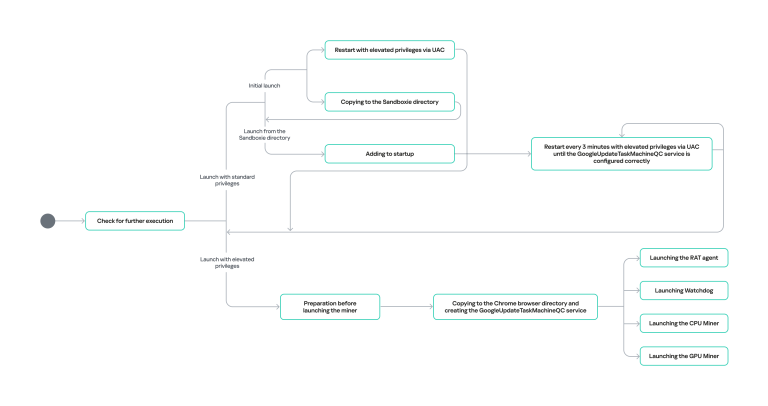
A stealthy SilentCryptoMiner variant uses a fake plugin update to infect systems. Protect your enterprise from this advanced cryptocurrency miner.

A fake RVTools installer campaign distributes a modular Python RAT. Learn how this malware uses signed certificates to evade security controls.

The dangerous Grandoreiro banking trojan returns. Discover how it utilizes an advanced DLL side loading technique to bypass corporate defenses.

Analyze the recent Red Hat NPM attack. Learn how hackers bypassed trusted publishing via GitHub Actions to deploy the Mini Shai-Hulud worm.
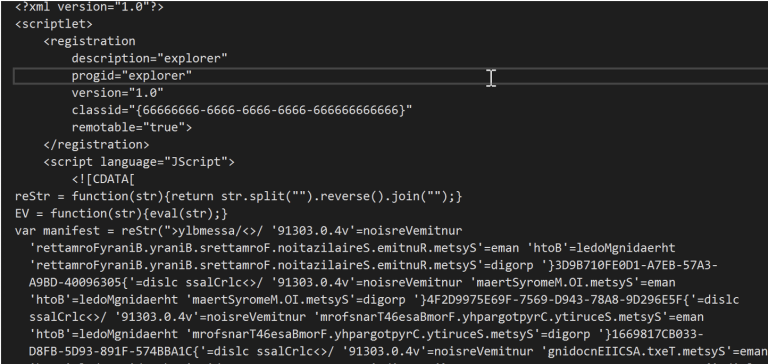
A stealthy Twill Typhoon RAT campaign targets APJ organizations. Discover how this threat exploits DLL side loading tradecraft to evade security.

A new Android banking trojan threat targets 180+ apps. Learn how credential harvesting overlays steal banking data.

A stealthy GPU cryptojacking campaign leverages AI search poisoning and process hollowing injection to hijack high-end rigs. Read the Microsoft report.

Akamai SIRT uncovers a new P2P cryptominer malware threat. Learn how Ollama endpoint attacks use decentralized libp2p networks to evade detection.