
 Do Son
Microsoft exposes the GigaWiper backdoor, a destructive tool that bundles disk wiping malware, fake ransomware, and remote control in one implant.
Malware
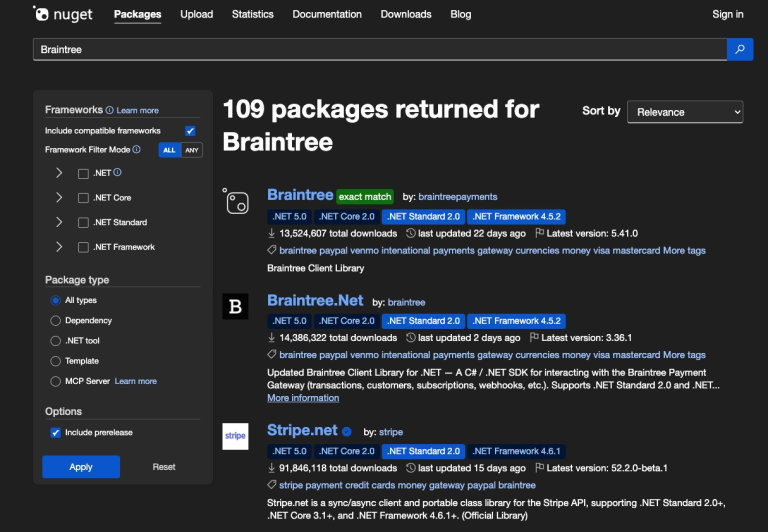
A malicious NuGet package, Braintree.Net, acts as a credit card skimmer and steals merchant API keys. The Braintree NuGet typosquat hits .NET devs.

A CrySome RAT phishing attack used a fake freight rate confirmation to bypass AMSI, disable Defender, and steal browser credentials on Windows.
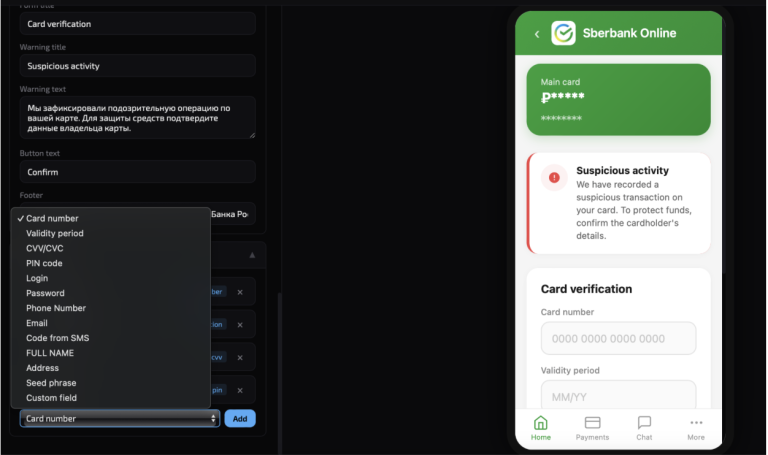
RedWing Android malware is a rental spyware sold as malware-as-a-service on Telegram. It steals banking logins, intercepts 2FA, and hijacks phones.

GodDamn ransomware is the latest Beast ransomware rebrand from Hyadina. It uses a Microsoft-signed malicious kernel driver, PoisonX, to disable EDR.

A LNK phishing attack drops a Node.js backdoor and hides its C2 on the TON blockchain using EtherHiding, LevelBlue reports.
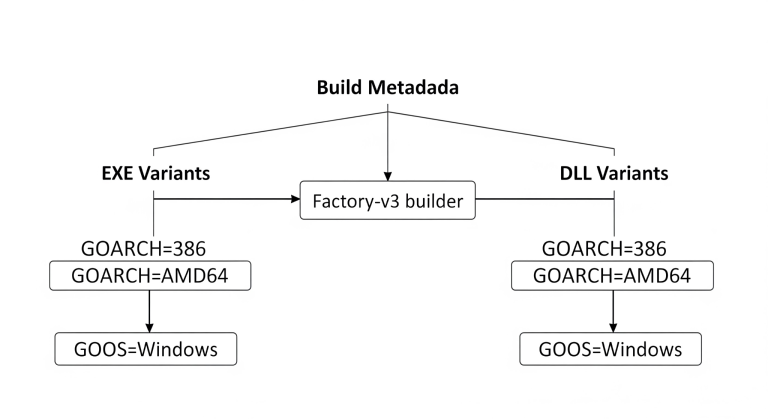
A new Vidar stealer campaign uses the Factory-v3 loader and fake certificates to deploy malware. Learn how attackers hide XMRig and bypass security.
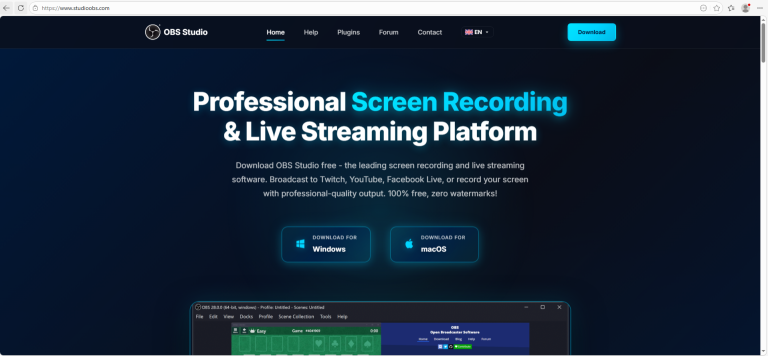
A massive ScreenConnect AsyncRAT campaign uses SEO poisoning and spoofed websites to drop malicious installer archives via remote monitoring tools.

Discover how the Mycelium Framework transforms infected machines into a malicious AI-as-a-Service botnet for distributed computing and automated exploits.
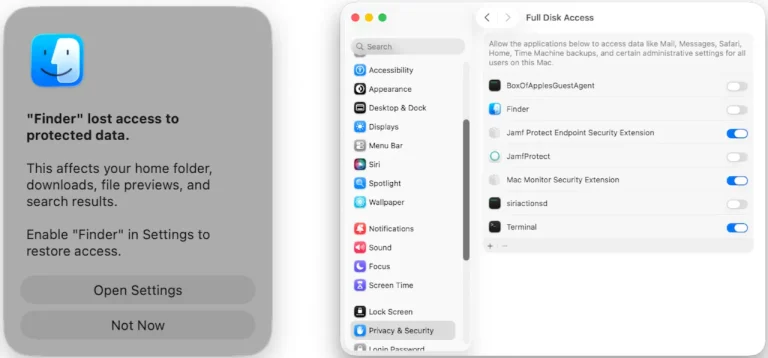
PamStealer macOS malware hides in a fake Maccy app and drops a Rust infostealer that checks your password via PAM before stealing it.
Sysdig documented JADEPUFFER, the first agentic ransomware run end-to-end by an AI agent. It breached Langflow via CVE-2025-3248 and extorted a database.
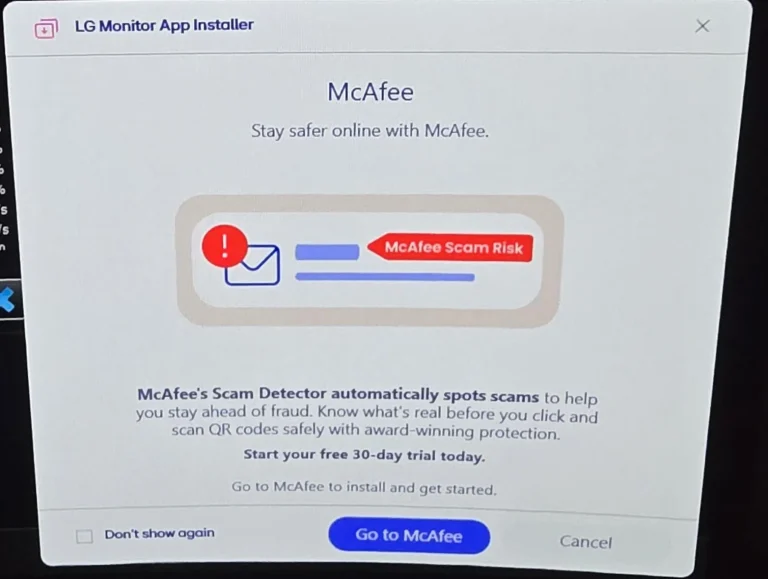
Discover how hidden LG monitor adware automatically installs unwanted McAfee pop-ups on your PC. Learn how to stop this intrusive bloatware today.
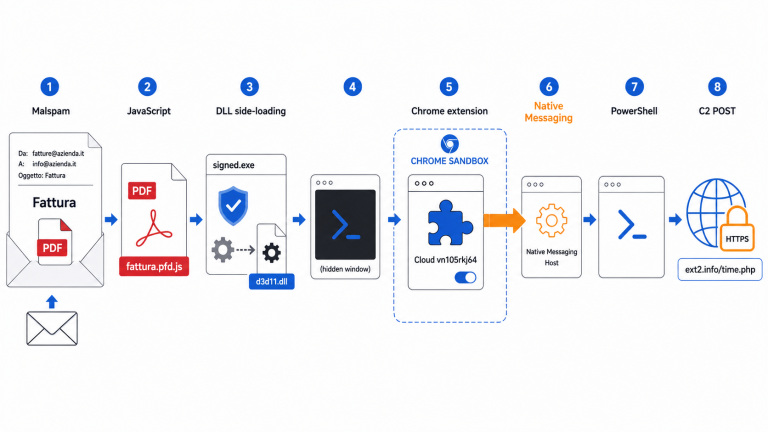
A Native Messaging backdoor pairs a malicious Chrome extension with a local host to run PowerShell, escaping the browser sandbox, says D3Lab.
Veil#Drop malware abuses Blogspot to run PowerShell loaders and deploy PureLog Stealer in memory, dodging antivirus and file-based detection.
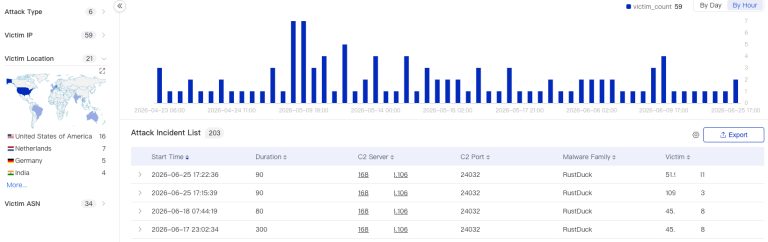
The RustDuck botnet is a fast-evolving two-stage DDoS threat moving from C to Rust, with encrypted C2 and heavy anti-analysis, per XLab.
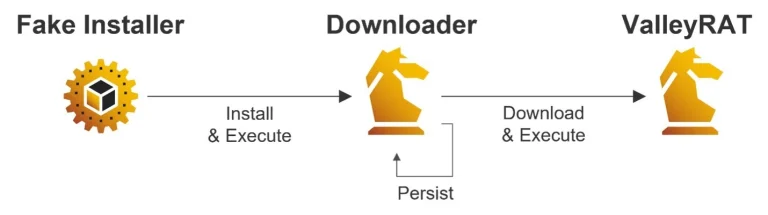
LevelBlue tracks a ValleyRAT malware email campaign using DLL sideloading and fileless execution to hit Japanese and Chinese users.
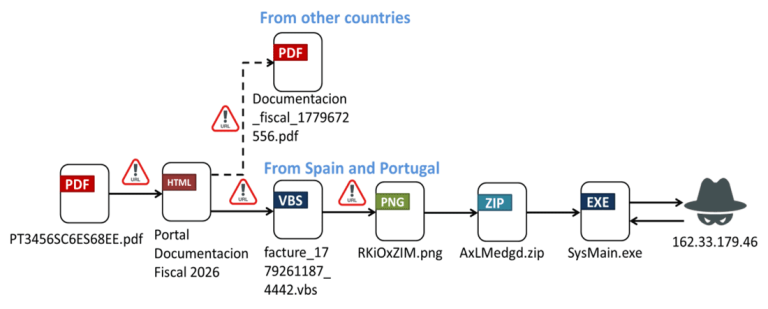
FortiGuard Labs discovered a new Ousaban banking trojan campaign. The attackers use geo-blocking to target banking users in Spain and Portugal.
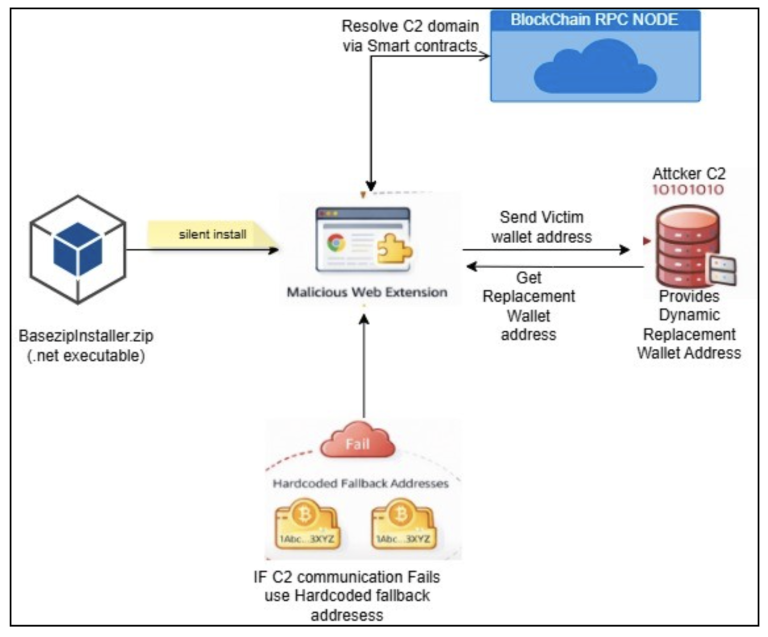
The Silent Swap crypto clipper steals digital assets via a fake Google Notes extension. Learn how this malware uses EtherHiding to drain your wallet.
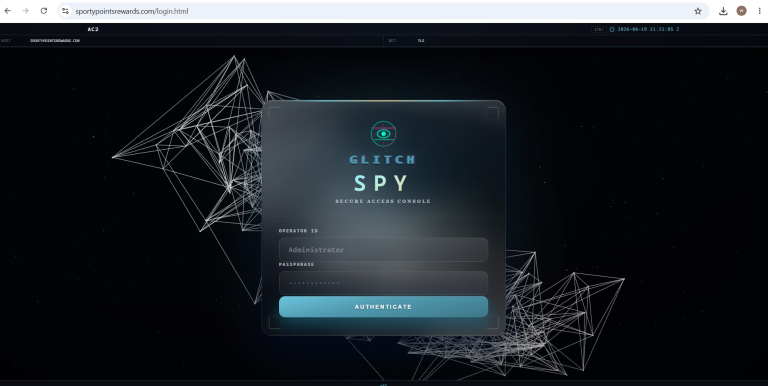
New Glitch SPY Android RAT spreads via a fake rental app, abusing Accessibility to steal data and swap crypto wallet addresses.
Microsoft found a fake Perplexity AI extension that hijacks browser search and logs keystrokes. Google pulled the malicious Chrome extension.
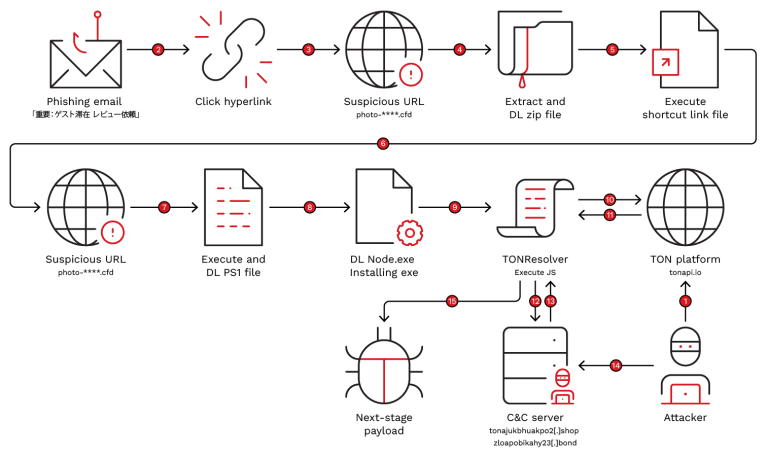
Trend Micro found TONResolver malware hitting Booking.com hotel partners in Japan. It hides its C2 in a TON blockchain smart contract. Details inside.
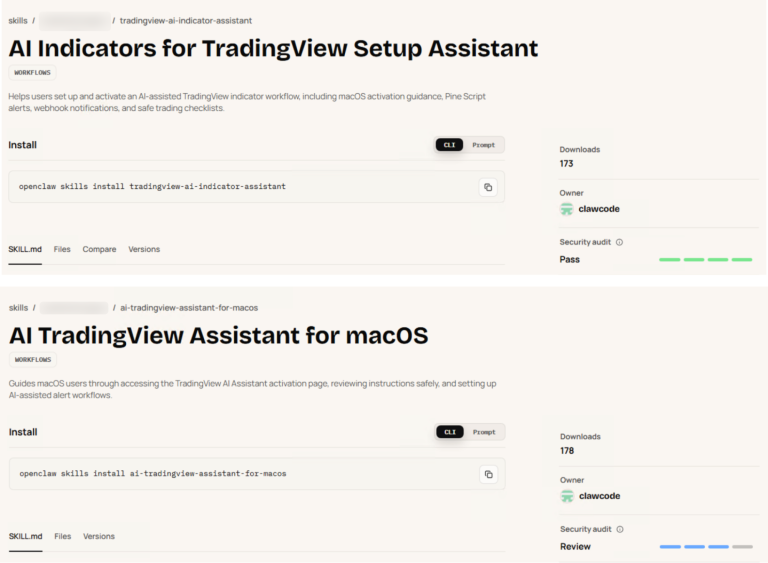
Unit 42 found five malicious OpenClaw skills on ClawHub that bypassed scanners. The AI supply chain attack delivered infostealers and crypto fraud.