
 Do Son
A new npm package uses prompt injection and token flooding for AI malware scanner evasion. Discover how attackers disrupt AI-assisted malware review.
Malware

GlassWASM malware hides WebAssembly payloads in trojanized Open VSX extensions, abusing Solana memos for stealthy command-and-control.

IBM X-Force links the Interlock and Rhysida ransomware ecosystem through shared malware like Supper, NodeSnake, and overlapping crypters.

Discover how APT37 NarwhalRAT malware uses MS-themed phishing and a dead-drop C2 to target users with a sophisticated Python backdoor.

FortiGuard Labs uncovered AsyncRAT AI lures using fake AI guides and an AutoHotkey loader to inject a stealthy .NET RAT into memory.
Acronis reveals Khmer Shadow, a new espionage campaign using NIGHTFORGE loader and DLL sideloading to target Cambodian government entities with Havoc Demon.

GoFlateLoader malware, a Golang loader, uses a giant PE overlay to evade scanners and deliver infostealers like Lumma, Vidar, and StealC.
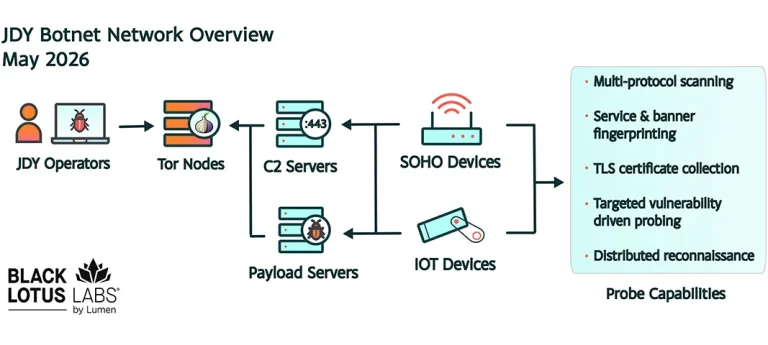
The JDY botnet, a China-nexus IoT network tied to Volt Typhoon, now spans 1,500+ devices and scans for new bugs like CVE-2026-35616 within hours.
A Mastra supply chain attack compromised 140+ npm packages, using the typosquatted easy-day-js dependency to drop a crypto-stealing infostealer.
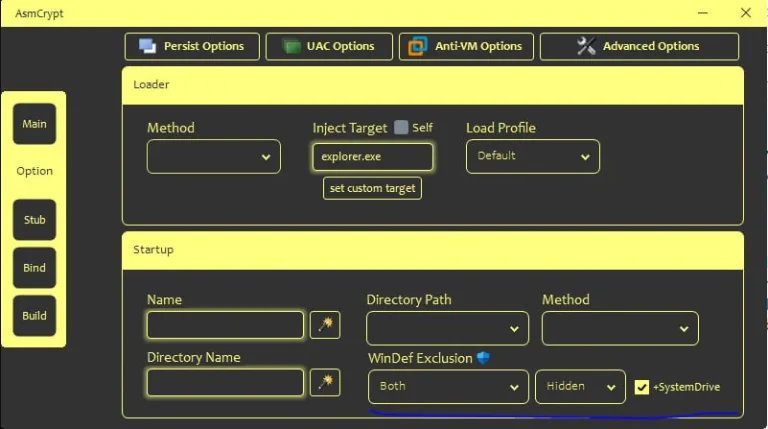
SilabRAT malware, aka SnappyClient, is a $5K/month MaaS RAT flagged as HijackLoader. It uses HVNC and cracks crypto wallets, per Group-IB.
A ShapedPlugin supply chain attack (CVE-2026-10735) injected malware into WordPress Pro plugins. Discover the impact and how to protect your site today.

UNK_DeadDrop phishing campaigns are targeting developers with fake jobs to deliver Overlord malware. Learn how to defend against this North Korean threat.

Discover how Fluffy Wolf phishing attacks target Russian organizations with the new PowerLoader malware to deploy PureRAT and Pay2Key ransomware.

Discover how a simple phishing email triggers a complex Agent Tesla infection chain, using process injection and in-memory loading to steal sensitive data.

Discover how the new MLTBackdoor malware family uses the ClickFix infection chain to establish footholds for ransomware attacks and lateral movement.

Howler Cell exposes an X-VPN DLL sideloading campaign delivering STX RAT via 11 trojanized installers targeting crypto and VPN users.

Discover how malicious Chrome extensions engage in traffic laundering while lying to users about collecting data on the official store.

Operation TaxShadow uses fake tax notices to spread in-memory tax phishing malware with WebSocket C2, per CYFIRMA's new report.

Discover how the stealthy VerdantBamboo malware campaign infiltrates network edge devices in this comprehensive Volexity threat report.

Read the latest Gafgyt malware analysis revealing how the dangerous COXMO botnet variant spreads via standalone scripts.

Discover how the Havoc stager campaign exploits fake invoices. Read the LevelBlue SpiderLabs report detailing this stealthy threat.

A new report reveals how malicious AI extensions use browser data exfiltration tactics to steal private conversations from ChatGPT and Claude.