 Do Son
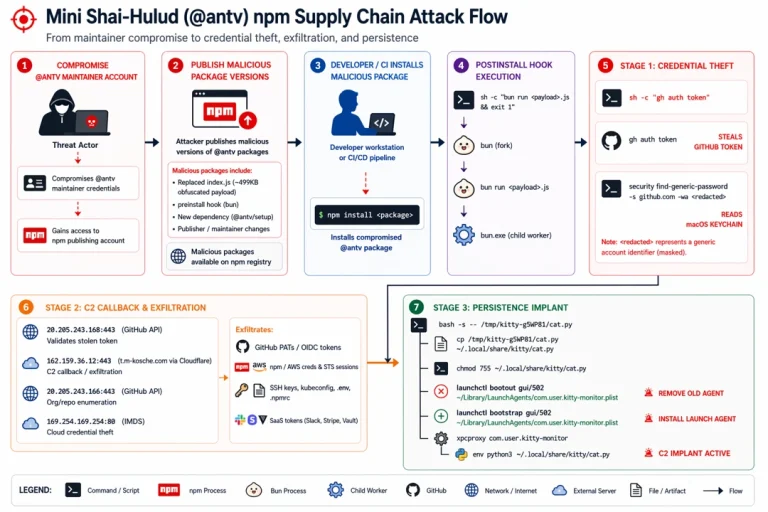
Microsoft warns of an aggressive Mini Shai-Hulud worm attack targeting the @antv npm ecosystem and stealing secrets from cloud-connected CI/CD pipelines.
Malware

Microsoft Threat Intelligence exposes a massive overhaul of the Kazuar backdoor. Secret Blizzard weaponizes a modular, multi-tiered P2P botnet.

Velvet Chollima leaks its own backend infrastructure keys inside a malicious "Tralert FX" installer signed with a valid EV certificate.

Kimsuky APT evolves its arsenal with "HelloDoor," a new Rust-based backdoor, and hijacks trusted VSCode Remote Tunneling to bypass corporate firewalls.

Point Wild exposes a sophisticated PyInstaller loader using in-memory AMSI patching and SHA-512 decryption to drop XWorm V7.4. Patch now!
New research by Intezer reveals the OrBit Linux rootkit is actually a fork of the open-source Medusa kit, actively weaponized across multiple APTs.
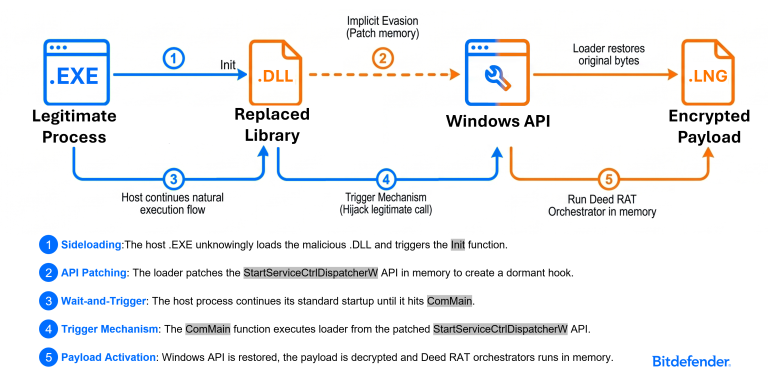
Bitdefender exposes a persistent FamousSparrow campaign using advanced DLL sideloading and Deed RAT to compromise energy infrastructure. Patch now!

The Mini Shai-Hulud npm worm has hijacked the atool account, poisoning AntV & timeago.js to scrape GitHub runner memory. Execute a full reset now!

TeamPCP has open-sourced the Shai-Hulud supply chain worm. Multiple malicious typosquatted NPM packages are already weaponizing the AI-synthesized code.

Urgent: Malicious Nx Console v18.95.0 briefly hit the VS Code Marketplace, targeting 2M+ installs with a macOS backdoor and token stealer. Audit now!

Cato CTRL intercepts "TencShell," a new stealth malware derived from open-source Rshell. Attackers use third-party access to breach networks!

McAfee Labs exposes a massive CountLoader campaign using EtherHiding and AMSI bypass to drop stealthy cryptocurrency clippers. Secure your assets!

Gamaredon targets critical systems by exploiting WinRAR vulnerability CVE-2025-8088 to drop GammaDrop malware. Secure your entry points now!

Paper Werewolf APT targets industrial sectors with PaperGrabber stealer and EchoGather RAT. Learn to detect their AI-assisted loaders and custom tools.

Critical: Cemu 2.6 Linux binaries were backdoored via a developer's stolen GitHub token. If you downloaded Cemu for Linux between May 6–12, audit your system now.

Gen Digital exposes a JDownloader site breach (May 6-7, 2026). Attackers used WDAC policies to kill antivirus and r77 rootkits for total system invisibility.

GemStuffer exploits RubyGems as an illicit data transport to scrape UK council portals. Discover how this supply chain attack bypasses standard defenses.
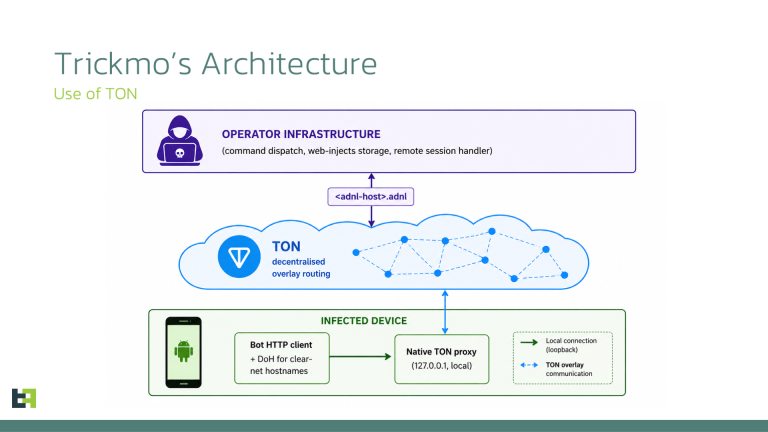
ThreatFabric uncovers TrickMo Variant C, a new Android banking trojan using the decentralized TON network to evade detection and turn phones into proxies.
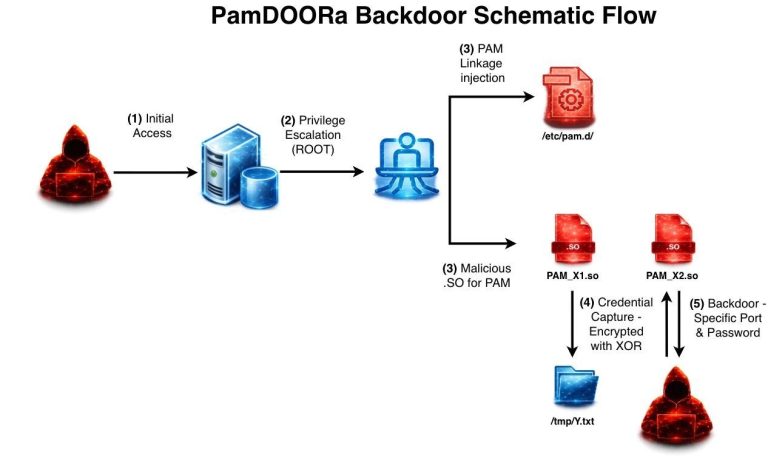
Flare unmasks PamDOORa: a $1,600 Linux backdoor that hijacks the PAM stack to harvest credentials and manipulate authentication logs to evade detection.
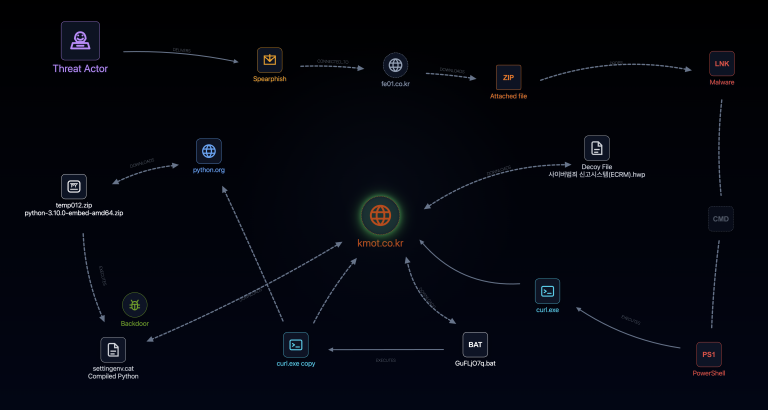
Genians unmasks an APT37 campaign using environment variable tricks and compiled Python malware to bypass EDR. Protect your network from these stealthy lures.
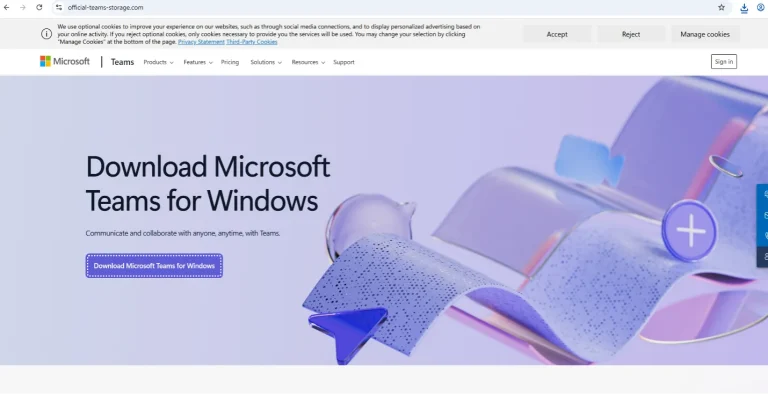
BlueVoyant unmasks "Lorem Ipsum": a well-funded campaign using SEO poisoning and signed MS Teams installers to deploy stealthy backdoors via image files.
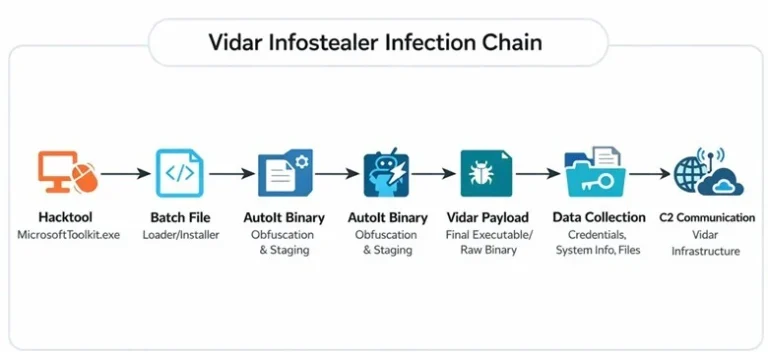
LevelBlue unmasks a stealthy Vidar Stealer campaign using AutoIt scripts and file renaming tricks to bypass EDR and harvest credentials. Is your system at risk?