 Do Son
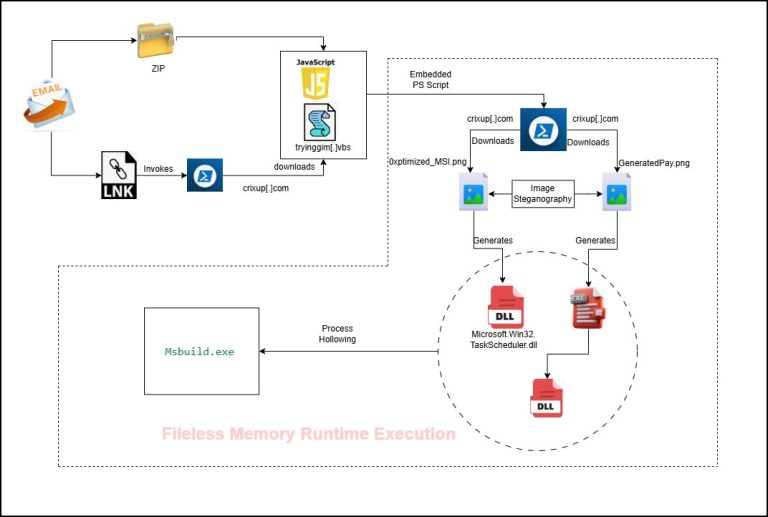
Trellix uncovers PureRAT, a modular Trojan hiding malware in PNG images. Learn how it uses steganography and fileless delivery to bypass Windows security.
Malware
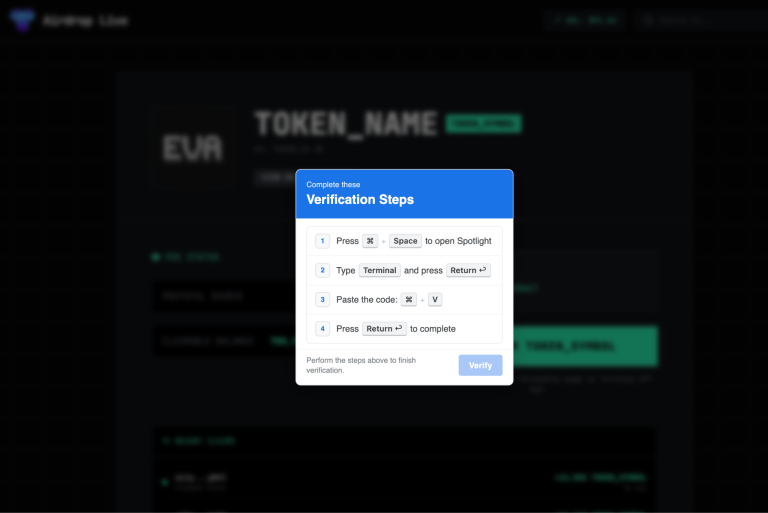
Netskope uncovers a ClickFix macOS campaign that holds the UI hostage to steal system passwords, Keychains, and 200+ browser extensions.
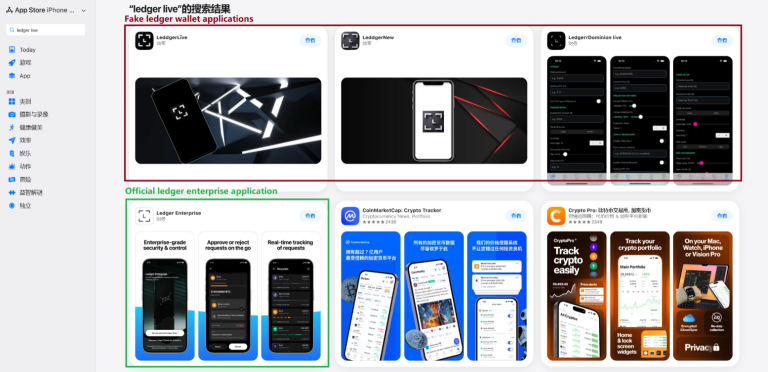
Kaspersky unmasks "FakeWallet," a Trojan on the Apple App Store using stubs & enterprise profiles to steal crypto seed phrases. Learn how to protect your keys.
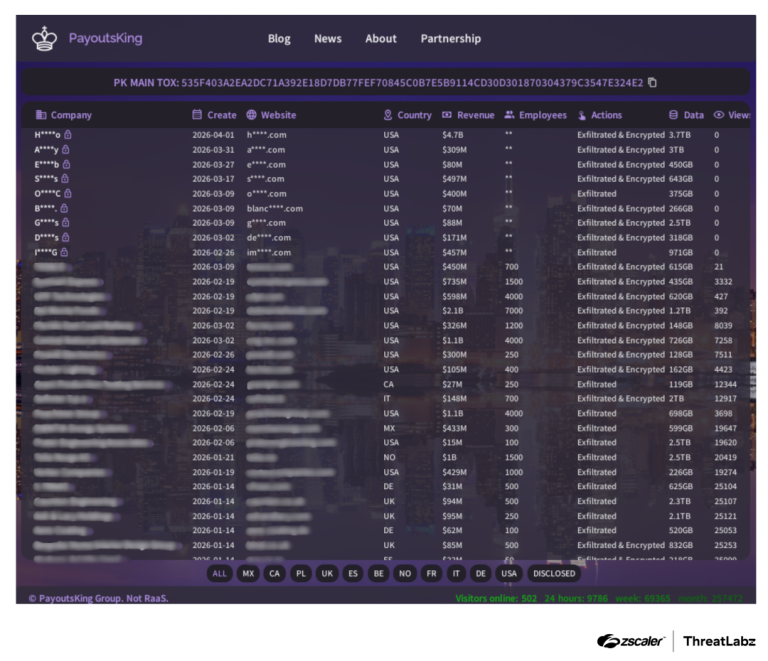
Payouts King, the successor to BlackBasta, uses vishing and direct syscalls to bypass EDR and strike global targets. Learn how to defend your enterprise.
Splunk STRT identifies a new campaign bundling Ghost RAT with CloverPlus adware to steal RDP credentials and monetize infections. Patch your systems now!
CYFIRMA uncovers an elite stealth framework hijacking signed Intel utilities via AppDomain Manager. It targets EMEA finance with undetectable memory-only code.
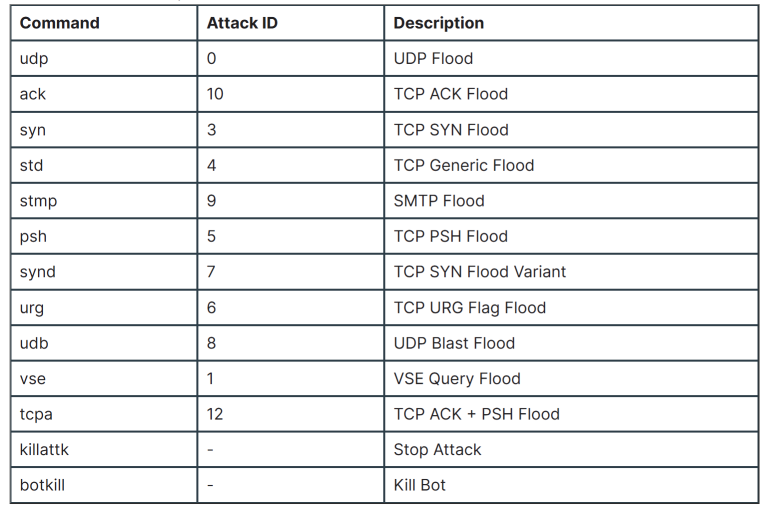
FortiGuard unmasks Nexcorium, a Mirai variant targeting DVRs via CVE-2024-3721. Secure your IoT devices against this multi-arch DDoS botnet. Patch now!
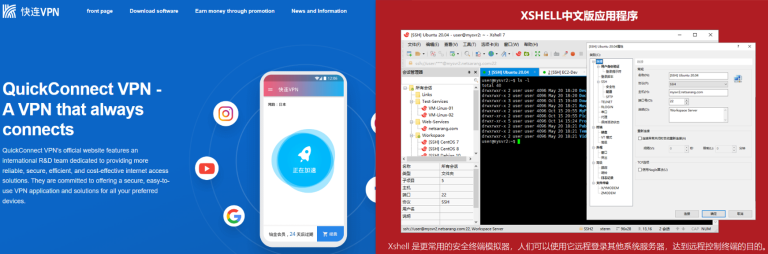
Kong RAT: A year-long SEO poisoning campaign targeting developers with trojanized SSH/VPN tools and .NET NativeAOT stealth. Learn how to stay protected.
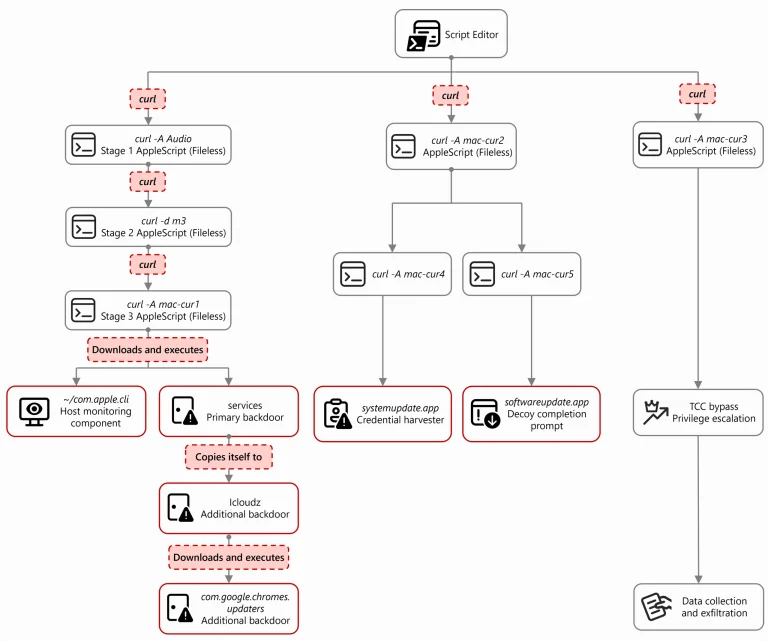
Microsoft uncovers Sapphire Sleet's macOS campaign. Using fake recruiters and AppleScript, they bypass TCC to steal crypto wallets, Telegram, and SSH keys.
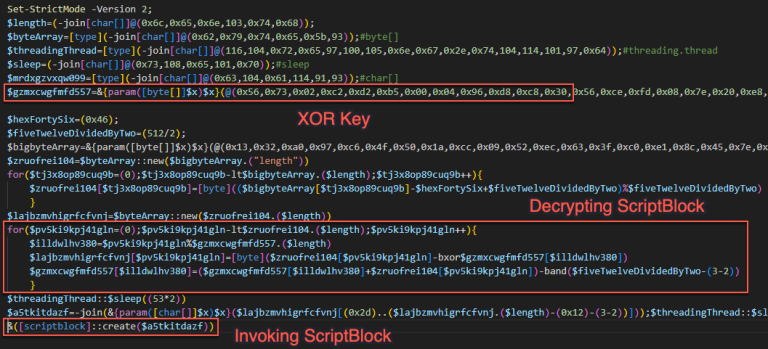
Rapid7 uncovers a fake Claude AI installer using ClickFix techniques to bypass AMSI and inject shellcode. Stay safe from this sophisticated AI-themed threat.

BitSight unmasks RondoDox: a modular botnet using "nanomites" to dodge debuggers while hijacking 18 architectures for Monero mining and gaming DoS attacks.

Darktrace uncovers ZionSiphon, a malware strain targeting water treatment via Modbus logic. Discover the new frontier of Israel-focused industrial sabotage.
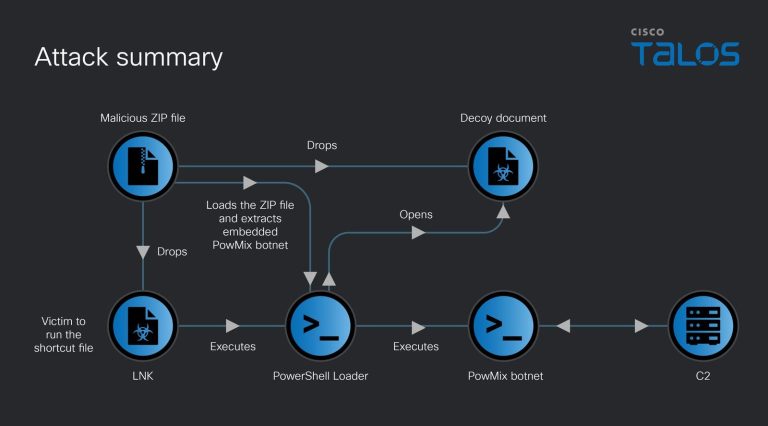
Cisco Talos uncovers PowMix, a stealthy botnet targeting Czech HR via AMSI bypass and Heroku-hosted C2. Learn how this malware evades modern EDR systems.
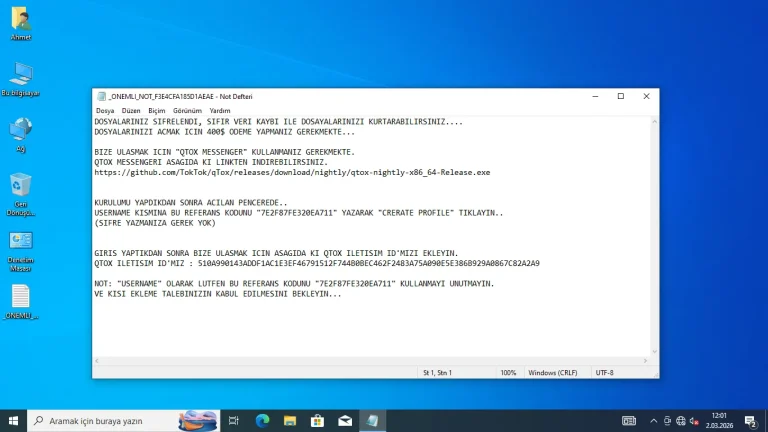
Acronis uncovers JanaWare, a persistent ransomware targeting Turkey since 2020. Discover how geofencing and polymorphism keep this threat in the shadows.
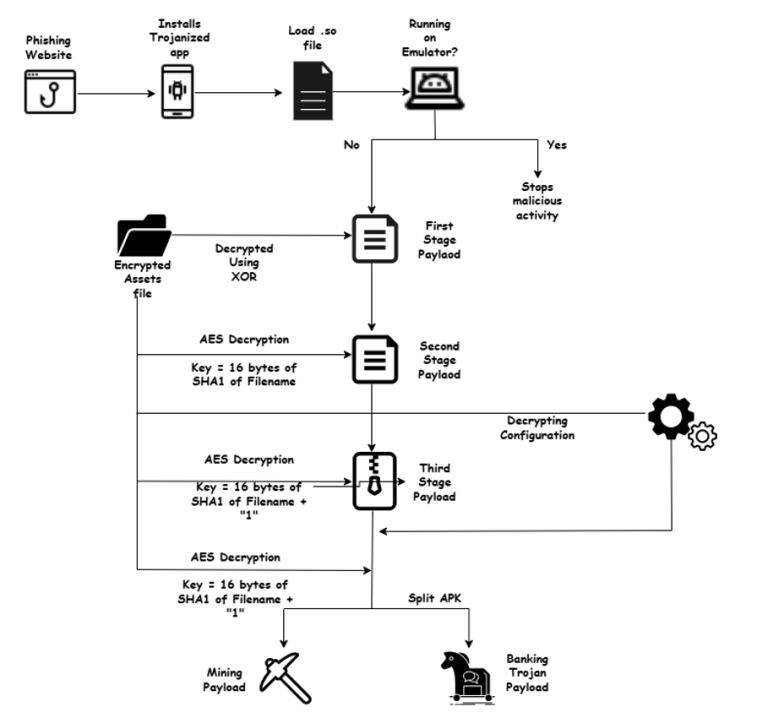
Cyble reveals MiningDropper, a modular Android threat delivering RATs and infostealers via multi-stage payloads. Protect your mobile devices now.
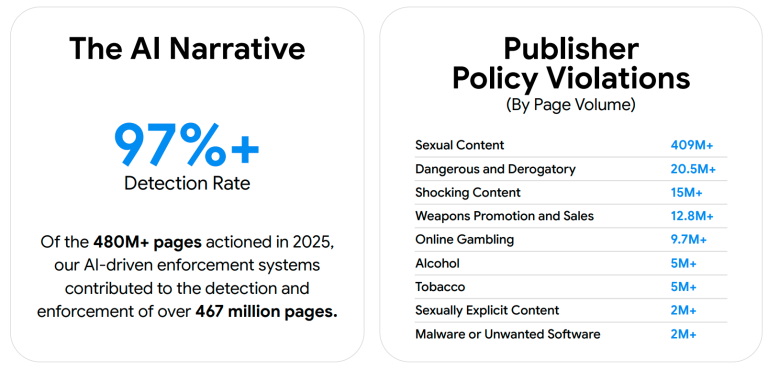
Google’s 2025 Ads Safety Report reveals how Gemini AI intercepted 99% of bad ads and reduced false account suspensions by 80%. Read the full scale of the defense.
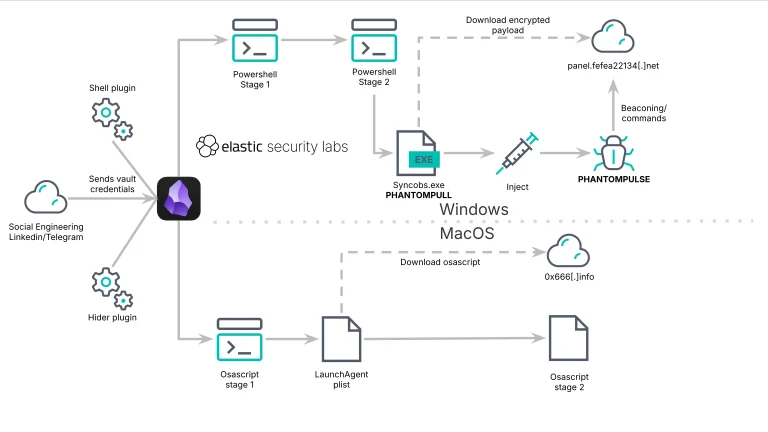
Elastic uncovers PHANTOMPULSE: A novel RAT abusing Obsidian plugins and blockchain C2. Stay safe from this AI-assisted campaign targeting crypto firms.
PolinRider targets 1,900+ GitHub repos using "history-falsification" to hide malware. DPRK's Lazarus Group uses fake job tests to breach developers.
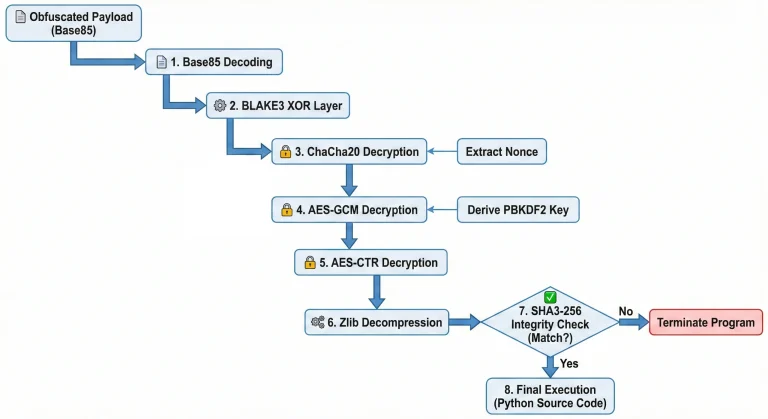
InfoGuard unmasks VIPERTUNNEL, a Python backdoor using sitecustomize.py for stealthy persistence in DragonForce ransomware attacks. Learn how to detect it.
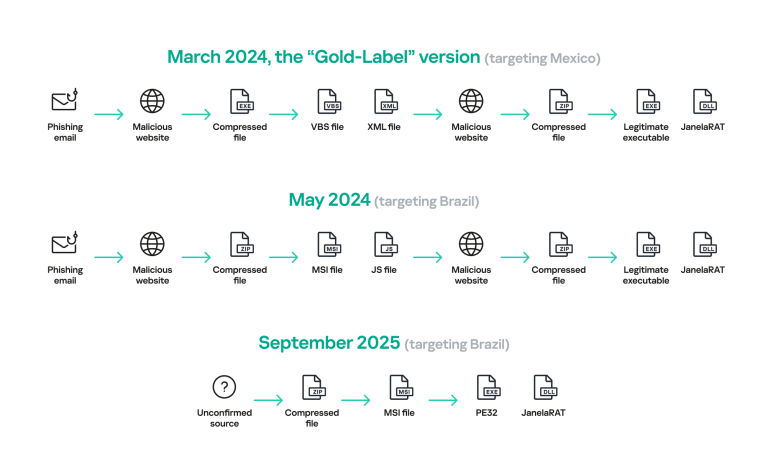
JanelaRAT targets banking users in Brazil and Mexico using window monitoring and fake updates. Learn how this 2026 threat bypasses MFA to hijack sessions.
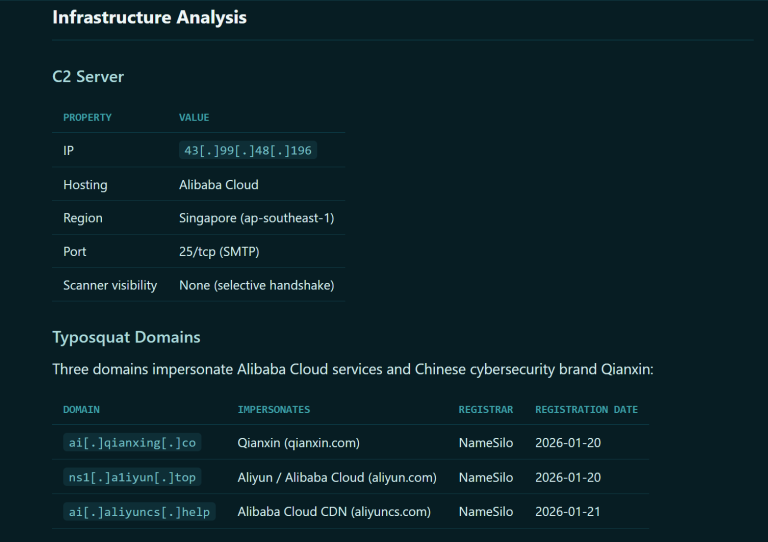
APT41's new zero-detection ELF backdoor uses SMTP (Port 25) to hijack Linux cloud workloads invisibly. Secure your credentials—audit your SMTP traffic today.
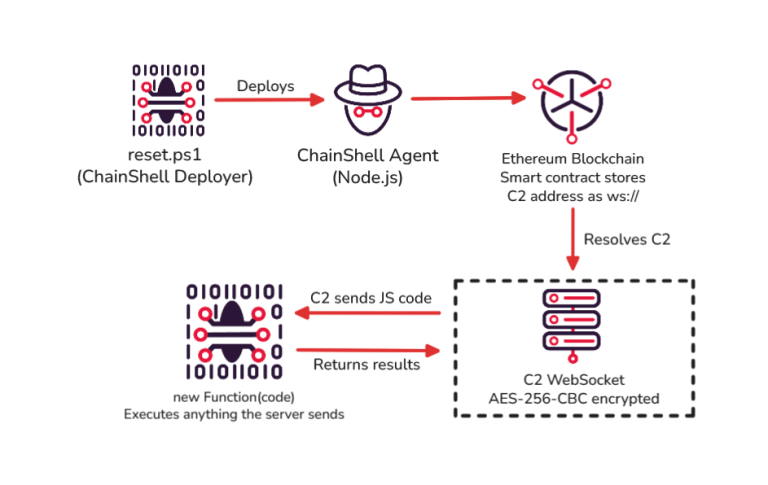
Iranian state actor Muddy Water adopts CastleRAT and ChainShell to hijack browsers and bypass MFA invisibly. A professional-grade shift in APT strategy.