 Do Son
Securonix uncovers FAUX#ELEVATE, a 25-second attack using 10MB "inflated" VBScripts to steal credentials and mine crypto in French corporate environments.
Malware

Axios versions 1.14.1 & 0.30.4 have been poisoned. A hijacked maintainer account is dropping a RAT via postinstall scripts. Revert to safe versions now!
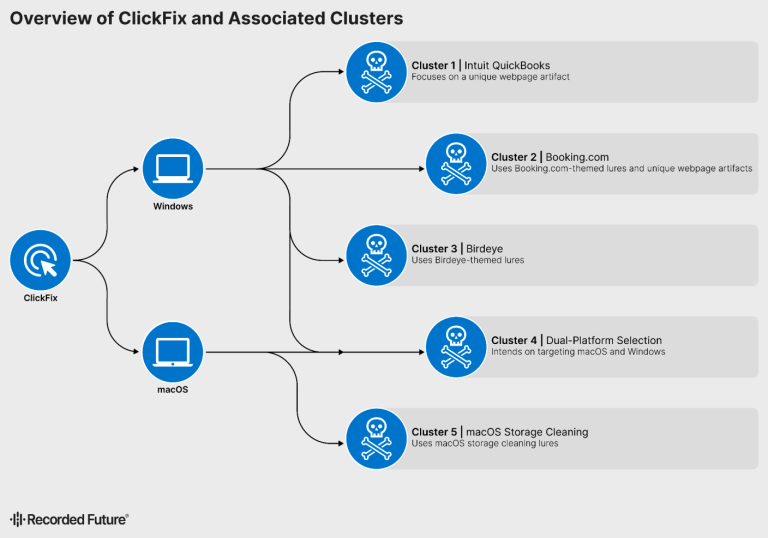
ClickFix has evolved into a high-ROI malware template used by APT28. Learn how this social engineering trick bypasses security by mimicking system errors.
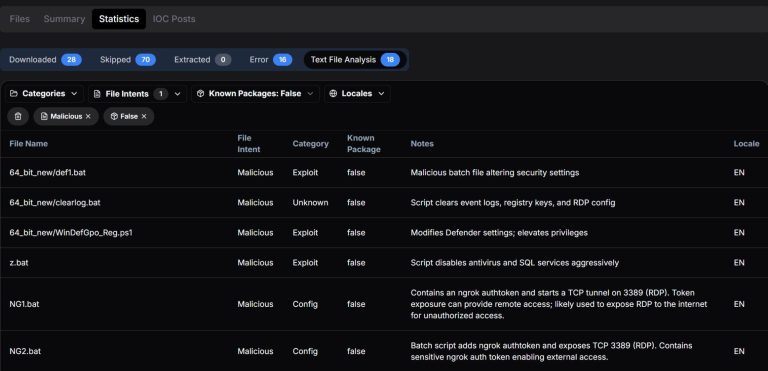
Hunt.io uncovers a Gentlemen ransomware toolkit on a bulletproof host. Learn how the z1.bat script destroys defenses and backups before encryption.
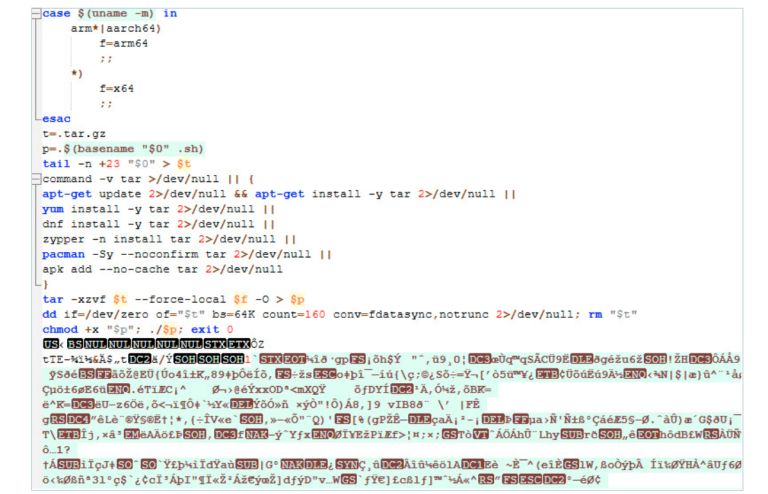
Morphisec uncovers Pay2Key’s Linux evolution. This dual-arch ransomware disables SELinux and AppArmor to encrypt x64/ARM64 servers. Secure your infra today!

LevelBlue SpiderLabs unmasks the PhantomVAI framework: a multi-stage, fileless attack hiding XWorm and Remcos RAT inside obfuscated VBS and PNG files.

Netskope uncovers TroyDen’s Lure Factory, an AI-powered operation using 300+ trojanized GitHub repos and a 29,000-year sleep to steal credentials.
Malwarebytes uncovers a PureHVNC RAT campaign using Google Forms to bait professionals. Learn how this stealthy infection chain targets 2026 business docs.

LevelBlue uncovers MioLab (Nova), a premium macOS MaaS targeting crypto wallets, Keychains, and Apple Notes. Protect your BIP39 seeds and Mac today.

Jamf Threat Labs uncovers GhostClaw, a macOS threat exploiting GitHub stars and AI workflows to steal credentials. Protect your dev environment today!

Elastic Security Labs uncovers SILENTCONNECT, a stealthy loader using Cloudflare and Google Drive to deliver RMM tools for "hands-on keyboard" attacks.
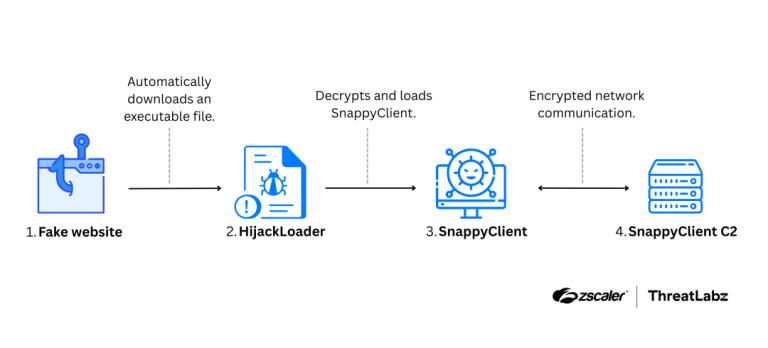
Zscaler ThreatLabz unmasks SnappyClient, a C++ C2 framework linked to HijackLoader. It uses AMSI bypass and Heaven’s Gate to steal crypto and gain remote access.
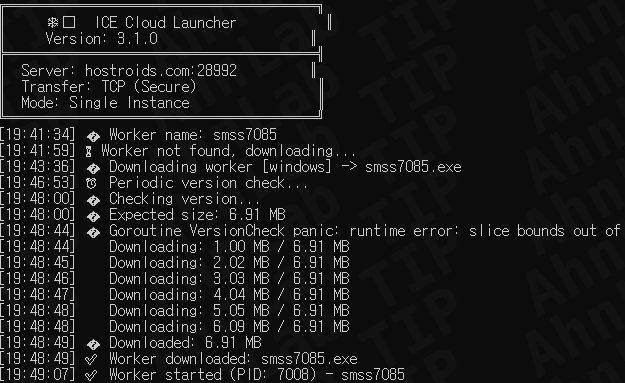
Larva-26002 strikes again with "ICE Cloud," a Go-based scanner using AI-assisted code to hijack MS-SQL servers. Discover the technical breakdown and defense.

Gen Threat Labs uncovers VoidStealer, the first malware using a debugger-based bypass to extract Chrome and Edge encryption keys via hardware breakpoints.
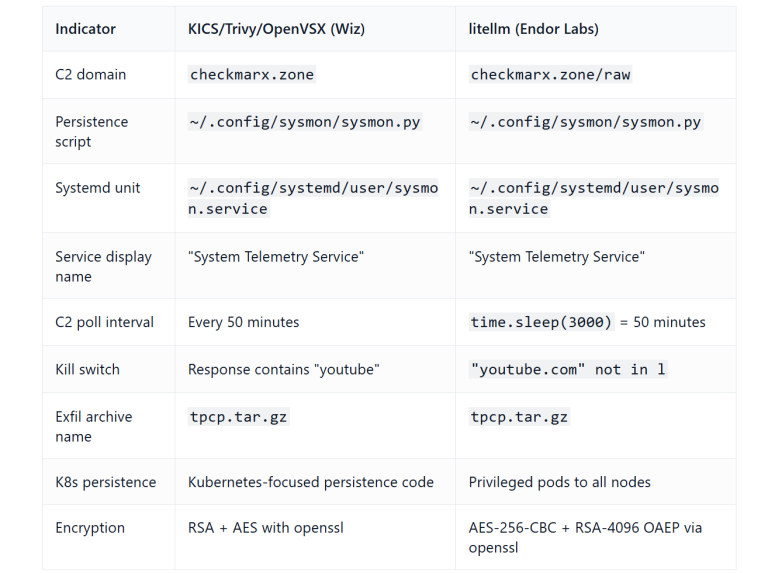
95M-download LiteLLM library hijacked on PyPI. TeamPCP's backdoor steals cloud tokens and hijacks Kubernetes clusters. Check for version 1.82.8 now.

Sophos uncovers Keenadu, a persistent Android firmware backdoor embedded in core libraries that gives attackers total control via the Zygote process.

Checkmarx warns of a supply chain breach on the OpenVSX registry and KICS GitHub Action. Malicious plugins were active briefly on March 23. Update now.

Trend Micro uncovers a selective PureLog Stealer campaign using fake legal notices and fileless execution to target healthcare and government sectors.
Researchers reveal Infostealer.Speagle, a "parasitic" malware hijacking Cobra DocGuard infrastructure to mask the theft of sensitive ballistic missile data.
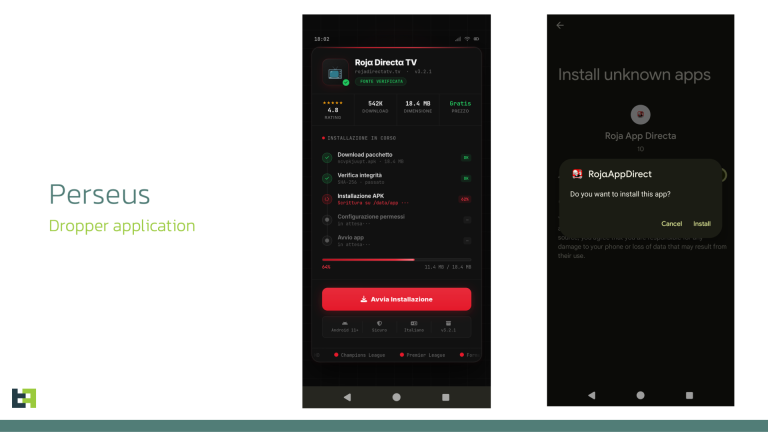
ThreatFabric uncovers "Perseus," an evolved Android malware targeting note-taking apps to steal recovery phrases and private data via accessibility services.
Beware of "MacSync Stealer": A new macOS malware campaign using SEO poisoning and terminal commands to hijack crypto wallets and system keys.
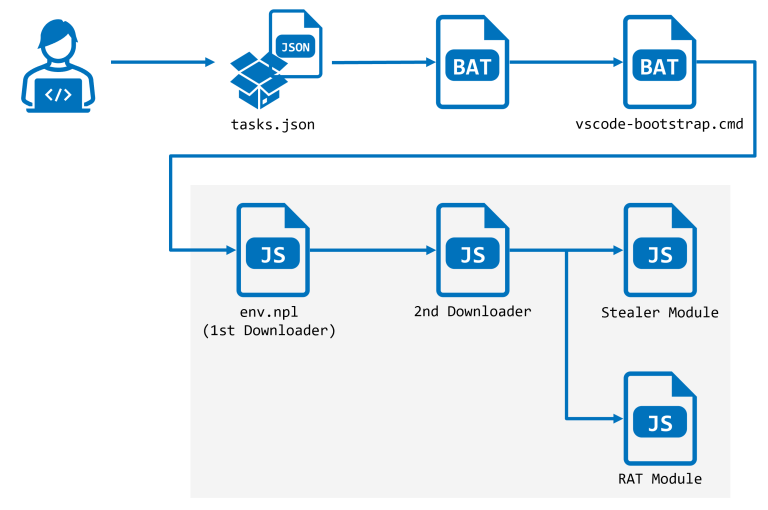
Researchers uncovered StoatWaffle, a new Node.js malware by North Korean hackers targeting developers via malicious VSCode repositories to steal data.