 Do Son
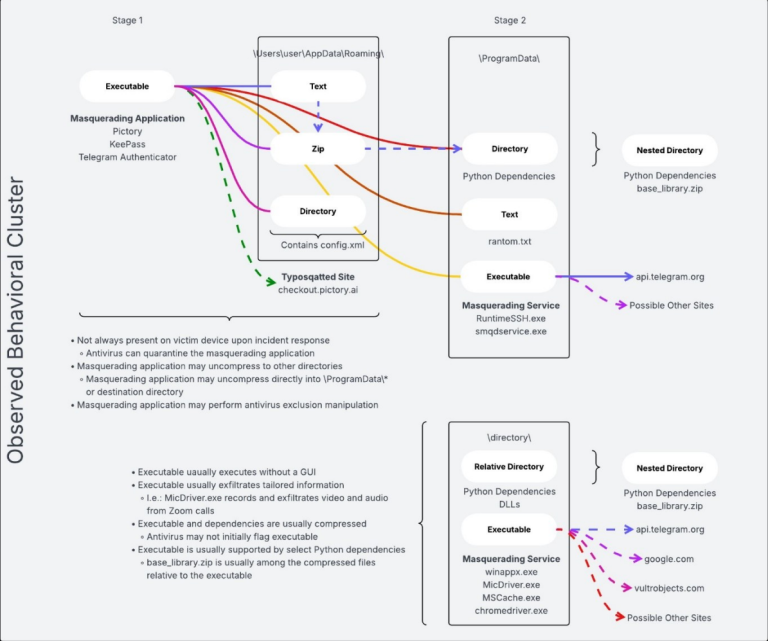
The FBI warns that Iran's MOIS is weaponizing Telegram as a Command-and-Control hub to deploy malware against global dissidents and journalists.
Malware
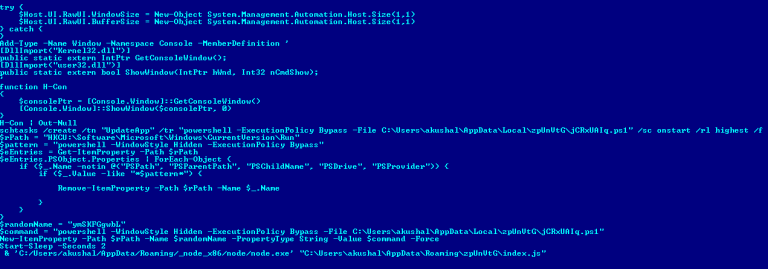
Bitdefender uncovers a malicious Windsurf IDE extension using the Solana blockchain as an unblockable C2 to steal developer credentials and source code.
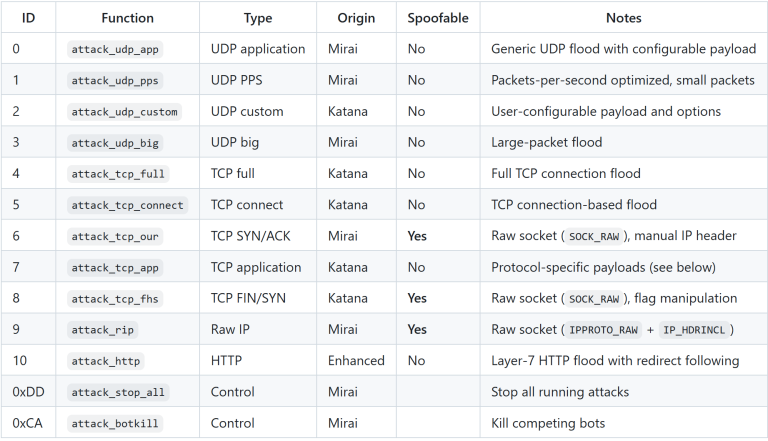
Nokia researchers uncover the Katana botnet, a Mirai variant using custom rootkits to hijack unmanaged Android TV boxes in a massive IoT turf war.

Hunt Intelligence uncovers the "Hex" botnet, a stealthy campaign using stolen SSH credentials and on-host compilation to evade traditional binary scanners.

Eclypsium uncovers two new Linux malware strains: a CondiBot DDoS variant and the Monaco SSH cryptominer targeting servers and IoT. Secure your network.

Acronis uncovers a massive campaign targeting gamers with fake cheats to deliver Vidar Stealer 2.0, a highly evasive malware stealing crypto and passwords.

The US DOJ, alongside Canada and Germany, has dismantled four massive IoT botnets responsible for record-breaking 30 Tbps DDoS attacks worldwide.

Researchers uncover a fake Telegram site distributing stealthy, memory-resident malware that bypasses Windows Defender. Always verify your download URLs.
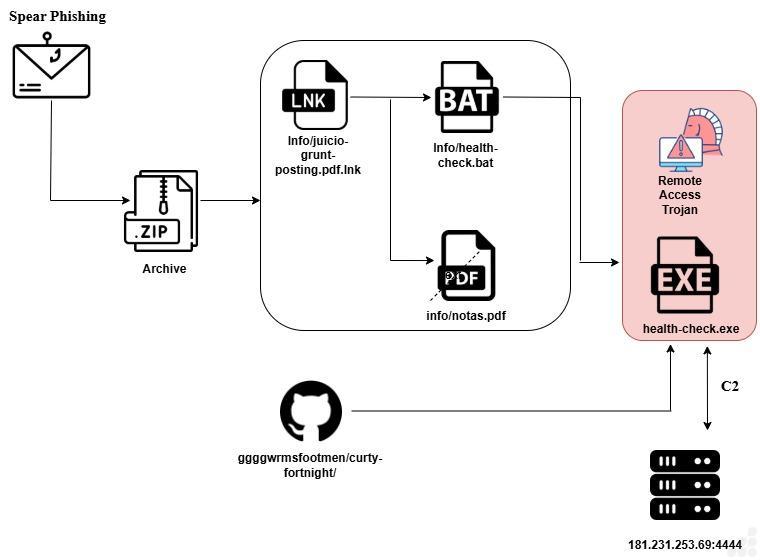
Lat61 Threat Intelligence uncovers a stealthy Rust RAT targeting Argentina's legal sector via weaponized judicial PDFs. Learn about its evasion tactics.

Trend Micro reveals Warlock ransomware is using kernel-level BYOVD attacks and abused IT tools to bypass security and hijack Active Directory.
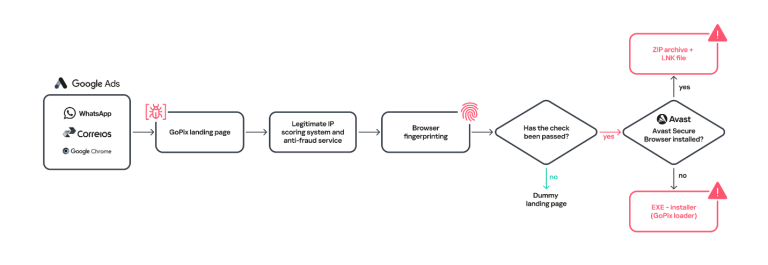
Kaspersky Labs details GoPix, a highly advanced Brazilian banking Trojan using memory-only implants and MitM attacks to target Pix and crypto.

Amazon threat intel reveals Interlock ransomware is actively exploiting a critical 10.0 CVSS Cisco zero-day (CVE-2026-20131) to hijack firewall networks.

StepSecurity uncovers a supply chain attack where a verified GitHub org, dev-protocol, was hijacked to spread malicious Polymarket bots and steal crypto.

Rapid7 exposes a global ClickFix campaign hijacking WordPress sites with fake Cloudflare CAPTCHAs to deliver stealthy infostealers and drain digital wallets.

Aryaka Threat Labs exposes BlackSanta, a Russian-linked malware targeting HR teams with fake resumes to deploy an EDR-killer and steal crypto wallets.

Uncontrolled access to weaponizable AI empowers both cybercriminals and state-sponsored actors. Learn how defenders can prepare for this emerging threat.

Socket Research exposes how GlassWorm malware abuses Open VSX dependencies for transitive delivery of an RCE backdoor using Solana blockchain dead drops.

LAB52 uncovers the DRILLAPP backdoor, a novel espionage campaign targeting Ukraine that weaponizes Microsoft Edge for screen recording and surveillance.

Socket uncovers a Packagist supply chain attack targeting Vietnamese OphimCMS streaming sites with trojanized themes linked to sanctioned entity FUNNULL.

Aikido uncovers a supply chain attack via AstrOOnauta, backdooring two popular React Native packages to steal crypto wallets and developer credentials.
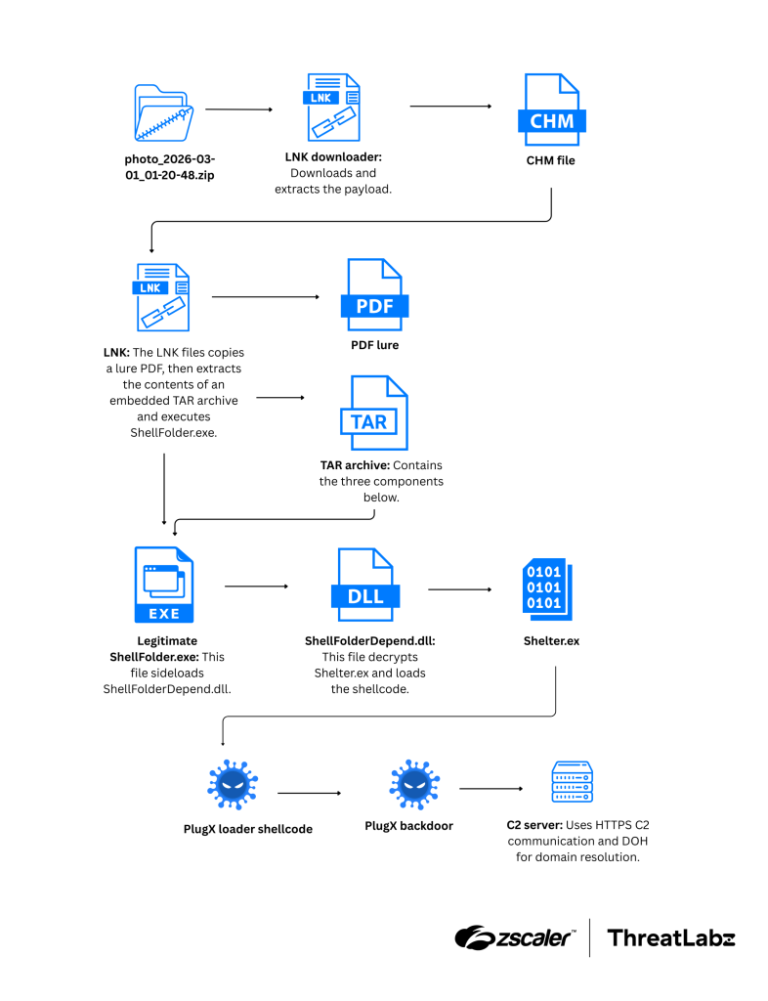
ThreatLabz reveals how China-nexus actor Mustang Panda weaponized Middle East conflict lures to deploy a stealthy PlugX backdoor within 24 hours.
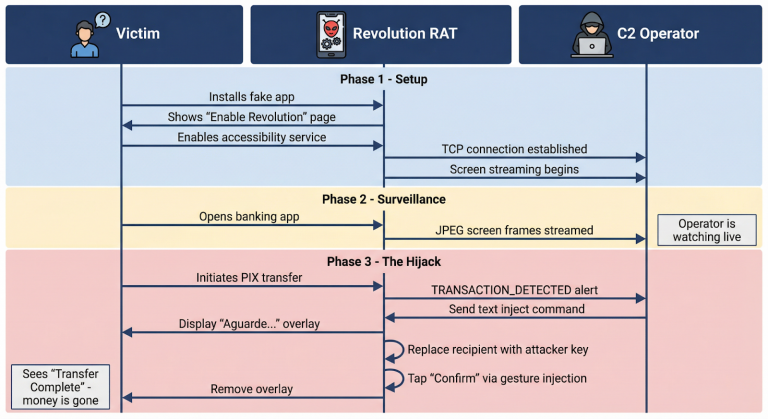
Zimperium's zLabs exposes PixRevolution, a novel Android banking trojan using real-time surveillance to hijack Brazil's PIX instant payments.