
 Do Son
Security researchers uncover a massive macOS malware campaign using "cracked" audio plugins and "ClickFix" tactics to deliver Odyssey and MacSyncStealer.
Malware
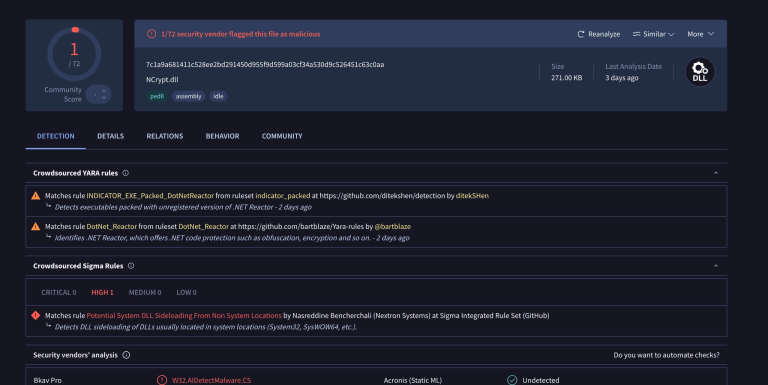
Socket researchers uncover a NuGet supply chain attack using "NCryptYo" to hijack ASP.NET apps. Attackers inject backdoors into production authorization layers.

Genians report reveals MuddyWater APT's shift to Rust-based malware and RMM tool abuse for long-term espionage across government and critical infrastructure.

Group-IB exposes Operation Olalampo: MuddyWater's new MENA campaign using AI-assisted Rust malware (CHAR) and Telegram bots for stealthy C2 communication.
FortiGuard Labs exposes a massive Silver Fox APT campaign targeting Taiwan. Hackers use tax-themed phishing and BYOVD attacks to deploy Winos 4.0 malware.

Malwarebytes exposes a deceptive campaign using fake Windows 11 Facebook ads to trick users into downloading stealthy info-stealing malware.
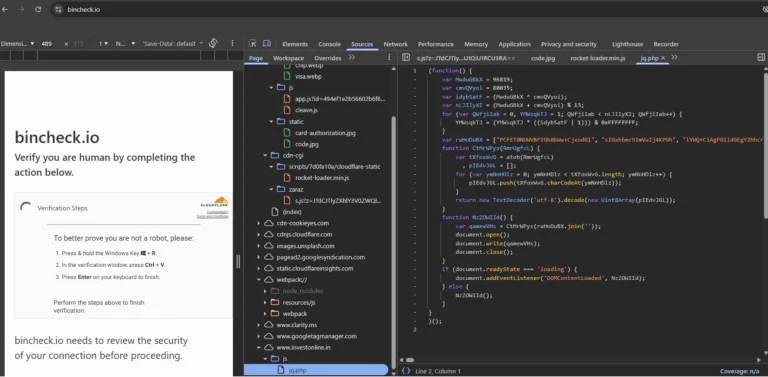
Elastic Security Labs uncovers a ClickFix campaign turning human helpfulness into a weapon. Fake verifications deploy the fileless MIMICRAT via PowerShell.

Unit 42 warns of active attacks on critical BeyondTrust flaw CVE-2026-1731. Hackers bypass auth for RCE and data theft. Patch self-hosted instances now.
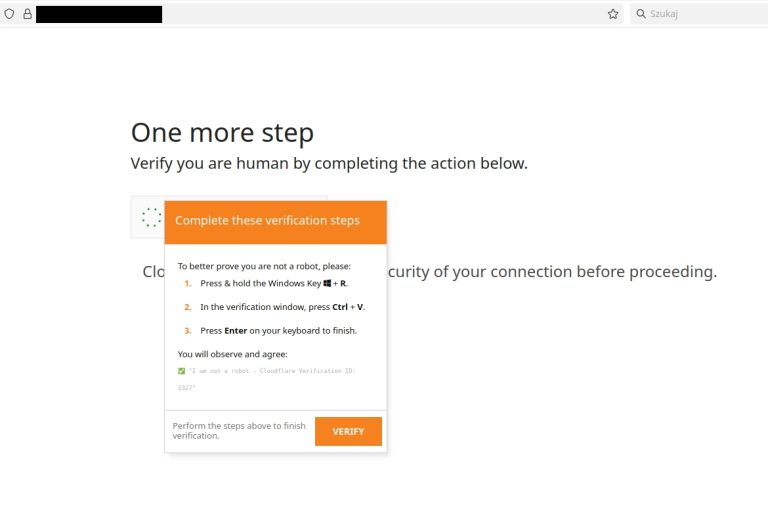
CERT Polska reveals how a fake "ClickFix" CAPTCHA campaign tricked users into deploying evasive Latrodectus and Supper malware. Protect your network now.
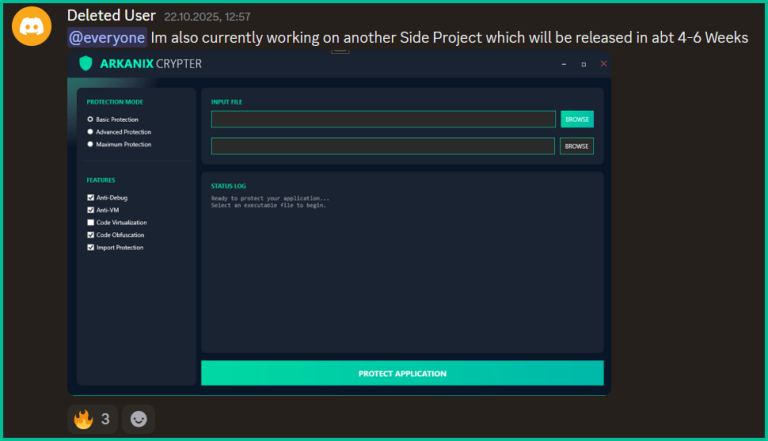
Kaspersky exposes Arkanix Stealer, a fast-moving MaaS operation leveraging Discord, tiered subscriptions, and AI-assisted development for quick data theft.
The FBI warns of a massive surge in ATM jackpotting attacks. Cybercriminals are using Ploutus malware to bypass the XFS layer and drain cash reserves.
Insikt Group exposes GrayCharlie compromising WordPress sites & US law firms. Attackers use "ClickFix" fake CAPTCHAs to deploy the NetSupport RAT.
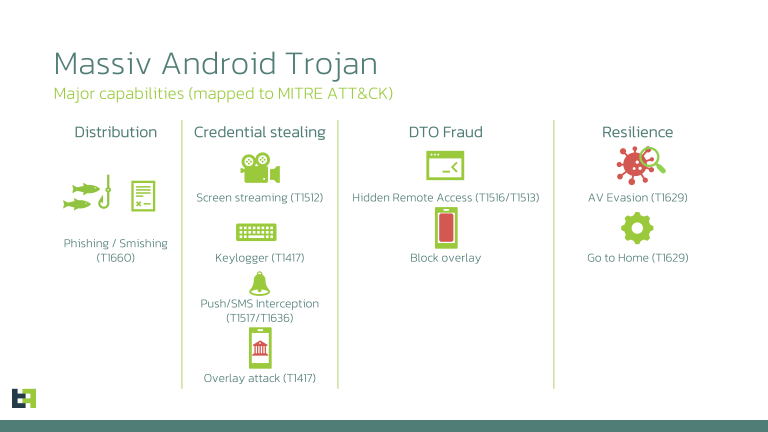
ThreatFabric exposes Massiv, a new Android banking Trojan hiding in fake IPTV apps. The malware uses accessibility permissions for full device takeover.

Texas AG Ken Paxton sues TP-Link, alleging the Wi-Fi giant's routers act as Trojan horses for CCP surveillance. State bans TP-Link gear for employees.

Google's VP Vijaya Kaza reveals 1.75M bad apps blocked in 2025. Android 16 introduces one-line tapjacking protection to fight AI-powered cyber threats.

Point Wild reveals a new Remcos RAT variant abandoning local storage for real-time webcam streaming, memory evasion, and aggressive anti-forensics.
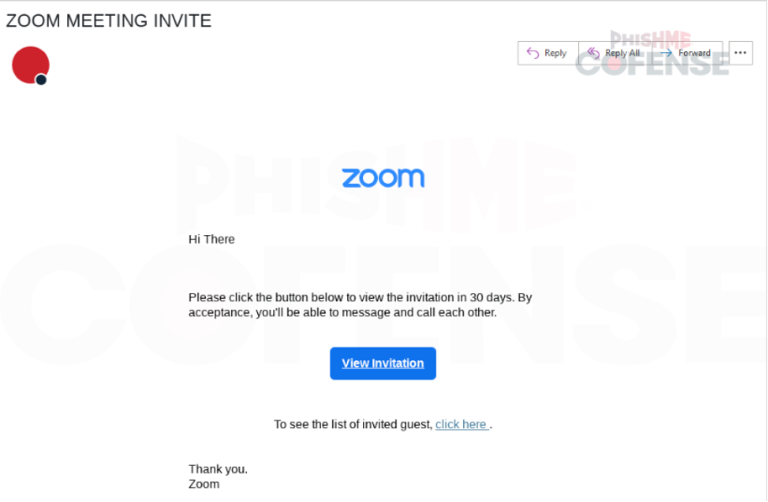
Cybercriminals are using fake DocuSign emails and the JWrapper framework to stealthily deploy SimpleHelp remote access tools. Learn how to spot the threat.

Acronis uncovers CRESCENTHARVEST, a new spyware targeting Iranian dissidents. Attackers use protest lures & Google DLL sideloading to steal data.
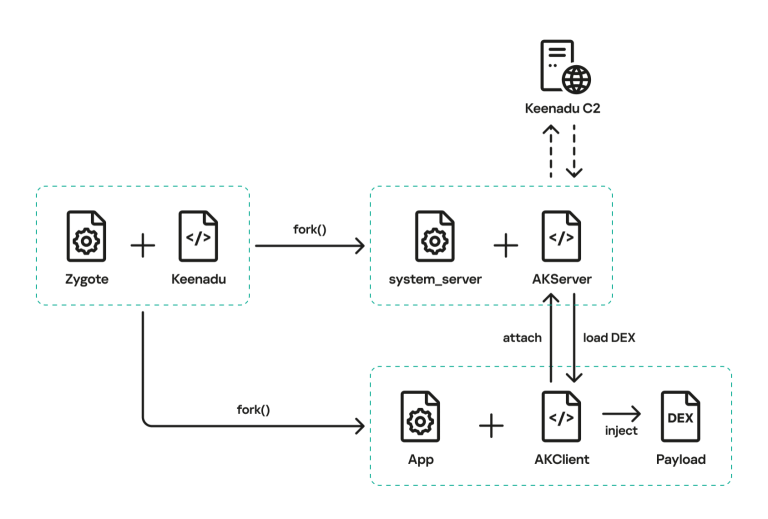
Kaspersky uncovers Keenadu, a firmware-level Android backdoor infecting the Zygote process. This pre-installed malware gives attackers full control.
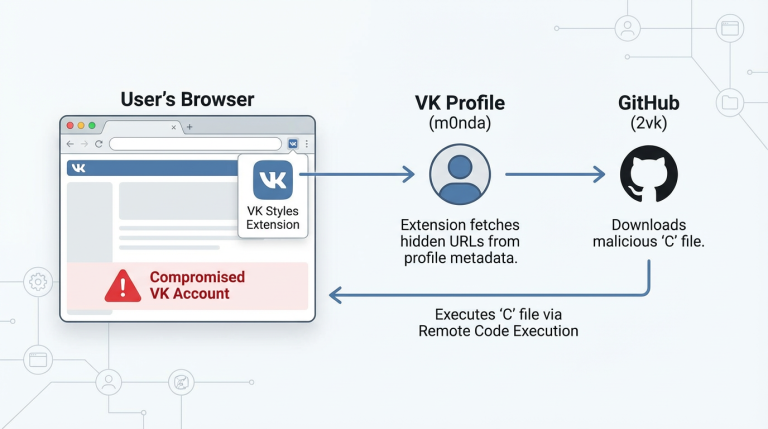
500k VK accounts hijacked by "VK Styles" extensions. Malware forces subscriptions and bypasses CSRF tokens. Remove the extension immediately.
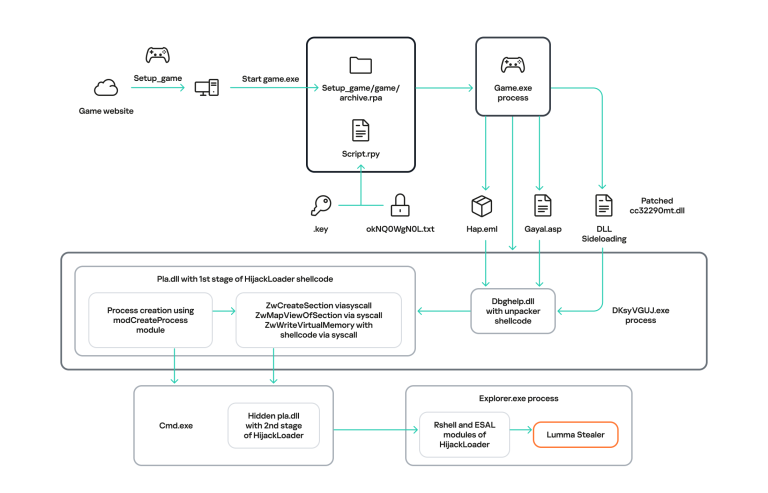
Kaspersky warns: Pirated visual novels are spreading RenEngine malware. Attackers use fake downloads to install ACR Stealer. Protect your data now.
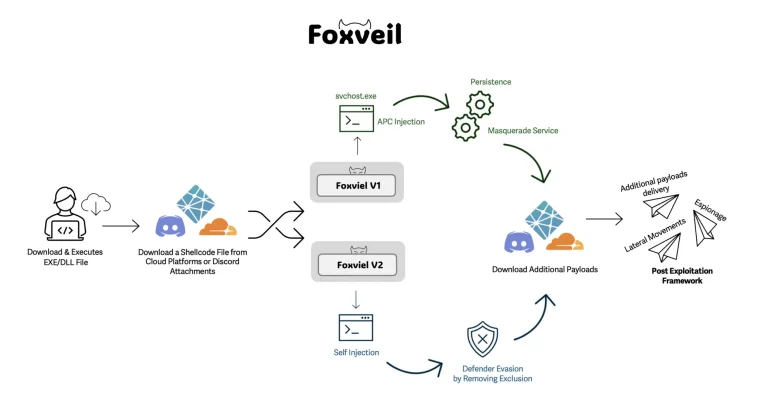
Cato CTRL discovers Foxveil, a new malware loader abusing Cloudflare, Netlify & Discord to bypass defenses. Active since Aug 2025. Learn the signs.