
 Do Son
Critical dYdX supply chain attack: Compromised npm & PyPI packages steal seed phrases & deploy RATs. Remove @dydxprotocol/v4-client-js immediately.
Malware

Zscaler reveals Marco Stealer, a new malware harvesting crypto & cloud files. It uses AES-256 encryption & kills analysis tools. Learn how to detect it.

Darktrace finds Mac malware using a fake "Compatibility Wizard" to trick users. The AppleScript attack bypasses TCC to drop a Node.js backdoor.

Cisco Talos exposes DKnife, a router malware that inspects traffic and swaps legitimate downloads for ShadowPad backdoors. Active since 2019.

TGR-STA-1030 (UNC6619) hits 70+ orgs in 37 countries. The Asia-based group uses the new ShadowGuard eBPF rootkit to hide in Linux kernels.

Stan Ghouls group targets Uzbekistan via fake court emails and malicious Java loaders. Learn how they deploy NetSupport RAT to spy on victims.

APT28 (Fancy Bear) weaponized CVE-2026-21509 in 24 hours to target NATO. New "BeardShell" and "NotDoor" malware steals emails. Patch Office now.

Silent Push reveals a massive SystemBC botnet with 10,000+ infected IPs. The SOCKS5 proxy malware hit government domains and uses bulletproof hosting.

Microsoft warns of "CrashFix": malicious extensions crash browsers to trick users into running a "fix" that installs a RAT. Beware fake ad blockers.

Darktrace dissects SnappyBee (Deed RAT), a stealthy Salt Typhoon backdoor. Learn how it uses DLL side-loading & memory hooking to evade modern AV.

Silver Fox APT targets users with fake LINE installers delivering ValleyRat. New campaign uses rare "PoolParty" injection to evade detection.
Microsoft warns: Infostealers now target macOS & use WhatsApp worms. "Eternidade" & "Crystal PDF" steal credentials via cross-platform attacks.

Lotus Blossom compromises Notepad++ infrastructure to deploy "Chrysalis" malware. Rapid7 reveals the group using Microsoft Warbird to evade detection.

BlueNoroff hackers use fake "audio issues" on Teams calls to trick macOS users. The "fix" runs terminal commands that steal Keychains. Watch out.

GlassWorm malware found in Open VSX extensions. Hackers stole AWS & SSH keys from macOS devs using Solana C2. 22k+ downloads affected. Check your tools.
New "PhantomVAI" malware recycles old Hackforums "RunPE" code to bypass modern EDR. Campaigns use task scheduler masquerading to deliver infostealers.
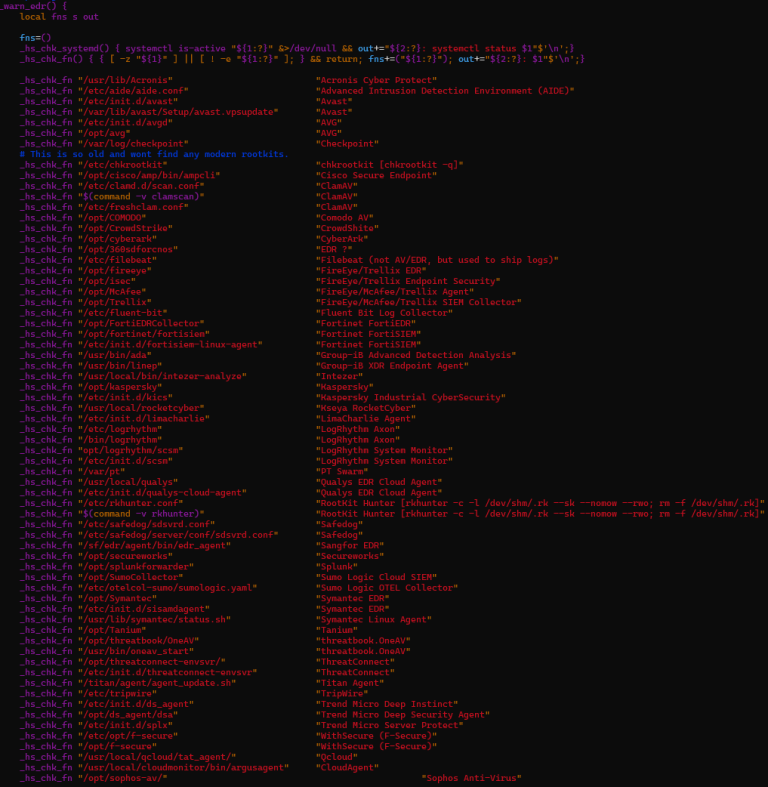
Cyble uncovers "ShadowHS," a fileless Linux malware weaponizing hackshell. It uses GSocket tunneling to evade firewalls and kill rival bots.

APT42 targets defense officials with "TAMECAT," a modular PowerShell backdoor. The malware uses social engineering and Telegram C2 to steal secrets.

In a troubling convergence of trusted developer infrastructure and cybercrime, Bitdefender researchers have uncovered a sophisticated Android...

Interlock ransomware exploits a zero-day in gaming anti-cheat drivers to blind defenses. "Hotta Killer" tool targets education sector. Read the analysis.
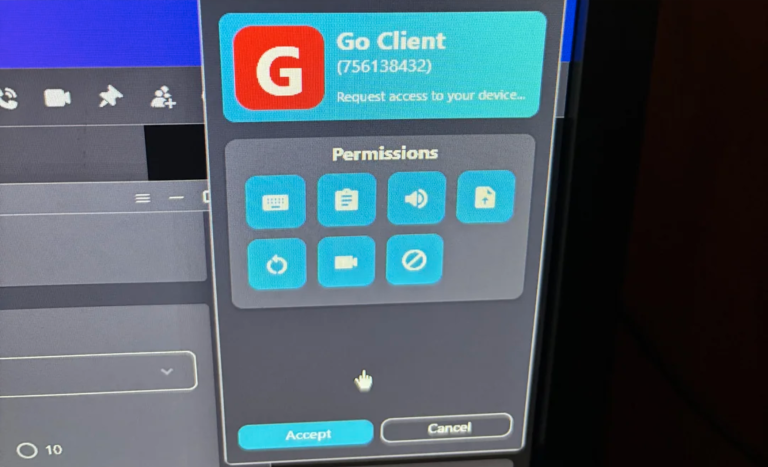
A massive botnet is targeting RustDesk users with fake "Go Client" connection requests. Learn how to lock down your ID and prevent unauthorized remote takeovers.

CERT Polska reveals destructive attacks on energy infrastructure. "Static Tundra" used DynoWiper and LazyWiper to brick OT devices. Read more.