
 Do Son
Zscaler ThreatLabz uncovers Dust Specter, an Iran-linked cyber campaign hijacking Iraqi government infrastructure to deploy custom AI-assisted malware.
Malware

Researcher @goyaramen reveals how PRC threat actors like Mustang Panda use expired domains and Cloudflare to mask their PlugX C2 infrastructure.
IAS Threat Lab unmasks Genisys, a massive AI-powered mobile ad fraud scheme hijacking smartphones to generate fake traffic and steal from advertisers.

Cybersecurity researchers uncover OCRFix, a Russian-linked botnet using EtherHiding and fake CAPTCHAs to mask its C2 servers in blockchain smart contracts.

Socket researchers uncover a Packagist supply chain attack where fake Laravel utility packages secretly install a persistent Remote Access Trojan (RAT).
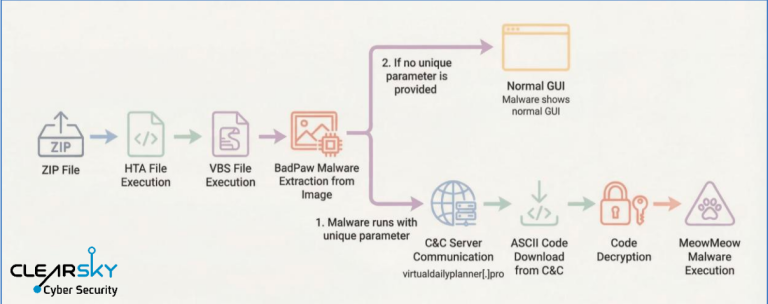
ClearSky uncovers a Russian campaign targeting Ukraine with BadPaw and MeowMeow malware, using steganography and feline decoys for stealthy espionage.

Check Point Research uncovers Silver Dragon, an APT41-linked group using the GearDoor backdoor and Google Drive for stealthy cyber espionage.
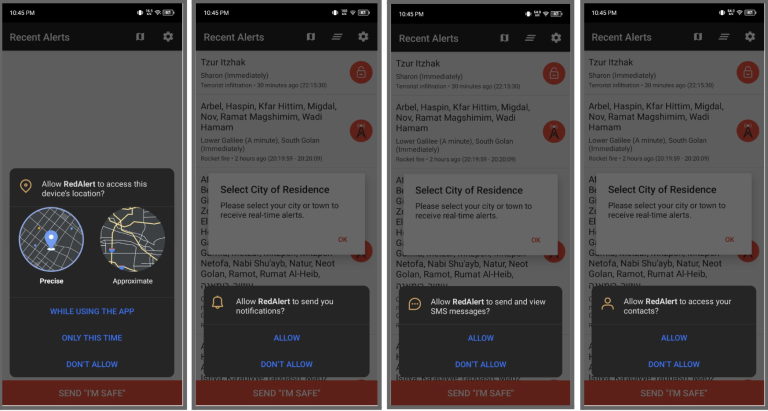
CloudSEK exposes a smishing campaign spreading a trojanized "Red Alert" app. The fake emergency tool tracks locations and steals data during air raids.

Moonlock Lab uncovers a North Korean-aligned malware campaign targeting Web3 pros. Attackers use fake VC profiles and ClickFix CAPTCHAs to deploy malware.

Malwarebytes uncovers a trojanized FileZilla campaign using DLL hijacking and DNS-over-HTTPS to silently steal FTP credentials and bypass security.
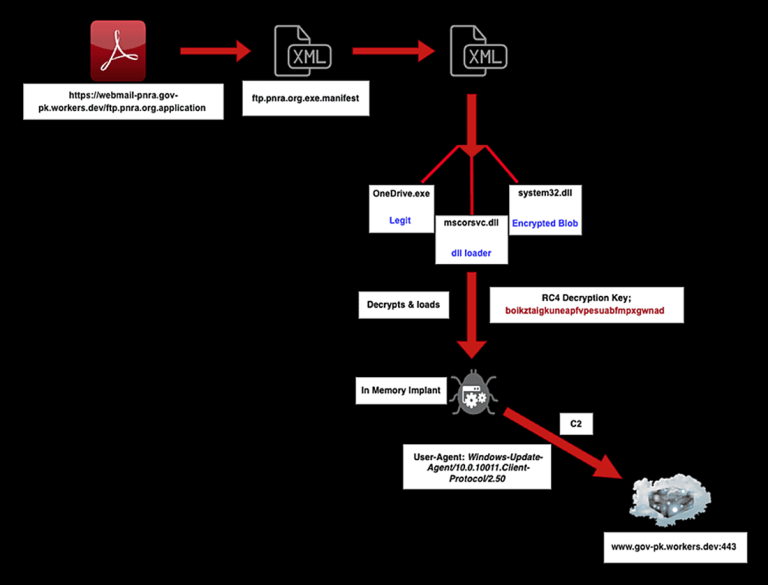
Arctic Wolf details a year-long cyber espionage campaign by Sloppy Lemming, deploying the custom BurrowShell malware against Pakistan and Bangladesh.

Following the Lumma takedown, the sophisticated AuraStealer malware is rapidly gaining ground, using TikTok scams and stealth to harvest data.

LAB52 exposes a new China-aligned espionage campaign using fake meeting invitations and G DATA antivirus components to stealthily deploy the PlugX RAT.

Socket uncovers "StegaBin," a North Korean malware campaign hiding C2 URLs in Pastebin essays to steal developer secrets via 26 typosquatted npm packages.
Akamai SIRT reveals Zerobotv9, a new Mirai-based botnet targeting enterprise n8n workflow platforms and Tenda routers via critical vulnerabilities.

Zscaler unmasked APT37's "Ruby Jumper" campaign, which uses weaponized USBs and cloud services to bypass network isolation and steal data from air-gapped systems.

G DATA reveals how pirated gaming site PiviGames distributes ACRStealer via "spaghetti code" HijackLoader and DLL sideloading, causing total account takeovers.
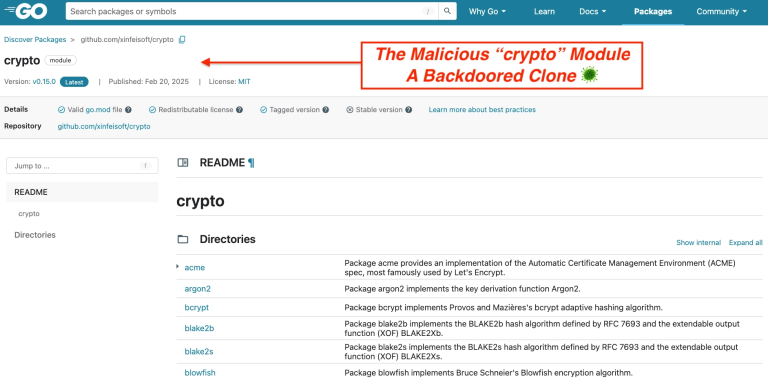
Socket uncovers a malicious Go module mimicking golang.org/x/crypto. It steals passwords via ReadPassword and deploys the Rekoobe backdoor on Linux systems.
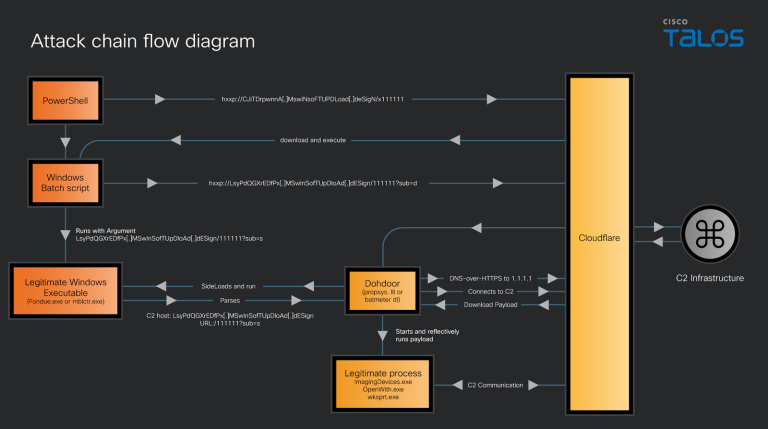
Cisco Talos uncovers "Dohdoor," a stealthy backdoor used by UAT-10027. It abuses DNS-over-HTTPS via Cloudflare to spy on U.S. healthcare and education sectors.
CYJAX uncovers "OCRFix," a stealthy campaign using fake Tesseract OCR sites, ClickFix social engineering, and EtherHiding to bypass security via blockchain.

Tenable uncovers "ambar-src," a malicious npm package mimicking "ember-source." It uses preinstall scripts to deploy reverse shells and Apfell malware.
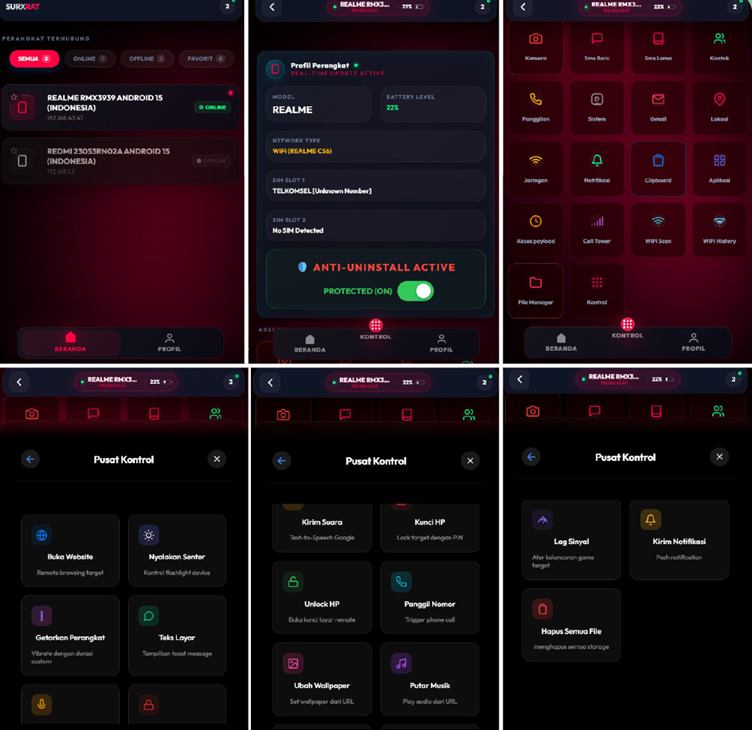
Cyble Research unmasks SURXRAT V5, a professionalized Android RAT experimenting with AI-assisted modules and hybrid monetization via Firebase infrastructure.