 Do Son
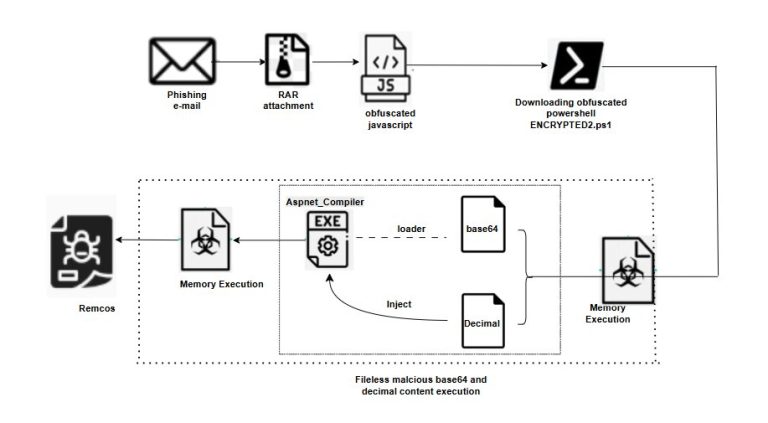
Trellix uncovers a stealthy, fileless Remcos RAT campaign utilizing process hollowing to execute entirely in memory and evade traditional security.
Malware
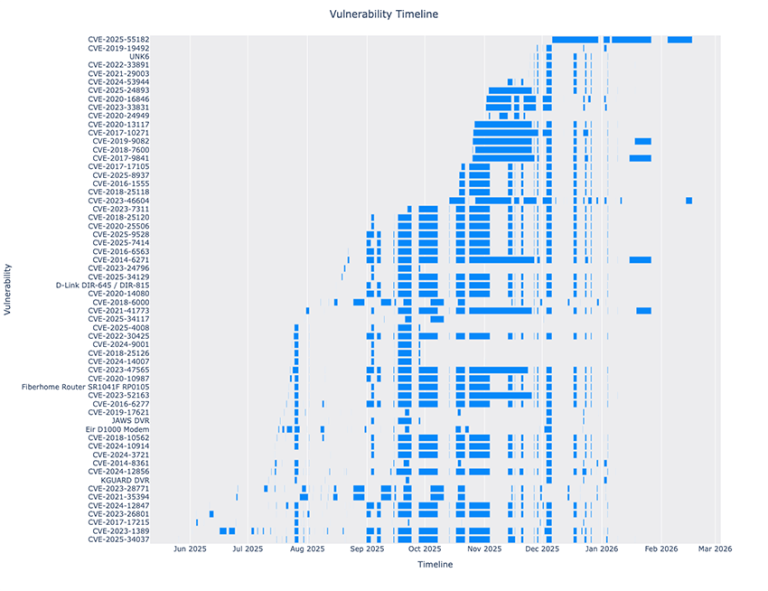
BitSight exposes RondoDox, a relentless IoT botnet using a "shotgun approach" with 174 exploits to hijack residential devices for massive DoS attacks.

BlueVoyant exposes Blitz Brigantine's new tactics: using email bombing, Microsoft Teams lures, and covert DNS MX tunneling to deploy AOBackdoor.
Black Lotus Labs uncovers KadNap, a stealthy P2P botnet infecting over 14,000 Asus routers to fuel the Doppelgänger dark web proxy network.

Unit 42 exposes CL-STA-1087, a suspected Chinese state-sponsored cyber espionage group using custom backdoors to infiltrate Asian military networks.

Trend Micro exposes KongTuke's new "CrashFix" tactic, which tricks enterprise users via fake Chrome errors into deploying the fileless modeloRAT backdoor.

Cyfirma uncovers the RuTaxi Android banking Trojan, a highly persistent malware using VNC capabilities to hijack Russian bank accounts and crypto wallets.
A critical 9.4 CVSS tag poisoning attack (CVE-2026-31976) hit the xygeni-action GitHub Action, injecting a C2 backdoor into CI/CD pipelines. Update now.
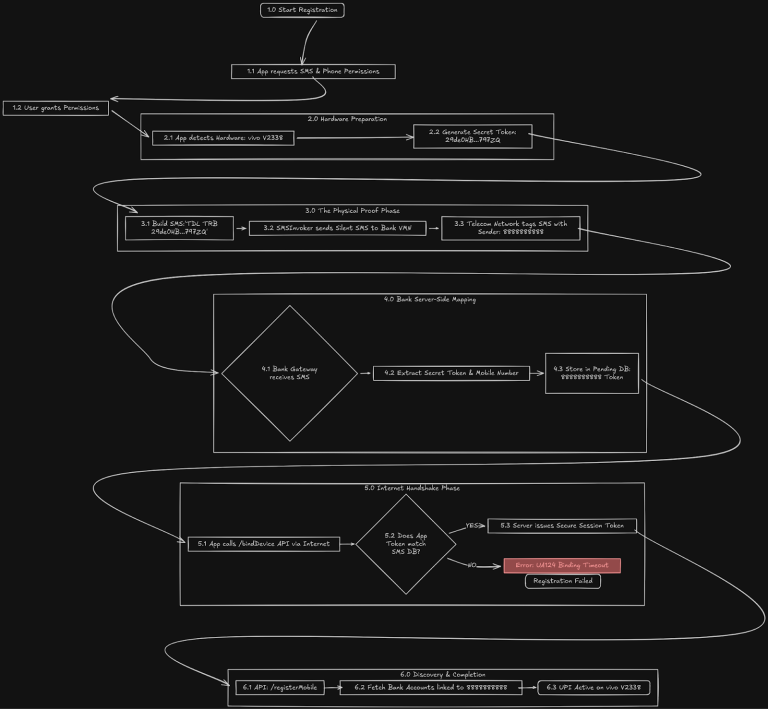
CloudSEK reveals how attackers use LSPosed and the "Digital Lutera" module to bypass Android UPI SIM-binding, gaslighting payment apps for remote fraud.

Once a "Featured" tool, the ShotBird extension now delivers malware via "vibecoded" scripts and fake updates. Remove it now to protect your passwords and data.
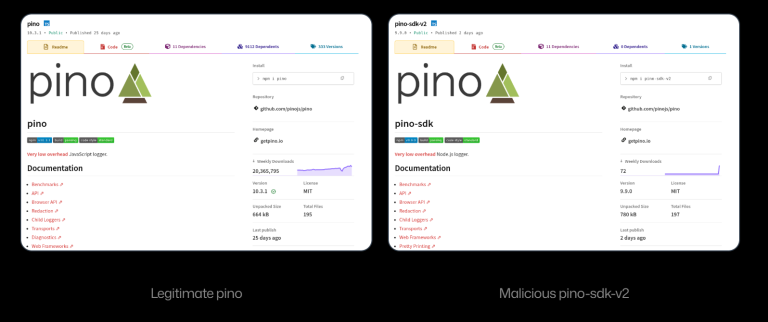
SafeDep uncovers pino-sdk-v2, a malicious npm package impersonating the pino logger to silently steal .env secrets and exfiltrate them via Discord.
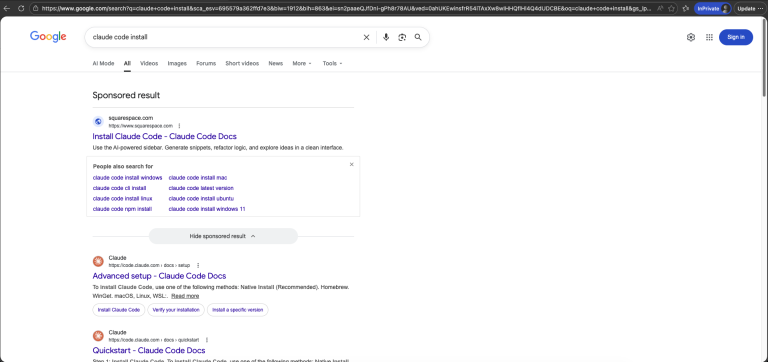
Hackers are targeting AI developers with a fake Claude Code "InstallFix" malvertising campaign, using malicious terminal commands to drop Amatera malware.
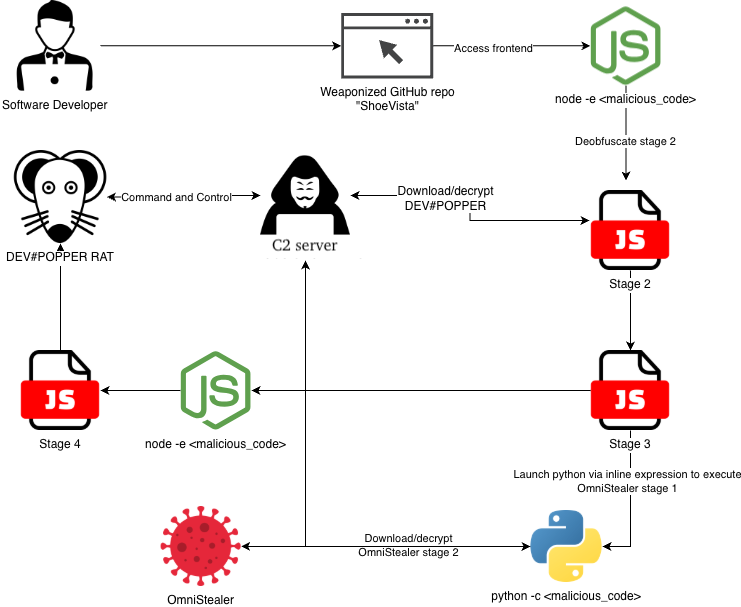
eSentire exposes DEV#POPPER, a North Korean RAT hiding in GitHub repos. It uses blockchain to deploy OmniStealer, targeting crypto and dev secrets.
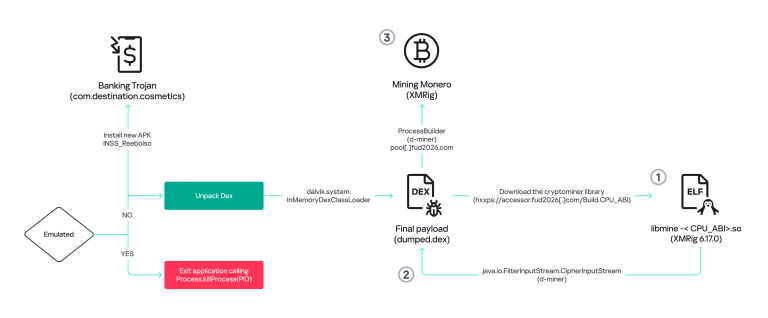
Kaspersky uncovers BeatBanker, an Android malware in Brazil using an audio loop to evade detection while mining crypto and stealing banking credentials.

Chinese APTs like Camaro Dragon are targeting Qatar with PlugX malware and Cobalt Strike, weaponizing Middle East tensions for cyberespionage.
A fake CleanMyMac website is using ClickFix tactics to trick macOS users into installing SHub Stealer, a potent malware targeting passwords and crypto.
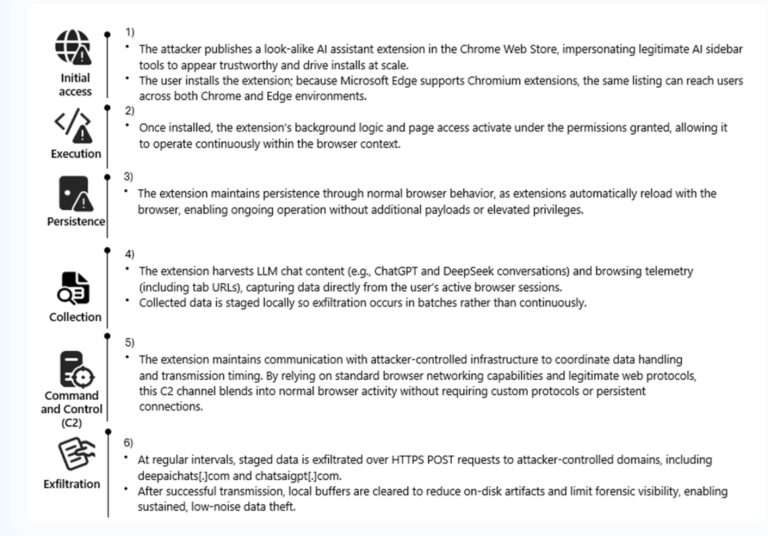
Microsoft Defender uncovers a massive campaign of malicious Chromium extensions impersonating AI tools to steal data from 900,000 users. Audit browsers now.
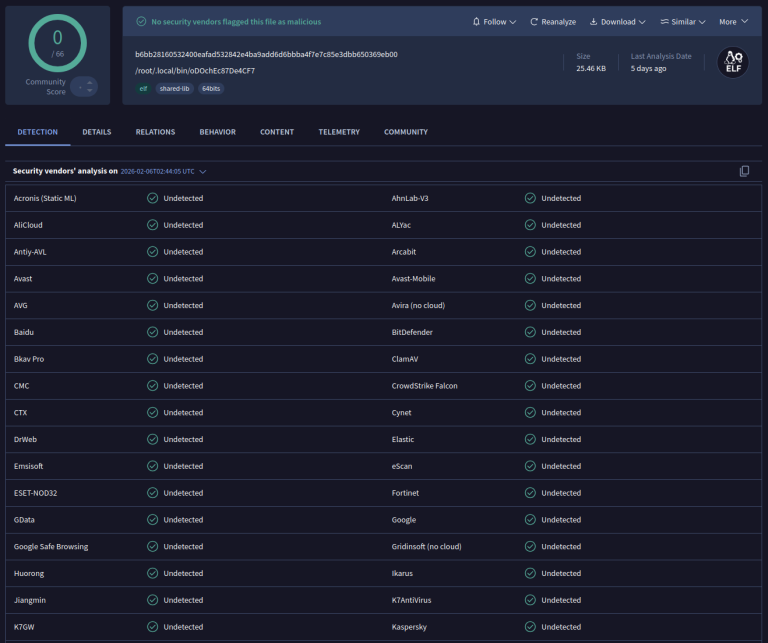
Cyble Research unmasks ClipXDaemon, a C2-less Linux malware that silently hijacks cryptocurrency wallet addresses in X11 clipboard environments.

Cisco Talos exposes UAT-9244, a China-linked APT targeting South American telecoms with stealthy malware like the BitTorrent-based PeerTime and TernDoor.

Iranian APT Seedworm intensifies cyberespionage against US and Israeli networks using a new stealth backdoor called Dindoor. Read the full threat report.

Trend Micro reveals the BoryptGrab info stealer campaign using SEO-optimized fake GitHub repos to deploy the TunnesshClient reverse SSH backdoor.
Researchers uncover a massive campaign by a Vietnamese operator using GitHub and Polygon blockchain smart contracts to distribute the StealC infostealer.