
 Do Son
VirusTotal warns of massive supply chain attack on OpenClaw. Hackers use fake "skills" to deploy malware like Atomic Stealer. Verify your agents.
Malware

APT28 launches "Operation Neusploit" targeting Europe. Hackers exploit CVE-2026-21509 to deploy MiniDoor malware via RTF files. Patch Office now.

IClickFix malware hijacks 3,800+ WordPress sites with fake Cloudflare CAPTCHAs. This watering hole attack tricks users into running malicious PowerShell.

Cisco Talos warns of UAT-8099 targeting Asian IIS servers with region-locked BadIIS malware. New variants now attack Linux systems.

Attackers use fake DHL invoices to sideload Phantom Stealer v3.5.0 via a signed Java utility. Malware hides in AddInProcess32.exe. Watch out.
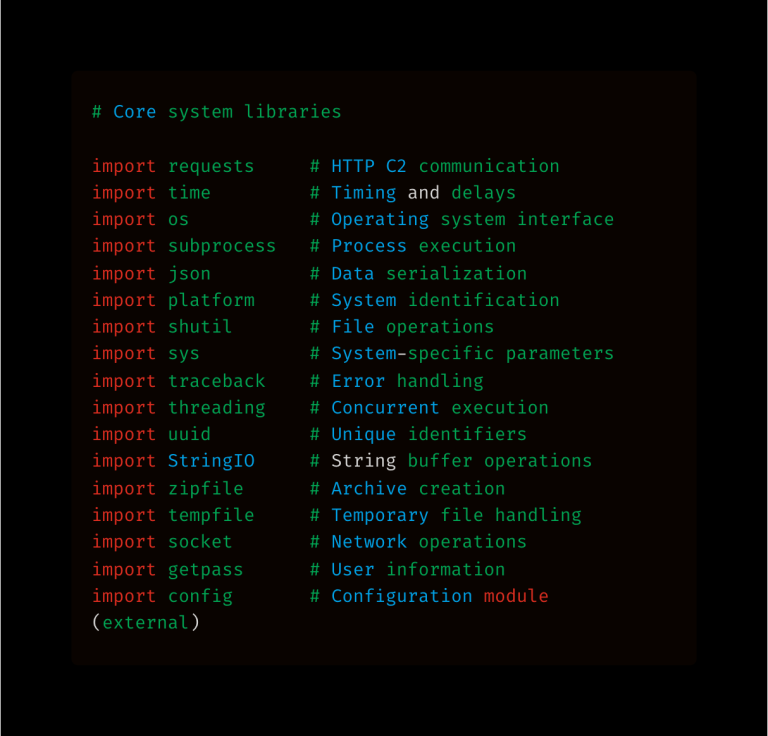
K7 Labs uncovers a stealthy Python-based RAT disguised as an ELF binary. Features adaptive beaconing and anti-forensics to stay hidden. Read the analysis.

New AI-generated malware campaign targets job seekers. Vietnamese actor "Huna" uses fake job offers to deliver PureRAT via Dropbox.

Critical supply chain attack hits eScan antivirus. Hackers hijacked updates to install malware and disable the AV. Manual patch required.

Pakistan-linked spies target India with "Sheet Attack," using Google Sheets for C2 and GenAI to build malware. Learn about SHEETCREEP and FIREPOWER.
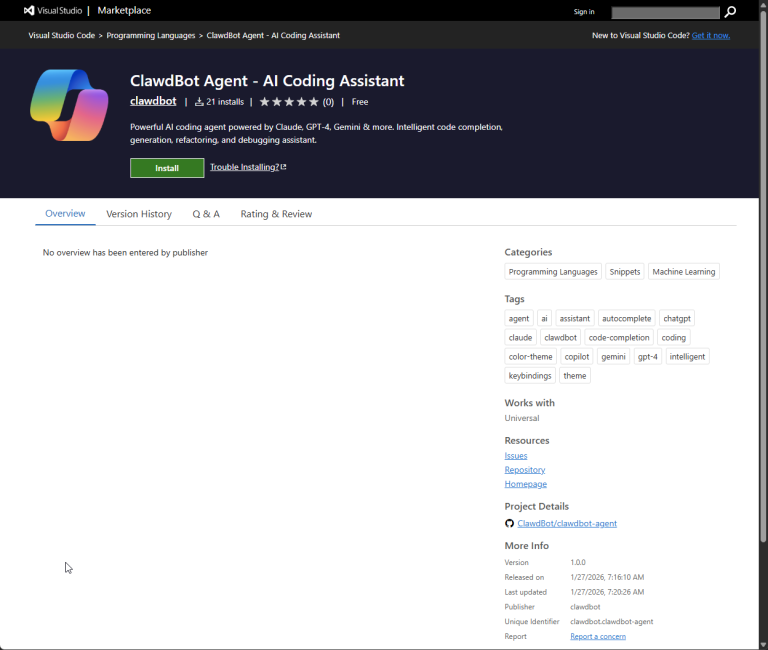
Malicious "ClawdBot Agent" VS Code extension exposed. Functioning as a real AI tool, it silently dropped malware. Microsoft removed it after 21 installs.

New Fake CAPTCHA campaign uses Google Calendar & steganography to drop Amatera Stealer. See how this attack exploits legitimate Windows tools to stay hidden.
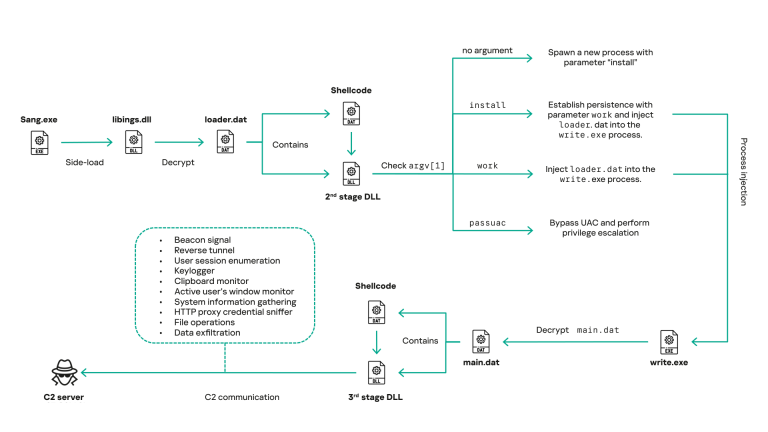
HoneyMyte (Mustang Panda) shifts to real-time surveillance using updated CoolClient. New 2025 campaign uses Pixeldrain for stealthy exfiltration.

New "Gopher Strike" & "Sheet Attack" campaigns hit Indian govt. Linked to Pakistan, attackers use GitHub C2 & GenAI malware to evade detection.

Trend Micro uncovers PeckBirdy, a JScript C&C framework used by China-aligned APTs. It uses lightweight, fileless tactics to target Asian governments.

Malicious npm package "ansi-universal-ui" drops "G_Wagon" infostealer to steal cloud keys and wallets. Check for .gwagon_status and rotate creds now.
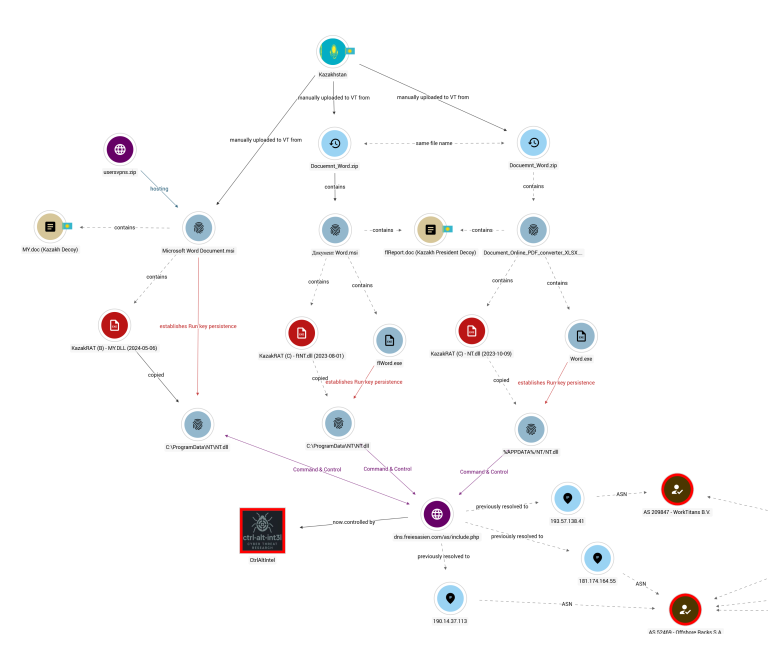
Researchers uncover "KazakRAT," a state-affiliated spyware targeting Kazakhstan & Afghanistan. A lapsed domain allowed experts to sinkhole the C2.

New ClearFake malware uses fake CAPTCHAs & "ClickFix" tactics to trick users into pasting malicious code. 150k victims infected via blockchain.

Official EmEditor installer hijacked to push malware. This supply chain attack steals credentials & evades detection. Check your logs for these domains.

DPRK spies weaponize Visual Studio Code tunnels to bypass security. Darktrace reveals a campaign targeting South Korea with government decoys.

New Osiris ransomware hits Southeast Asia, linking to Inc & Medusa groups. It uses BYOVD tactics to disable defenses. Unrelated to the 2016 variant.

Malicious PyPI package "sympy-dev" impersonates SymPy to install XMRig miners via fileless execution. Check your dependencies immediately.

New macOS malware "MacSync" uses fake cloud installers & "ClickFix" terminal commands to steal crypto. It bypasses Gatekeeper to trojanize wallet apps.