
 Do Son
The SolyxImmortal info stealer targets user data. Learn how this Python malware steals passwords and abuses Discord webhooks to exfiltrate files.
Malware

Microsoft uncovers a massive npm dependency confusion attack targeting enterprise infrastructure. Learn how these malicious packages discovered run code.

FortiGuard Labs exposes a highly evasive PureLogs info stealer campaign utilizing process hollowing and fileless execution.

Fox-IT uncovers a sophisticated Lazarus memory-only toolset used to compromise financial firms via an evasive three-stage malware pipeline.
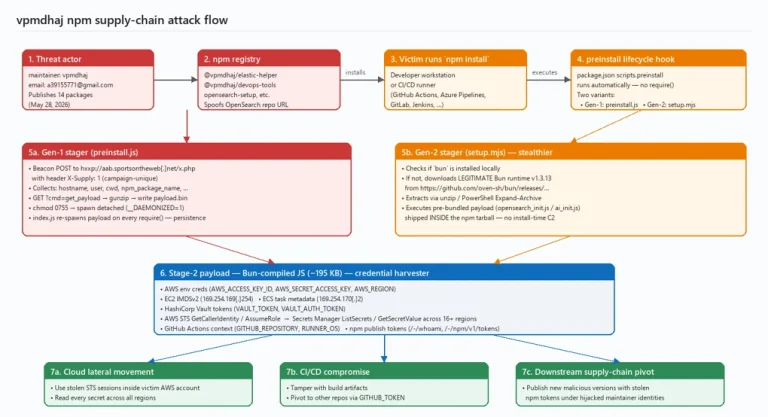
A critical npm supply chain attack exploits lookalike packages to distribute credential harvesting malware. Learn how to protect your cloud assets.
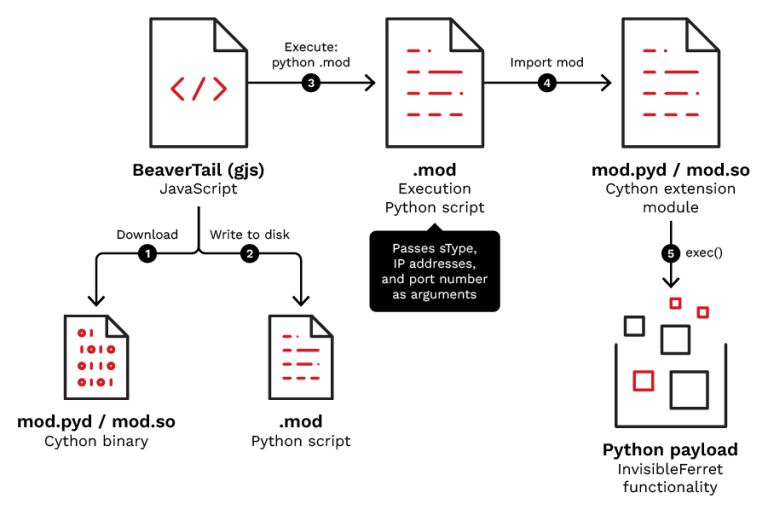
TrendAI Research exposes the new Void Dokkaebi Cython malware campaign. Learn how InvisibleFerret uses binary compilation to evade security teams.
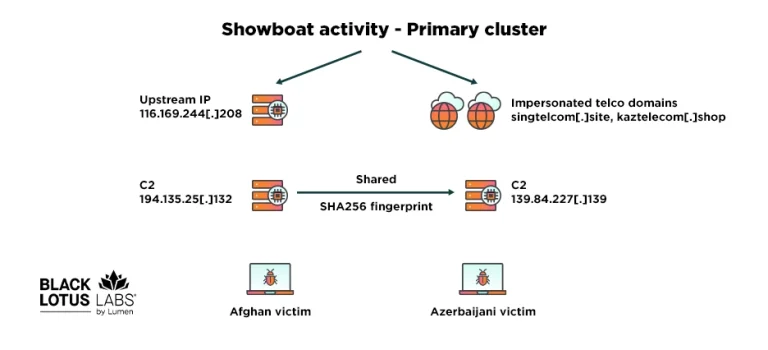
Discover the new Showboat Linux malware framework uncovered by Black Lotus Labs. Learn how PRC threat actors target telecommunications networks.
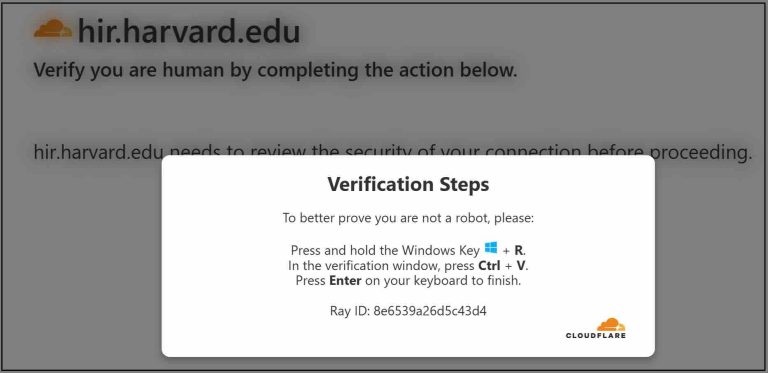
XLab uncovers a massive Ghost CMS poisoning campaign utilizing CVE-2026-26980 to launch FakeCaptcha attacks. Learn how to secure your site.
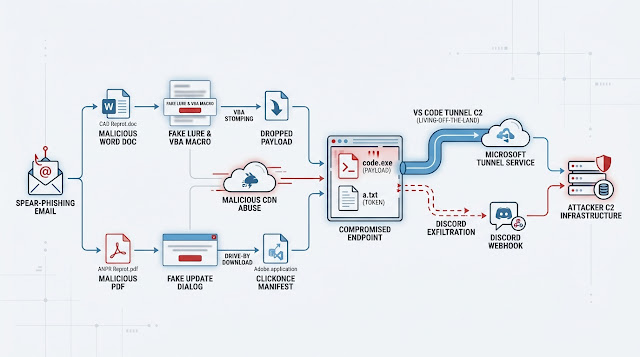
Learn how a sophisticated phishing campaign leverages VS Code Remote Tunnels abuse to bypass security and control enterprise networks.

Researchers uncover the Tampered Chef malware cluster disguised as PDF editors and tools. Learn how these stealthy threats bypass corporate defenses.

Security researchers have exposed a malicious Go module backdoor hidden inside the shopsprint/decimal package that executes code using stealthy DNS TXT records.

TrendAI exposes Banana RAT, a fileless banking trojan by SHADOW-WATER-063 that uses in-memory execution and fake UI overlays to hijack Pix-QR transfers.

A recent report shows persistent P2Pinfect botnet activity inside Google Kubernetes Engine via exposed Redis instances. Learn how to secure your network.
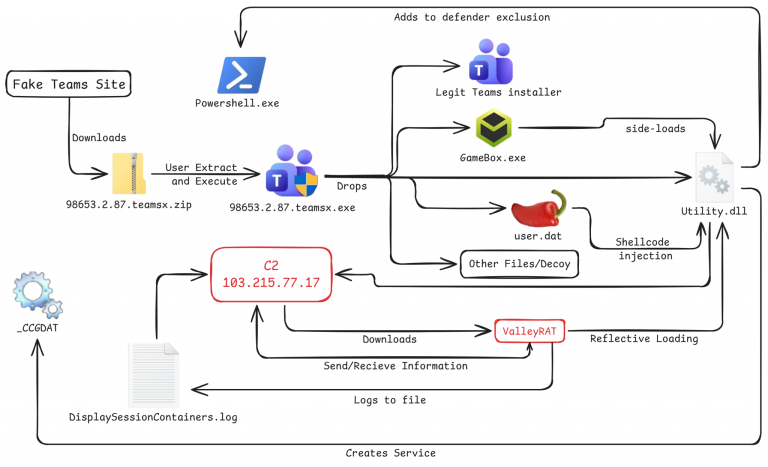
A sophisticated ValleyRAT malware campaign uses fake Microsoft Teams installers and DLL sideloading to evade Windows Defender detection.

Socket exposes a clever cross-ecosystem supply chain attack targeting PHP packages by hiding a malicious JS postinstall backdoor inside package.json.
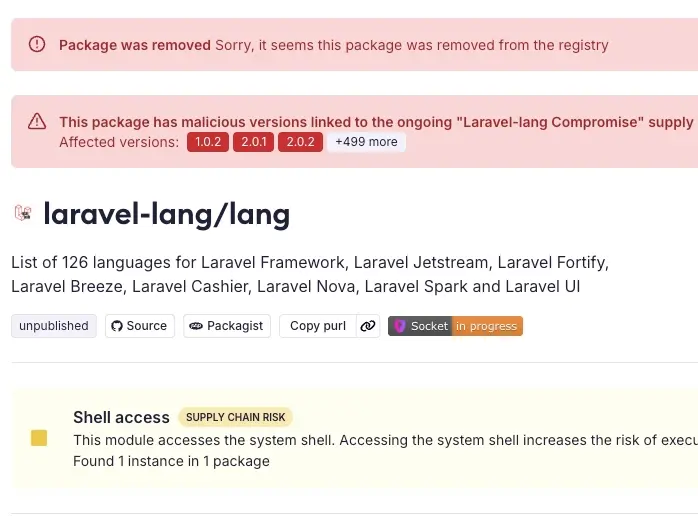
DevOps Alert: Over 700 laravel-lang localization package versions have been backdoored with a cross-platform 17-collector info-stealer. Audit your logs.
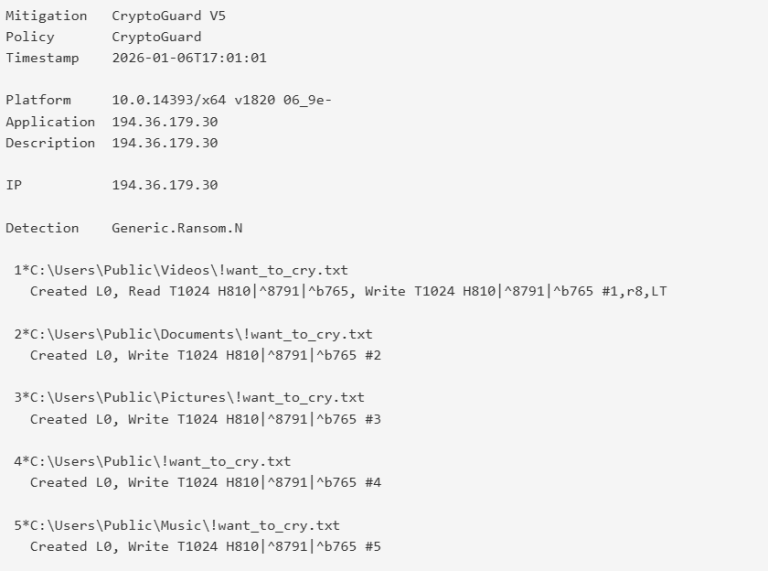
Sophos exposes WantToCry, a remote ransomware campaign that avoids EDR by using brute-forced SMB shares to read, encrypt, and rewrite files from afar.
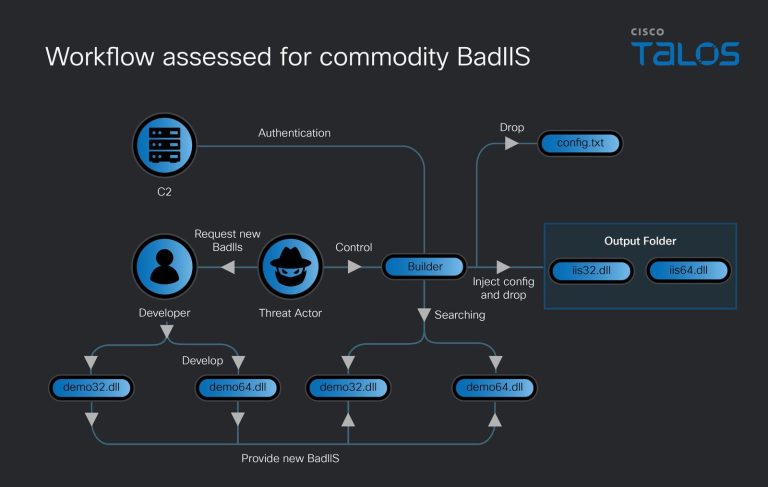
Cisco Talos exposes a commodity BadIIS variant sold as a service by dev "lwxat," featuring automated builders for traffic hijacking and reverse proxying.
Bypassing Terminal Protections: New SHub “Reaper” Variant Abuses AppleScript to Loot macOS Endpoints

Bypassing Terminal Protections: New SHub “Reaper” Variant Abuses AppleScript to Loot macOS Endpoints
SentinelOne exposes the SHub Stealer "Reaper" variant. It bypasses Apple's latest Terminal paste mitigations to hijack crypto wallets and corporate documents.

Symantec exposes fast16, a 2005 cyber-sabotage framework designed to inject an in-memory Lua engine and corrupt uranium-compression weapons simulations.
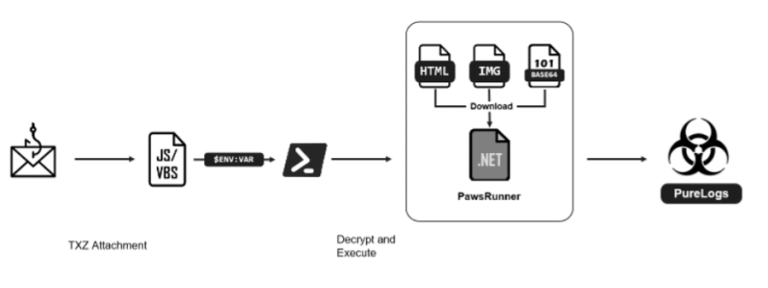
FortiGuard Labs warns of PawsRunner, a new .NET steganography loader hiding PureLogs infostealer payloads inside cat images to bypass corporate EDR.
Unit 42 exposes the new Gremlin stealer. It uses memory-resident techniques to hijack active browser session tokens and completely bypass MFA.