Skip to content
November 19, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • ADVISORIES
    • Microsoft
    • Fortinet
    • Ivanti
    • Cisco
    • Linux
    • Citrix
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q3 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Malware
  • Vulnerability News
  • Submit Press Release
Light/Dark Button
  • Home
  • News
  • Malware
  • Deceptive WeedHack Malware Campaign Infects Thousands of Minecraft Players
  • Malware

Deceptive WeedHack Malware Campaign Infects Thousands of Minecraft Players

Do Son June 8, 2026 3 minutes read
0
WeedHack malware campaign free Minecraft mods

WeedHack malware campaign | Image: McAfee Labs

Malware as a Service Targets Online Gaming Communities

A highly dangerous underground network is actively compromising the systems of thousands of online gamers. McAfee Labs exposed a massive WeedHack malware campaign spreading through gaming forums. This malicious operation operates under a commercialized service framework. To maximize corporate reach, the threat actors distribute their implants through popular gaming platforms. Consequently, standard signature blocklists often fail to detect the initial compromised files. Software security groups encourage extreme caution when downloading unverified external extensions.

Spreading Through Fake Videos and Poisoned Search Results

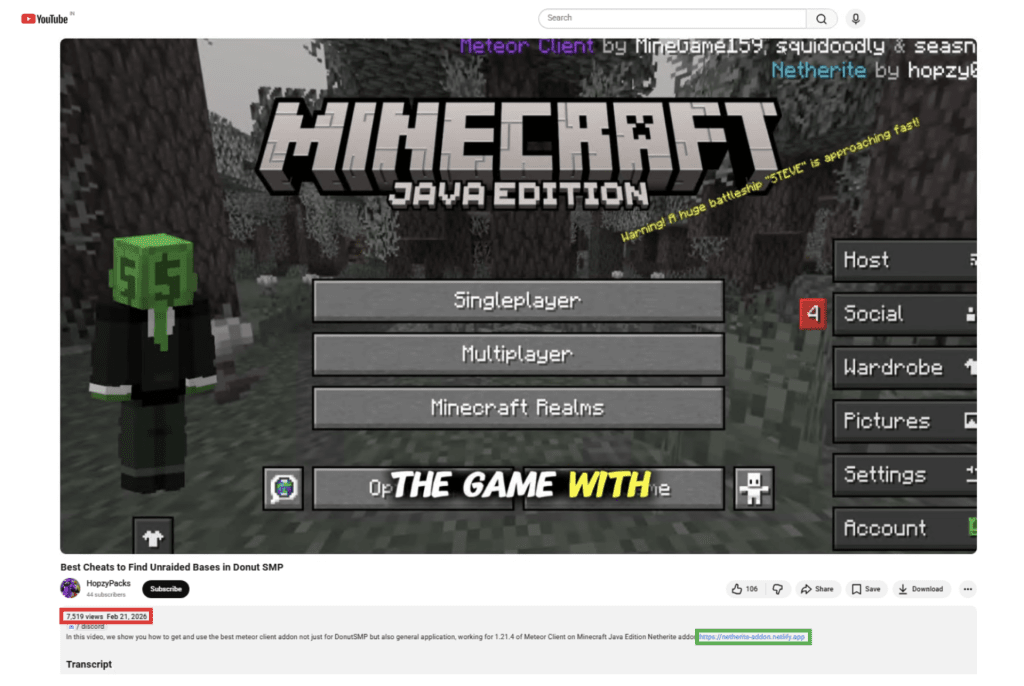
To begin with, the distribution pipeline relies heavily on deceptive social engineering tricks. The malicious operators provide detailed training manuals to help their subscribers launch successful attacks. For example, threat actors build highly polished video reviews showcasing advanced game capabilities. These video tutorials link directly to unverified download pages hidden inside the description blocks. According to the report, “Attackers create convincing YouTube videos reviewing or demonstrating Minecraft clients and mods.”

Understanding the SEO Poisoning Danger

Furthermore, the attackers deploy optimized web environments to trick search engine ranking algorithms. These rogue pages specifically masquerade as official portals offering free Minecraft mods. By using search engine optimization poisoning, the actors successfully hijack organic web traffic. Casual players see fake warnings instructing them to skip native antivirus blocklists. This systematic manipulation facilitates rapid computer infections without raising any initial network alerts.

The Silent Four Stage Infection Chain

Initial Homing and Protection Disabling

Subsequently, the compromised data packet initiates a hidden multi-layered execution process. The tool launches silently in the background without creating a visible terminal console. First, the script resolves its backend command hub using the public Ethereum blockchain infrastructure. Then, the malware turns off local Windows Defender defenses to protect its files from deletion. The report explicitly outlines this core setup phase. “Infection happens in four stages that happen silently in the background after a victim opens the downloaded file.”

Establishing Administrative Persistence

Additionally, the utility establishes an enduring presence by creating a custom background task. This persistent helper forces the computer to restart the malware every time a user logs into the terminal. For un-paying subscribers, the script simply harvests saved browser cookies and Discord access tokens. However, premium customers receive a much more aggressive toolkit for five dollars a month. This upgrade provides full remote desktop controls along with active keylogging and file alteration capabilities.

Invasive Stalking and the Peer Cyberbullying Epidemic

Moreover, the low financial barrier of this operation has attracted a younger generation of malicious hackers. Investigators discovered that many buyers deploy these remote utilities for personal harassment rather than simple financial fraud. Attackers record private video logs from victim webcams and share the footage as competitive trophies.

The technical writeup notes: “While monitoring the campaign’s Telegram channel, which had over 850 members during the time of our research, we observed that many customers appear to be teenagers and young adults, and a significant portion are using the remote access tools not for financial gain, but to harass and intimidate other players.”

Hardening Recommendations for Systems

Ultimately, neutralizing this active WeedHack malware campaign requires immediate perimeter adjustments. Users must completely avoid downloading unverified modification client files. In addition, turning on real-time web reputation blocklists stops the initial redirect loop. If an extrusion occurs, defenders should immediately reset all active session credentials. Finally, reporting the incident to local law enforcement preserves vital telemetry to stop these underground distribution rings permanently.

Add Daily CyberSecurity as a preferred source on Google

Related coverage

  • WeedHack Malware Still Hits Minecraft Gamers via Fake Sites
  • ViperSoftX Resurfaces: Stealthy Crypto-Stealing Malware Hits Global Users!
  • SmartRAT ClickFix Campaign Identified
  • Zloader Resurfaces: Stealthier Trojan Evolves with DNS Tunneling and WebSocket C2
  • New variant of Mispadu Stealer is Exploiting CVE-2023-36025 Vulnerability
  • Styx Stealer: The Evolved Threat to Your Crypto and Data
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: Account Hijacking Cyberbullying Discord Tokens Minecraft Security Remote Access Trojan SEO Poisoning WeedHack Malware

Leave a Reply Cancel reply

You must be logged in to post a comment.

🚨 Active Exploits in the Wild

  • CVE-2026-123890CVSS 9.8
    A malicious actor with network access to vCenter may exploit this issue to bypass authentication and gain unauthorized...
    Watchtower Verified📅 Updated: Nov 19, 2026
  • CVE-2026-114938CVSS 8.1
    Vulnerability in the Oracle Java SE, Oracle GraalVM for JDK, Oracle GraalVM Enterprise Edition product of Oracle Java...
    Admin intel📅 Updated: Nov 19, 2026
  • CVE-2010-20126CVSS 5.1
    Virtual Keyboard plugin for SquirrelMail through 0.9.1 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers to...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2012-20007CVSS 9.3
    ThinkPHP 2.0 through 2.2 and 3.0 Lite mode contains an eval injection vulnerability in the Dispatcher PATH_INFO parsing,...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2012-20008CVSS 8.7
    openSIS 5.1 before 9.0 contains a local file inclusion vulnerability that allows authenticated users to include arbitrary files...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2026-119618CVSS 8.1
    Concurrent Execution using Shared Resource with Improper Synchronization vulnerability in Apache HTTP Server's mod_http2 in assign_headers() can lead...
    Admin intel📅 Updated: Nov 18, 2026
  • CVE-2024-10441CVSS 9.8
    Improper encoding or escaping of output vulnerability in the system plugin daemon in Synology BeeStation OS (BSM) before...
    CISA KEV📅 Added to KEV: Nov 18, 2026
  • CVE-2026-40217CVSS 8.8
    LiteLLM through 2026-04-08 allows remote attackers to execute arbitrary code via bytecode rewriting at the /guardrails/test_custom_code URI.
    CISA KEV📅 Added to KEV: Nov 18, 2026
Powered by CVE Watchtower

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Get free CVE alerts Pro from $7/mo

Critical Vulnerabilities

  • CVE-2026-115560CVSS 9.2
    Session serializer mismatch can lead to remote code execution. PHP's session upload progress feature can write attacker-controlled data...
    📅 Updated: Nov 19, 2026
  • CVE-2026-129182CVSS 9.2
    Use-after-free via repopulation of last_fatal_error_backtrace global after shutdown. As part of CVE-2026-109619 (GHSA-6wmf-4rv5-p3rp), PHP 8.5.12 fixes a generic...
    📅 Updated: Nov 19, 2026
  • CVE-2026-129496CVSS 9.2
    Timezone cache use-after-free can lead to remote code execution. PHP can retain a reference to a freed timezone...
    📅 Updated: Nov 19, 2026
  • CVE-2026-129481CVSS 9.2
    Use-after-free after interrupted session shutdown. PHP can retain a pointer to a script filename after session shutdown is...
    📅 Updated: Nov 19, 2026
  • CVE-2026-129474CVSS 9.2
    Use-after-free in magic method backtraces can lead to remote code execution. PHP can access freed memory when collecting...
    📅 Updated: Nov 19, 2026
  • CVE-2026-129289CVSS 9.2
    PHP-FPM request smuggling through an unread HTTP request body. PHP can fail to discard unread bytes from an...
    📅 Updated: Nov 19, 2026
  • CVE-2026-126714CVSS 9.2
    Partially overwritten session files can lead to remote code execution. PHP's file-based session handler can leave a session...
    📅 Updated: Nov 19, 2026
  • CVE-2026-123890CVSS 9.8
    A malicious actor with network access to vCenter may exploit this issue to bypass authentication and gain unauthorized...
    📅 Updated: Nov 19, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About Daily CyberSecurity
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DMCA
  • Privacy Policy

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.