 Do Son
The SideCopy APT campaign deploys custom RATs. Learn how the SideCopy APT campaign malware exploits mshta to target academic and government networks.
Remote Access Trojan
CoreRAT malware powers Core Werewolf attacks on Russian defense and government targets, using fake military PDFs and Telegram phishing.

Cisco Talos found msaRAT malware, a Rust RAT from the Chaos ransomware group that hides C2 traffic inside headless Chrome and Edge sessions.

Proofpoint details the Cruciferra crypter service that cloaks RATs and infostealers using BYOVD EDR tampering and 90+ custom encryption routines.

A CrySome RAT phishing attack used a fake freight rate confirmation to bypass AMSI, disable Defender, and steal browser credentials on Windows.
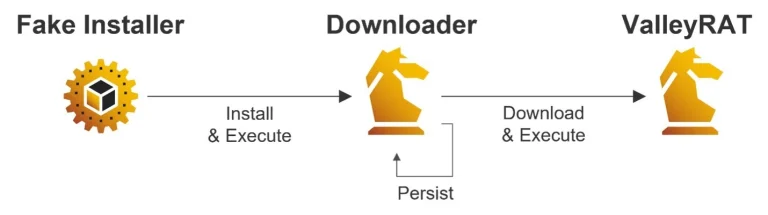
LevelBlue tracks a ValleyRAT malware email campaign using DLL sideloading and fileless execution to hit Japanese and Chinese users.
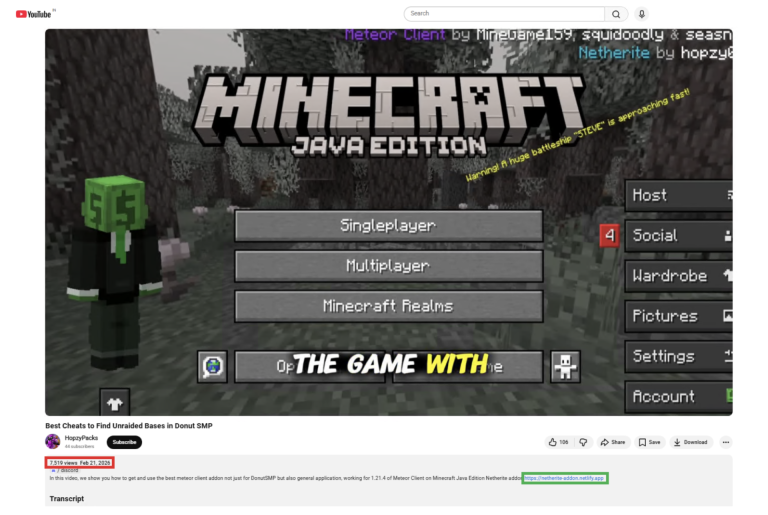
The active WeedHack malware campaign spreads via fake videos offering free Minecraft mods, leading to account hijacking and stealthy cyberbullying.
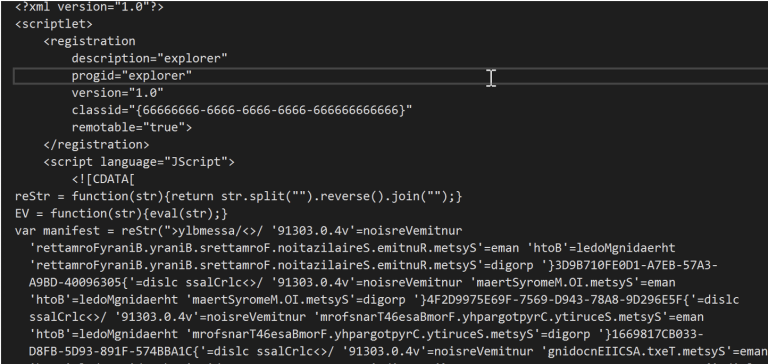
A stealthy Twill Typhoon RAT campaign targets APJ organizations. Discover how this threat exploits DLL side loading tradecraft to evade security.
Point Wild exposes a sophisticated PyInstaller loader using in-memory AMSI patching and SHA-512 decryption to drop XWorm V7.4. Patch now!
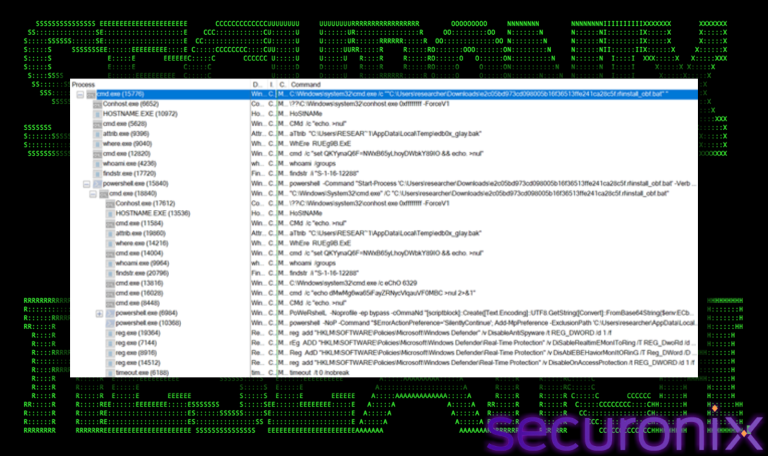
Meta Description (152 Characters)Securonix uncovers Deep#Door: a self-contained Python RAT that uses TCP tunneling and obfuscated scripts to bypass traditional defense. Secure your systems now.
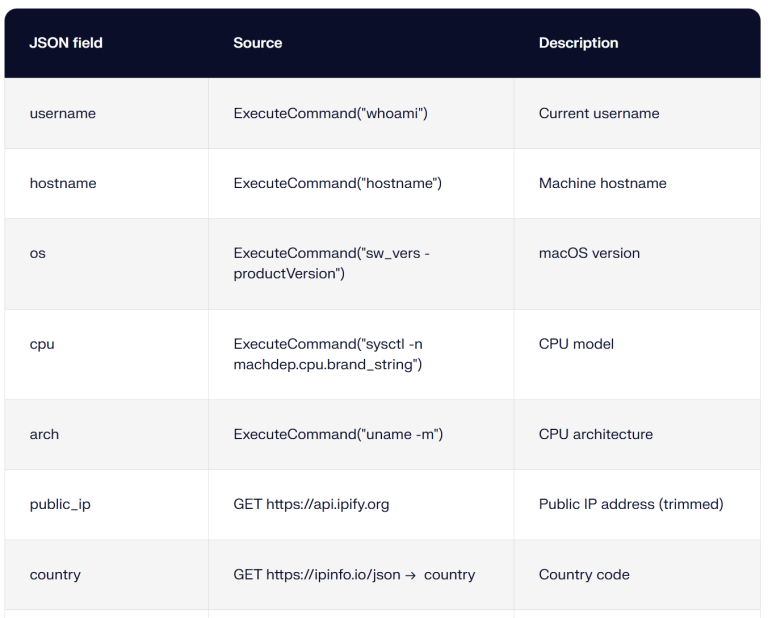
Minirat, a Go-based macOS RAT, exploits npm supply chains to bypass security. It features VM detection, AES encryption, and persistence. Secure your dev tools.
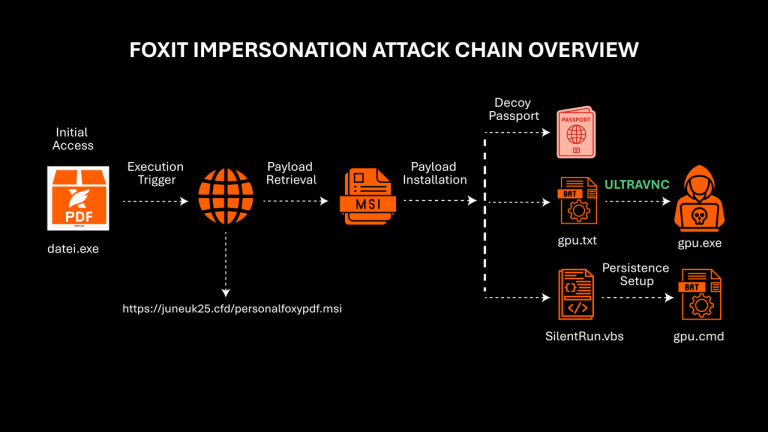
G DATA warns Foxit PDF users of a global malware campaign using fake installers and Danish passport decoys to deploy hidden UltraVNC remote access tools.
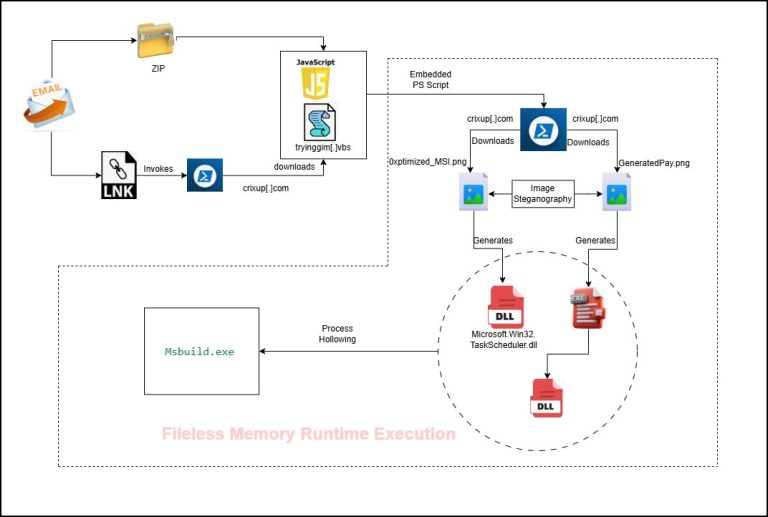
Trellix uncovers PureRAT, a modular Trojan hiding malware in PNG images. Learn how it uses steganography and fileless delivery to bypass Windows security.
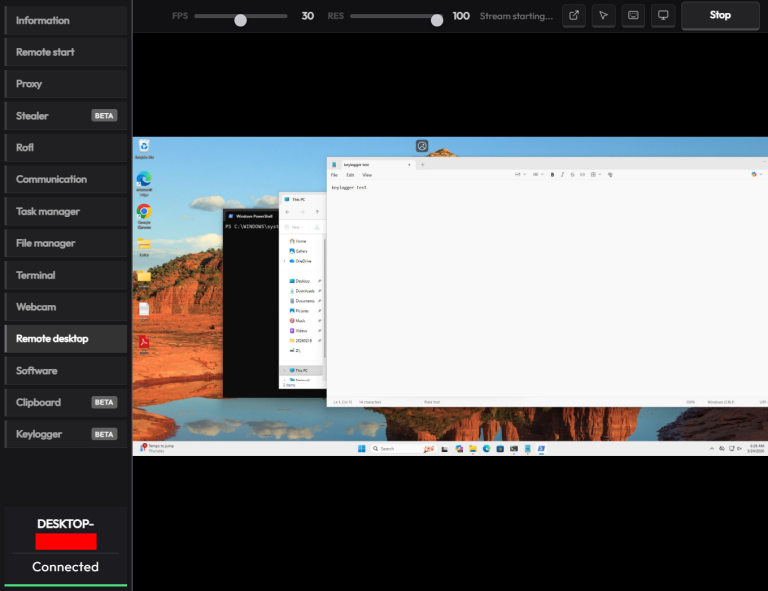
Kaspersky uncovers CrystalX RAT, a malicious MaaS on Telegram that pairs data theft with "prankware" to troll victims and lock systems. Patch now!
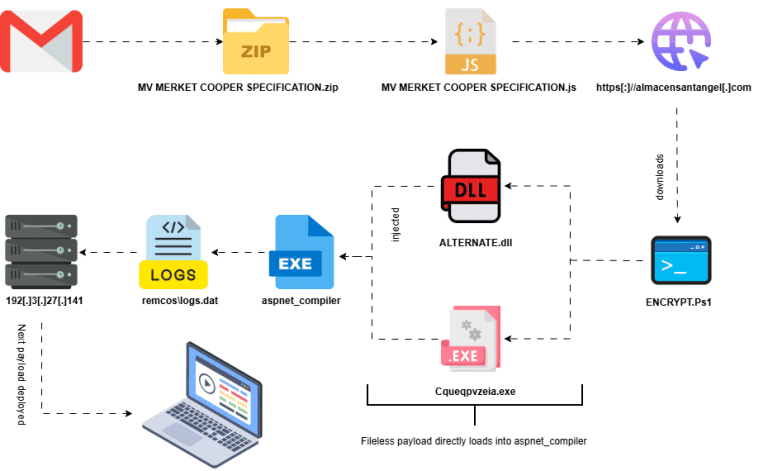
Researchers unmask a fileless Remcos RAT campaign using obfuscated JS and LOLBins to hijack systems in-memory. See the technical breakdown from Lat61.

Operation DualScript uses parallel execution to bypass defenses, hijacking crypto wallets and banking data via RetroRAT and clipboard swapping.

Researchers unmask ResokerRAT, a stealthy Trojan using Telegram to spy on systems and block security tools like Task Manager. Is your PC calling home?

The Axios npm hijack exposed millions to a RAT. Discover how North Korean-nexus actor UNC1069 used a masterful phishing ruse to bypass 2FA and steal credentials.
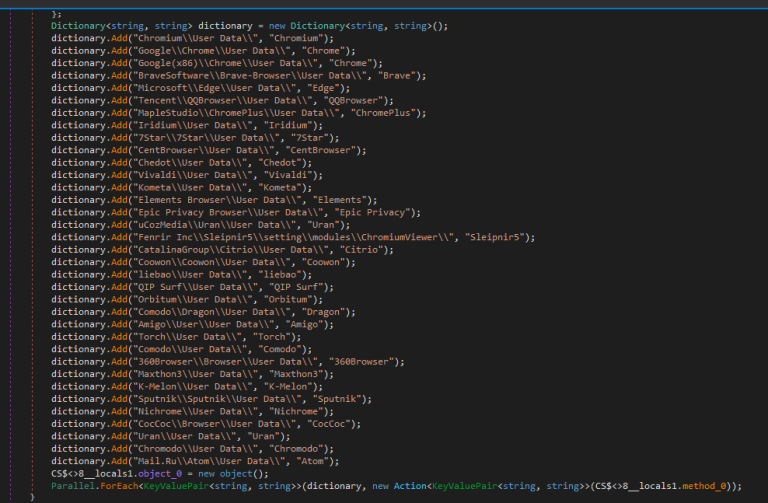
Malwarebytes uncovers a PureHVNC RAT campaign using Google Forms to bait professionals. Learn how this stealthy infection chain targets 2026 business docs.
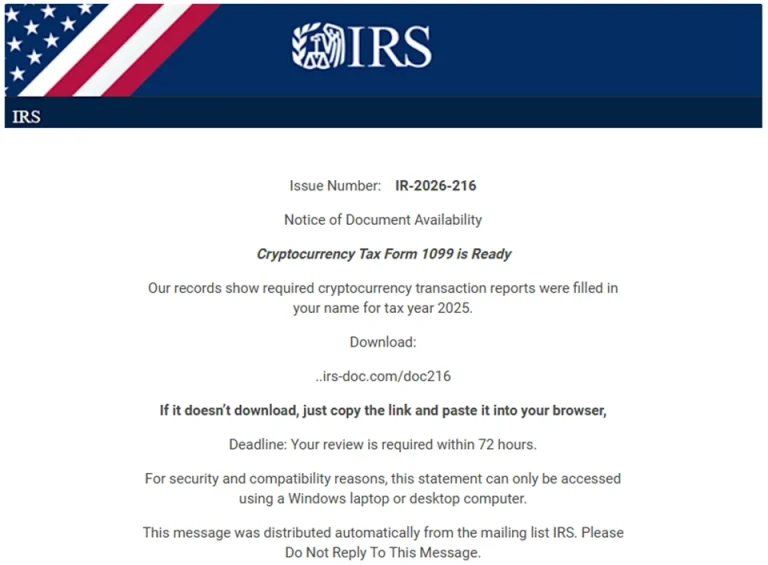
Microsoft warns of a surge in tax-themed phishing using PhaaS and ScreenConnect RATs to bypass MFA and hijack systems. Protect your W-2 data this season.
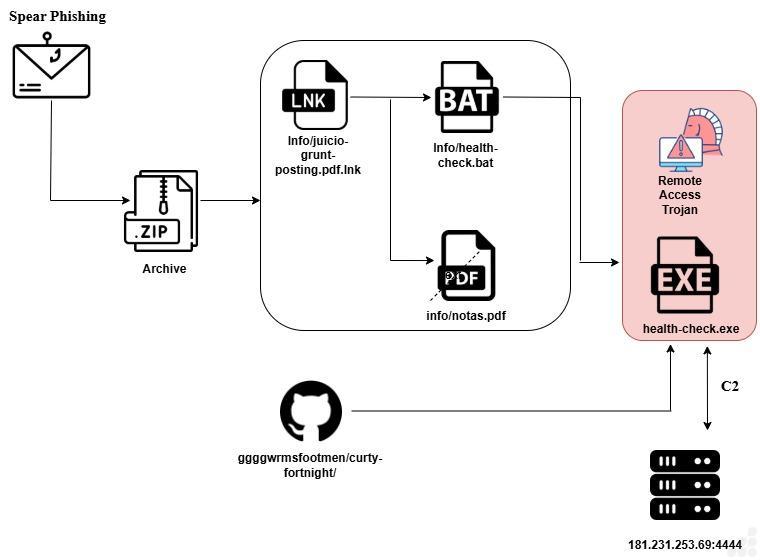
Lat61 Threat Intelligence uncovers a stealthy Rust RAT targeting Argentina's legal sector via weaponized judicial PDFs. Learn about its evasion tactics.
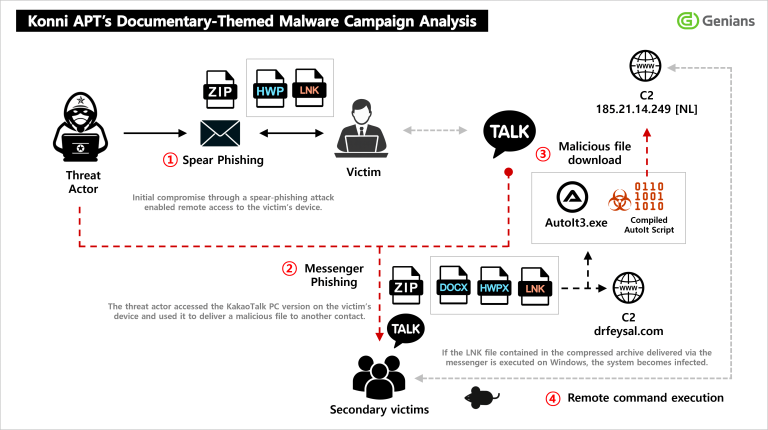
Genians Security Center reveals a new Konni APT campaign hijacking KakaoTalk PC sessions to distribute EndRAT, RftRAT, and RemcosRAT to trusted contacts.