 Do Son
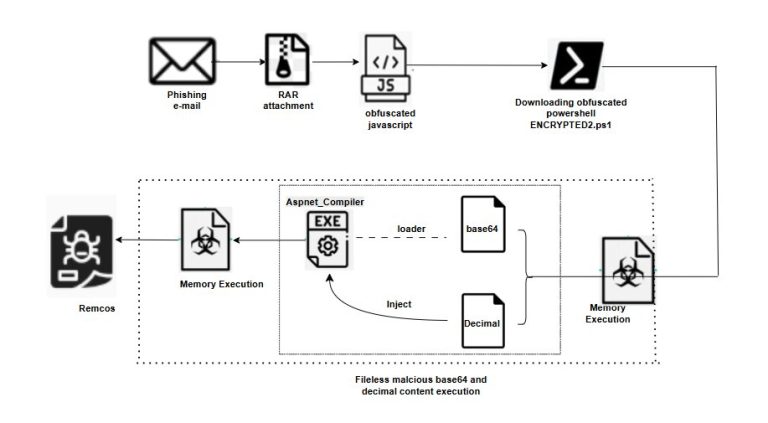
Trellix uncovers a stealthy, fileless Remcos RAT campaign utilizing process hollowing to execute entirely in memory and evade traditional security.
Remote Access Trojan

Cyfirma uncovers the RuTaxi Android banking Trojan, a highly persistent malware using VNC capabilities to hijack Russian bank accounts and crypto wallets.
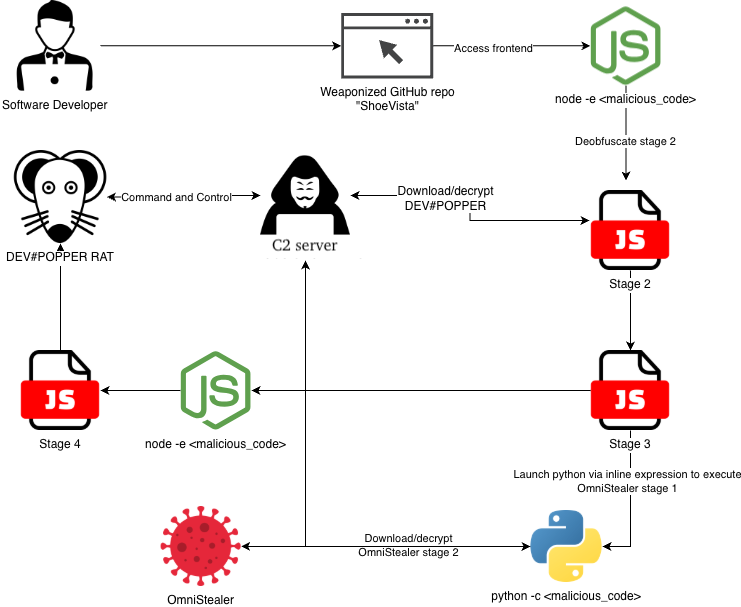
eSentire exposes DEV#POPPER, a North Korean RAT hiding in GitHub repos. It uses blockchain to deploy OmniStealer, targeting crypto and dev secrets.
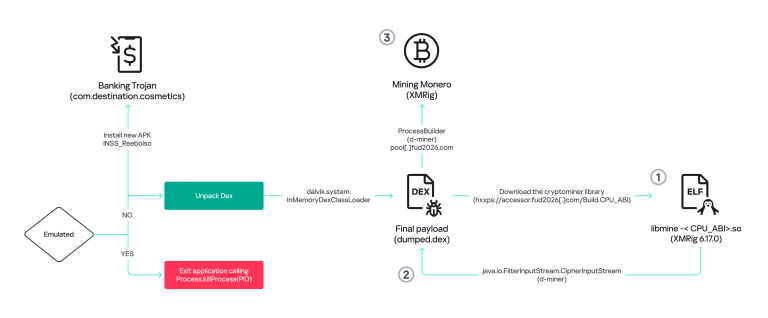
Kaspersky uncovers BeatBanker, an Android malware in Brazil using an audio loop to evade detection while mining crypto and stealing banking credentials.

Socket researchers uncover a Packagist supply chain attack where fake Laravel utility packages secretly install a persistent Remote Access Trojan (RAT).

CYFIRMA reveals a new cyber espionage campaign by Transparent Tribe (APT36) targeting Indian defense with stealthy multi-stage malware and decoy PDFs.

Cofense uncovers a stealthy campaign abusing legacy WebDAV in Windows File Explorer to bypass browsers and EDR, delivering XWorm and Async RAT via UNC paths.
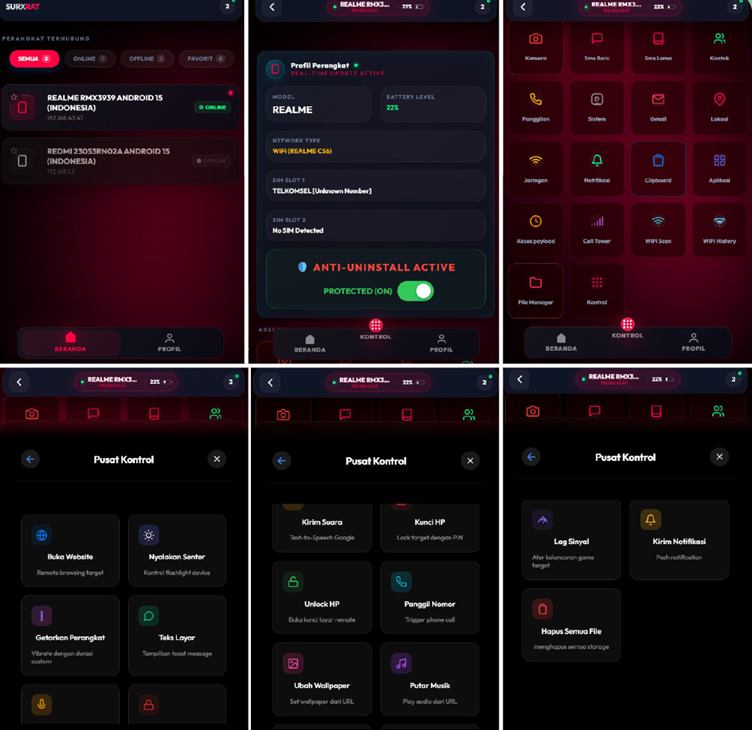
Cyble Research unmasks SURXRAT V5, a professionalized Android RAT experimenting with AI-assisted modules and hybrid monetization via Firebase infrastructure.
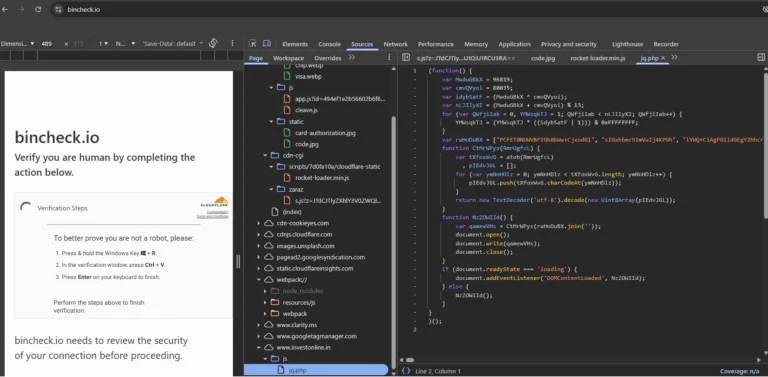
Elastic Security Labs uncovers a ClickFix campaign turning human helpfulness into a weapon. Fake verifications deploy the fileless MIMICRAT via PowerShell.

Point Wild reveals a new Remcos RAT variant abandoning local storage for real-time webcam streaming, memory evasion, and aggressive anti-forensics.
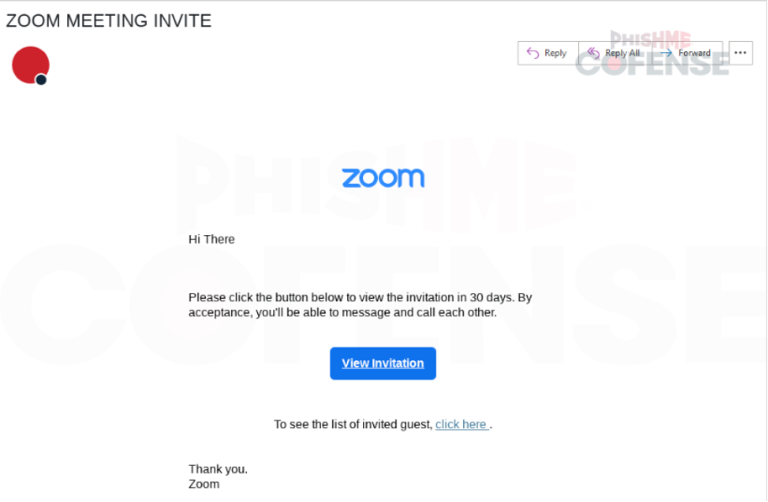
Cybercriminals are using fake DocuSign emails and the JWrapper framework to stealthily deploy SimpleHelp remote access tools. Learn how to spot the threat.

Acronis uncovers CRESCENTHARVEST, a new spyware targeting Iranian dissidents. Attackers use protest lures & Google DLL sideloading to steal data.

Critical dYdX supply chain attack: Compromised npm & PyPI packages steal seed phrases & deploy RATs. Remove @dydxprotocol/v4-client-js immediately.

Microsoft warns of "CrashFix": malicious extensions crash browsers to trick users into running a "fix" that installs a RAT. Beware fake ad blockers.
CYFIRMA unmasks APT36's latest campaign: a fake JLPT exam lure using fileless LNK malware to evade antivirus and spy on Indian government targets.

iVerify exposes Cellik, a $150/mo Android RAT that wraps malicious code inside Play Store apps to grant attackers total device control.

PyStoreRAT, a new fileless RAT, is spreading via fake GitHub repositories targeting developers. It executes as a JS implant via mshta.exe and includes explicit evasion logic against CrowdStrike.

A new C-compiled RAT, CastleRAT, uses Steam Community pages to hide its C2. The malware deploys advanced features like UAC Bypass, screen capture, and clipboard hijacking for espionage.

A new ValleyRAT campaign targets English job seekers. The malware uses DLL sideloading via a trojanized Foxit PDF Reader executable to run a Remote Access Trojan and exfiltrate data.

Darktrace exposed TAG-150, a new MaaS operator compromising 469+ US devices in months. The group uses ClickFix to trick victims into running malicious PowerShell that deploys the CastleLoader/CastleRAT backdoor.

Akamai exposed a malware that hides RAT C2 traffic by spoofing LLM chat-completion API requests on Tencent Cloud Serverless Functions. The payload is delivered via LNK/Sangfor DLL sideloading.

A new campaign is using Bitcoin wallet lures to distribute DarkComet RAT. The UPX-packed trojan gains persistence via a fake explorer.exe binary and uses keylogging and remote control to steal data.