
 Do Son
Trustwave exposes Blind Eagle (APT-C-36) leveraging exposed infrastructure and VBS malware in phishing campaigns, targeting Colombian banks with blatant disregard for concealment.
Remote Access Trojan

Sucuri uncovers a complex multi-stage malware campaign infecting WordPress sites via header.php to deliver a hidden RAT (client32.exe) and evade detection.

DRAT V2, a new Delphi-compiled RAT from TAG-140 (SideCopy/Transparent Tribe), is targeting Indian government entities with expanded post-exploitation and refined C2 techniques.

North Korean APT Kimsuky is using GitHub private repos, Dropbox, and XenoRAT malware via spearphishing to compromise victims and conduct cyber-espionage.

Red Canary uncovers Mocha Manakin, a new threat group using "paste and run" social engineering to deploy NodeInitRAT, a custom NodeJS RAT with potential ransomware links.

Shadow Vector campaign uses malicious SVGs in phishing emails to deliver AsyncRAT & RemcosRAT in Colombia, leveraging advanced DLL sideloading and in-memory execution.

The SERPENTINE#CLOUD campaign exploits Cloudflare Tunnel subdomains and LNK files to deliver in-memory RATs like AsyncRAT and Remcos, evading detection.

A new campaign, "Stargazers Ghost Network," weaponizes Minecraft mods on GitHub to distribute a multi-stage infostealer, targeting user credentials and crypto wallets.

North Korean APT Famous Chollima (Wagemole) is using a new Python-based RAT, PylangGhost, in fake job interviews to target crypto professionals and steal credentials.

Threat actors are actively compromising poorly managed MySQL servers, using UDFs to inject Gh0stRAT, XWorm, HpLoader, and legitimate Zoho agents for full system control and data theft.
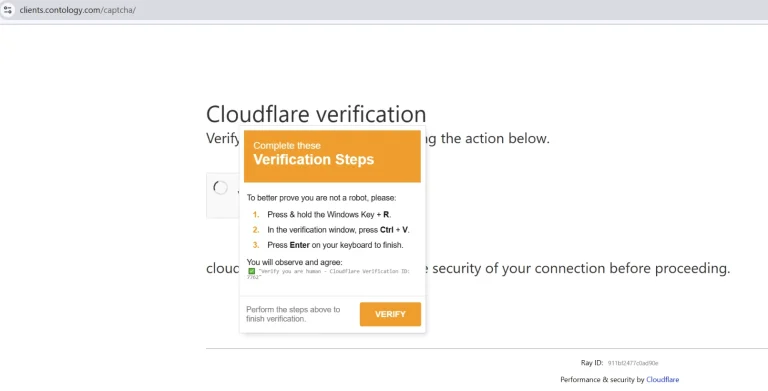
Elastic uncovers a sophisticated ClickFix campaign deploying the GHOSTPULSE loader to deliver ARECHCLIENT2 malware, leveraging social engineering for credential theft and remote access.

A new wave of invoice-themed phishing emails is distributing the Sorillus RAT across Europe, leveraging legitimate platforms like OneDrive and Ngrok for stealthy delivery.

KimJongRAT is back with new PE and PowerShell variants, using LNK files and CDNs to steal browser, email, and over 30 crypto wallet details from victims.

A fileless AsyncRAT campaign, dubbed "Clickfix," targets German-speaking users, luring them into executing obfuscated PowerShell payloads via fake verification prompts.

Censys uncovers "sostener.vbs," an obfuscated VBScript launching a multi-stage RAT delivery pipeline, affecting dozens and potentially linked to Blind Eagle APT.

CyberEye, a modular .NET RAT, offers widespread data theft and surveillance using a builder, Telegram C2, and anti-analysis features, making it a new threat.

CYFIRMA uncovers DuplexSpy, a powerful C# RAT on GitHub with surveillance, persistence, and anti-analysis features, posing a significant cybercrime threat.

A sophisticated "ClickFix" phishing campaign uses fake Booking.com CAPTCHAs to deliver RATs and info stealers to the hotel and travel industry.

Sophos X-Ops found a backdoored Sakura RAT targeting hackers and cheaters, spreading info-stealers via hidden scripts in open-source projects.
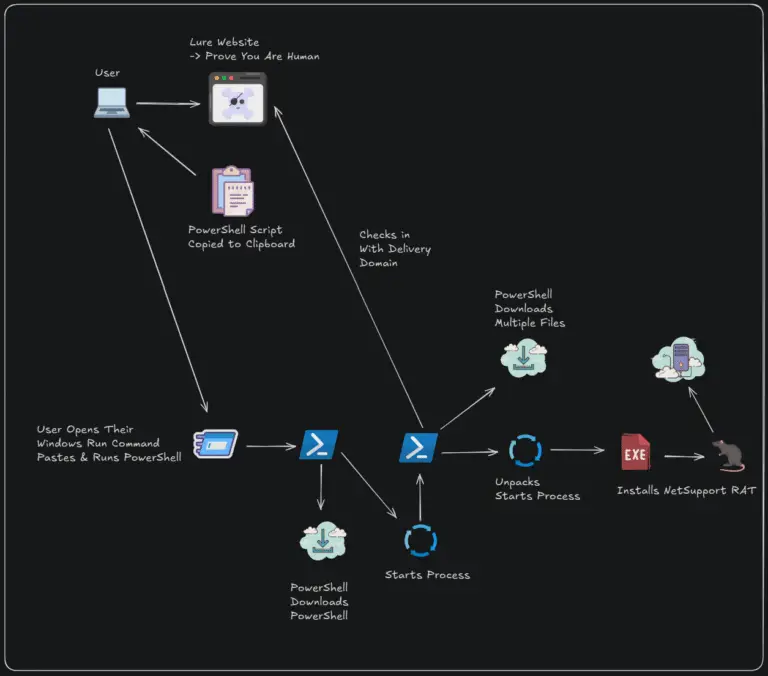
A new campaign uses fake DocuSign & Gitcodes pages to trick users into manually installing NetSupport RAT, gaining remote control.

IBM X-Force warns of a new phishing campaign by Hive0131 targeting Colombian users with DCRat malware via fake legal notices.

A stealthy spear-phishing campaign uses fake Rothschild job offers to trick finance execs into installing NetBird RAT, gaining remote access.