
 Do Son
Malicious scripts disguised as Cloudflare human verification are embedded in WordPress themes, tricking users into executing PowerShell commands that deliver malware.
Remote Access Trojan

Remcos RAT campaign evades antivirus using PowerShell-based in-memory execution. Steals data, bypasses UAC, and avoids detection with stealthy tactics.

Aikido discovers a Remote Access Trojan (RAT) hidden in rand-user-agent, a popular npm package with 45,000 weekly downloads.

Trustwave uncovers a fake CAPTCHA campaign delivering NodeJS backdoors via PowerShell and TryCloudflare, with SOCKS5 tunneling and RAT capabilities.

Cyfirma uncovers a Python-based RAT using Discord for command and control. It can lock screens, simulate BSOD, move the mouse, and steal data.

DslogdRAT malware exploited Ivanti Connect Secure via CVE-2025-0282, using web shells and C2 channels to evade detection and persist in networks.

A deep dive into a sophisticated multi-stage malware attack using Cloudflare to deliver AsyncRAT. Learn how attackers evade detection and compromise systems.

Learn about ResolverRAT, a new remote access trojan using advanced evasion to avoid detection. This malware employs sophisticated techniques.
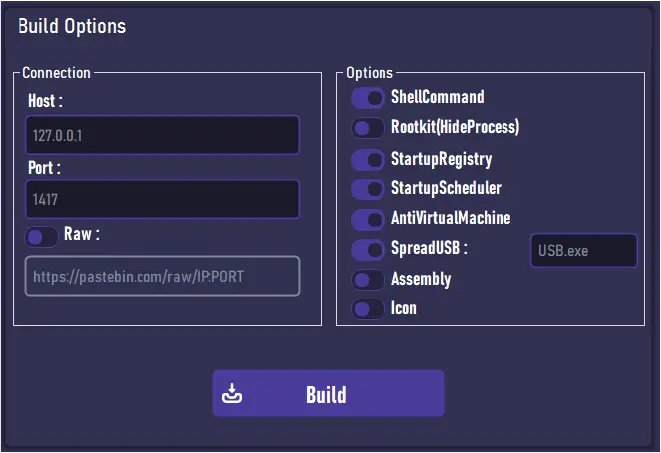
CYFIRMA researchers discovered Neptune RAT, an advanced Remote Access Trojan targeting Windows. Learn about its destructive features, evasion techniques, and distribution methods.
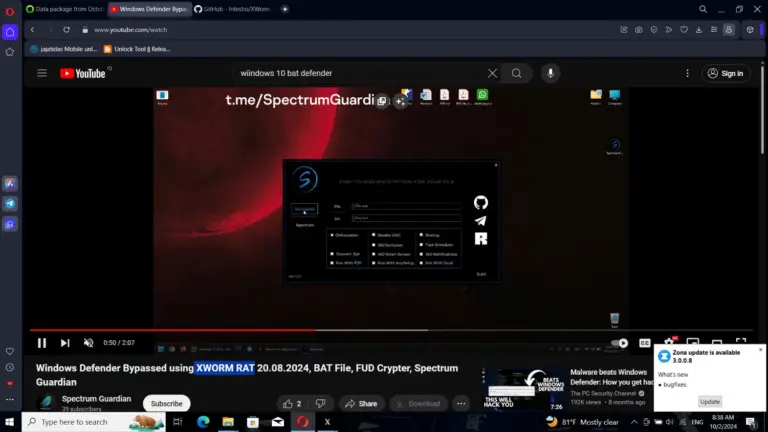
Beware of the XWorm Remote Access Trojan (RAT) builder attack. Discover how threat actors are targeting inexperienced cybersecurity enthusiasts with this malicious software.

Explore the sophisticated NonEuclid RAT and its evolution in malware sophistication. Discover its ransomware encryption and anti-VM checks.

Mustang Panda has been conducting a series of targeted attacks since April 2024, focusing on entities with interests in tax compliance and education

This particular scheme involves the misuse of GoTo Meeting, a popular online meeting platform, to deploy the notorious Remcos Remote Access Trojan

TRU have uncovered a disturbing trend in FIN7 attacks demonstrating the notorious cybercrime group's evolving tactics for infiltrating systems

The subsequent investigation unveiled a sophisticated RAT deployment masquerading as a standard Microsoft update process.

the 2023 Threat Insights Report recently published by HP Wolf Security, a significant surge in campaigns deploying RAT is recorded