 Do Son
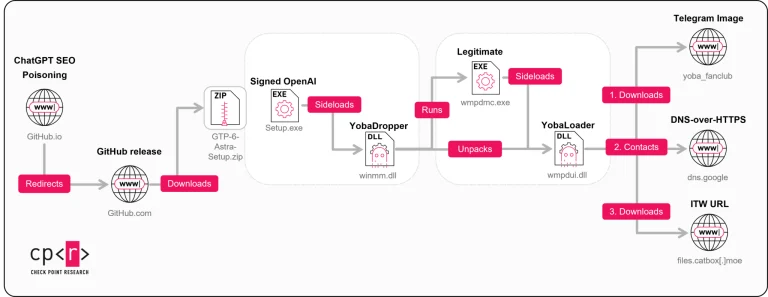
Check Point reveals the Yoba malware campaign. This GitHub Yoba malware campaign uses signed OpenAI and Anthropic binaries to sideload YobaLoader.
SEO Poisoning
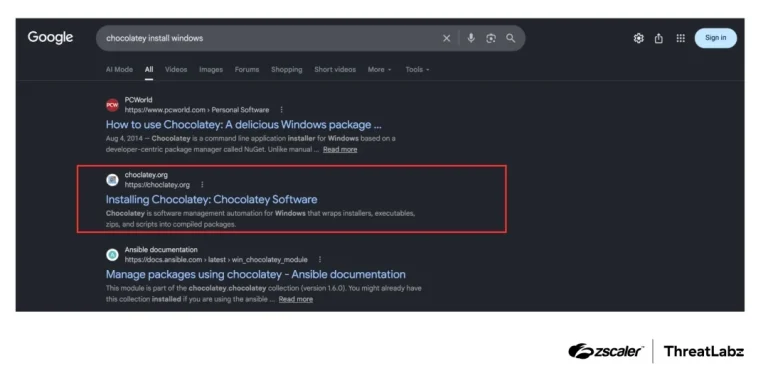
Zscaler uncovers an SEO poisoning campaign using fake Chocolatey and Massgrave sites to drop Armorsteal malware and Python Armorsteal malware modules.
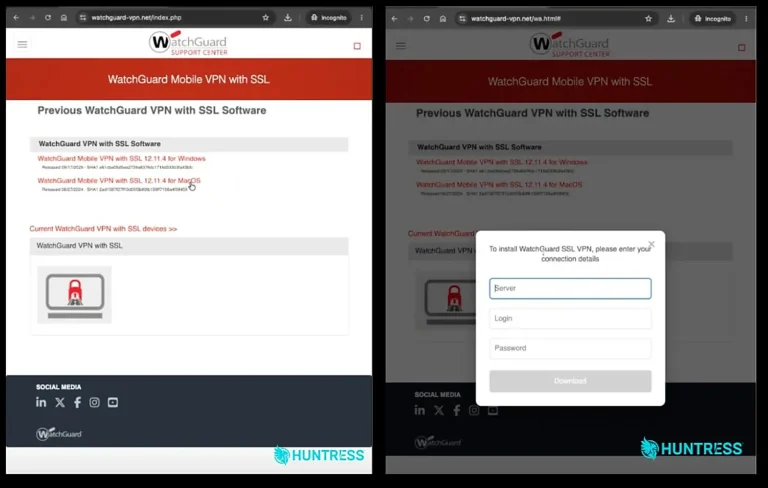
Huntress uncovers a WatchGuard VPN phishing campaign where a WatchGuard VPN phishing site steals logins twice before serving the real client.
The Gambling Goblin campaign turns Brazilian government websites into an SEO weapon. Suspected Gambling Goblin operators push illicit gambling pages.
WeedHack malware still targets Minecraft gamers through fake client sites and Minecraft SEO poisoning, McAfee Labs warns.

A massive cloud DNS takeover campaign exploits abandoned enterprise domains to serve Thai gambling content. 163 organizations are currently compromised.
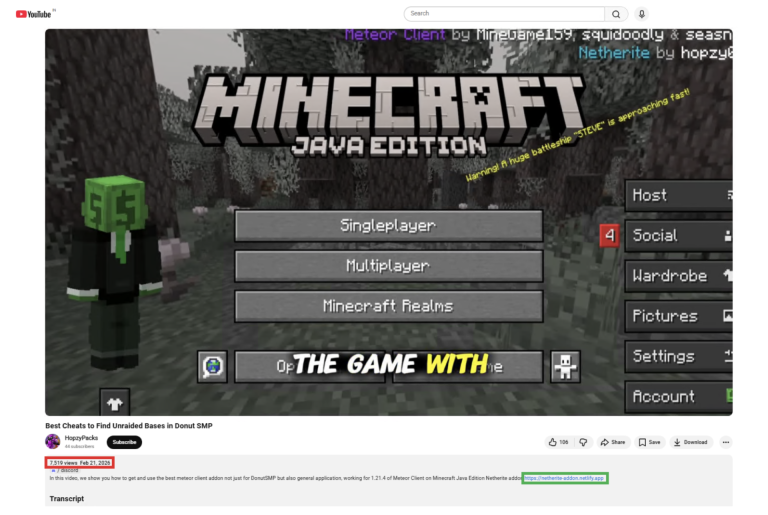
The active WeedHack malware campaign spreads via fake videos offering free Minecraft mods, leading to account hijacking and stealthy cyberbullying.

EclecticIQ warns of a malicious AI installer campaign using SEO poisoning to deliver fileless infostealers to developer environments.
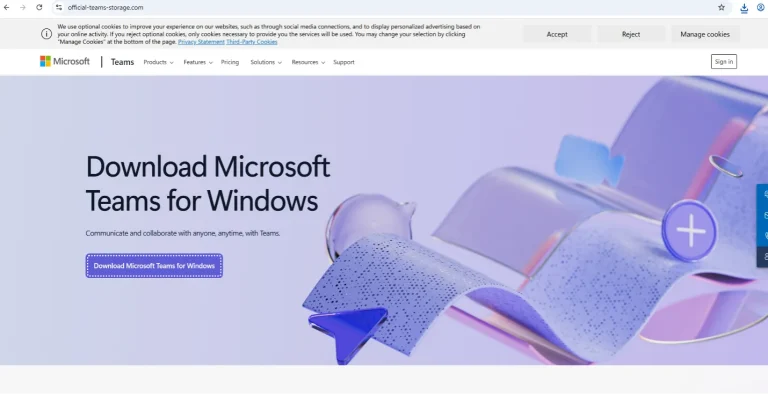
BlueVoyant unmasks "Lorem Ipsum": a well-funded campaign using SEO poisoning and signed MS Teams installers to deploy stealthy backdoors via image files.
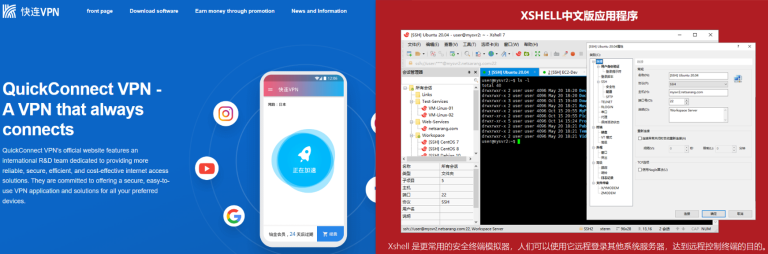
Kong RAT: A year-long SEO poisoning campaign targeting developers with trojanized SSH/VPN tools and .NET NativeAOT stealth. Learn how to stay protected.

Kaspersky reveals a fileless Trojan campaign targeting Proxifier searches. Learn how this "ClipBanker" hijacks crypto wallets via search engine poisoning.

Microsoft DART uncovers Storm-2755, a "payroll pirate" using AiTM traps and SEO poisoning to steal salaries. Protect your organization from this MFA bypass.

Beware of "MacSync Stealer": A new macOS malware campaign using SEO poisoning and terminal commands to hijack crypto wallets and system keys.

Microsoft Defender Experts warn of Storm-2561 using SEO poisoning to distribute fake enterprise VPN clients like Pulse Secure, stealing user credentials.
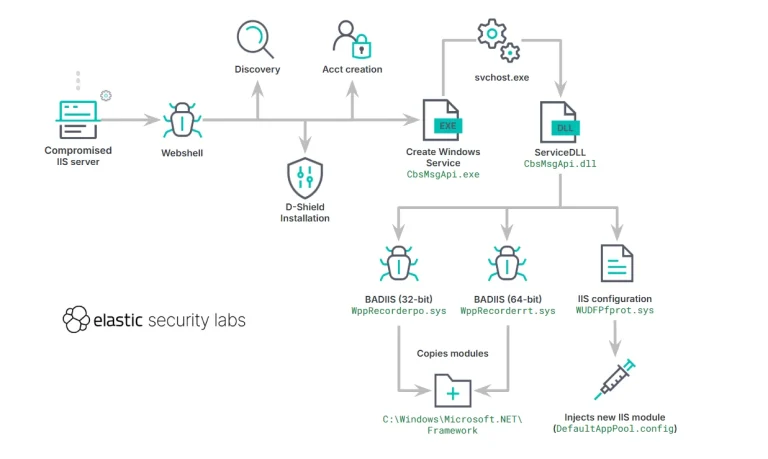
Elastic Security Labs uncovers BADIIS malware compromising 1,800+ IIS servers. Attackers use SEO poisoning to redirect users to illicit gambling sites.

Hackers are hijacking NGINX servers via malicious config injections. Datadog warns of silent traffic redirection for SEO poisoning. Check your proxy_pass.

Chinese APT Silver Fox is using a Cyrillic false flag in an SEO poisoning campaign impersonating Microsoft Teams. The attack installs ValleyRAT for espionage and financial fraud.

Acronis exposed TamperedChef, a global campaign using US shell companies to sign trojanized apps. The malware deploys a stealthy, obfuscated JavaScript backdoor via a scheduled task for long-term persistence.

The TamperedChef malware campaign uses trojanized apps and digitally signed binaries to steal browser data. Attackers use SEO poisoning to trick users into downloading.

A new large-scale SEO poisoning campaign, "Operation Rewrite," uses the BadIIS module to hijack web servers, manipulate search results, and redirect users to scams.

LastPass warns of a new SEO poisoning campaign that uses fake GitHub repos to trick Mac users into downloading Atomic Stealer, a malware that steals data.

A new report reveals a malware campaign using SEO poisoning to target Chinese-speaking users. Attackers use fake software sites to deliver Hiddengh0st and Winos.